
CVE-2026-73309
 bombobombone/cve-2026-73309
Proof-of-concept and technical write-up for CVE-2026-73309, an OAuth2 authentication bypass in XenForo before 2.3.13. Demonstrates empty…
authentication-authorizationexploitationpapers-research+2
bombobombone/cve-2026-73309Proof-of-concept and technical write-up for CVE-2026-73309, an OAuth2 authentication bypass in XenForo before 2.3.13. Demonstrates empty…
 hunt-benito/the-same-key-opens-every-box-cve-2026-71960-hard-coded-jwt-secret-in-cudy-wr3000-mesh-mqtt
PoC toolkit that unpacks router firmware, decrypts device secrets, forges JWT tokens, and exploits CVE-2026-71960/71961 to take over Cudy WR3000 mesh…
 squeeze440/cve-2026-73519-wolfstack-poc
PoC for CVE-2026-73519 - WolfStack hardcoded cluster secret leads to unauthenticated RCE (CVSS 9.8)
 george0papasotiriou/cve-2026-23006-kyber-ciphertext-length-side-channel
Python PoC for CVE-2026-23006, demonstrating a Kyber ciphertext length side-channel that leaks secret key bits via statistical analysis of…
 shinthink/cve-2026-66066
CVE-2026-66066 — KindaRails2Shell: Rails Active Storage/libvips Arbitrary File Read → RCE. MATLAB/HDF5 dual-identity file → SECRET_KEY_BASE theft →…
 george0papasotiriou/cve-2026-21004-sqlite-fts3-match-infoleak-via-query-crafting
Proof-of-concept exploit for CVE-2026-21004: uses crafted SQLite FTS3/4 MATCH prefix queries as a blind oracle to recover indexed secret data…
 george0papasotiriou/cve-2026-4567-post-quantum-kem-timing-side-channel-kyber-decapsulation-
Demonstrates a timing side-channel in Kyber KEM decapsulation using a vulnerable C server and Python attack script, measuring ciphertext rejection…
 0xsha/kindarails2shell
Single-file PoC for Rails CVE-2026-66066: arbitrary file read, secret recovery, threaded scanning, and conditional RCE via signed image variations.
 oscerd/cve-2026-46726
Reproducer for CVE-2026-46726: Apache Camel camel-vertx-websocket unfiltered inbound header injection enabling SSRF and secret disclosure via…
 covepseng/cve-2026-49352-poc
Exploitability PoC for CVE-2026-49352 (9router Hardcoded JWT Secret Authentication Bypass)
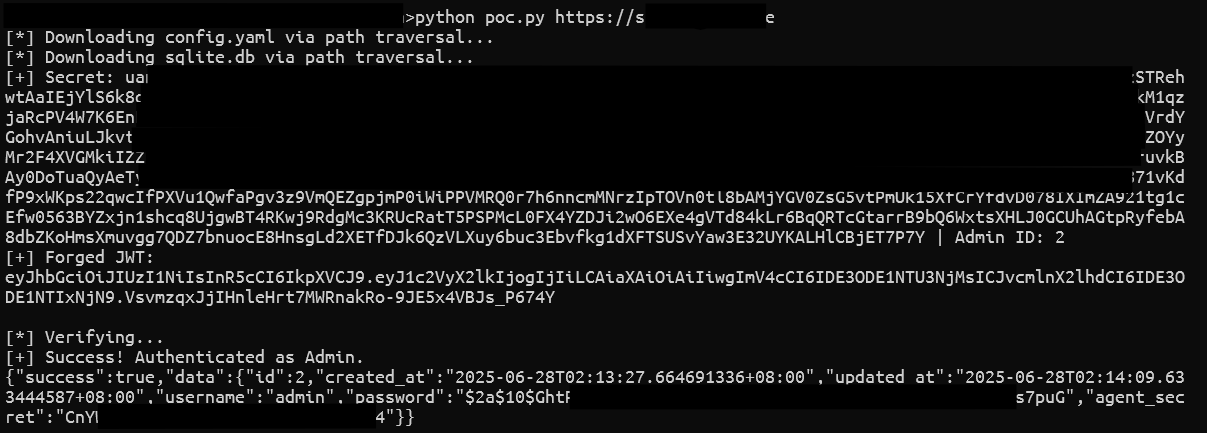 tar-xz/cve-2026-53519-poc
PoC exploit for CVE-2026-53519.
 okymi-x/cve-2021-43798
Python toolkit for authorized testing of CVE-2021-43798 Grafana path traversal, with arbitrary file read PoC, secret decryption, and user hash export…
 faridi-m/cve-2021-22911-rocketchat
Exploit for Rocket.Chat 3.12.1 RCE via pre-auth NoSQL injection, leaking admin TOTP secret and password reset token to achieve remote code execution…
 crowthearchfiend/rtcore64-probe
A tiny cpp program to test reading memory using a vulnerable RTCore64.sys driver/device (CVE-2019-16098). It tries to read a "secret" from its own…
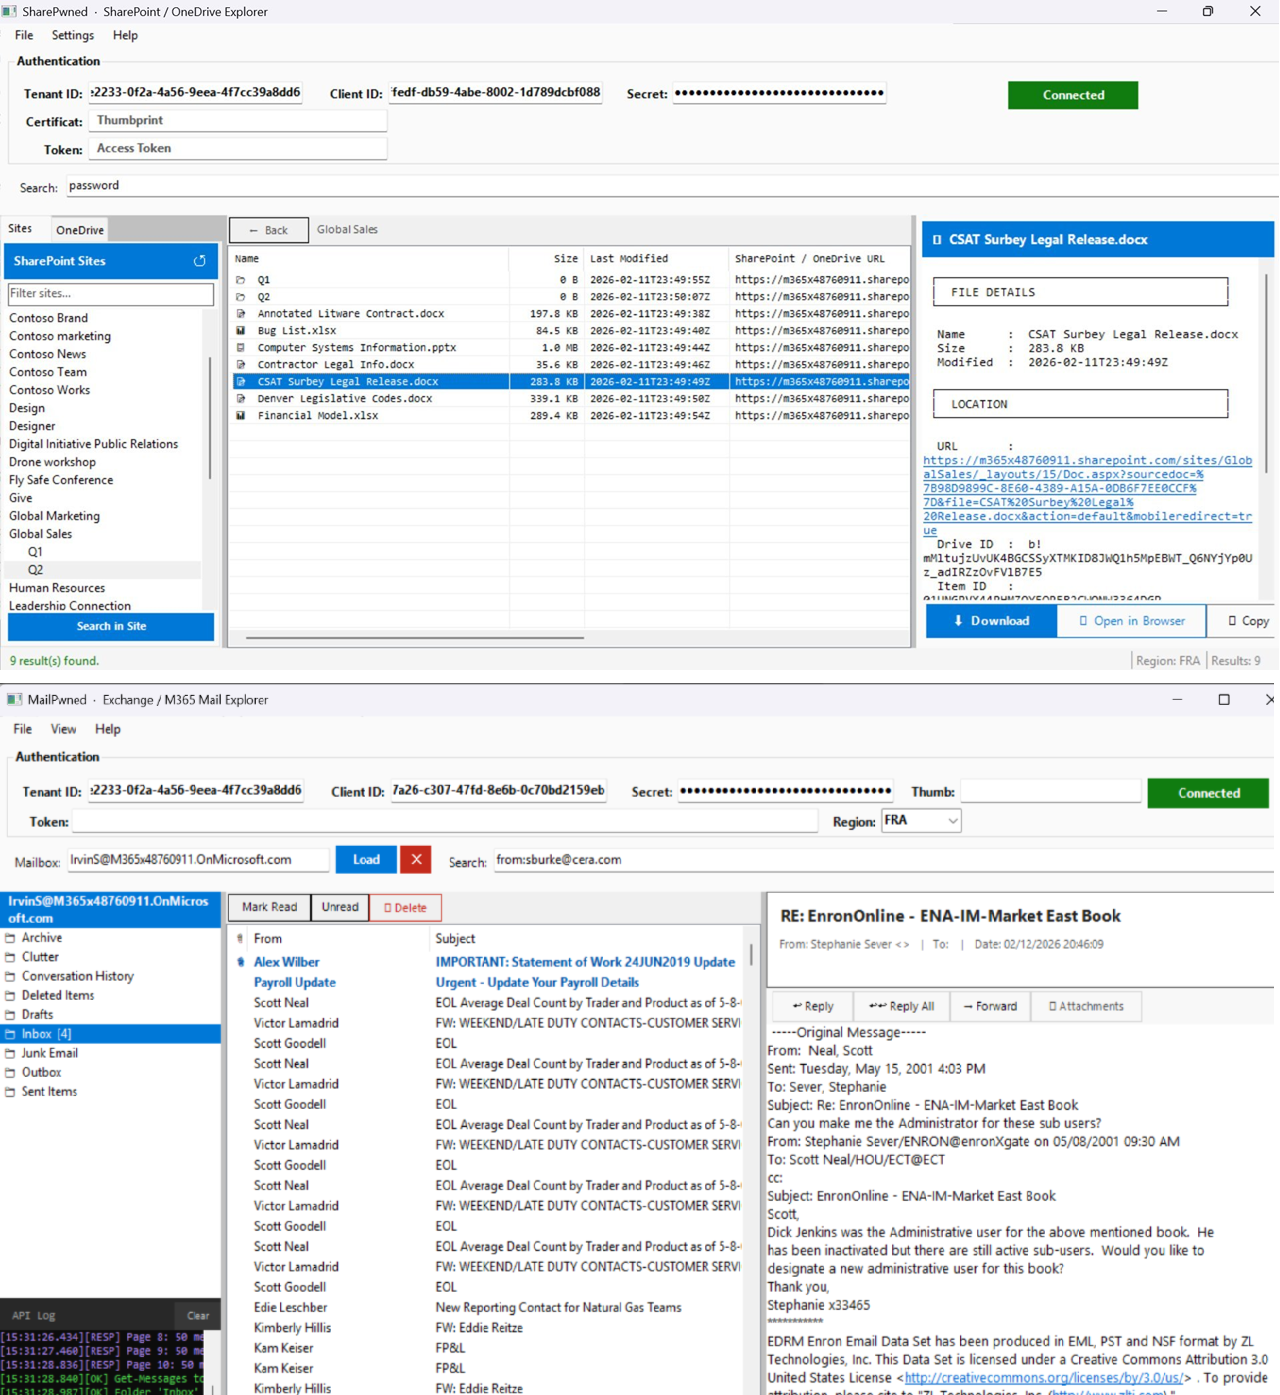 otterhacker/m365pwned
Two WinForms GUI tools for enumerating, searching, and exfiltrating data from M365 environments using application-level OAuth tokens
 dedsecteam-blackhat/cve-2025-68860
Exploit script for CVE-2025-68860 targeting WordPress Mobile Builder plugin. Generates forged JWT tokens using a hardcoded secret to authenticate as…
 fevra-dev/claimjumper
Professional JWT security testing toolkit. Analyze, crack, forge, and exploit JSON Web Tokens with 15+ vulnerability checks, 100k secret wordlist,…
 comerc/cve-2025-68664
Detailed disclosure of CVE-2025-68664, a critical deserialization vulnerability in LangChain core allowing secret exfiltration and potential RCE via…