
CVE-2026-104110
 pervinzahidli/cve-2026-104110
Unauthenticated disclosure of internal folder path, client email, and upload policy for FileRise Pro client portals via /api/pro/portals/get.php
api-securityauthenticationexploitation+5
pervinzahidli/cve-2026-104110Unauthenticated disclosure of internal folder path, client email, and upload policy for FileRise Pro client portals via /api/pro/portals/get.php
 thoropass-public/area51
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 romain-deperne/cve-2026-33715
Proof-of-concept exploit for unauthenticated SSRF and open email relay in Chamilo LMS via install.ajax.php, allowing internal network probing and…
 sam00/poc-cve-2026-54121-certighost
Exploit toolkit for AD CS CVE-2026-54121: low-privileged domain users impersonate a Domain Controller, forge certificates, and compromise the domain…
 blue-chocolates/cve-2016-10033
Exploit for CVE-2016-10033, a remote code execution vulnerability in PHPMailer, enabling unauthenticated attackers to execute arbitrary code via…
 shinthink/cve-2026-54390
CVE-2026-54390 — JTL Shop Smarty SSTI RCE | Pre-Auth Template Injection via fetch('string:' . ) | 5.2.0-5.7.1
 0x00phantom-hat/cve-2026-12400-exploit
Authenticated WordPress IDOR exploit for CVE-2026-12400; enumerates FlowForms REST form IDs and modifies form content or hijacks email notifications.
 jeanback1/cve-2019-9053-exploit
Automated exploit for CVE-2019-9053, a time-based blind SQL injection in CMS Made Simple ≤2.2.9. Extracts admin credentials (username, email,…
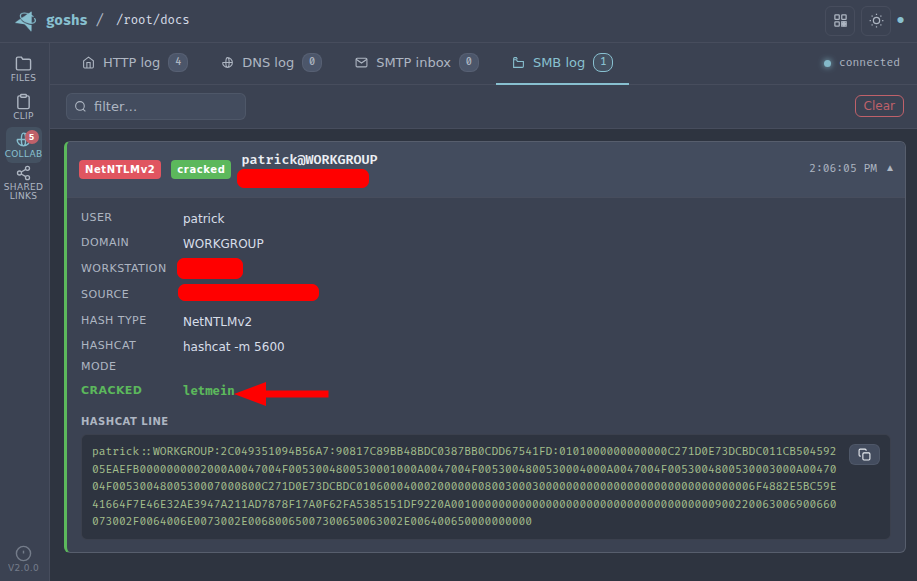 a-poc/redteam-tools
Tools and Techniques for Red Team / Penetration Testing
 safebreach-labs/eventlogin-cve-2025-29969
Exploitation of CVE-2025-29969
 thewoodenbench/cve-2025-66956
Insecure Access Control in Contact Plan, E-Mail, SMS and Fax components in Asseco SEE Live 2.0 allows remote attackers to access and execute…
 randomrobbiebf/cve-2024-0368
Hustle Plugin <= 7.8.3 contains hardcoded HubSpot API credentials in inc/providers/hubspot/hustle-hubspot-api.php
 redpack-kr/blackash-cve-2025-20393
CVE-2025-20393
 cyberleelawat/cve-2025-20393
Cisco is aware of a potential vulnerability. Cisco is currently investigating and will update these details as appropriate as more…
 thewoodenbench/cve-2025-66955
Local File Inclusion in Contact Plan, E-Mail, SMS and Fax components in Asseco SEE Live 2.0 allows remote authenticated users to access files on the…
 7h30th3r0n3/cve-2025-51586-prestashop-poc
PrestaShop AdminLogin Email Enumeration PoC - CVE-2025-51586. This repository provides an ethical Proof-of-Concept (PoC) for the PrestaShop…
 randomrobbiebf/cve-2025-8422
Propovoice <= 1.7.6.7 - Unauthenticated Arbitrary File Read
 dthkhang/cve-2023-5561-poc
PoC exploit for CVE-2023-5561 that enumerates WordPress user email addresses via the /wp-json/wp/v2/users API endpoint. For authorized security…