

NetExec
 pennyw0rth/netexec
Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…
command-and-controldatabase-securityexploitation+14
6.0k
pennyw0rth/netexecPost-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…
 tc4dy/cve-2026-41940-poc-exploit
PoC exploit for CVE-2026-41940 targeting cPanel/WHM authentication bypass via CRLF injection. Supports session hijacking, RCE, reverse shell, mass…
 tc4dy/cve-2026-6875-poc-exploit
CVE-2026-6875 ServiceNow Pre-Auth RCE Framework 🔥 JS Injection → Sandbox Escape → RCE → Root. Features: --detect, --exec, reverse/interactive shell,…
 adfortunato/metasploitable3-pentest-writeup
Home-lab penetration test report of Metasploitable3 covering Nmap recon, Drupalgeddon RCE, SQL injection, SSH credential reuse, sudo privilege…
 principlecheck/kslkatzbof
Beacon Object File for in-line LSASS credential extraction using the KslD.sys BYOVD technique. Extracts NT hashes and cleartext passwords from…
 aramosf/cve-2026-24031
Self-contained Python PoC for Dovecot SQL authentication bypass: logs in as any user without the real password and enumerates usernames on vulnerable…
 cerberusmrxi/cve-2025-48932-invision-community-sqli-exploit
CVE-2025-48932 - Unauthenticated SQL injection exploit for Invision Community ≤ 4.7.20. Fully automated exploitation with database enumeration,…
 cerberusmrxi/cpanel-whm-cve-2026-41940-auth-bypass-exploit
Critical authentication bypass exploit for cPanel/WHM CVE-2026-41940. Leverages CRLF injection in cpsrvd daemon to gain root WHM access without…
 michaeladamgroberman/cve-2026-13768
CVE-2026-13768: Privileged iothubowner IoT Hub credential — fleet enumeration, device RCE, home-network pivot — Gardyn (ICSA-26-183-03)
 0xdak/cve-2026-44881_exploit
Single-script exploit for CVE-2026-44881 that chains .git credential leakage, Portainer Git-symlink injection, arbitrary host file read, and SSH…
 coolkiee/cve-2019-9053
Python exploit for CVE-2019-9053 targeting SQL injection in CMS Made Simple, enabling automated time-based blind injection and credential extraction.
 zycoder0day/cve-2026-5076
Proof-of-concept exploit for CVE-2026-5076 demonstrating unauthenticated admin account takeover in ARMember Premium via SQL injection and plaintext…
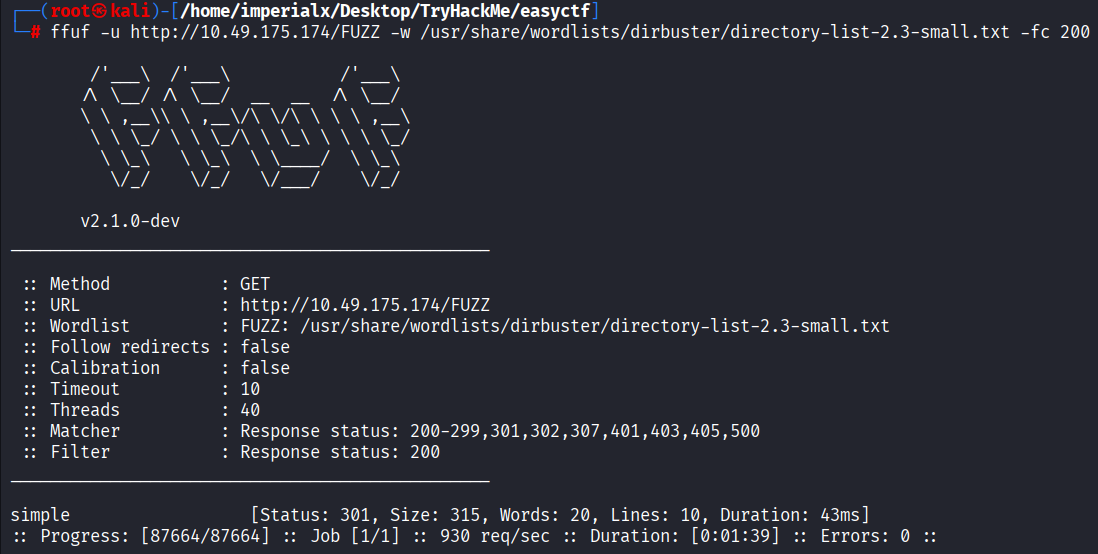 imperialx1104/simple-ctf-writeup
Professional TryHackMe Simple CTF walkthrough covering enumeration, CMS Made Simple SQL Injection (CVE-2019-9053), credential recovery, SSH access,…
 sardine-web/automated-scanner-cve-2026-41940
Automated scanner & post-exploitation toolkit for CVE-2026-41940 — cPanel & WHM root authentication bypass via session-file CRLF injection
 anach-ai/cve-2026-41940
CVE-2026-41940 — cPanel/WHM Auth Bypass By Dr.Anach, CRLF injection in `cpsrvd` Basic auth handler → unauthenticated WHM API access → RCE as root.…
 themalwareguardian/cve-2018-14847
Analysis and PoC for CVE-2018-14847, MikroTik RouterOS Winbox information disclosure vulnerability allowing unauthenticated read access to the…
 mr-redoo7/cve-2026-27739-poc
Python PoC exploiting CVE-2026-27739 in Angular SSR: header injection via prototype pollution and SSRF chaining to AWS IMDS/GCP metadata for…
 b0b0haha/cve-2026-29954
Proof-of-concept demonstrating SSRF and HTTP header injection in KubePlus ResourceComposition, enabling cloud metadata access and IAM credential…