CnaEmulator
 iterat0r/cnaemulator
Standalone emulation and testing harness for Cobalt Strike Aggressor Scripts (.cna) that validates syntax, mocks Beacon APIs, and executes BOFs via…
command-and-controldynamic-analysis-sandboxingeducation+7
22
iterat0r/cnaemulatorStandalone emulation and testing harness for Cobalt Strike Aggressor Scripts (.cna) that validates syntax, mocks Beacon APIs, and executes BOFs via…

 immunityinc/libptrace
An event driven multi-core process debugging, tracing, and manipulation framework.
 thisistfs/rogue-framework
Desktop workbench for AFL++ fuzzing, cross-architecture QEMU emulation, harness development, Ghidra headless analysis, custom mutators, and patch…
 miscusi-peek/cheatengine-mcp-bridge
Connect your favorite AI agents directly to Cheat Engine via MCP. Automate reverse engineering, pointer scanning, and memory analysis using natural…
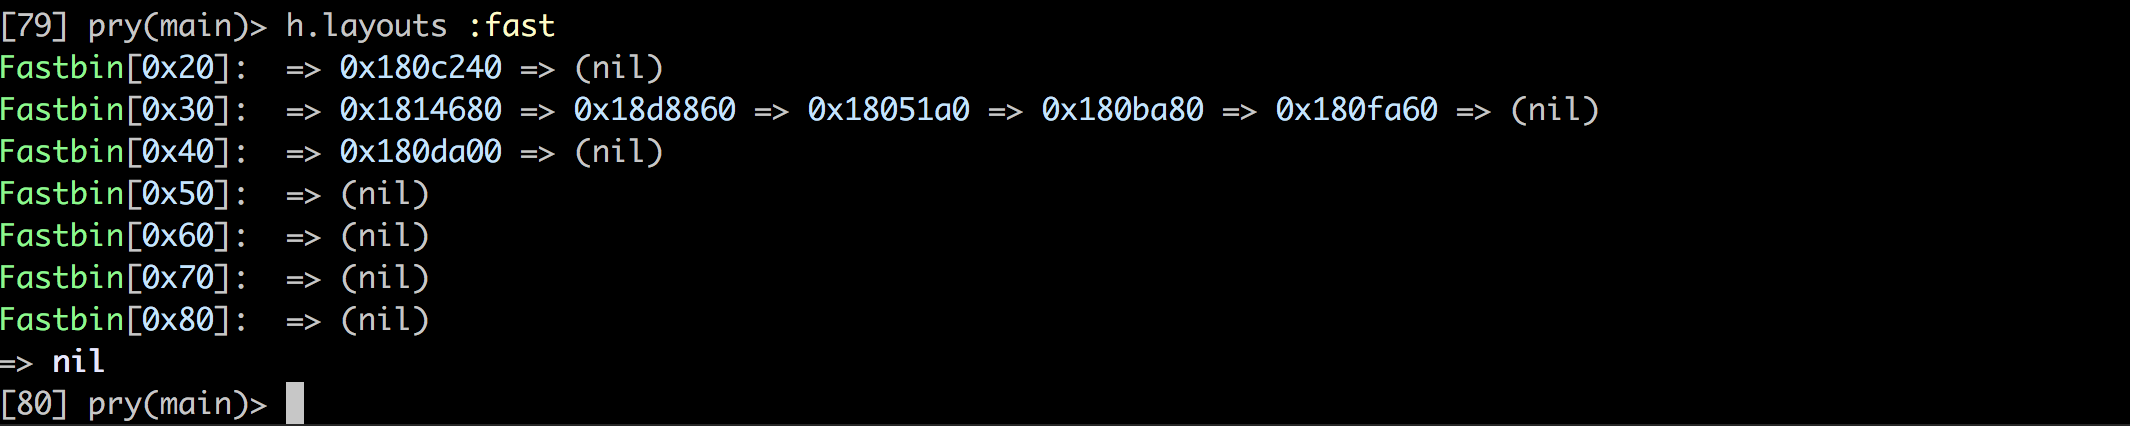 david942j/heapinfo
An interactive memory info for pwning / exploiting
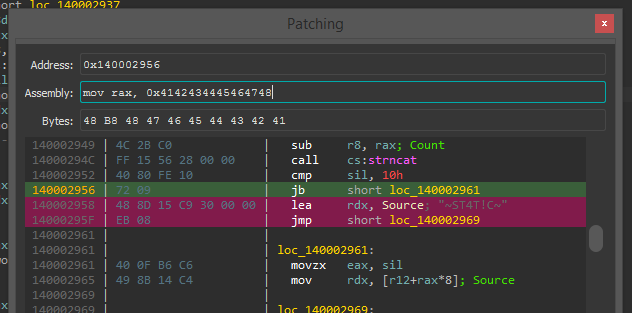 gaasedelen/patching
An Interactive Binary Patching Plugin for IDA Pro
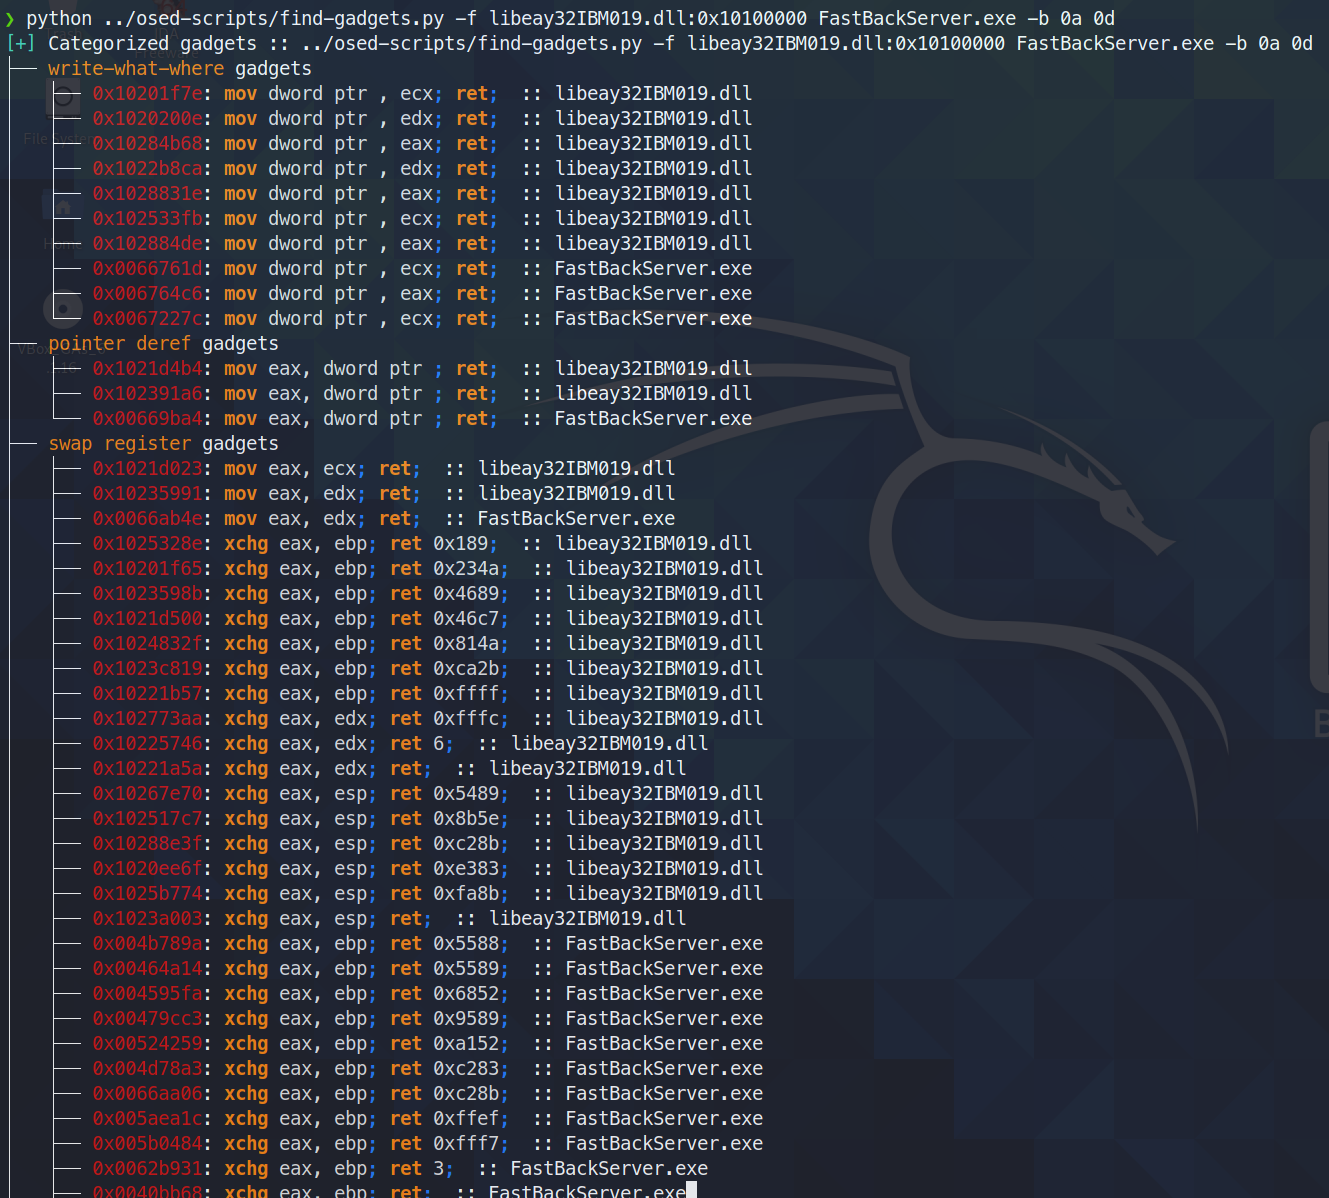 epi052/osed-scripts
bespoke tooling for offensive security's Windows Usermode Exploit Dev course (OSED)
 therealdreg/shellex
C-shellcode to hex converter, handy tool for paste & execute shellcodes in IDA PRO, gdb, windbg, radare2, ollydbg, x64dbg, immunity debugger & 010…
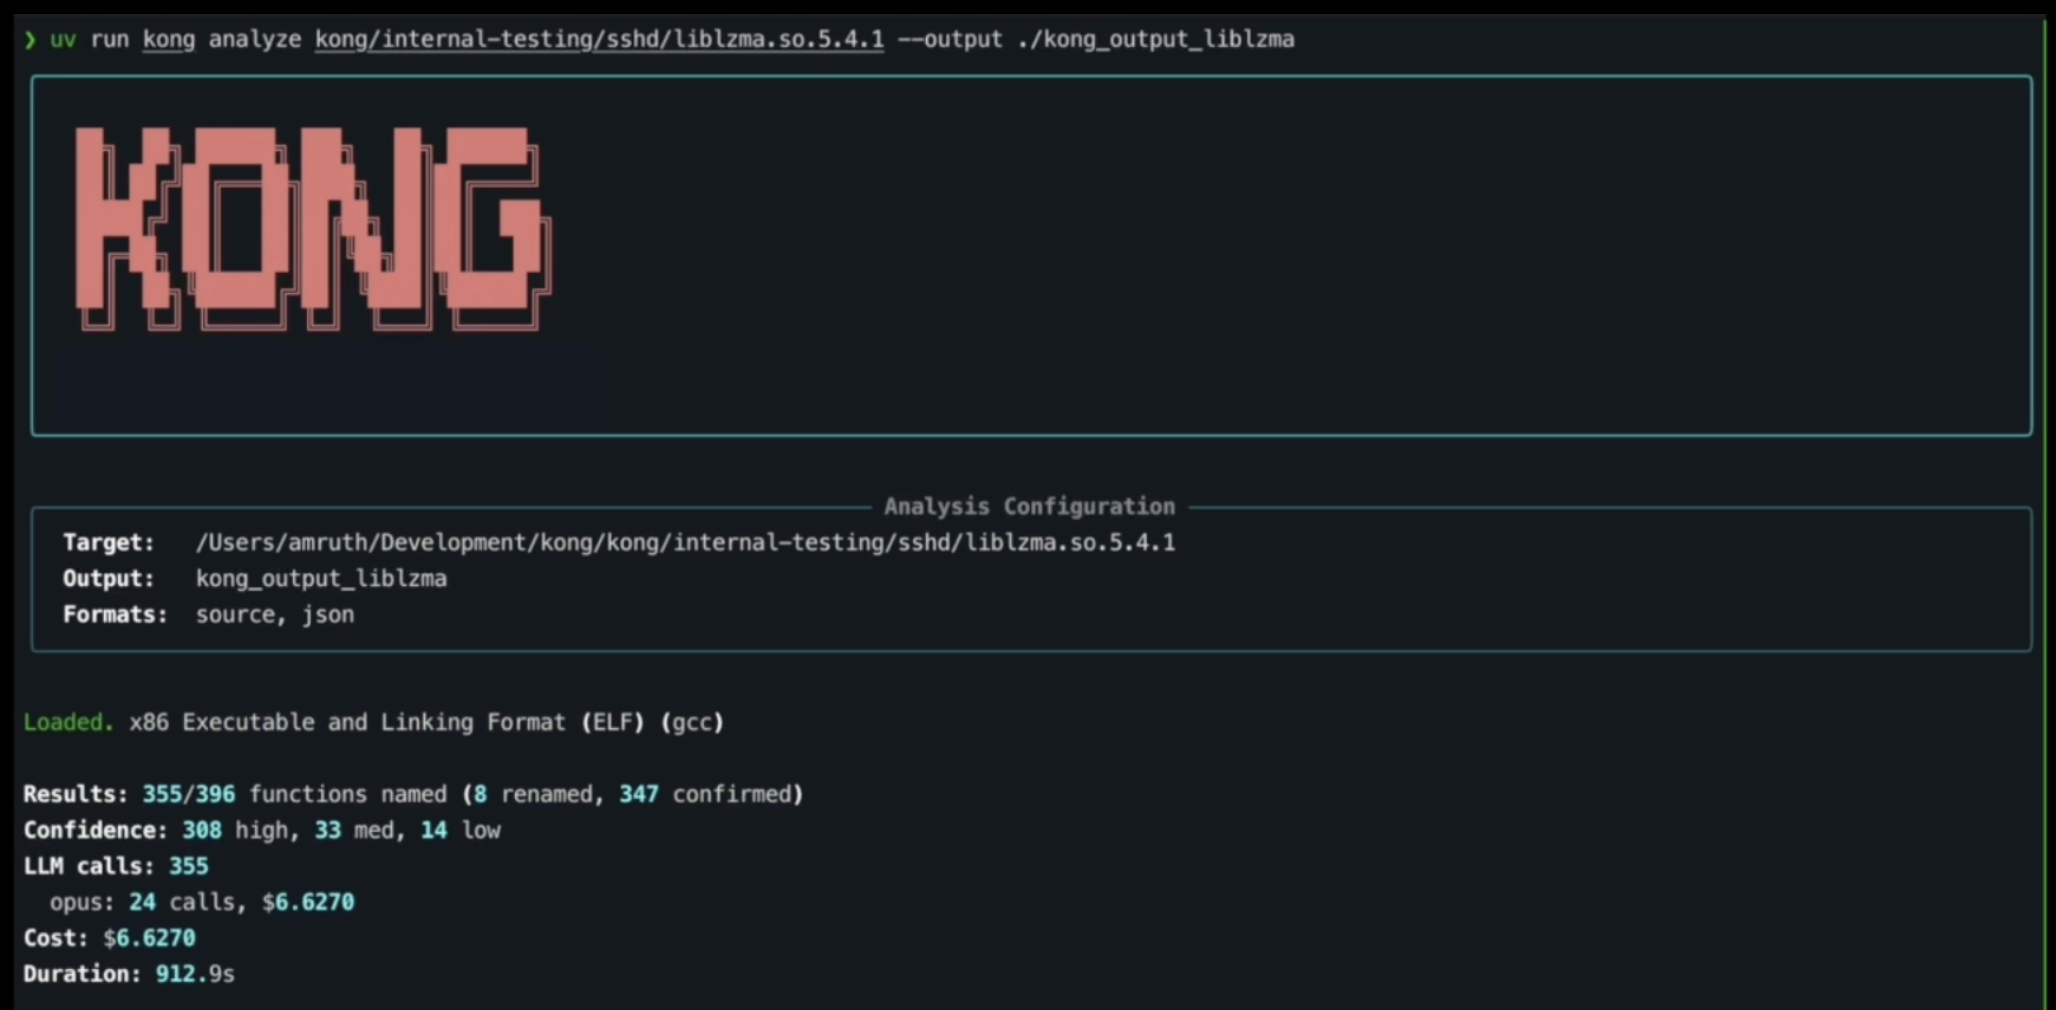 amruth-sn/kong
The world's first agentic reverse engineer.
 rizlmaulanaa/cve-2026-23479-redis-uaf-proof-of-concept
Proof of concept with GDB‑assisted exploitation (educational / lab use only)
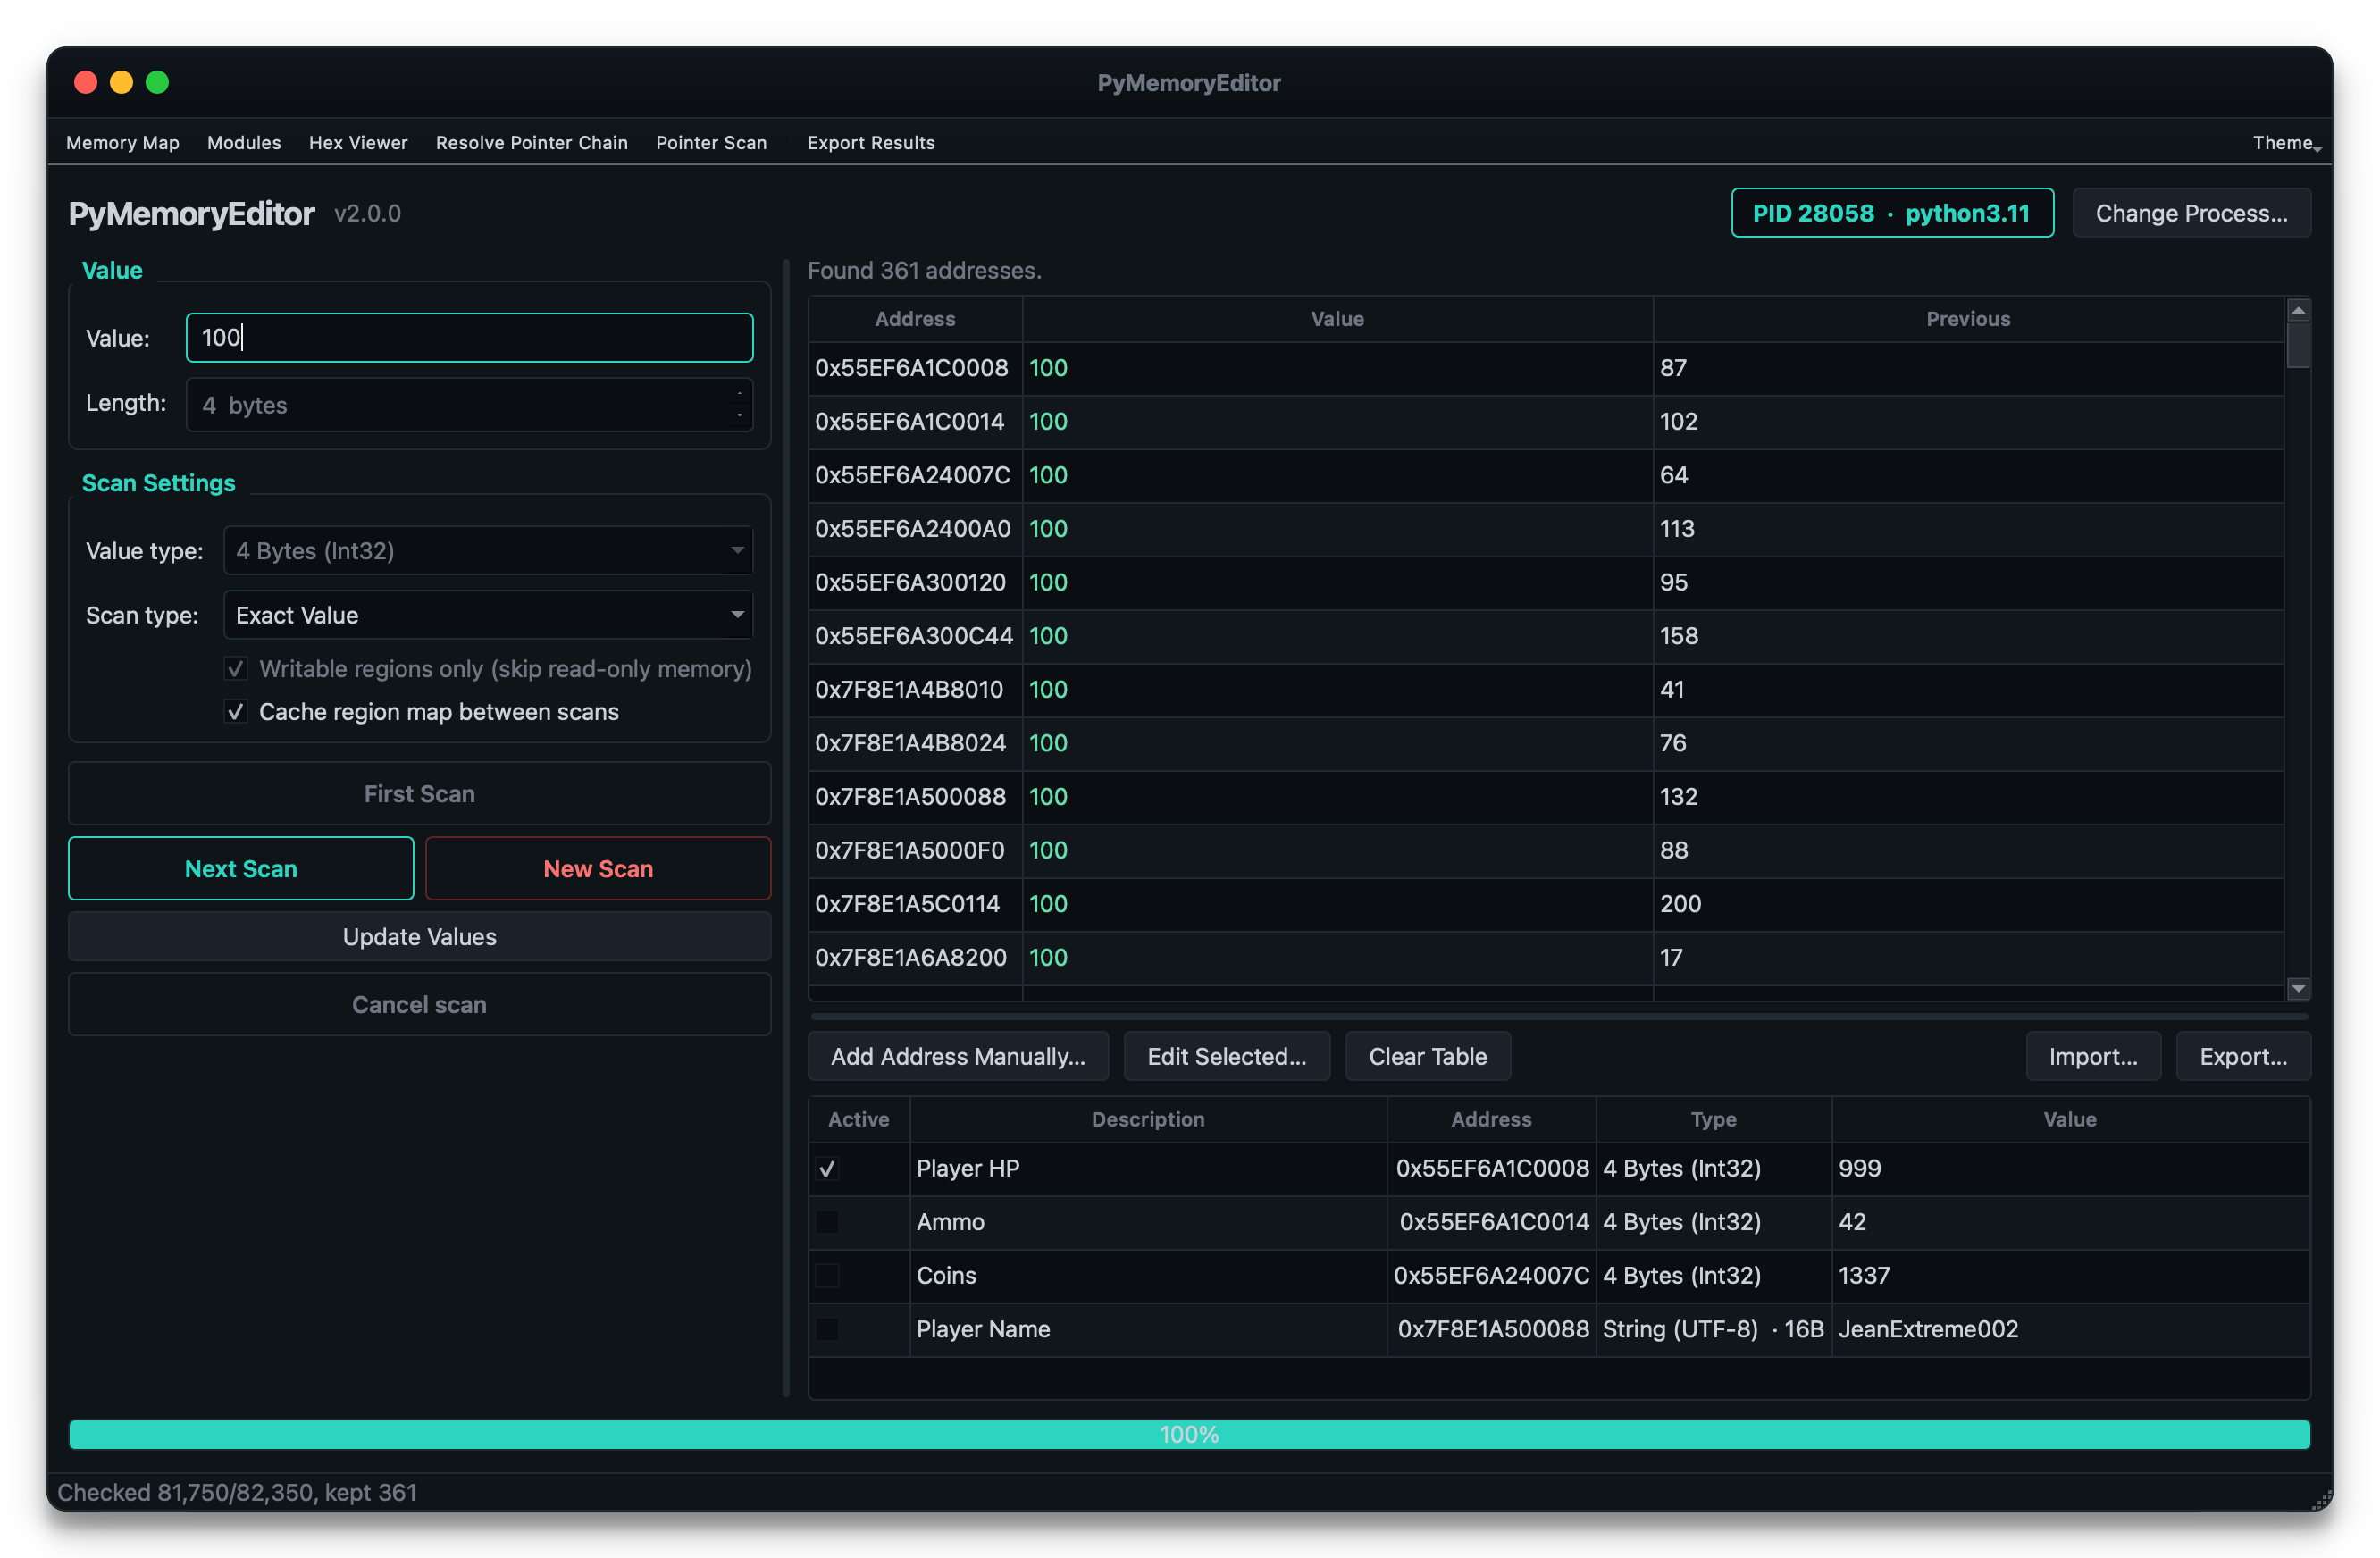 jeanextreme002/pymemoryeditor
A pure-Python library, app and MCP that lets you inspect, modify and search the memory of any running process in a few lines of Python :snake: .
 canomer/cve-2026-36981-kernel-eop-poc
Project Date : Feb 2026 / Memory corruption vulnerability within the kernel driver of MiniTool. Demonstrates a debugger-assisted arbitrary kernel…
 owenpawl/cerberus-re-skill
cerberus-re is a local Apple-focused reverse-engineering workbench for building a repeatable three-headed static/dynamic/instrumentation loop around…
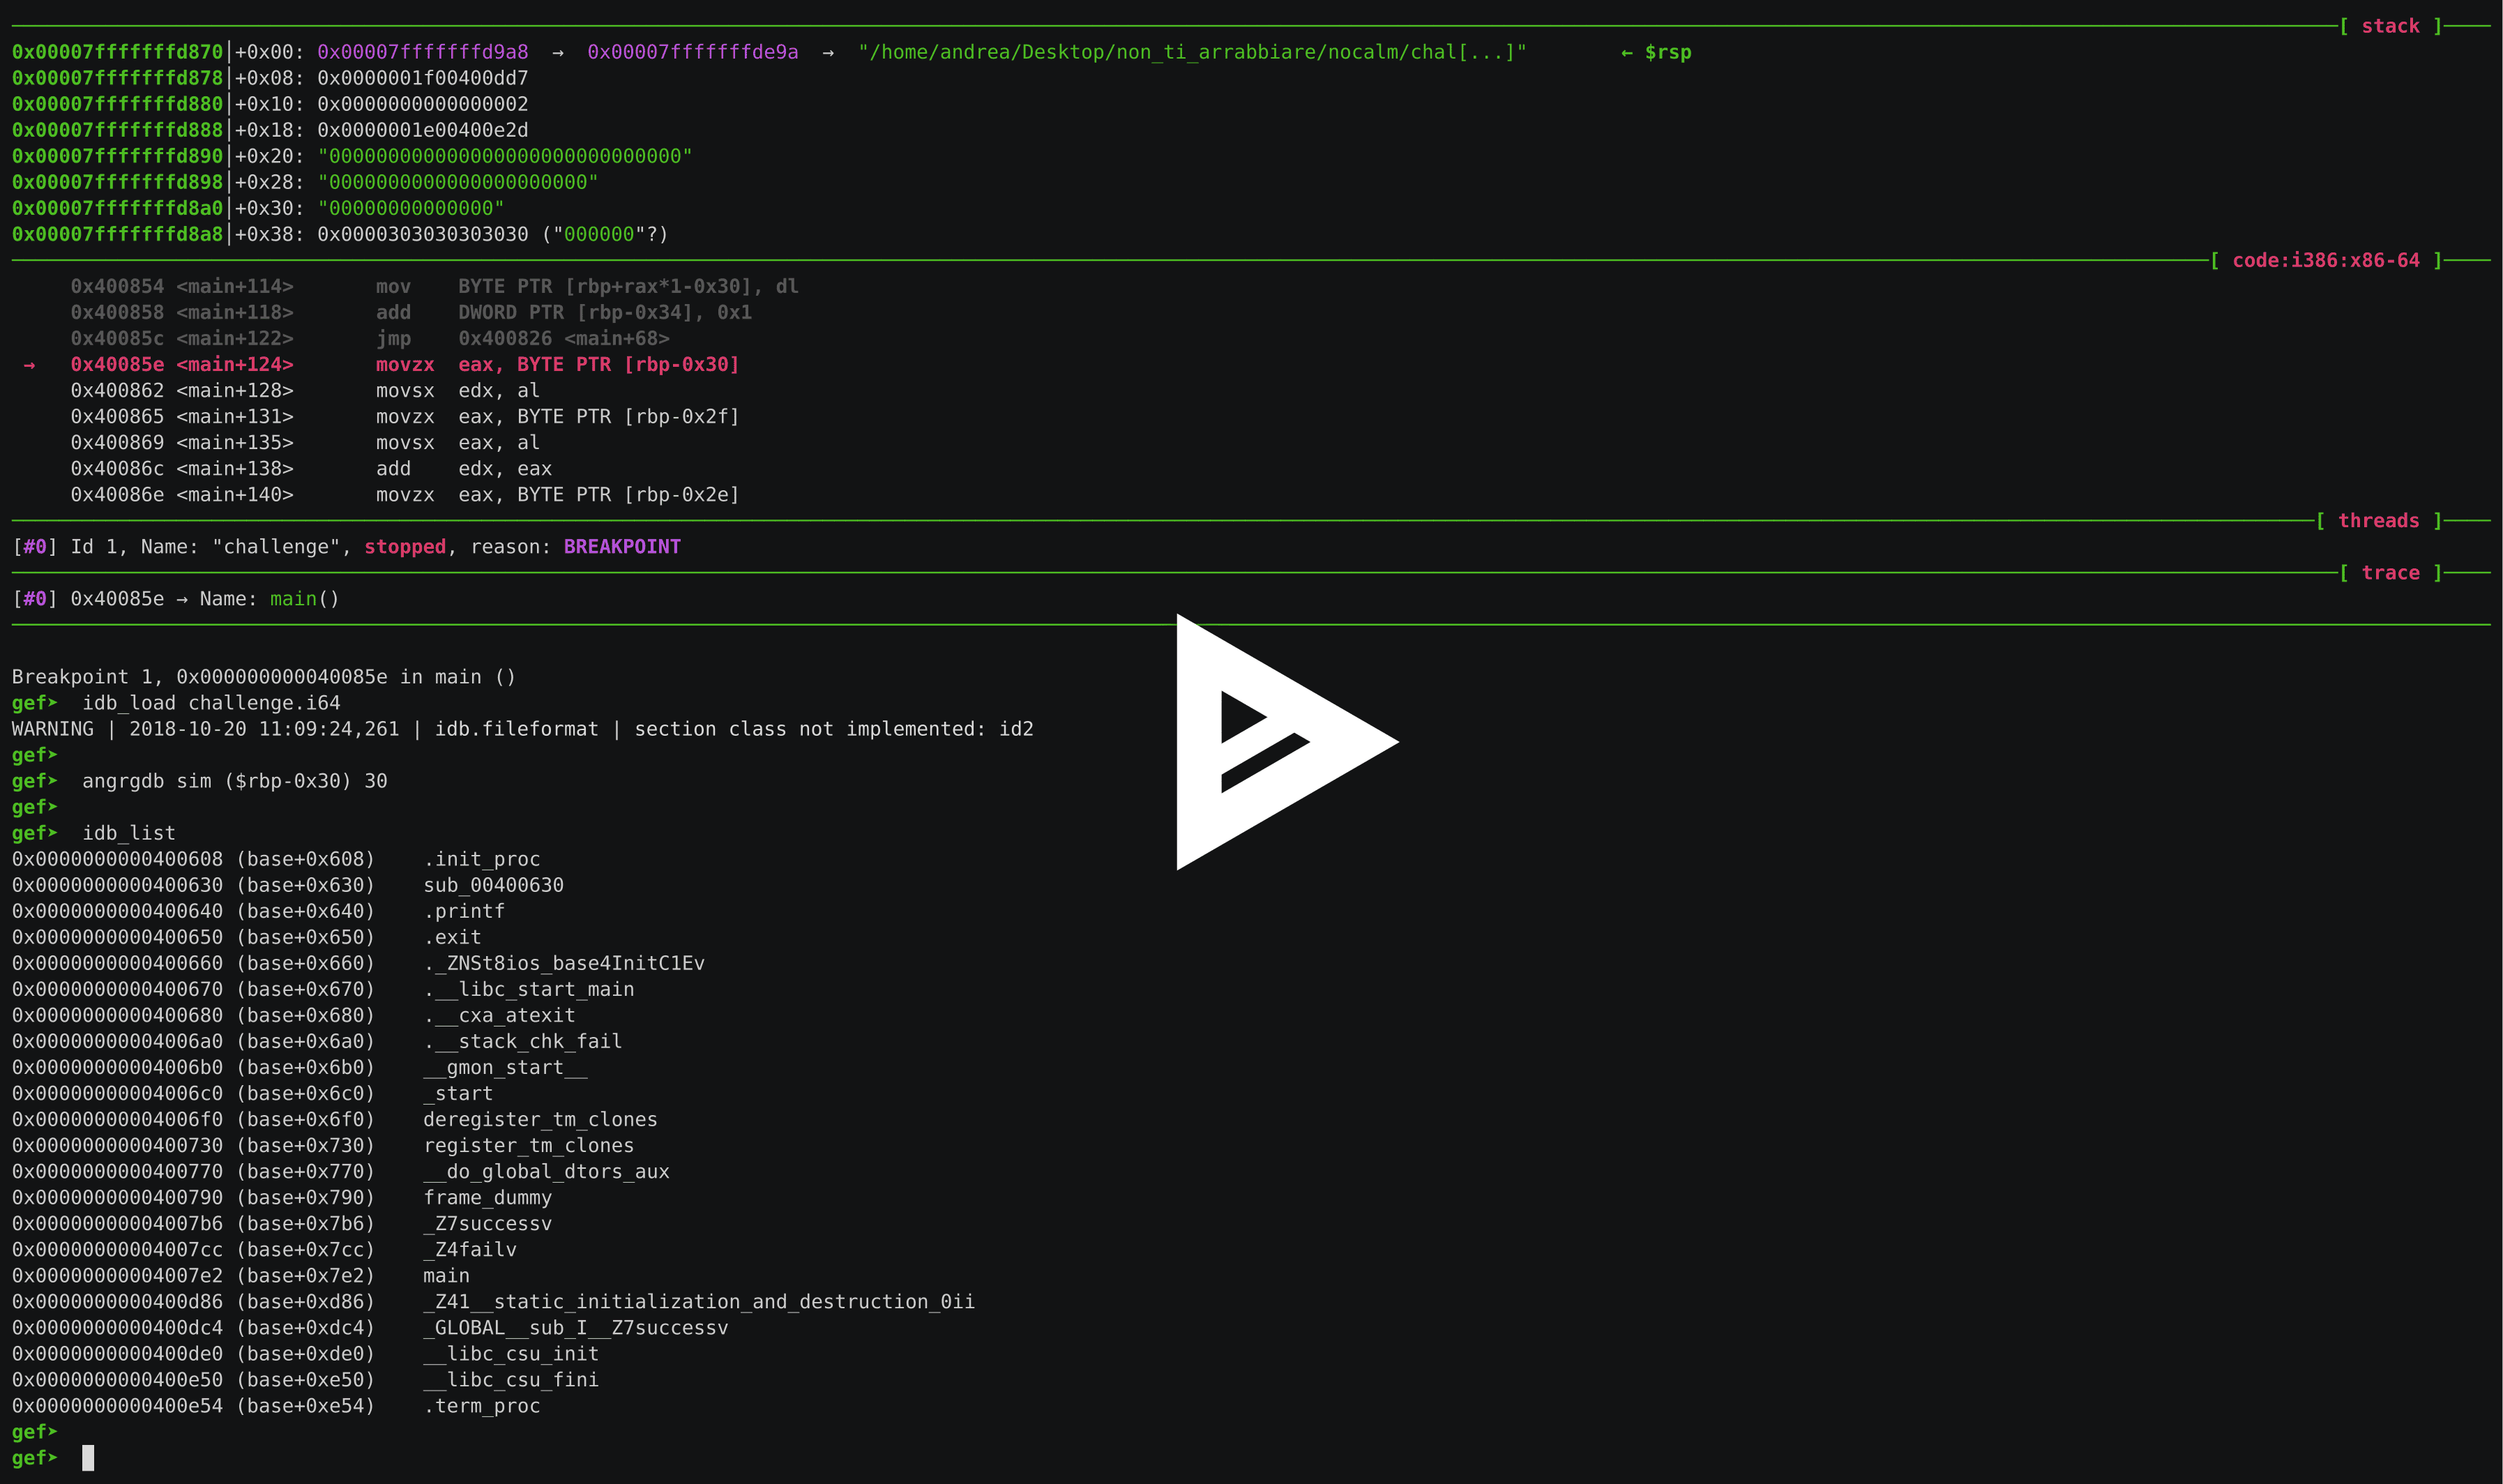 andreafioraldi/angrgdb
Use angr inside GDB. Create an angr state from the current debugger state.
 dinosn/fastjson-jsontype-rce-lab
Docker labs + defensive scanner for fastjson remote-class-load RCE. fastjson 1.2.66-1.2.83: @JSONType resource probe (CVE-2026-16723). fastjson2…
 helgesverre/livewire-honeypot
High-interaction honeypot mimicking a vulnerable Laravel/Livewire app. Captures RCE exploits and webshells targeting CVE-2024-47823, CVE-2025-54068,…