
cve-2017-5638
 jrrdev/cve-2017-5638
Docker-based vulnerable environment and Python exploit script demonstrating CVE-2017-5638 (Apache Struts2 RCE) for educational security testing.
educationexploitationpenetration-testing+2
14
jrrdev/cve-2017-5638Docker-based vulnerable environment and Python exploit script demonstrating CVE-2017-5638 (Apache Struts2 RCE) for educational security testing.
 k9-modz/cve-2023-38873-g1
Proof-of-concept demonstrating a Clickjacking vulnerability on the G1 website, with a malicious iframe overlay and social engineering popup for…
 nxploited/cve-2025-39601
WordPress Custom CSS, JS & PHP plugin <= 2.4.1 - CSRF to RCE vulnerability
 ravi-lk/cve-2026-10104-poc
Product Video Gallery for Woocommerce <= 1.5.1.8 - Authenticated Stored Cross-Site Scripting Proof of Concept
 menevarad007/cve-2026-37750
Reflected XSS proof-of-concept for School Management System 1.0, demonstrating unauthenticated JavaScript execution via the type parameter in…
 minhhk68/cve-2026-13156
CVE-2026-13156 Vulnerability Advisory & PoC — Discovered by Huynh Kien Minh (MinhHK).
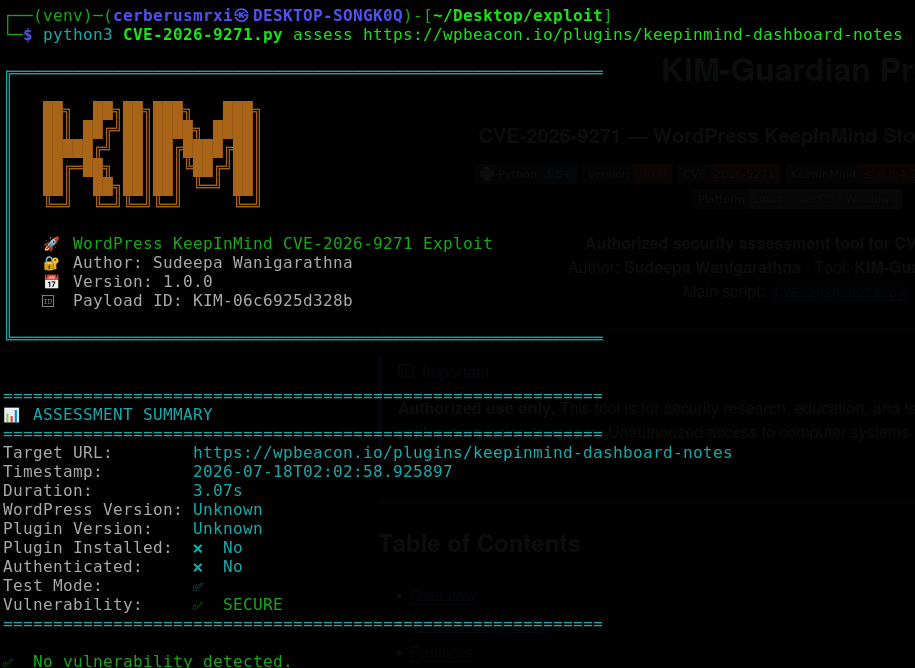 cerberusmrxi/wordpress-keepinmind-cve-2026-9271-exploit
Authorized stored XSS assessment tool for CVE-2026-9271 in WordPress KeepInMind plugin. Detects vulnerable versions, injects safe test payloads, and…
 joaovicdev/exploit-cve-2026-63030
Docker-based vulnerable WordPress lab with Python exploit demonstrating pre-auth route confusion and SQL injection chain (CVE-2026-63030 +…
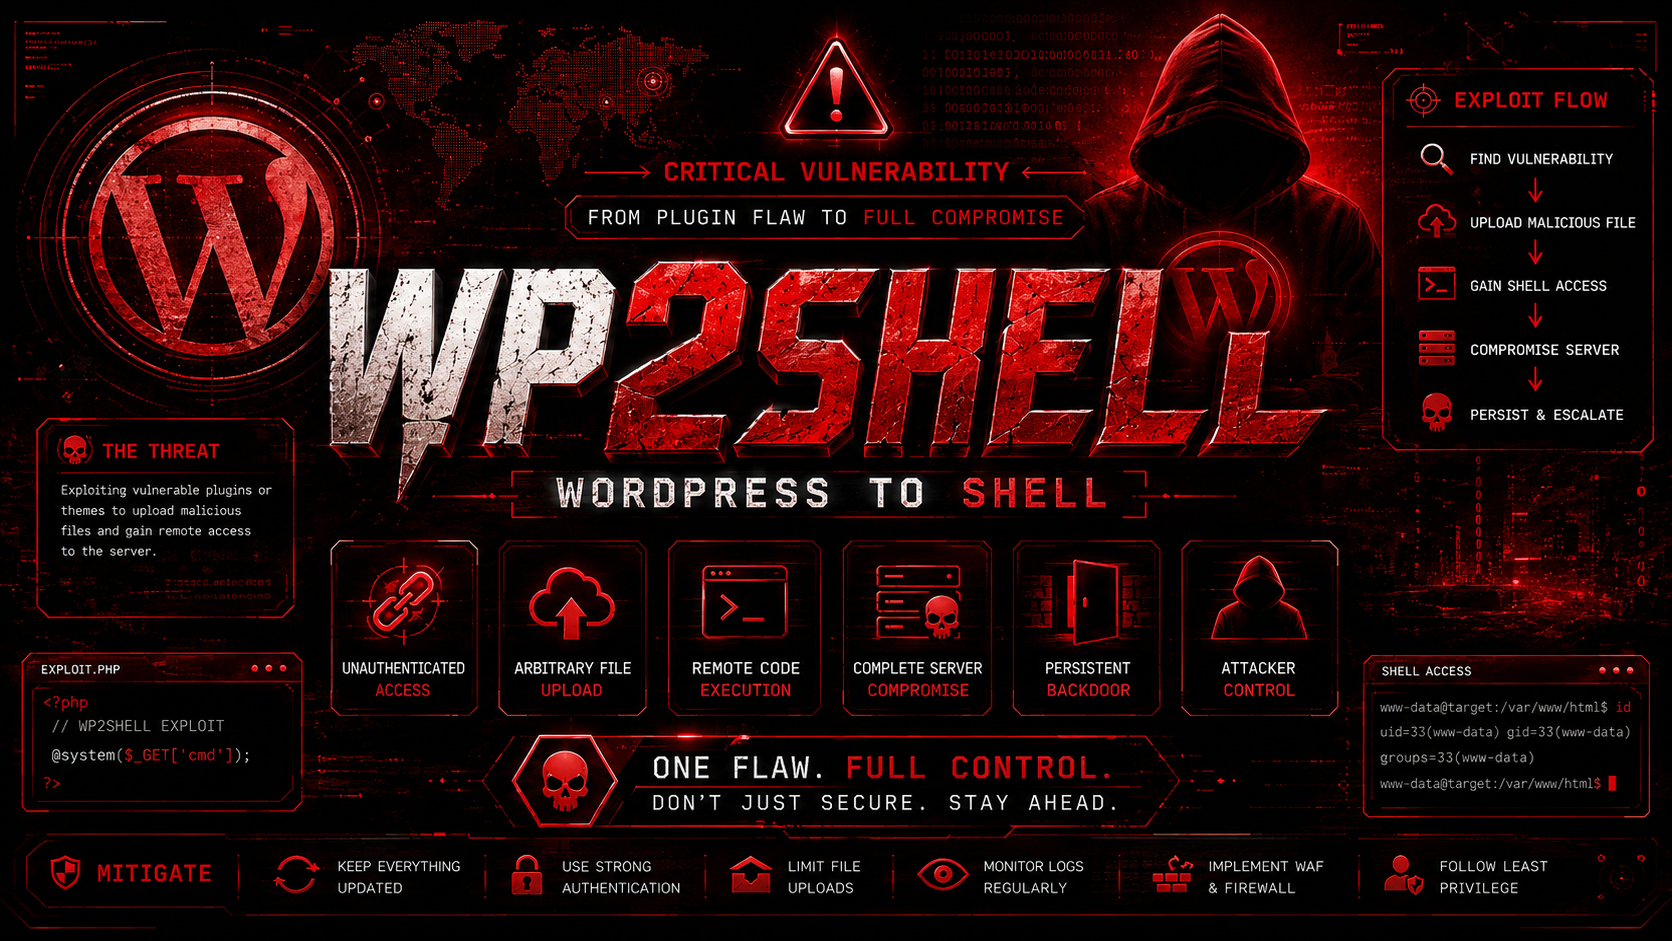 lucifer0xf/wp2shell-wordpress-town
Unauthenticated Remote Code Execution (RCE) in WordPress Core allows attackers to execute arbitrary code without logging in by chaining…
 anandjogawade/cve-2026-48849-roundcube-webmail-stored-xss
This repository documents CVE-2026-48849, a Stored Cross-Site Scripting (XSS), HTML Injection, and CSS Injection vulnerability discovered in…
 saku0512/cve-2026-9086-poc
CVE-2026-9086 proof-of-concept for Keycloak client URI validation bypass using mixed-case javascript: and data: XSS payloads, with Docker-based…
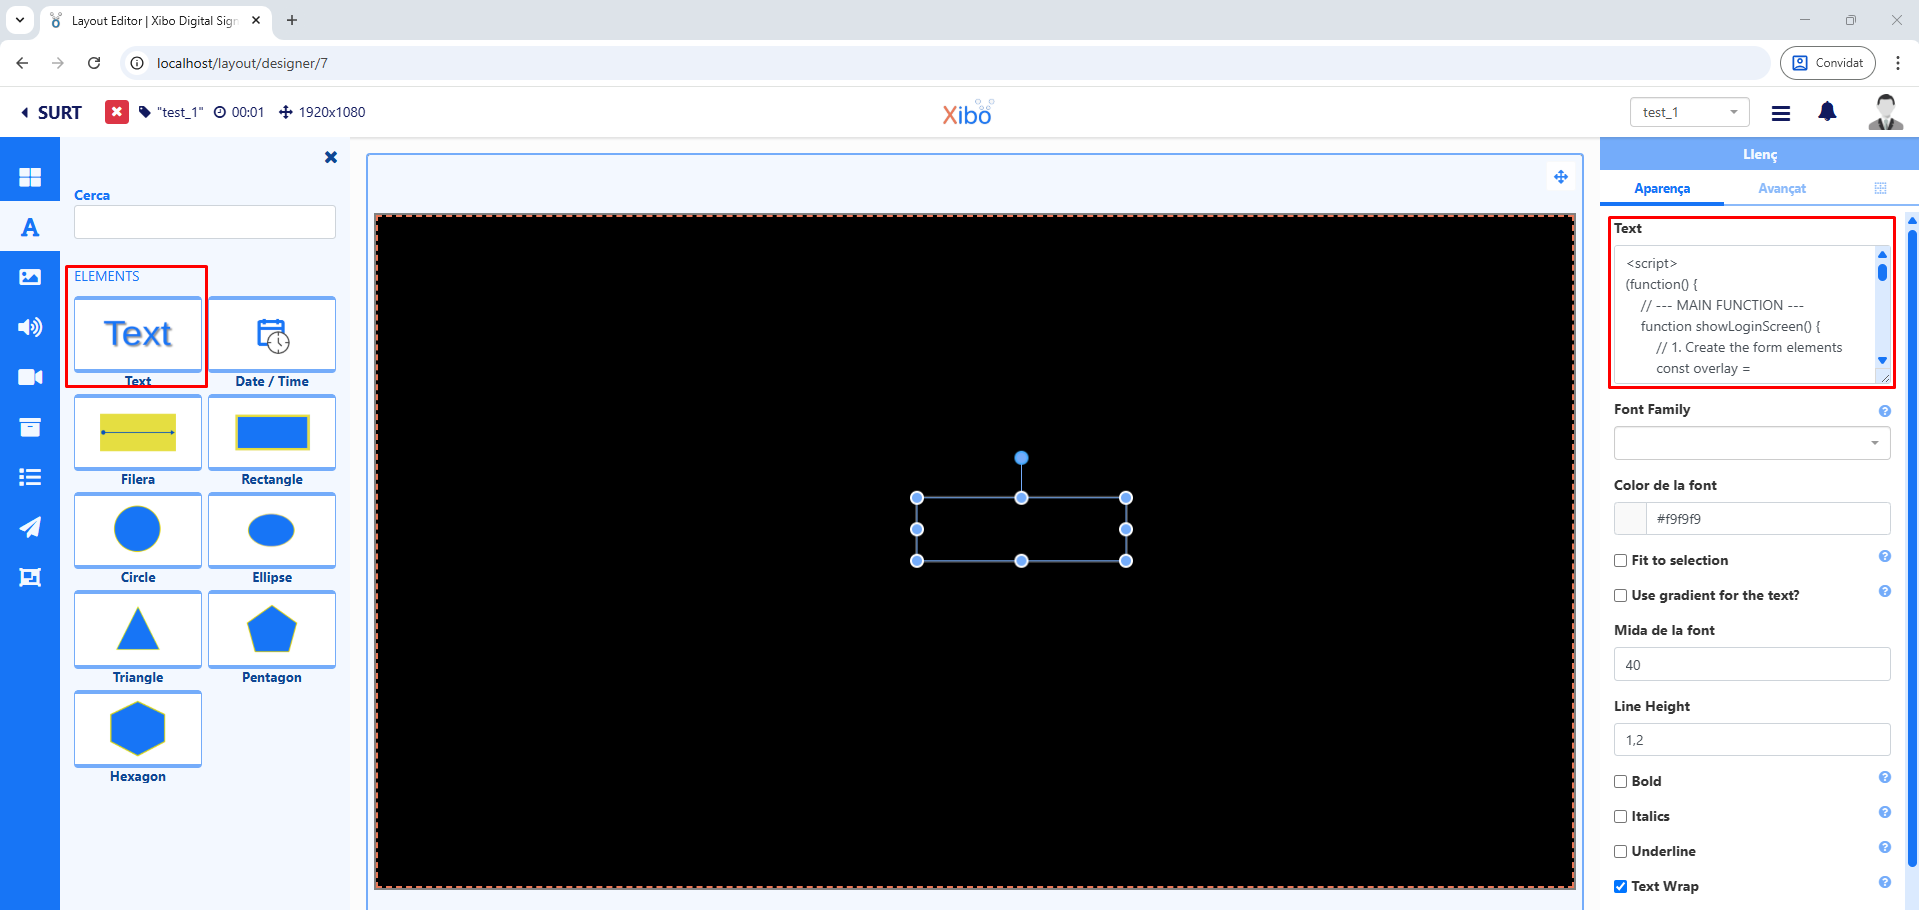 marinafabregat/cve-2025-41088
Stored Cross-Site Scripting (XSS) in Xibo Signage's Xibo CMS v4.1.2, due to a lack of proper validation of user input.
 diegomjx/cve-2023-41425-wondercms-authenticated-rce
Xss injection, WonderCMS 3.2.0 -3.4.2
 nxploited/cve-2025-25101
WordPress Munk Sites plugin <= 1.0.7 - CSRF to Arbitrary Plugin Installation vulnerability
 natsuki-engr/live-server-evil-crawler
Live Server VSCode Vulnerability (CVE-2025-65717) Demo