

SSTImap
 vladko312/sstimap
Automatic SSTI detection tool with interactive interface
code-analysiscommand-and-controldynamic-code-analysis+6
vladko312/sstimapAutomatic SSTI detection tool with interactive interface
 open-flaw/cve-2026-56848
Exploit PoC for CVE-2026-56848, a Node.js HTTP/2 heap-use-after-free that allows remote unauthenticated DoS. Includes raw-socket trigger, ASan build…
 ghostvectoracademy/dllhijackhunter
Automated DLL Hijacking Discovery, Validation, and Confirmation. Turning local misconfigurations into weaponized, confirmed attack paths.
 stealthcopter/wordpress-hacking
A collection of useful resources for hacking WordPress and it's plugins and themes
 robertdfrench/ifuncd-up
GNU IFUNC is the real culprit behind CVE-2024-3094
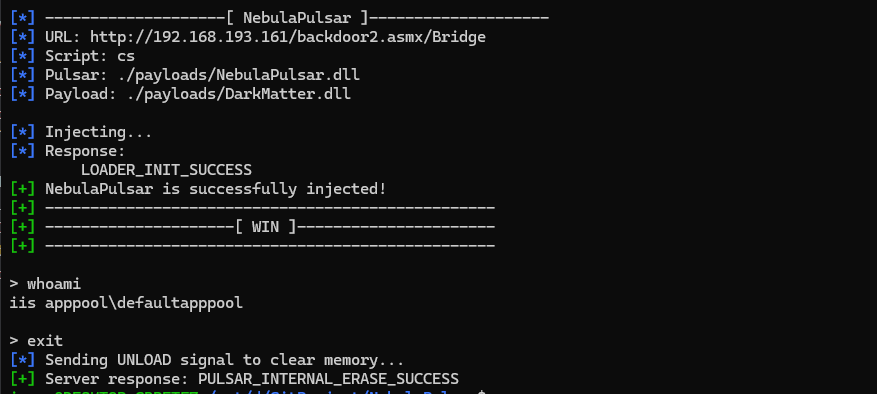 iss4cf0ng/nebulapulsar
NebulaPulsar is a proof-of-concept in-memory implant framework for Java (JSP) and ASP.NET (ASPX/ASHX/ASMX) webshells, originally developed as part of…
 zhzyker/vulmap
Web vulnerability scanner and exploitation tool with POC/EXP modes for known CVEs across webapps such as Weblogic, Shiro, Struts2, and Tomcat;…
 byt3bl33d3r/offensivedlr
Toolbox containing research notes & PoC code for weaponizing .NET's DLR
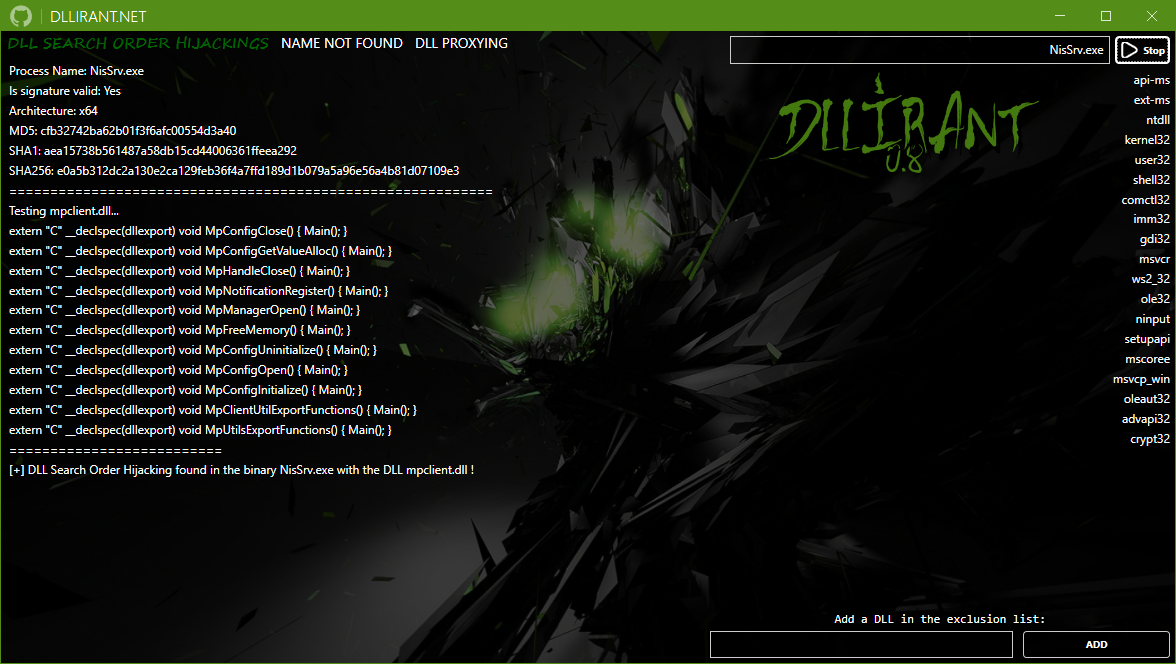 redteamsocietegenerale/dllirant
DLLirant is a tool to automatize the DLL Hijacking researches on a specified binary.
 google/path-auditor
Runtime libc function auditor that detects file access race conditions and symlink vulnerabilities by hooking filesystem syscalls via LD_PRELOAD,…
 cornerpirate/java-stager
A PoC Java Stager which can download, compile, and execute a Java file in memory.
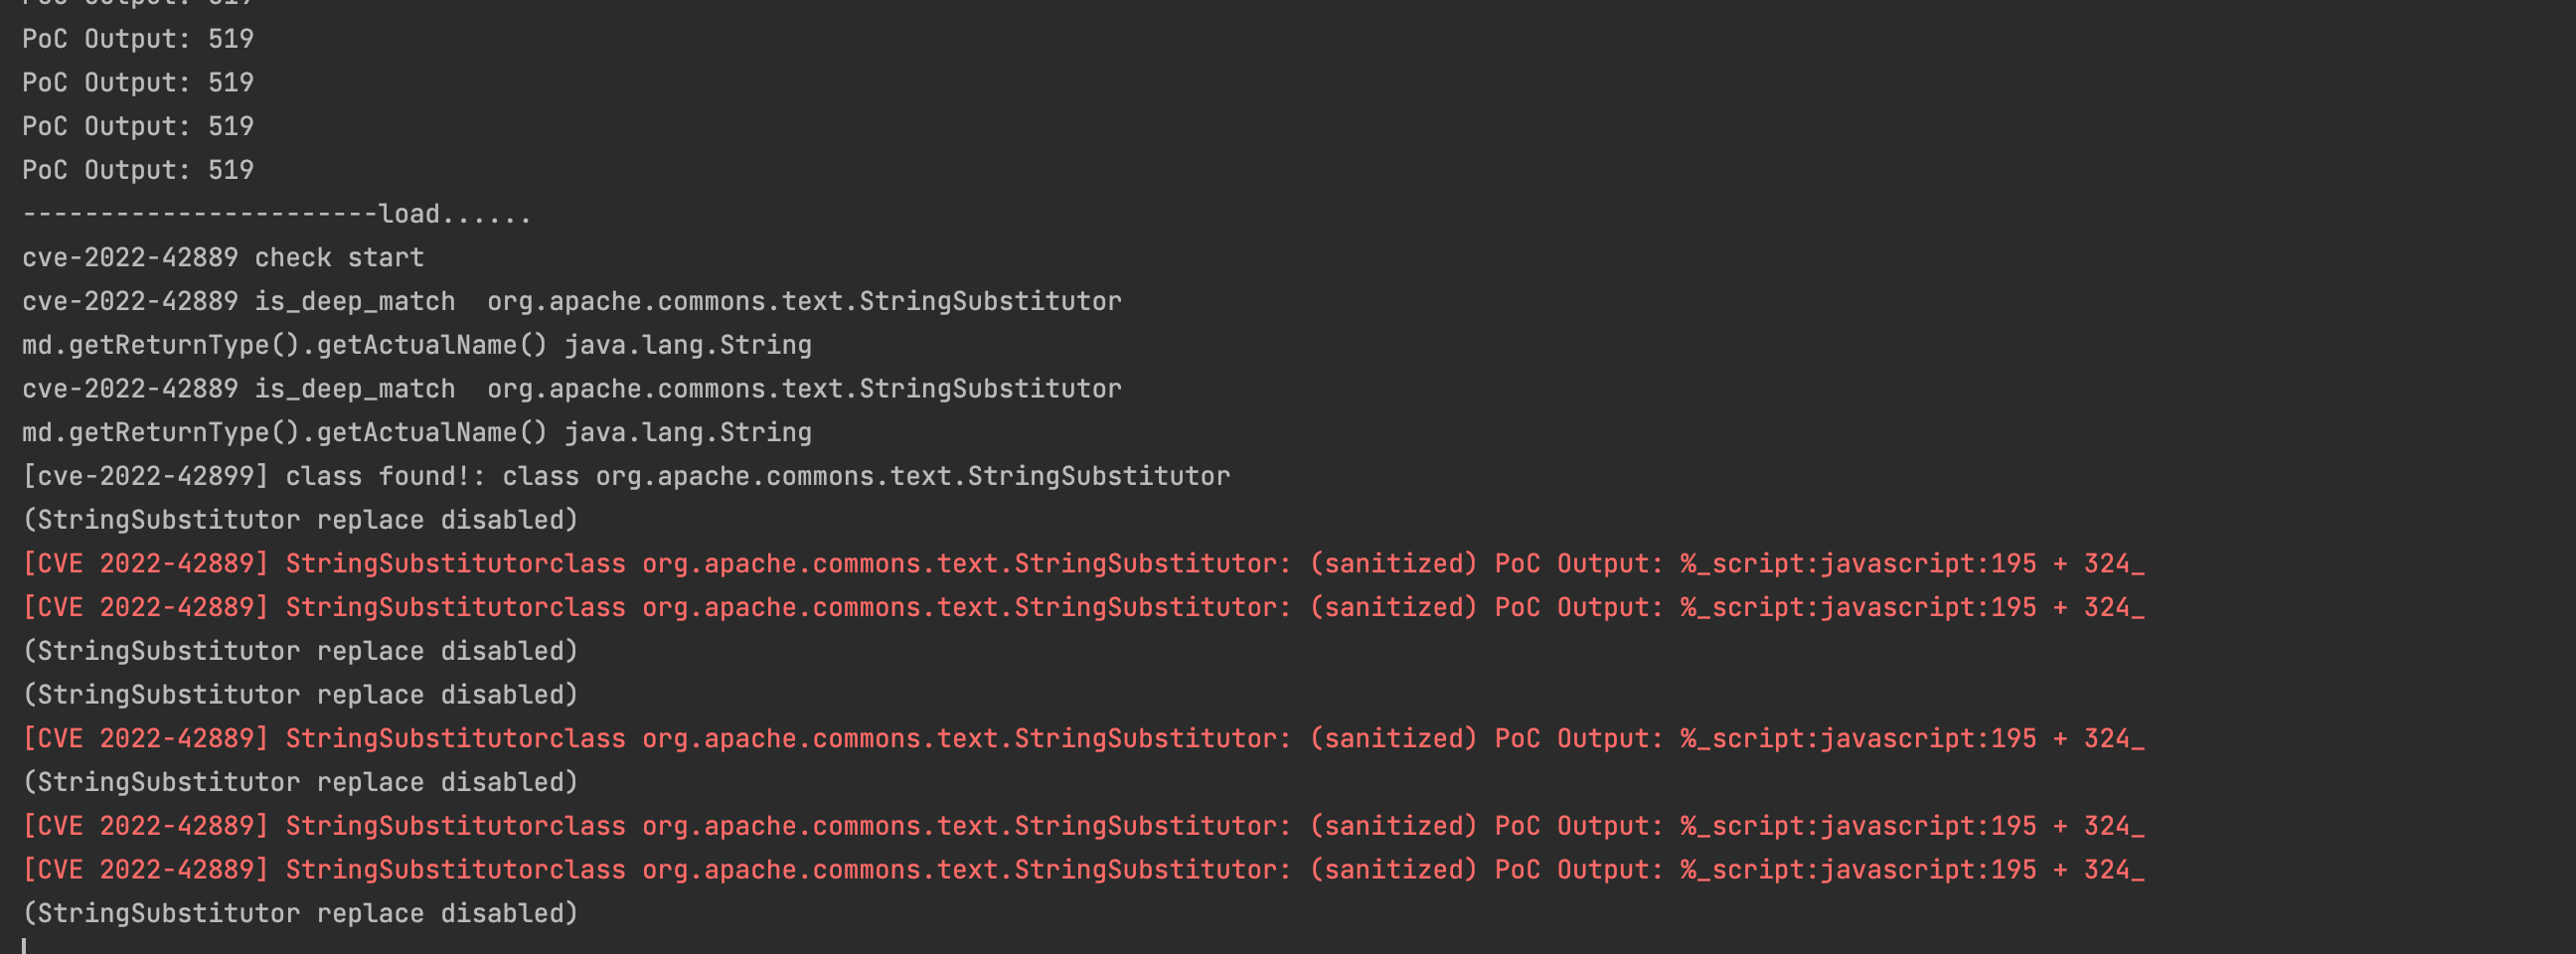 uk0/cve-2022-42889-intercept
通过 jvm 启动参数 以及 jps pid进行拦截非法参数
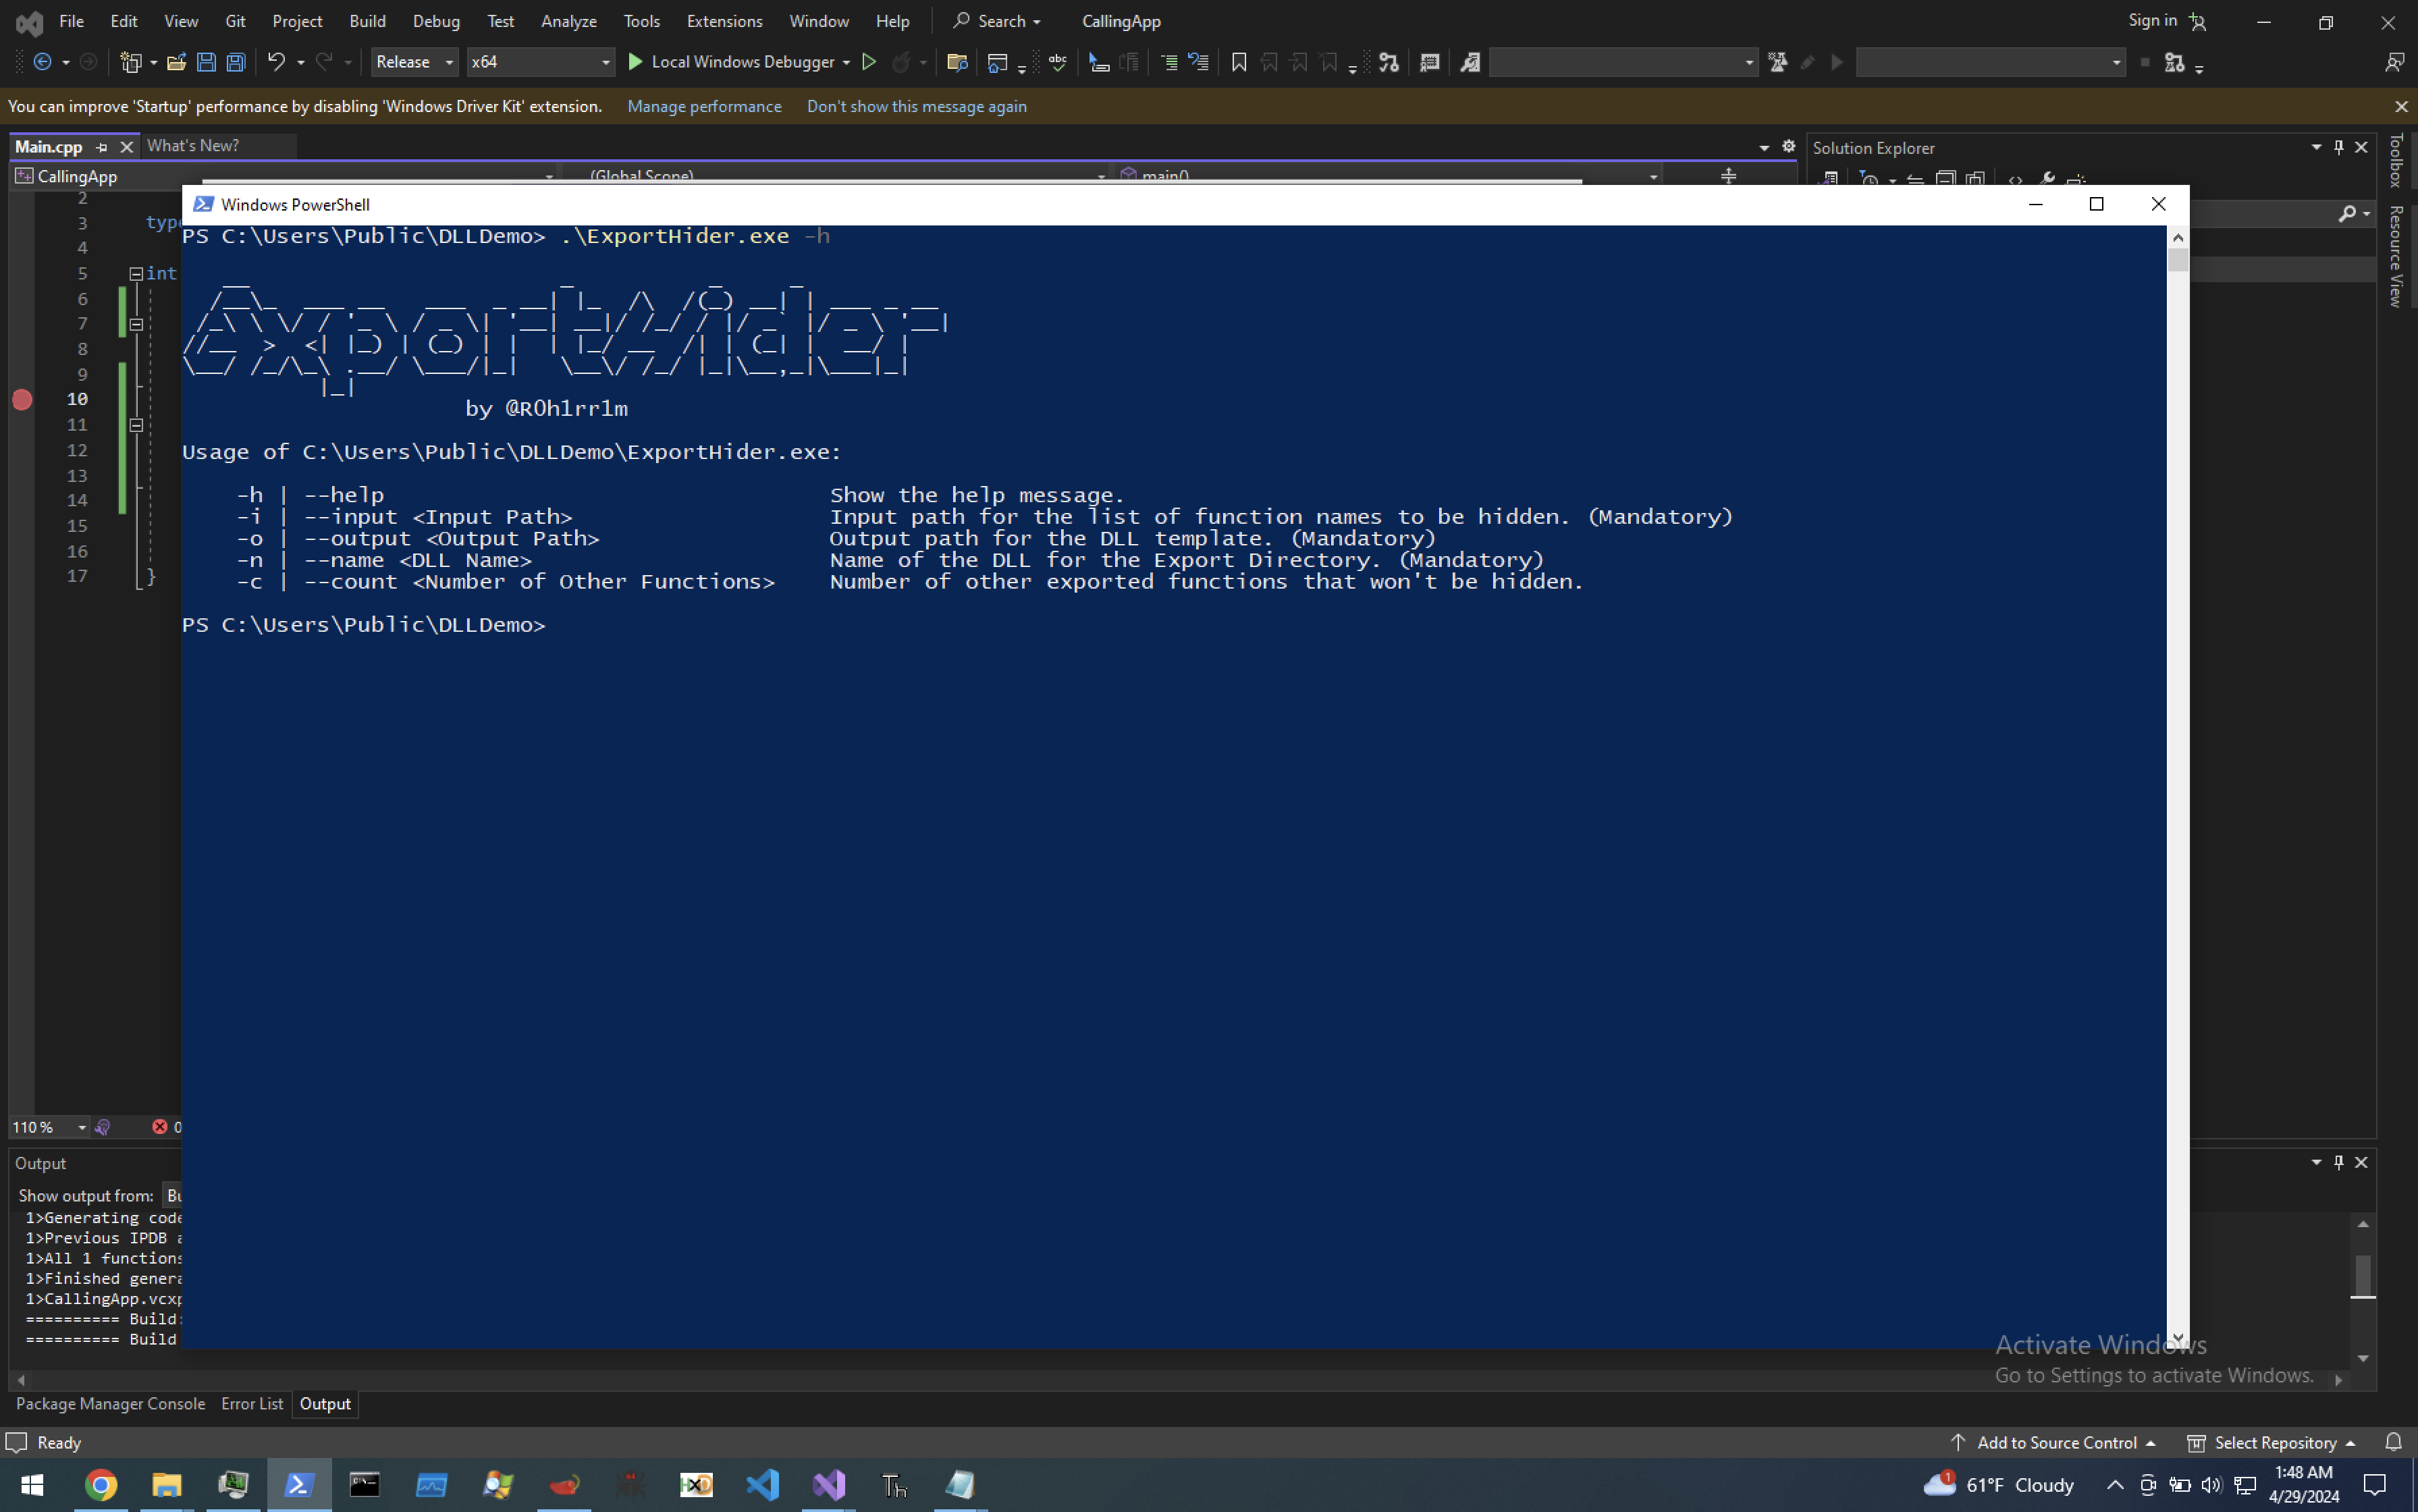 frkngksl/exporthider
ExportHider: Generating Export Table during Runtime to Hide the Exported Functions from the DLL File.
 abubakar-shahid/cve-2024-36886
Academic research on N-Day Linux kernel vulnerabilities, analyzing CVE-2024-36886 in the TIPC networking subsystem, lifecycle, impact, and mitigation…
 hupe1980/cve-2021-3129
Laravel debug mode - Remote Code Execution (RCE)
 jpiechowka/jenkins-cve-2016-0792
Exploit for Jenkins serialization vulnerability - CVE-2016-0792
 raka200juta/28458
Python exploit script for CVE-2020-28458, a prototype pollution vulnerability in DataTables. It sends crafted payloads to target URLs, supports proxy…
 shoucheng3/x-stream__xstream_cve-2021-21345_1-4-15
Java XML serialization library with a focus on CVE-2021-21345 exploit analysis and deserialization vulnerability testing for web applications.