
Medusa
 ascotbe/medusa
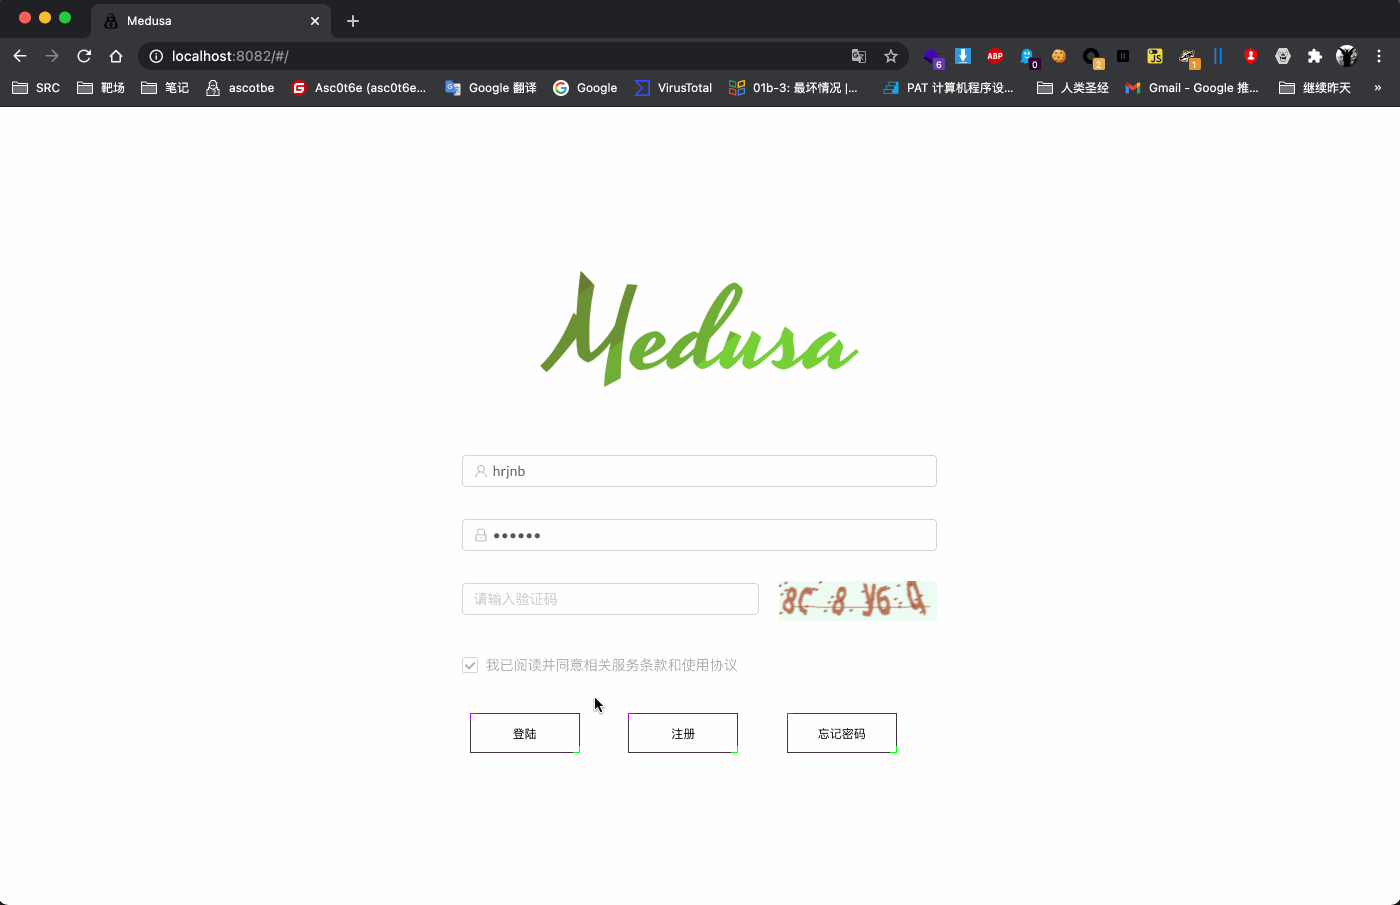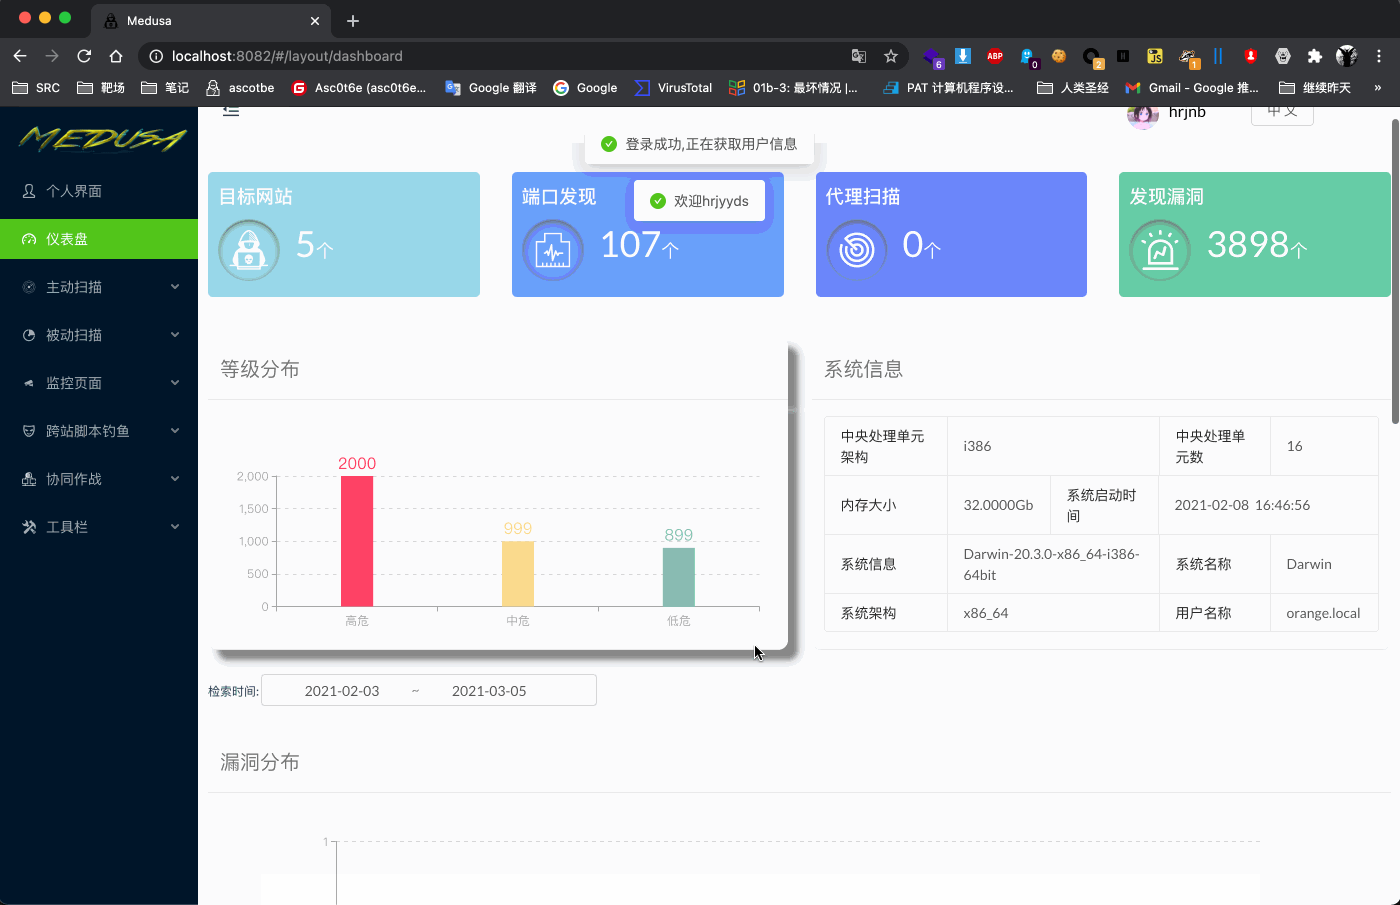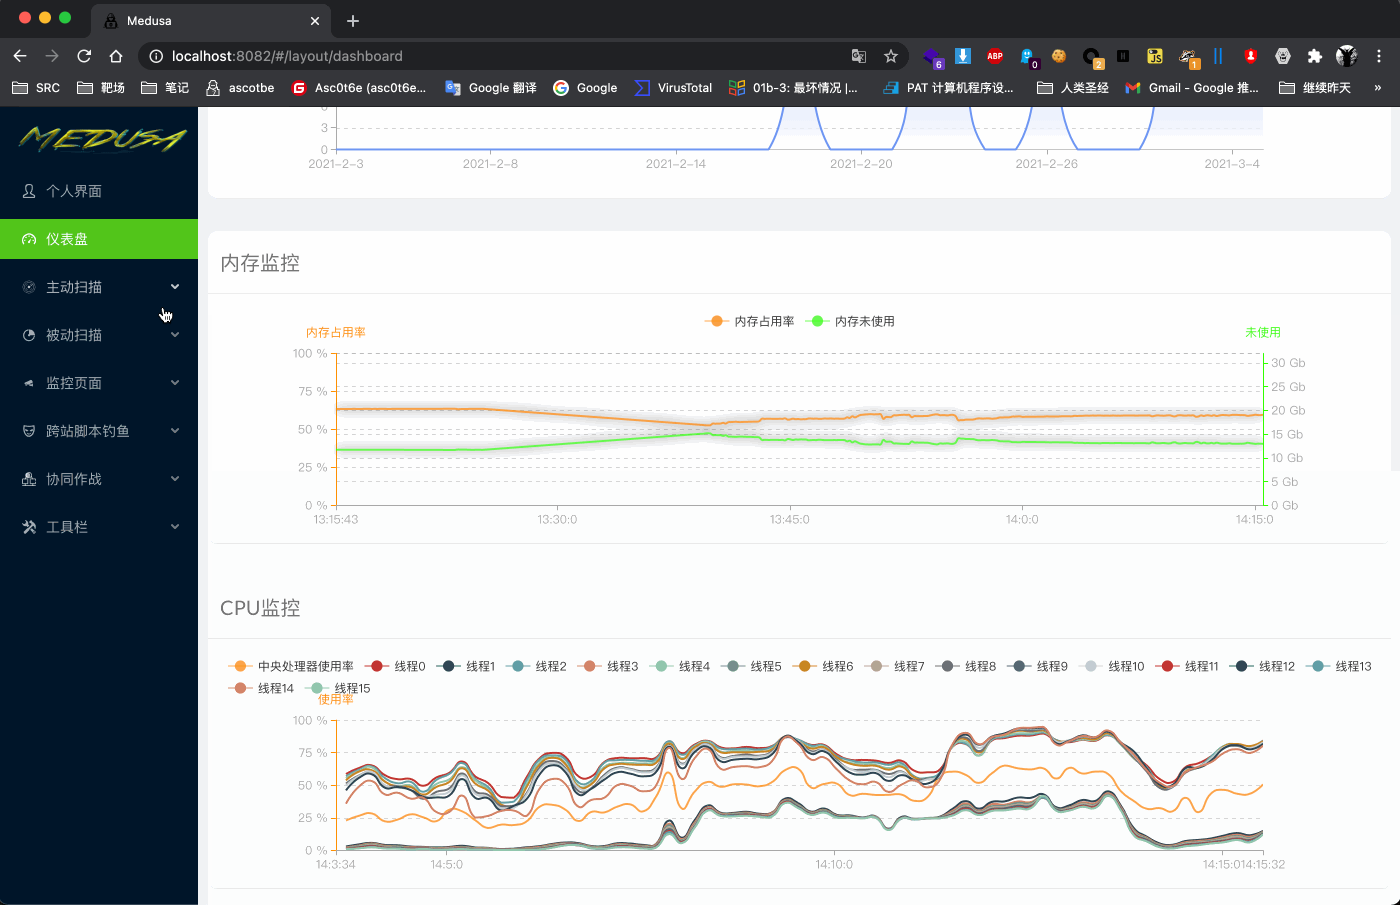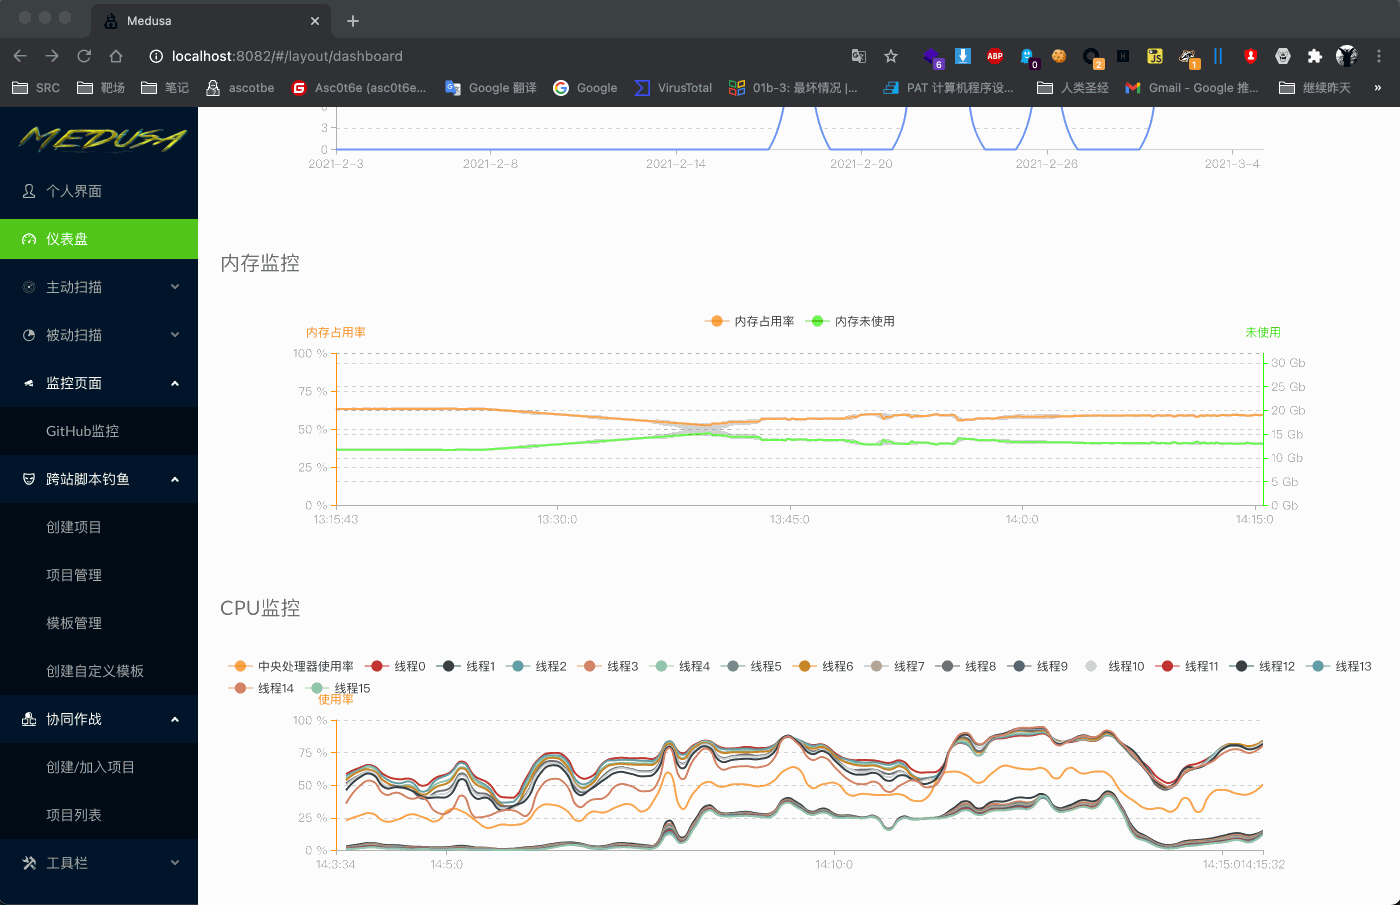
🐈Medusa是一个红队武器库平台,目前包括XSS平台、协同平台、CVE监控、免杀生成、DNSLOG、钓鱼邮件、文件获取等功能,持续开发中
dns-analysisexploit-frameworkspayload-generation+4
2.2k
ascotbe/medusa🐈Medusa是一个红队武器库平台,目前包括XSS平台、协同平台、CVE监控、免杀生成、DNSLOG、钓鱼邮件、文件获取等功能,持续开发中
 qi4l/jyso
Dual-purpose JNDI injection and Java deserialization exploitation framework with advanced bypass capabilities for WAF, RASP, and high JDK versions.…
 hktalent/cve_2020_2546
CVE-2020-2546,CVE-2020-2915 CVE-2020-2801 CVE-2020-2798 CVE-2020-2883 CVE-2020-2884 CVE-2020-2950 WebLogic T3 payload exploit poc python3,
 go-spider/cve-2018-3252
Exploit for CVE-2018-3252 targeting WebLogic deserialization vulnerability. Includes payload generation with ysoserial and a Python proof-of-concept…
 depthsecurity/netmri-2014-3418
Metasploit module exploiting InfoBlox Network Automation CVE-2014-3418 command injection to create a sudo user and deliver a reverse Meterpreter…
 dntaskmehow/babef
Research exploit framework for CVE-2026-44714, a bitcoinj signature verification flaw enabling transaction spoofing and payment hijacking, with PoC,…
 dntaskmehow/marabuse
Exploit framework for CVE-2026-39987, an unauthenticated RCE in Marimo, with a reverse shell, NKAbuse blockchain botnet payload, and Ruby C2 server.
 j4ck3lsyn-gen2/cve-2026-58457
PoC tools for CVE-2026-58457: Unauthenticated OS Command Injection leading to remote root on Shenzhen Aitemi M300 Wi-Fi Repeater (MT02). Includes…
 n1shant-sinha/cve-2017-0199
Exploit toolkit CVE-2017-0199 - v2.0 is a handy python script which provides a quick and effective way to exploit Microsoft RTF RCE. It could…
 sivapriyaranganatha/cve-2020-6418
Exploit for CVE-2020-6418, a type confusion in V8, allowing remote code execution via crafted HTML page. Uses Metasploit to deliver a reverse shell…
 kautilyagupt/cve-2024-26169-detail-1
Metasploit module for exploiting CVE-2017-11882 (MS Office Equation Editor vulnerability) using mshta.exe payload execution for remote code execution.
 abdurahmon3236/cve-2024-6366
Metasploit exploit module for CVE-2024-6366, an unauthenticated file upload remote code execution in WordPress User Profile Builder before 3.11.8,…
 cxyofficial/x200-cve-2026-43499
Exploit tool targeting CVE-2026-43499 with automated payload delivery and vulnerability verification for penetration testing engagements.
 nate0634034090/nate158g-m-w-n-l-p-d-a-o-e
### This module requires Metasploit: https://metasploit.com/download# Current source: https://github.com/rapid7/metasploit-framework##class…
 kphongagsorn/adobe-flash-cve2018-15982
Metasploit module and Python script to generate SWF payloads exploiting CVE-2018-15982, a use-after-free vulnerability in Adobe Flash Player enabling…
 abdurahmon3236/-cve-2024-31211
Metasploit module that exploits a WordPress unserialization vulnerability (CVE-2024-31211) in WP_HTML_Token to achieve remote code execution.
 reajason/memshellparty
一款专注于 Java 主流 Web 中间件的内存马快速生成工具,致力于简化安全研究人员和红队成员的工作流程,提升攻防效率
 codingranjith/hackingtoolkit
ALL IN ONE Hacking Tool For Hackers, Penetration Tester and Cybersecurity. New Version Beginner to Advanced Tool. This Tool is made for educational…