
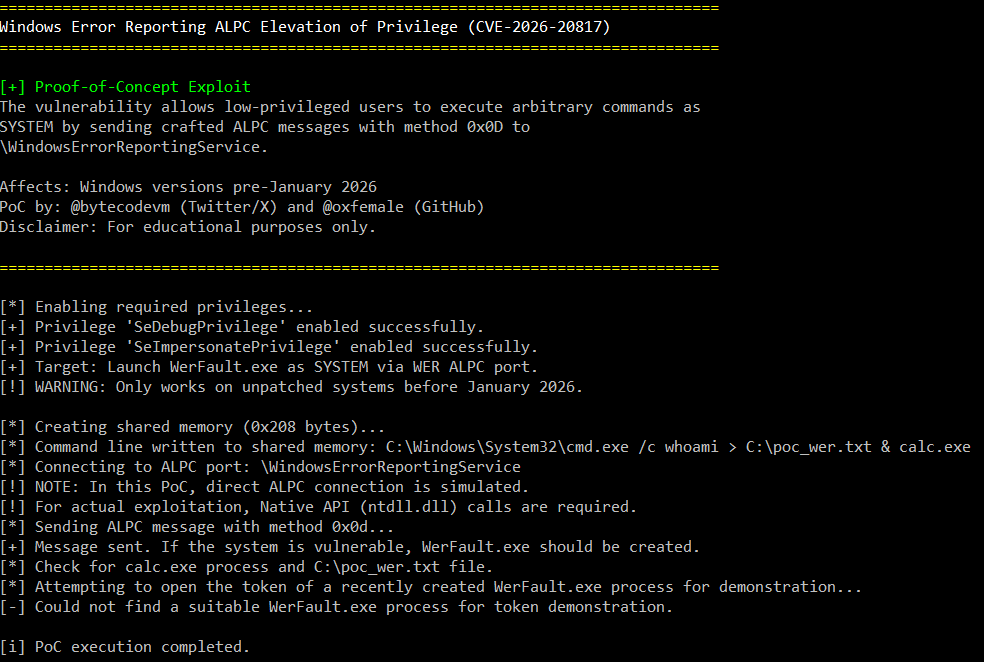
CVE-2026-20817
 oxfemale/cve-2026-20817
Proof-of-concept exploit for CVE-2026-20817, a local privilege escalation in Windows Error Reporting (WER) via ALPC, allowing low-privileged users to…
binary-exploitationexploitationexploit-frameworks+2
131
oxfemale/cve-2026-20817Proof-of-concept exploit for CVE-2026-20817, a local privilege escalation in Windows Error Reporting (WER) via ALPC, allowing low-privileged users to…
 f1tz/cve-2020-0796-lpe-exp
Compiled Windows SMBv3 local privilege escalation exploit targeting CVE-2020-0796 (SMBGhost). Tested on x64 Win10 1909.
 fenalik/cve-2021-1732
CVE-2021-1732 local privilege escalation exploit for Windows 10, with research and proof-of-concept code targeting kernel-mode vulnerabilities.
 zoemurmure/cve-2023-21768-afd-for-winsock-eop-exploit
Local privilege escalation exploit for Windows Ancillary Function Driver (afd.sys) targeting CVE-2023-21768, with post-exploitation cleanup code.…
 hackspeak/cve-2026-62735
Local privilege escalation exploit for Windows HTTP.sys integer overflow (CVE-2026-62735), demonstrating crash and full SYSTEM shell via nonpaged…
 maxprog-svg/cve-2026-68820_mass_exploit
Automated local privilege escalation exploit for Windows 10/11 targeting AFD.sys use-after-free to gain SYSTEM, with PPL bypass and EDR evasion for…
 simoesctt/sctt-2026-33-0002-dwm-visual-field-singularity
Exploit research targeting Windows DWM to achieve local privilege escalation via a theoretical Visual-Field Singularity, bypassing graphics isolation…
 chompie1337/windows_mskssrv_lpe_cve-2023-36802
Local privilege escalation exploit for CVE-2023-36802 targeting Windows kernel streaming service (MSKSSRV) on Windows 11 22H2, using I/O Ring…
 k8gege/cve-2021-1675
Exploit for CVE-2021-1675 (PrintNightmare) enabling local and remote SYSTEM-level privilege escalation on Windows via the Print Spooler service.…
 crackercat/cve-2020-1020-exploit
Local privilege escalation exploit for CVE-2020-1020 targeting Windows 7/8/8.1 x64 via Type1 Font Pool Overflow.
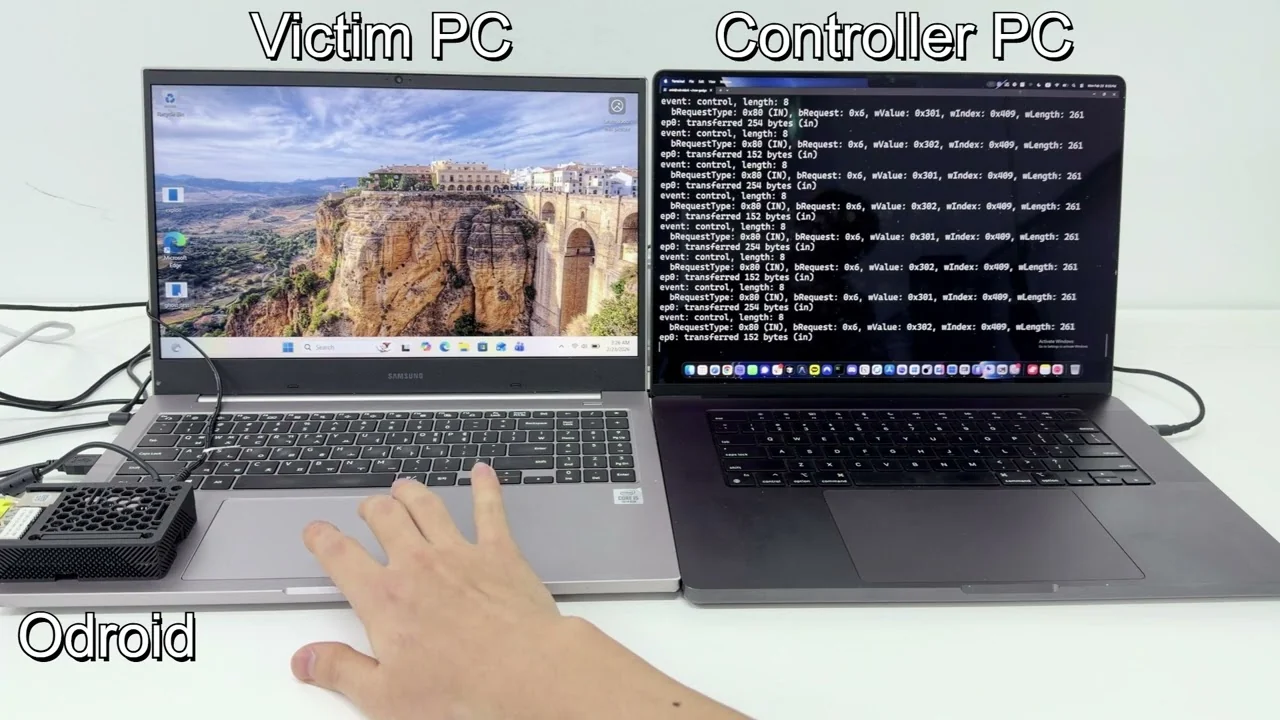 enki-kr/cve-2026-32223-usbprint-exploit
Proof-of-concept exploit for CVE-2026-32223, a heap-based buffer overflow in Windows USB print driver (usbprint.sys), achieving local privilege…
 zmkeh/cve-2025-29824-clfs-local-privilege-escalation
Local privilege escalation exploit for CVE-2025-29824 targeting the Windows Common Log File System (CLFS) driver, providing proof-of-concept code for…
 simoesctt/-sctt-2026-33-0002-dwm-visual-field-singularity
Weaponizes a Visual-Field Singularity in Windows Desktop Window Manager to achieve local privilege escalation to SYSTEM, bypassing Graphics Isolation…
 cyghtinc/cve-2024-30088-binary-lpe-privielege-escalation-cyght-toctou
Compiled proof-of-concept binary for local privilege escalation exploiting CVE-2024-30088, a TOCTOU vulnerability, targeting Windows systems.
 aazhuliang/cve-2021-31956-exp
Exploit for CVE-2021-31956, a Windows kernel privilege escalation vulnerability, targeting Windows 10 1903. Provides a proof-of-concept…
 bluefrostsecurity/cve-2019-1215
Local privilege escalation exploit for CVE-2019-1215, a use-after-free in ws2ifsl.sys, targeting Windows 10 19H1 x64 with kASLR, kCFG, and SMEP…
 andrewtrube/cve-2021-1675
Local privilege escalation exploit for CVE-2021-1675 (PrintNightmare) that installs a malicious DLL to gain SYSTEM access on vulnerable Windows…
 nbs32k/localstranger
PoC for WinNotify, demonstrated through a driver mapper, and local privilege escalation.