
aggrokatz
 sec-consult/aggrokatz
Aggrokatz is an aggressor plugin extension for Cobalt Strike which enables pypykatz to interface with the beacons remotely and allows it to parse…
exploit-frameworkspayload-developmentpenetration-testing+2
154
sec-consult/aggrokatzAggrokatz is an aggressor plugin extension for Cobalt Strike which enables pypykatz to interface with the beacons remotely and allows it to parse…
 rek2/goenumerator
A personal tool in GO for my usual first enumeration steps on a target
 ambionics/phpggc
PHPGGC is a library of PHP unserialize() payloads along with a tool to generate them, from command line or programmatically.
 m4sc3r4n0/avoidz
Avoidz tool to bypass most A.V softwares
 inf0secrabbit/badassmacros
C# tool that generates malicious VBA macros with shellcode injection, VBA purging, and sandbox detection for red team operations.
 xfox64x/cve-2016-5639
Crestron AirMedia AM-100 Traversal and Hashdump Metasploit Modules
 nickvourd/supernova
Multi-cipher shellcode encryptor and obfuscator with automatic output conversion to C, C#, Rust, Nim, Python, and more. Supports ROT, XOR, RC4, AES,…
 pimps/ysoserial-modified
That repository contains my updates to the well know java deserialization exploitation tool ysoserial.
 tanc7/exocet-av-evasion
EXOCET - AV-evading, undetectable, payload delivery tool
 openclarity/openclarity
OpenClarity is an open source platform built to enhance security and observability of cloud native applications and infrastructure
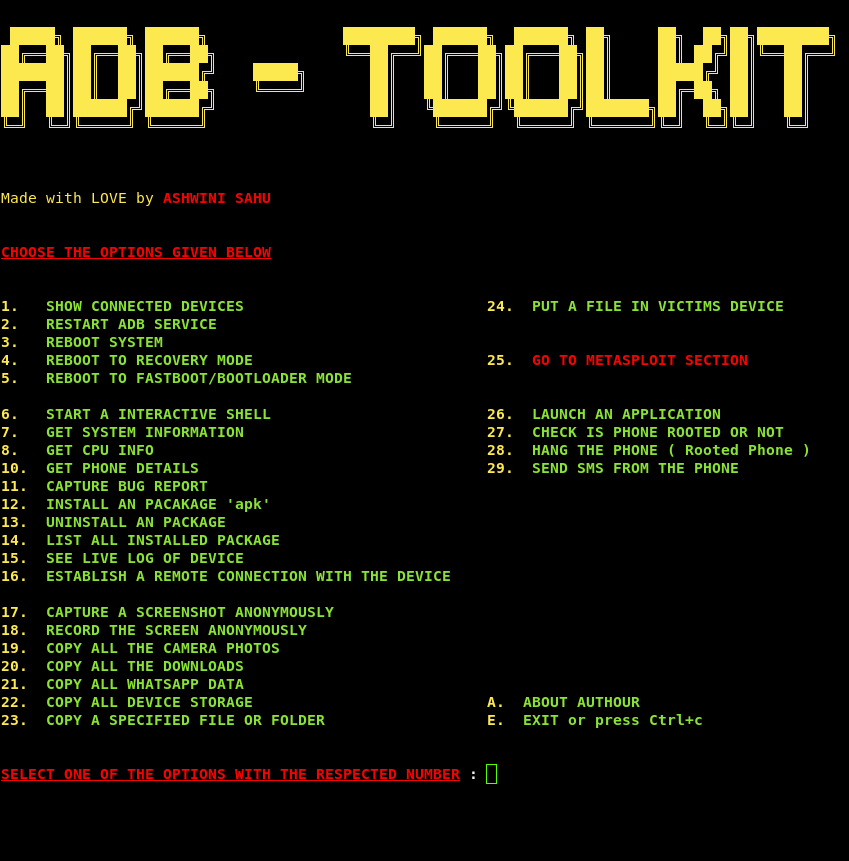 ashwin990/adb-toolkit
ADB-Toolkit V2 for easy ADB tricks with many perks in all one. ENJOY!
 darkr4y/geacon
Practice Go programming and implement CobaltStrike's Beacon in Go
 gl4ssesbo1/nebula
Nebula is a cloud C2 Framework, which at the moment offers reconnaissance, enumeration, exploitation, post exploitation on AWS, but still working to…
 samugit83/redamon
Autonomous AI red team framework that chains reconnaissance, exploitation, and post-exploitation into a single pipeline, then triages findings,…
 pablosnt/rekono
Offensive security platform that automates attack surface discovery and vulnerability management
 bo0l3an/cve-2024-49112-poc
CVE-2024-49112 LDAP RCE PoC and Metasploit Module
 neo-neo6/cve-2025-65018-heap-buffer-overflow-in-libpng-ps4-ps5-
Proof-of-concept exploit for a heap buffer overflow in libpng on PS4/PS5. Generates a malicious PNG that triggers the vulnerability when opened in…
 praetorian-inc/wasmforge
WasmForge — compile Go and C# programs to single-binary, WASM-sandboxed native executables with polymorphic output.