
phpggc
 ambionics/phpggc
PHPGGC is a library of PHP unserialize() payloads along with a tool to generate them, from command line or programmatically.
exploitationexploit-frameworkspayload-generation+1
3.9k
ambionics/phpggcPHPGGC is a library of PHP unserialize() payloads along with a tool to generate them, from command line or programmatically.
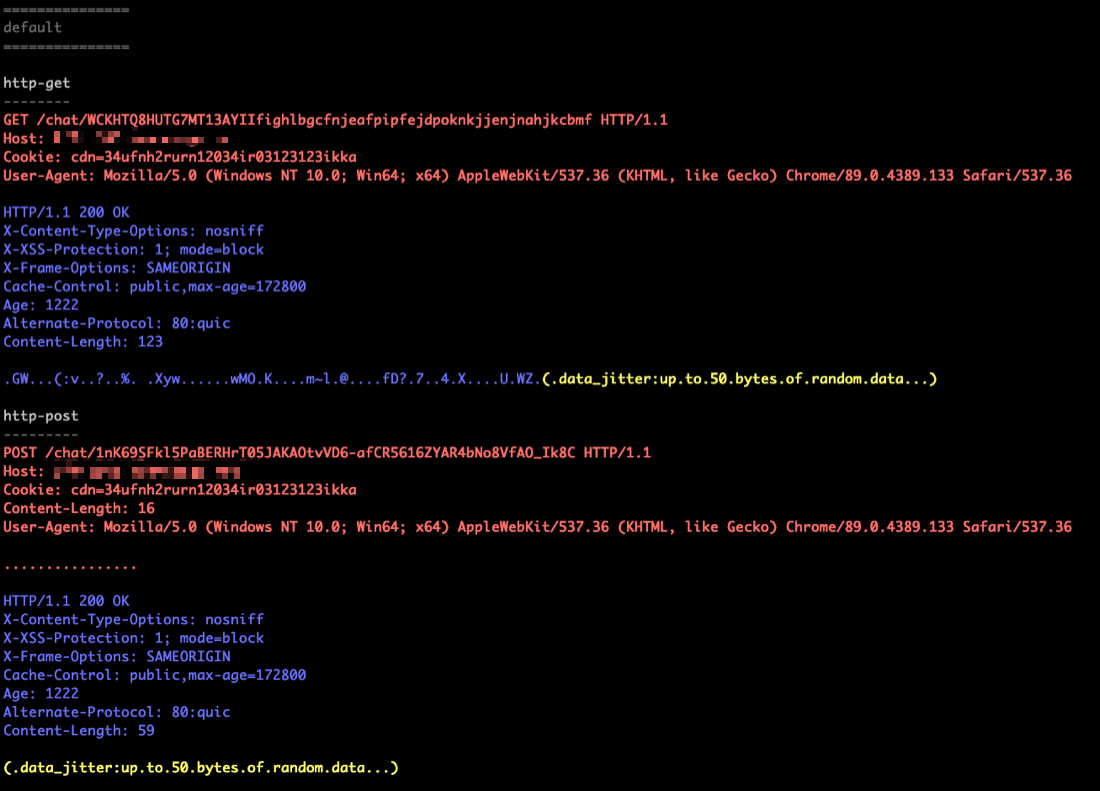 tylous/sourcepoint
Polymorphic C2 profile generator for Cobalt Strike that automates creation of evasive beacon configurations with randomized options for HTTP, DNS,…
 outflanknl/c2-tool-collection
A collection of tools which integrate with Cobalt Strike (and possibly other C2 frameworks) through BOF and reflective DLL loading techniques.
 pentoo/pentoo-overlay
Gentoo overlay for security tools as well as the heart of the Pentoo Livecd
 xaitax/sploitscan
Aggregates CVE details, exploit databases, and EPSS scores with AI risk assessment and vulnerability scanner import for prioritized patching.
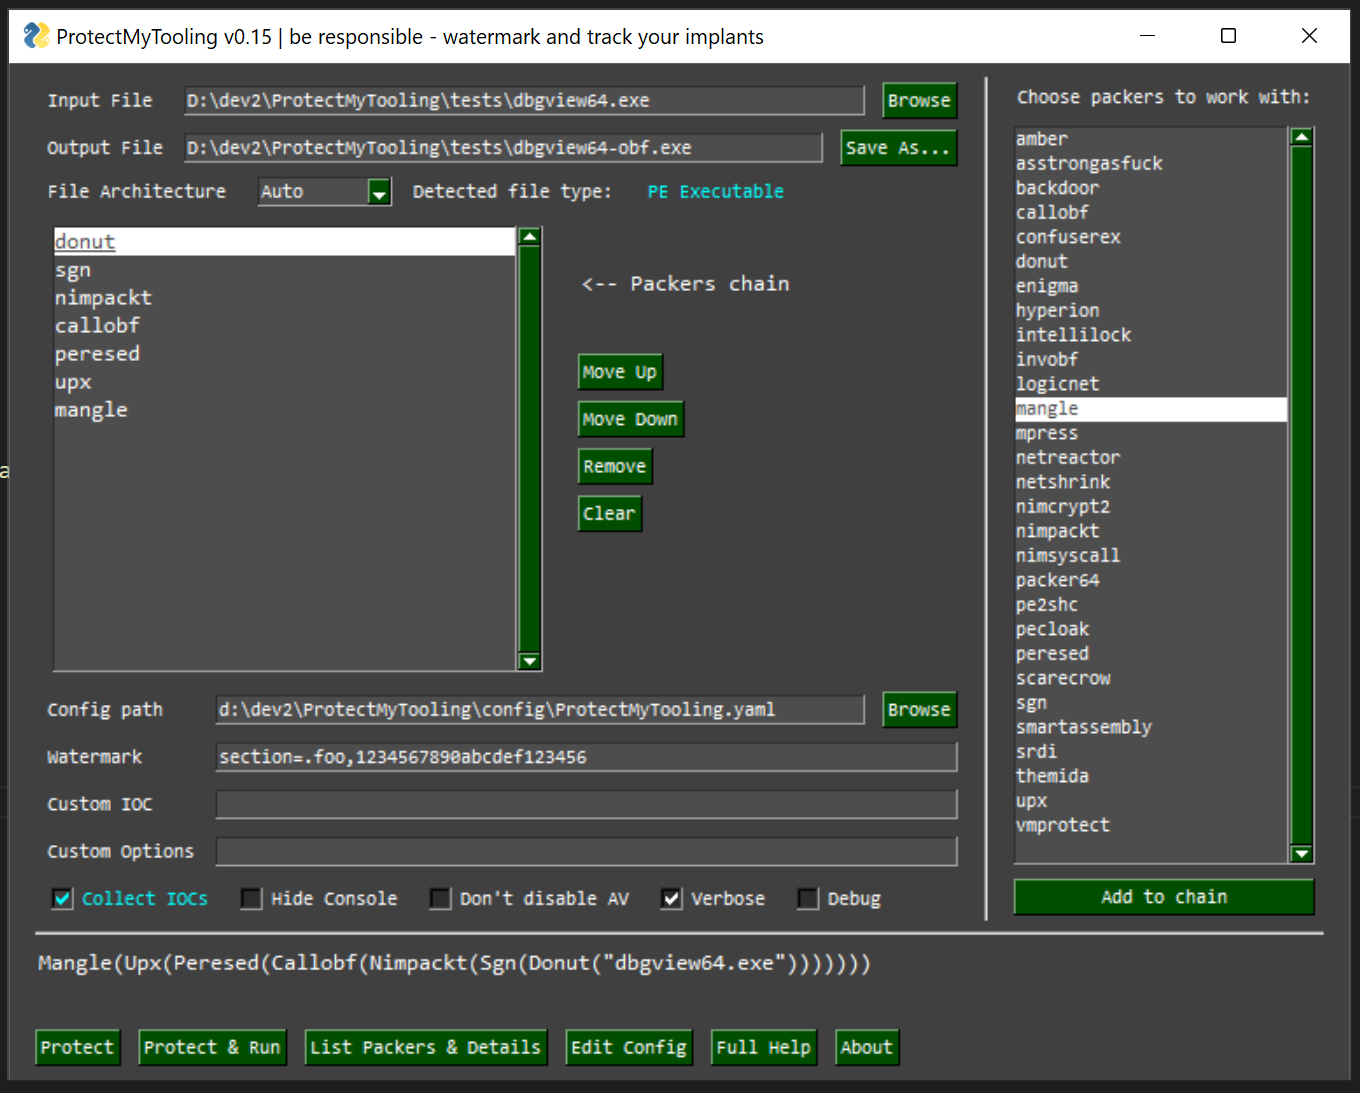 mgeeky/protectmytooling
Multi-Packer wrapper letting us daisy-chain various packers, obfuscators and other Red Team oriented weaponry. Featured with artifacts watermarking,…
 lachlan2k/react2shell-cve-2025-55182-original-poc
Original proof-of-concept exploits for React2Shell (CVE-2025-55182), demonstrating remote code execution in Next.js applications via Webpack chunk…
 mandiant/gopacket
A complete Go port of Impacket - 63 CLI tools and 24 libraries for Windows & Active Directory protocol attacks, compiled to a single dependency-free…
 pedrib/poc
Advisories, proof of concept files and exploits that have been made public by @pedrib.
 0xsp-srd/mortar
evasion technique to defeat and divert detection and prevention of security products (AV/EDR/XDR)
 xx0hcd/malleable-c2-profiles
Cobalt Strike - Malleable C2 Profiles. A collection of profiles used in different projects using Cobalt Strike https://www.cobaltstrike.com/.
 federicodotta/java-deserialization-scanner
All-in-one plugin for Burp Suite for the detection and the exploitation of Java deserialization vulnerabilities
 bluscreenofjeff/malleable-c2-randomizer
A script to randomize Cobalt Strike Malleable C2 profiles and reduce the chances of flagging signature-based detection controls
 d4vinci/pastejacker
Hacking systems with the automation of PasteJacking attacks.
 horizon3ai/cve-2022-40684
A proof of concept exploit for CVE-2022-40684 affecting Fortinet FortiOS, FortiProxy, and FortiSwitchManager
 jesusprubio/bluebox
A collection of exploits for different VoIP products.
 naksyn/pythonmemorymodule
pure-python implementation of MemoryModule technique to load dll and unmanaged exe entirely from memory
 inf0secrabbit/badassmacros
C# tool that generates malicious VBA macros with shellcode injection, VBA purging, and sandbox detection for red team operations.