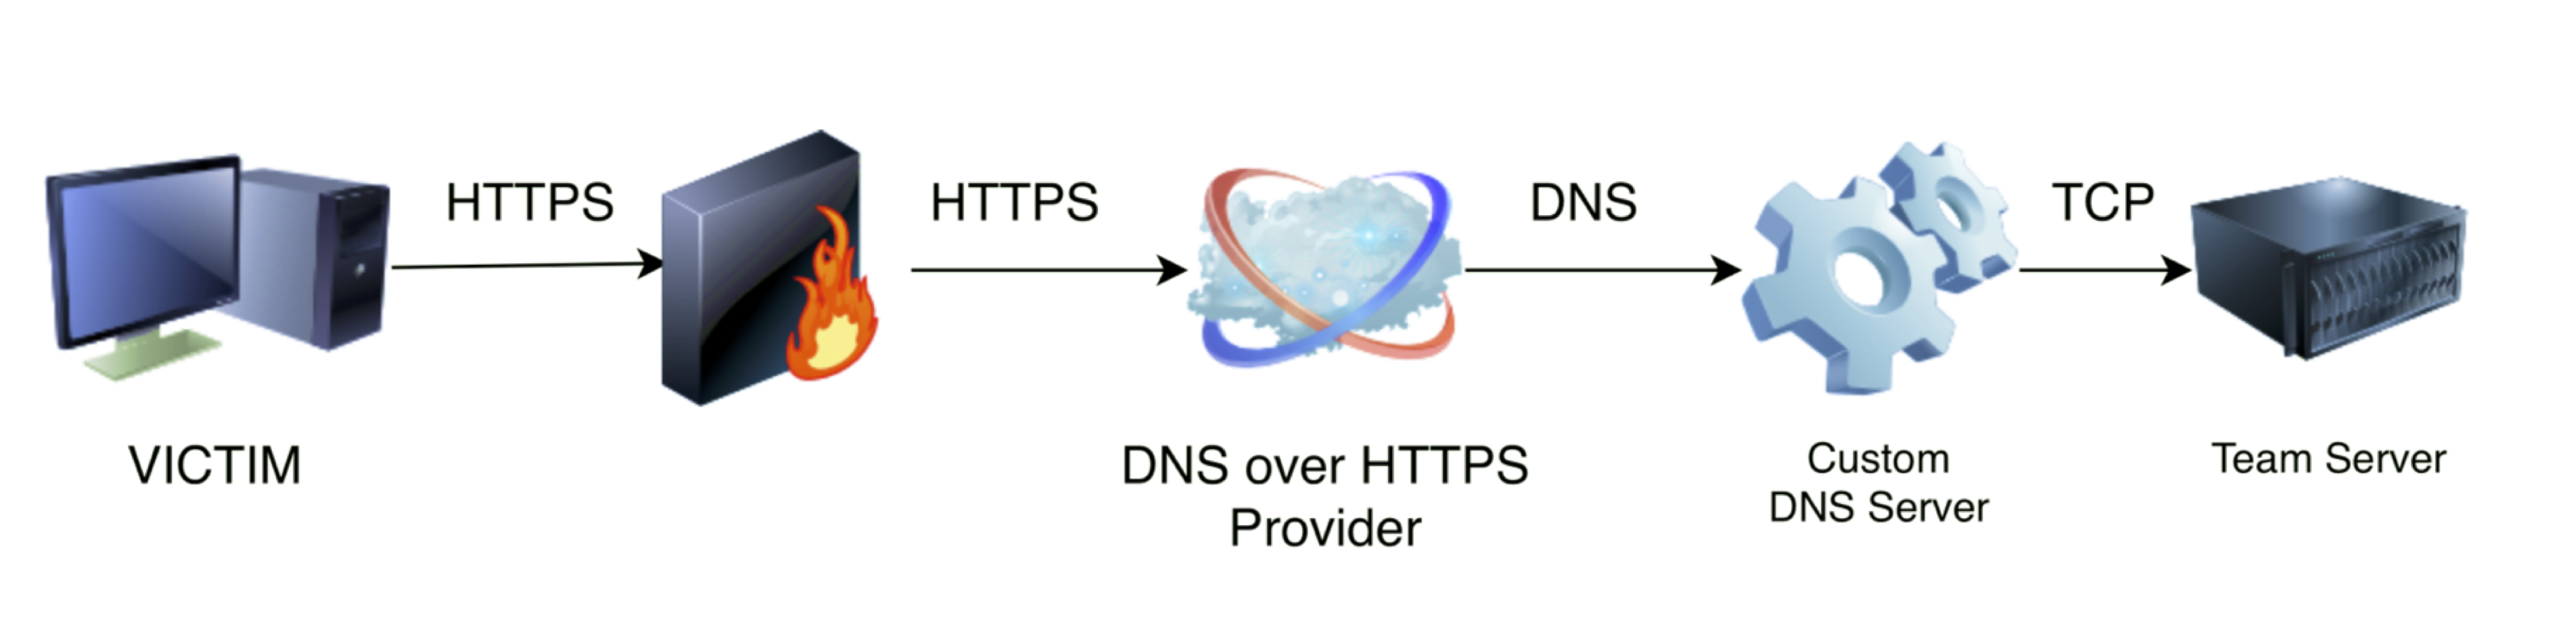
killchain
 ruped24/killchain
A unified console to perform the "kill chain" stages of attacks.
command-and-controlexploit-frameworkspayload-generation+5
2073 years ago
ruped24/killchainA unified console to perform the "kill chain" stages of attacks.
 vanshuk-bhagat/apache-http-server-vulnerabilities-cve-2021-41773-and-cve-2021-42013
In this project, I documented a detailed penetration testing process targeting Apache HTTP Server vulnerabilities, specifically CVE-2021-41773 and…
 projectdiscovery/nuclei-templates
Community curated list of templates for the nuclei engine to find security vulnerabilities.
 ghosttroops/scan4all
Official repository vuls Scan: 15000+PoCs; 23 kinds of application password crack; 7000+Web fingerprints; 146 protocols and 90000+ rules Port…
 anouarbensaad/vulnx
vulnx 🕷️ an intelligent Bot, Shell can achieve automatic injection, and help researchers detect security vulnerabilities CMS system. It can perform…
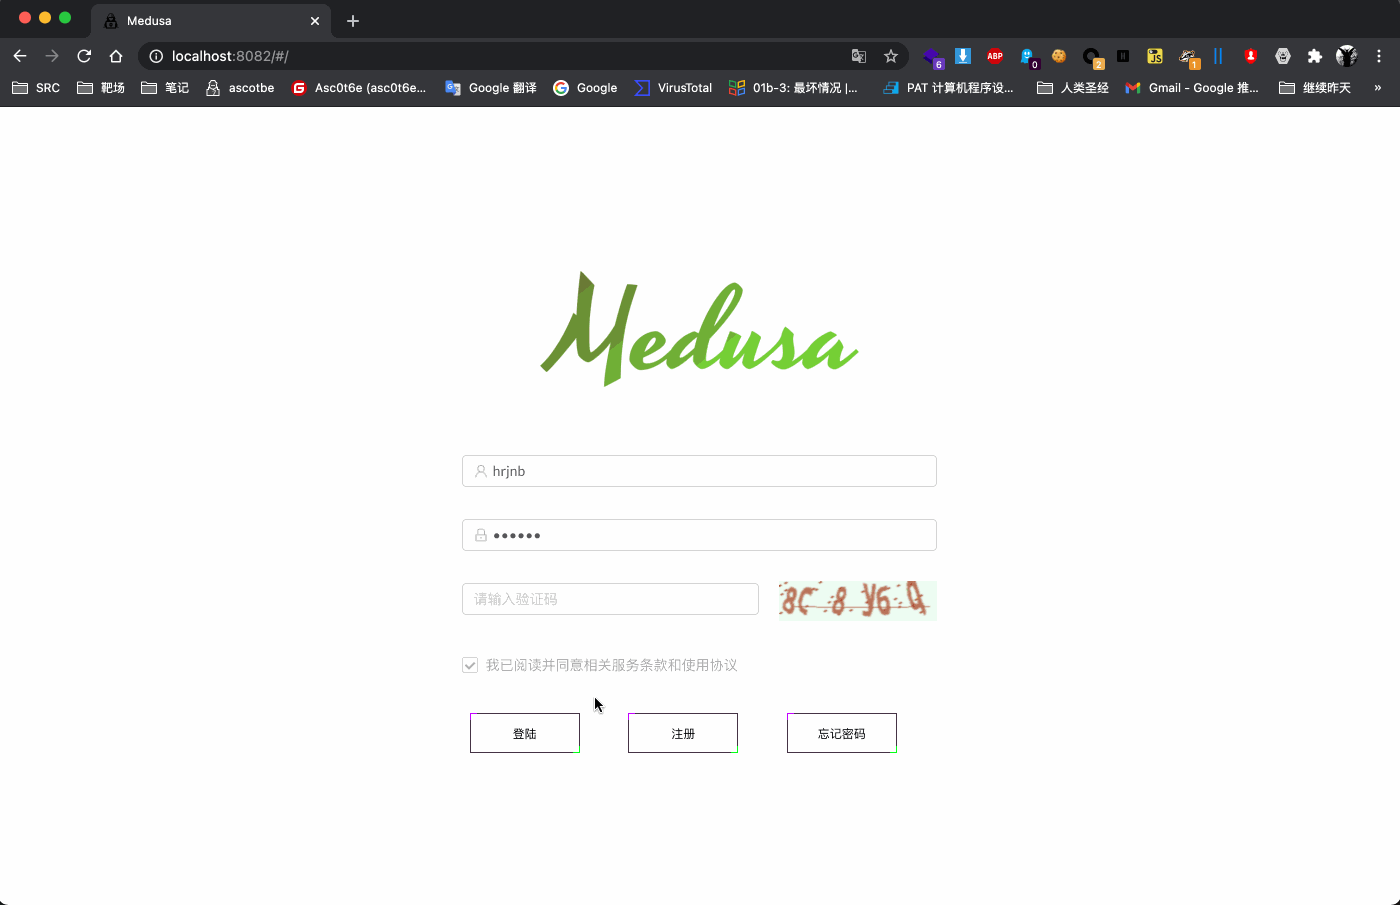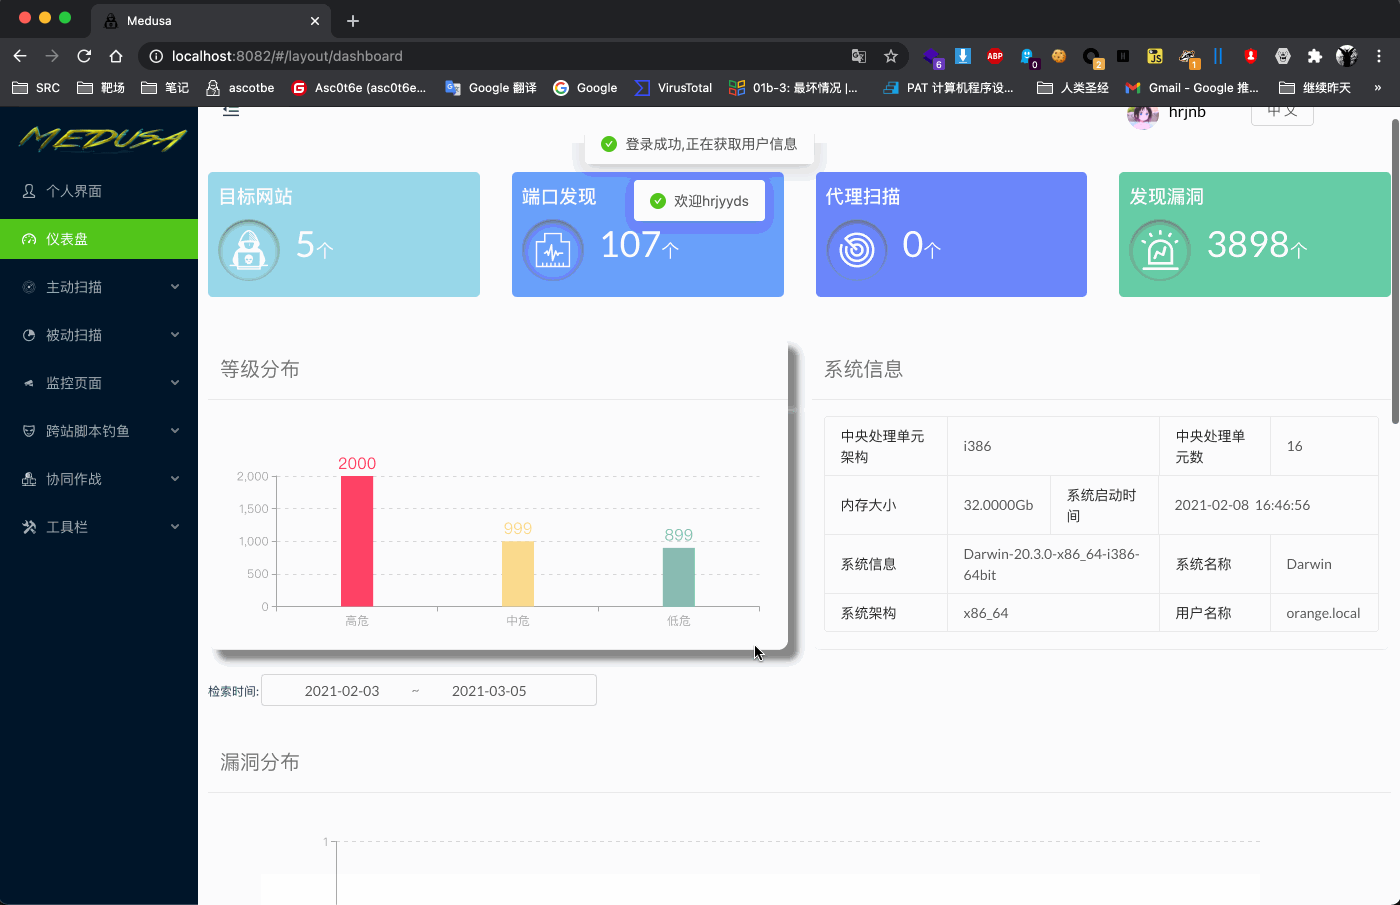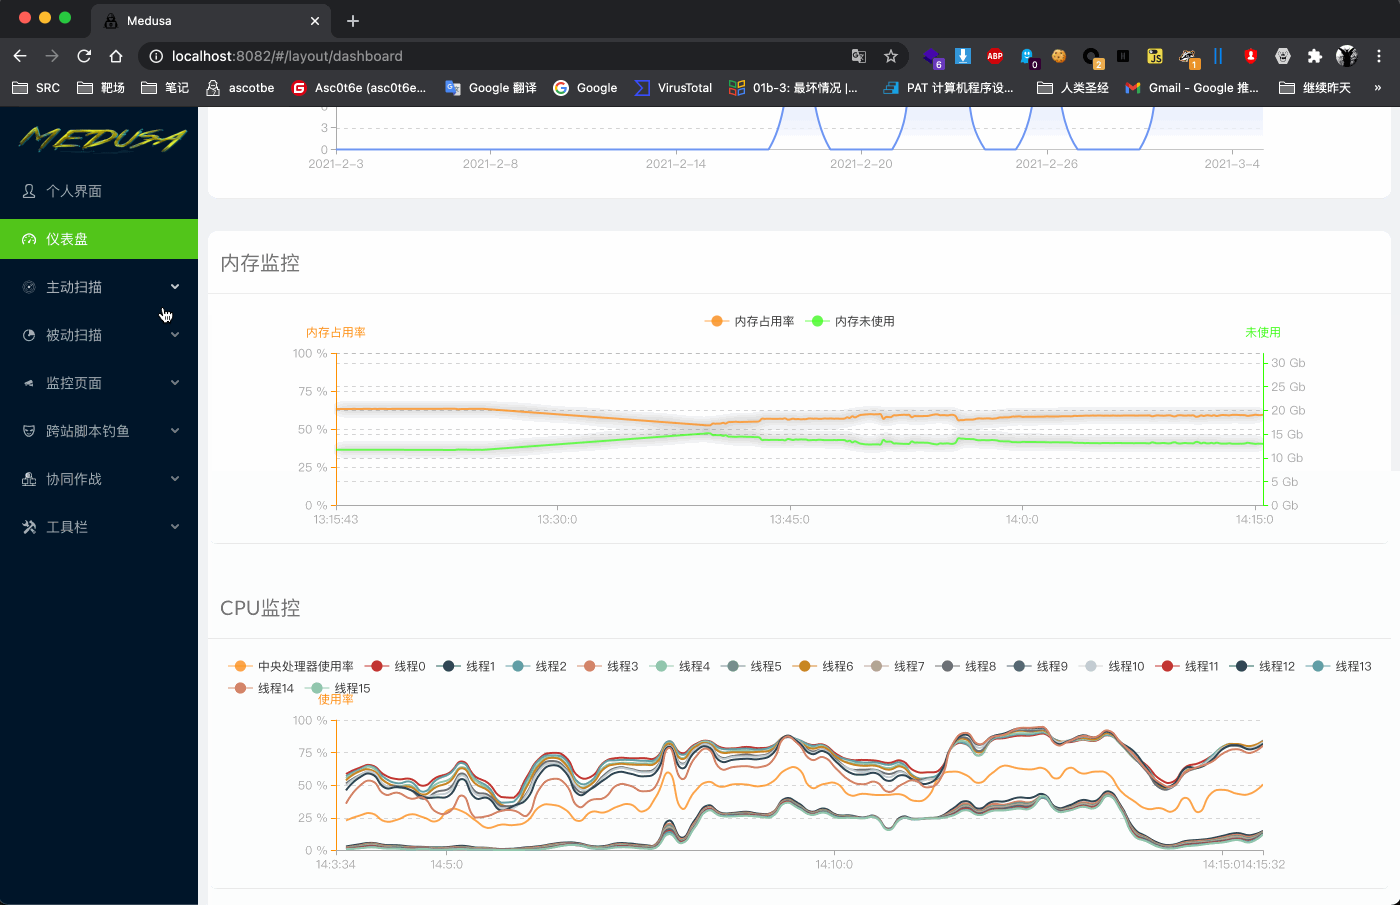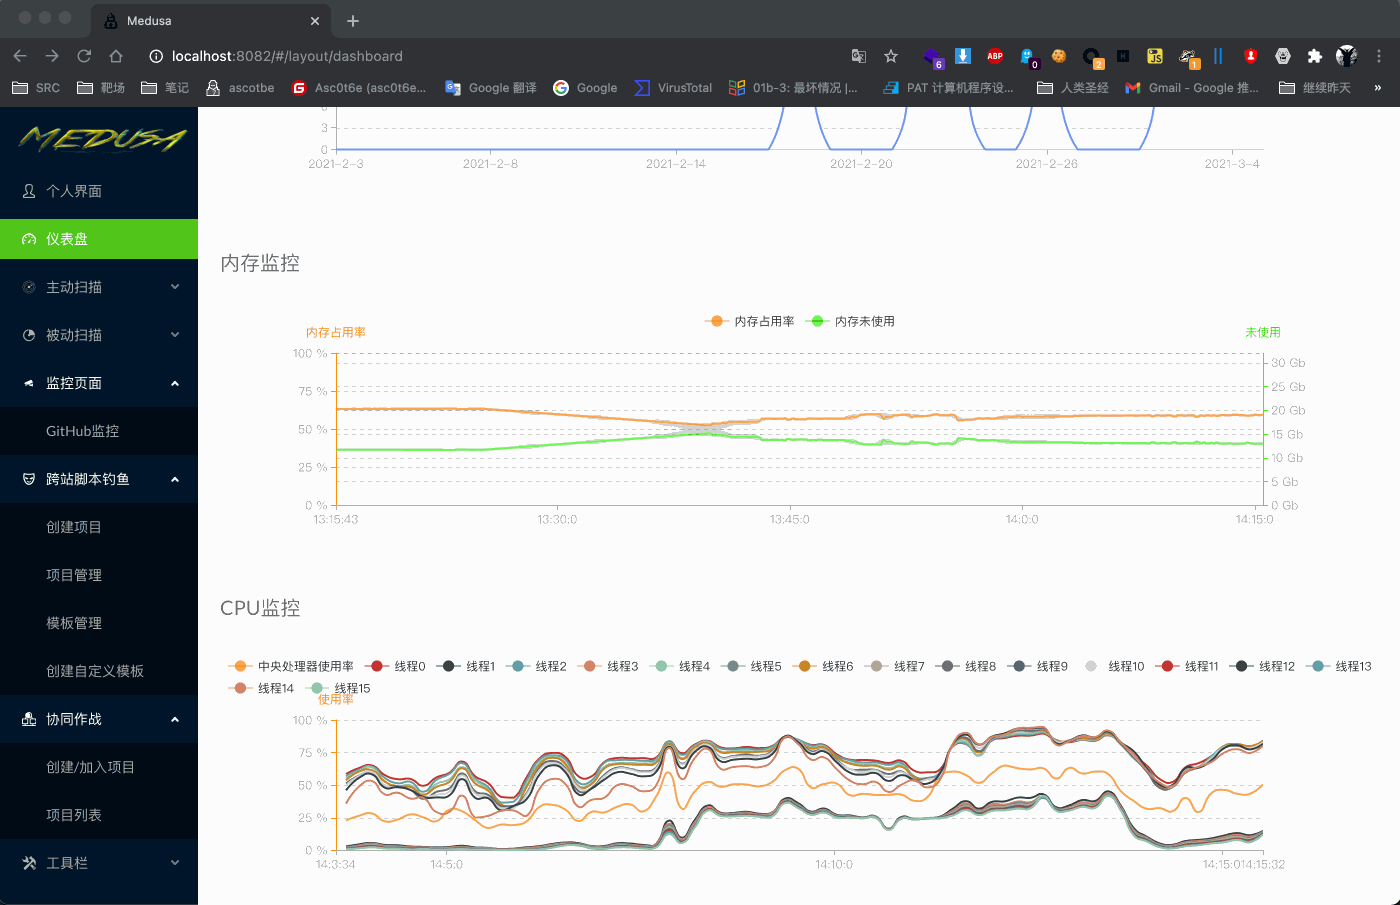 ascotbe/medusa
🐈Medusa是一个红队武器库平台,目前包括XSS平台、协同平台、CVE监控、免杀生成、DNSLOG、钓鱼邮件、文件获取等功能,持续开发中
 v3n0m-scanner/v3n0m-scanner
Popular Pentesting scanner in Python3.6 for SQLi/XSS/LFI/RFI and other Vulns
 infobyte/evilgrade
Evilgrade is a modular framework that allows the user to take advantage of poor upgrade implementations by injecting fake updates.
 ronin-rb/ronin
Ronin is a Free and Open Source Ruby Toolkit for Security Research and Development. Ronin also allows for the rapid development and distribution of…
 jiangsir404/poc-s
POC-T强化版本 POC-S , 用于红蓝对抗中快速验证Web应用漏洞, 对功能进行强化以及脚本进行分类添加,自带dnslog等, 平台补充来自vulhub靶机及其他开源项目的高可用POC
 bhavsec/autopentest-ai
Agentic Pentesting MCP server that discovers, exploits, and reports web application vulnerabilities.

 hamlasiraj/metasploit-bailiwicked_domain-fix
Fix for undefined method each in Metasploit’s bailiwicked_domain.rb (CVE-2008-1447 DNS cache poisoning module)
 g13net/lockjaw
Modular Windows C2 framework with a Rust teamserver, Zig implant, indirect syscalls, AMSI bypass, reflective/PoolParty injection, in-memory BOF…