CVE-2025-24203-iOS-Exploit-With-Error-Logging

Slightly improved exploit of the CVE-2025-24203 iOS vulnerability by Ian Beer of Google Project Zero

Slightly improved exploit of the CVE-2025-24203 iOS vulnerability by Ian Beer of Google Project Zero

Professional extension of sqlmap project

Module written in Ruby with the objective of exploiting vulnerabilities CVE-2023-2728 and CVE-2024-3177, both related to the secret mount policy in a…

In this project, I documented a detailed penetration testing process targeting Apache HTTP Server vulnerabilities, specifically CVE-2021-41773 and…

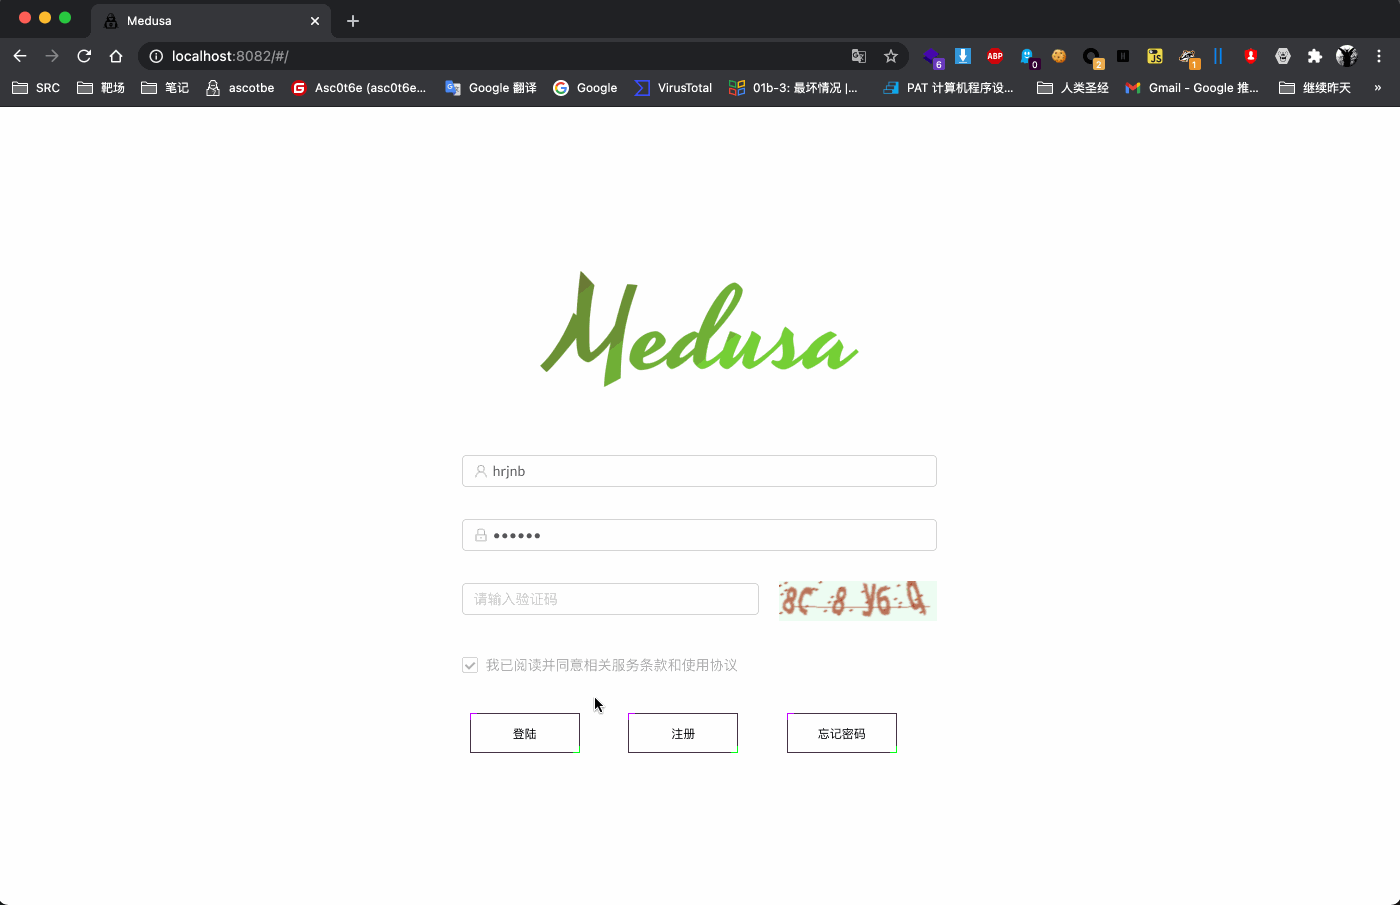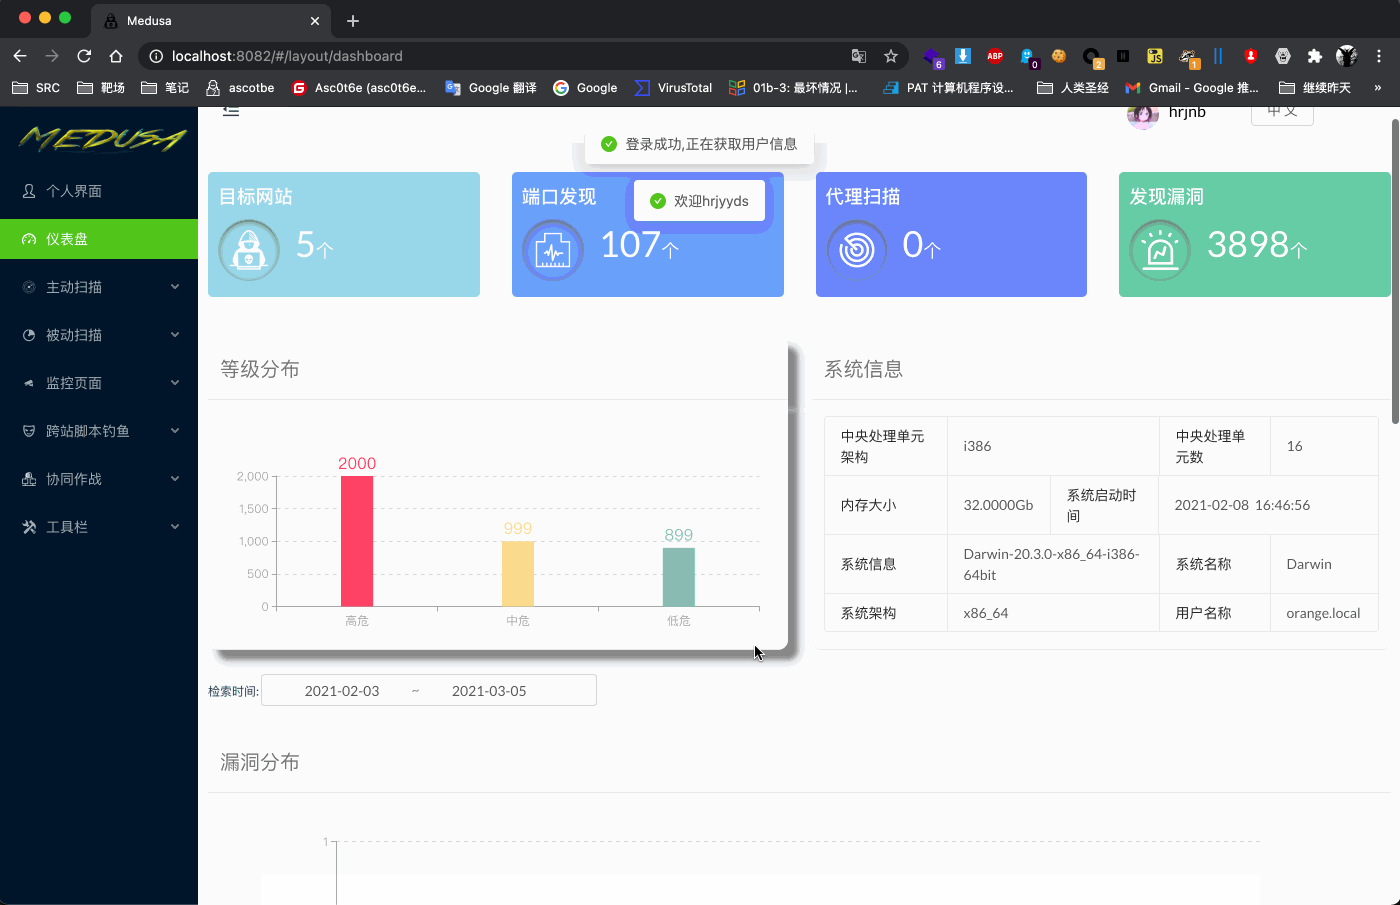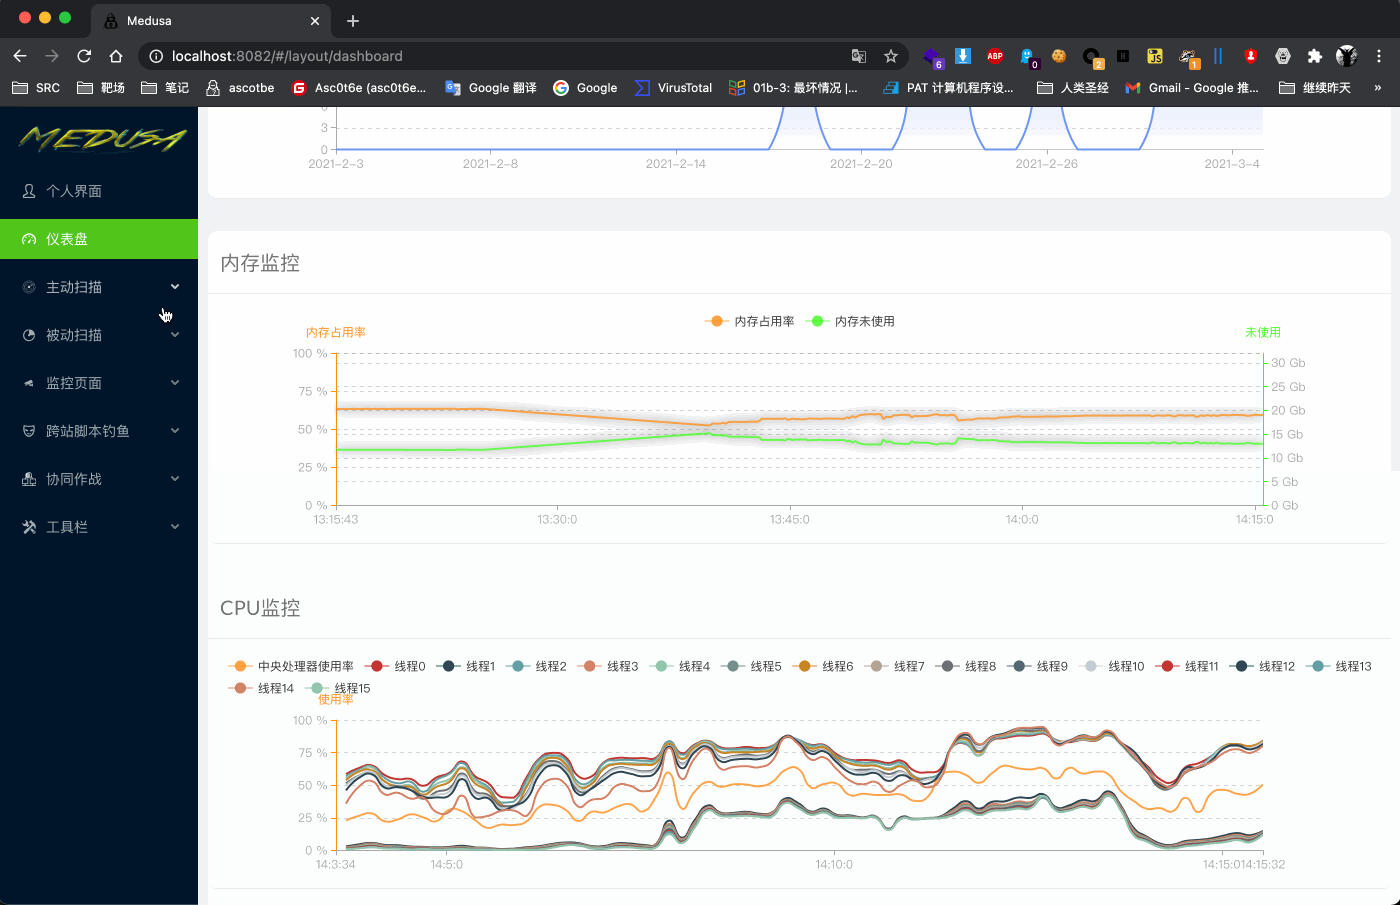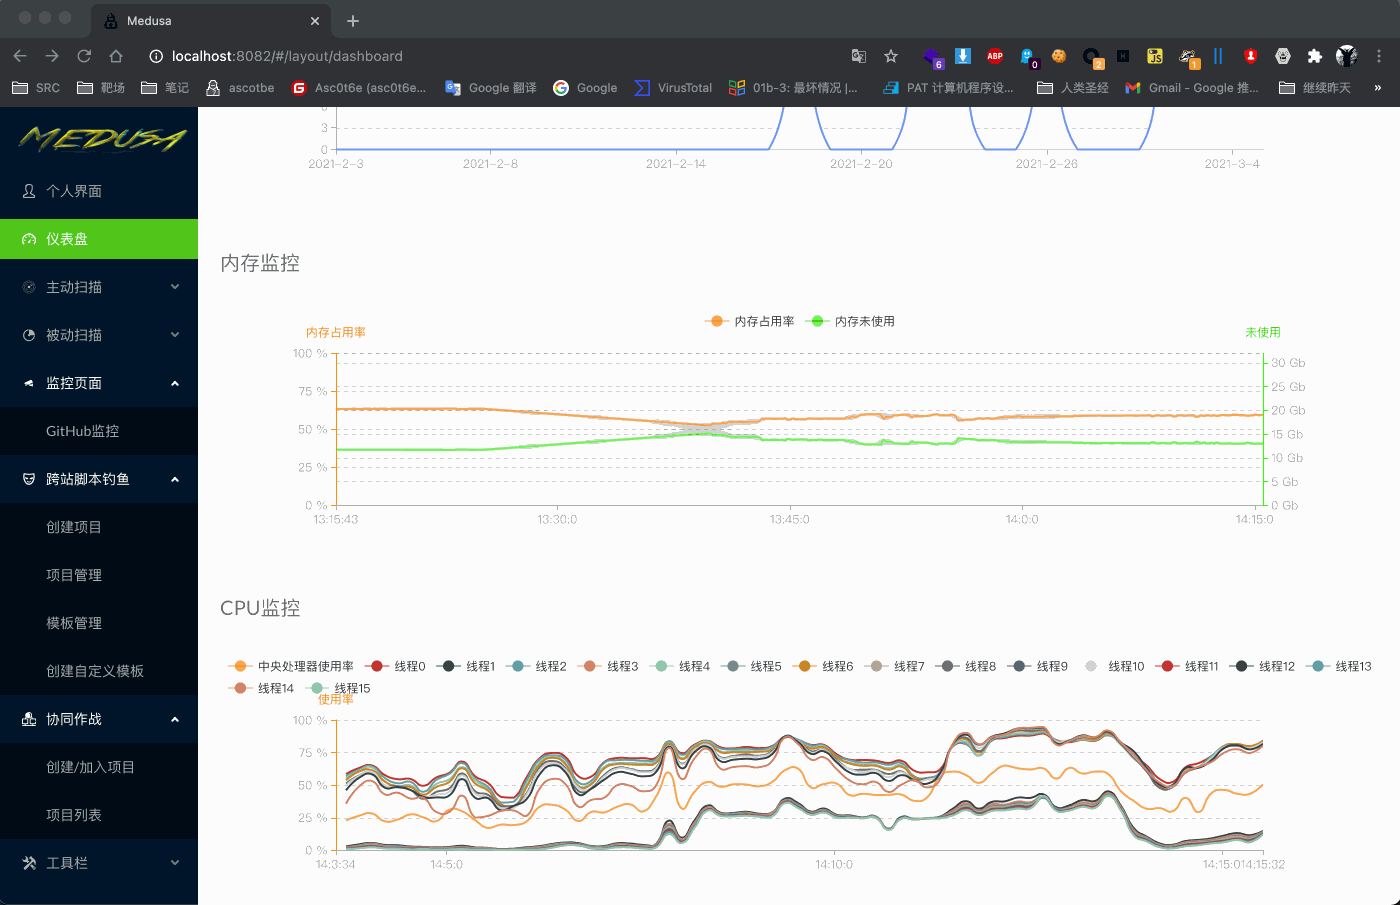
🐈Medusa是一个红队武器库平台,目前包括XSS平台、协同平台、CVE监控、免杀生成、DNSLOG、钓鱼邮件、文件获取等功能,持续开发中

Practice Go programming and implement CobaltStrike's Beacon in Go

A byte code analyzer for finding deserialization gadget chains in Java applications

The Open-Source AWS Cyber Range

exploitdb // The official Exploit-Database repository

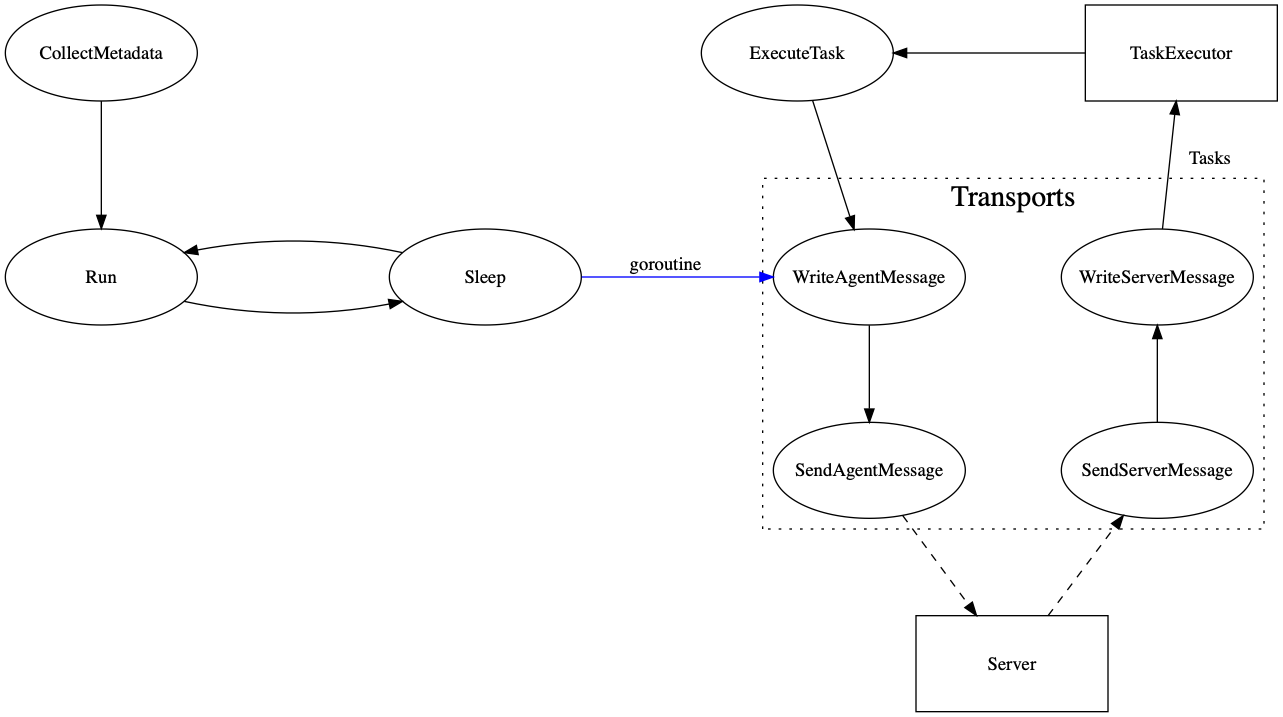
Automating Host Exploitation with AI

Red Team engagement platform with the goal of unifying offensive tools behind a simple UI

Toolkit to weaponize Chromium vulnerabilities into reliable, cross-platform, full-chain exploits

A demonstration of read write using cve-2025-43529 and userland PAC bypass on iOS 26.1

一个针对防御 log4j2 CVE-2021-44228 漏洞的 RASP 工具。 A Runtime Application Self-Protection module specifically designed for log4j2 RCE (CVE-2021-44228) defense.

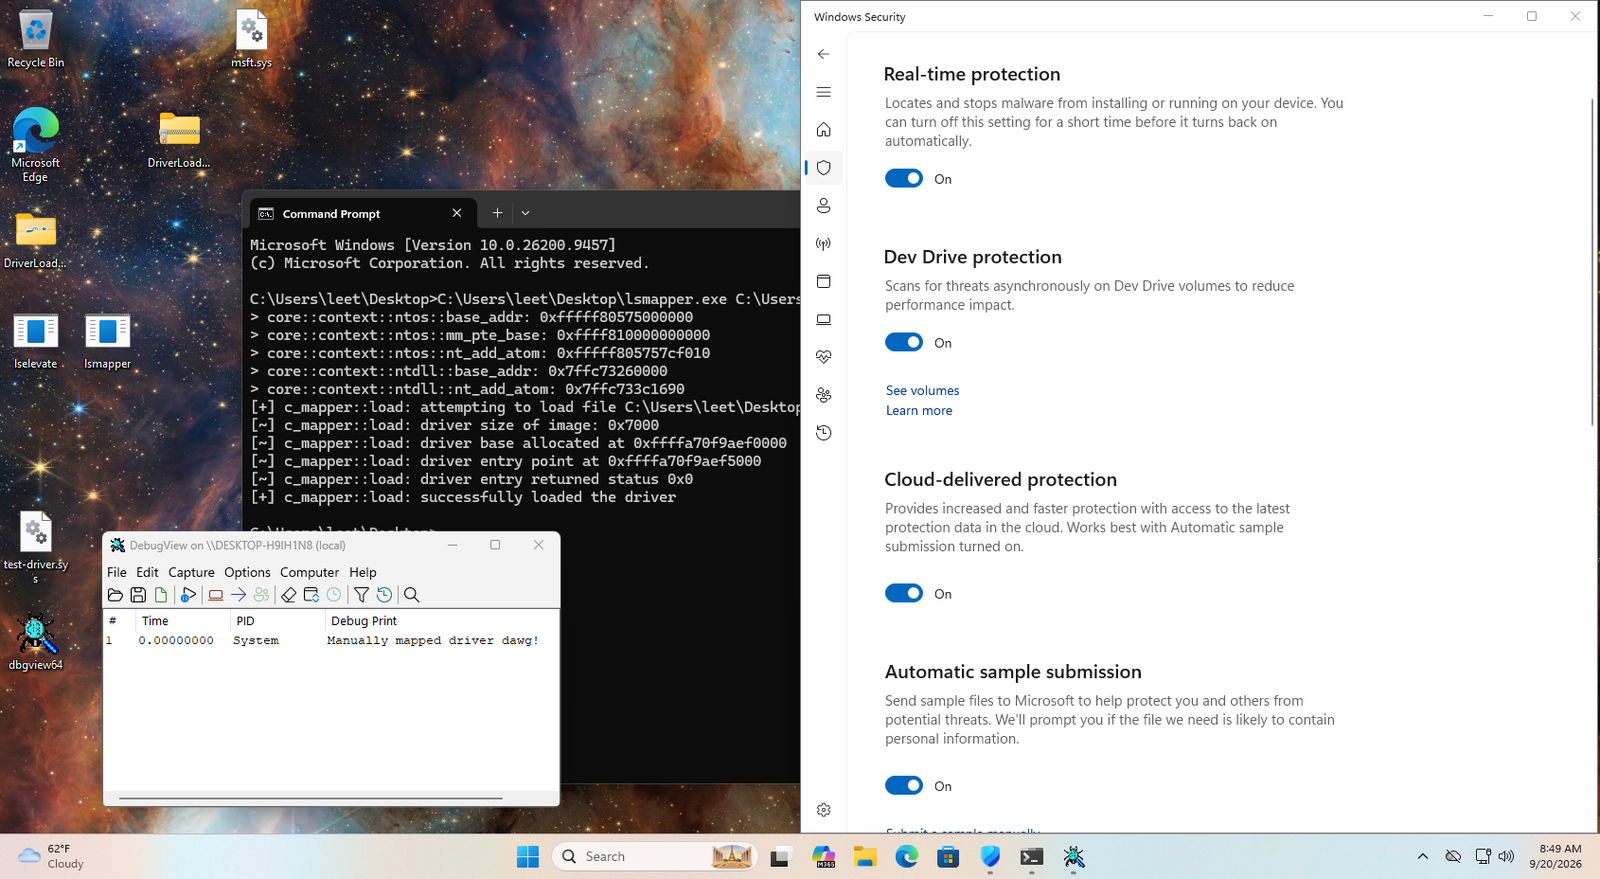
PoC for WinNotify, demonstrated through a driver mapper, and local privilege escalation.

Python-Based Pentesting Framework

Metasploit-Framework modules (scanner and exploit) for the CVE-2021-41773 and CVE-2021-42013 (Path Traversal in Apache 2.4.49/2.4.50)

End-to-end simulation of a Python dependency confusion attack, sudo privilege escalation (CVE-2025-32463), and rootkit-based persistence - with full…