
CVE-2022-30333
 rakhithjk/cve-2022-30333
Generates malicious RAR archives exploiting a path traversal vulnerability in unRAR to plant files at arbitrary locations, demonstrated with a Zimbra…
exploitationexploit-frameworkspayload-generation+3
rakhithjk/cve-2022-30333Generates malicious RAR archives exploiting a path traversal vulnerability in unRAR to plant files at arbitrary locations, demonstrated with a Zimbra…
 jjjjjjjj987/cve-2023-45866-py
Python-based proof-of-concept for CVE-2023-45866, a Bluetooth vulnerability, demonstrating exploitation techniques for security research and testing.
 luckythandel/cve-2021-4034
This is a POC for the vulnerability found in polkit's pkexec binary which is used to run programs as another users.
 krizzz07/cve-2020-0796
windows 10 SMB vulnerability
 ayoub-elbouzi/cve-2021-4034-pwnkit
PoC for PwnKit: Local Privilege Escalation Vulnerability in polkit’s pkexec (CVE-2021-4034)
 squirre17/cve-2021-4034
polkit-pkexec local privilege escalation vulnerability
 certologists/modified-cve-2024-37081-poc
Proof of concept for VMware vCenter CVE-2024-37081, modified to enhance usability for security testing and validation of the vulnerability.
 sornram9254/cve-2022-38577-processmaker
ProcessMaker before v3.5.4 was discovered to contain insecure permissions in the user profile page. This vulnerability allows attackers to escalate…
 shinthink/pbck-exploit
📤 Mass exploitation framework for CVE-2026-56290 — Page Builder CK Joomla unauthenticated file upload to RCE
 xn0kkx/cve-2026-31431_copyfail_linuxkernel_lpe
Educational rewrite of the Copy Fail PoC (CVE-2026-31431) — Linux kernel LPE via algif_aead in-place crypto + splice() page-cache write

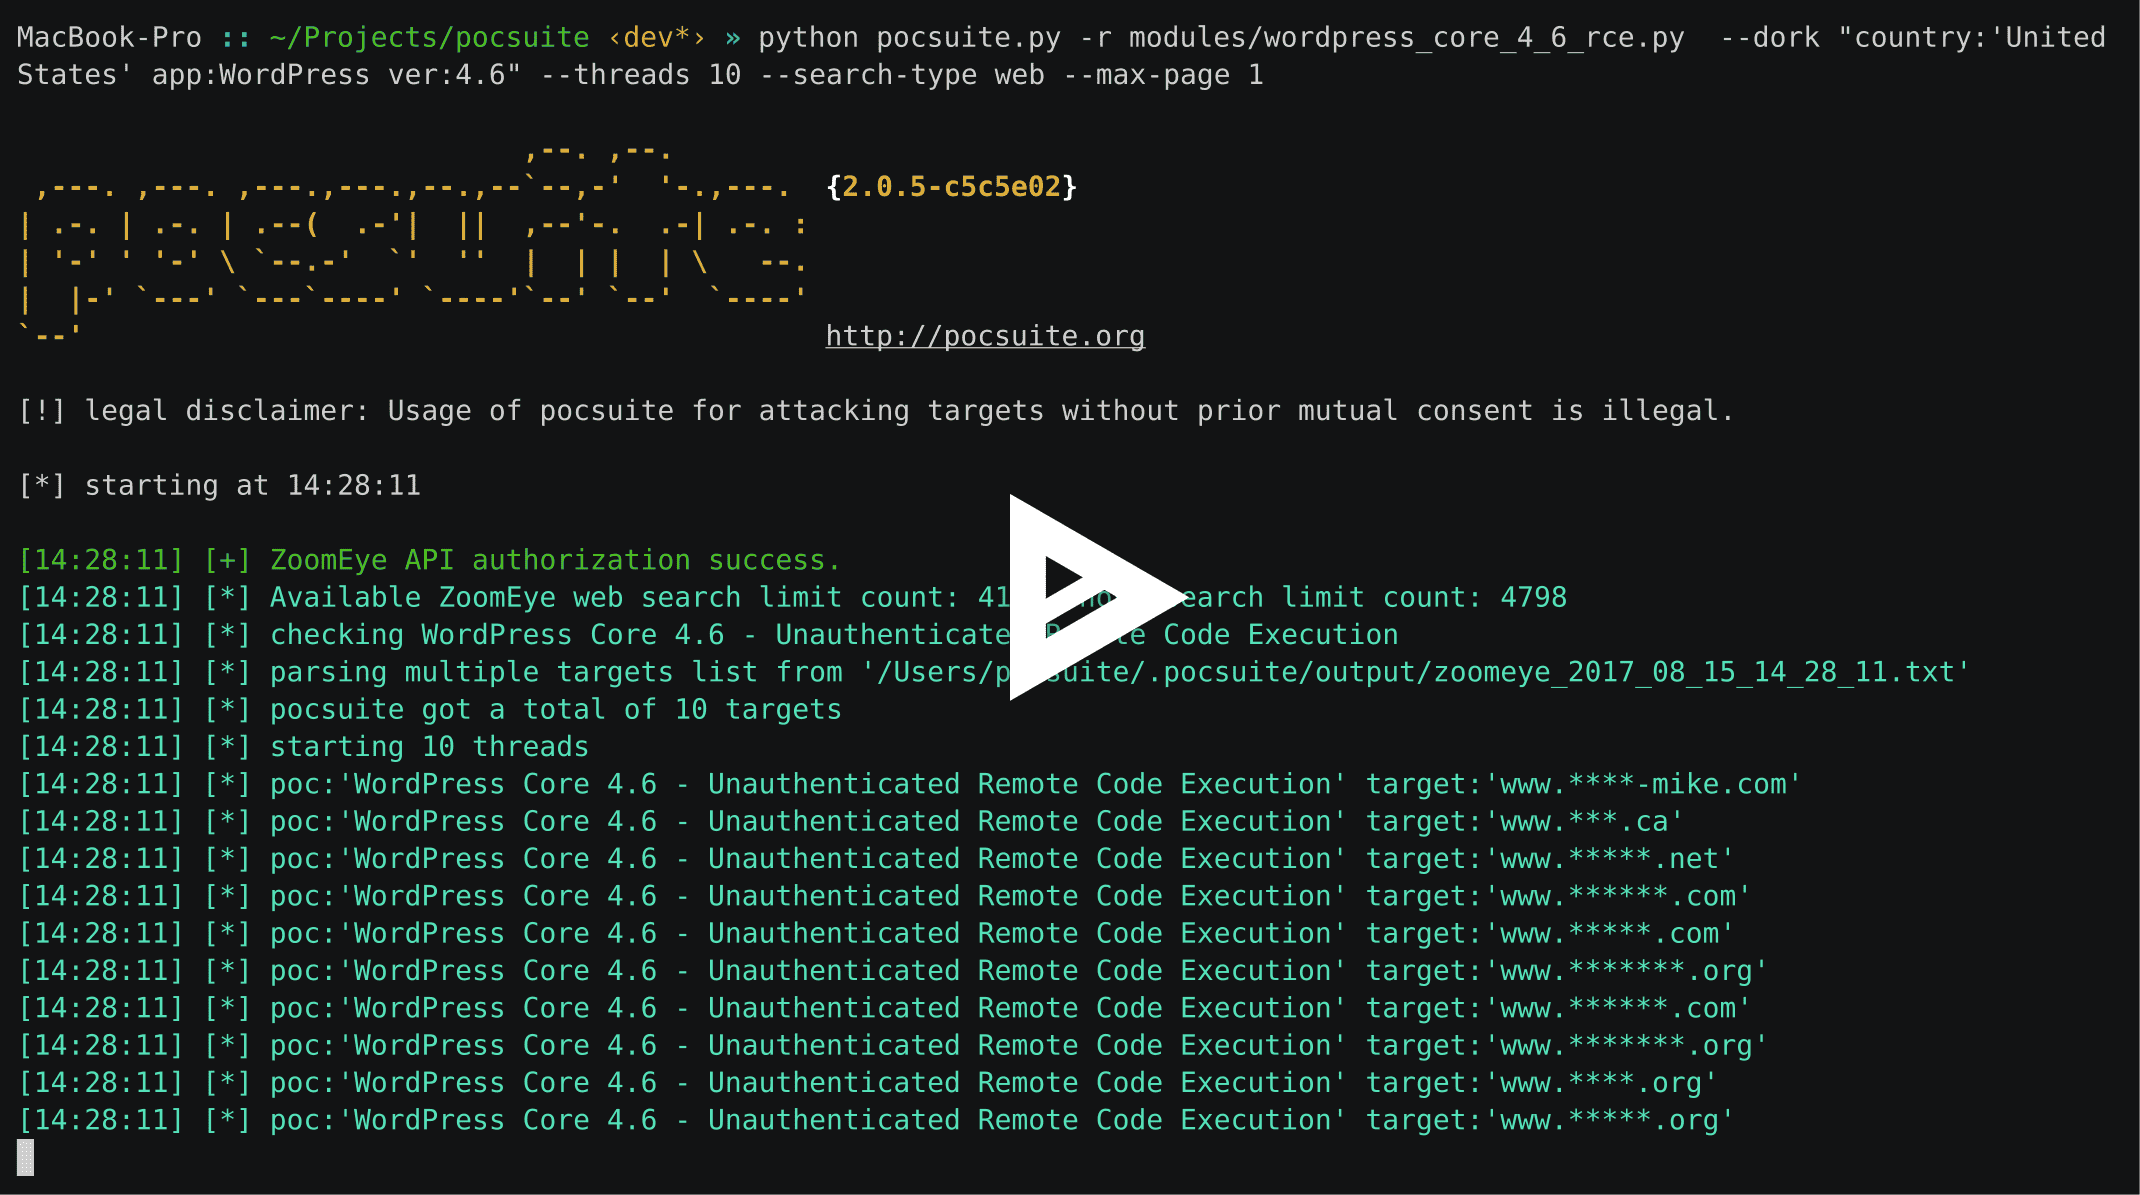 knownsec/pocsuite
This project has stopped to maintenance, please to https://github.com/knownsec/pocsuite3 project.
 deimosc2/deimosc2
DeimosC2 is a Golang command and control framework for post-exploitation.
 zeze-zeze/ioctlance
A tool that is used to hunt vulnerabilities in x64 WDM drivers
 mazen160/shennina
Automating Host Exploitation with AI
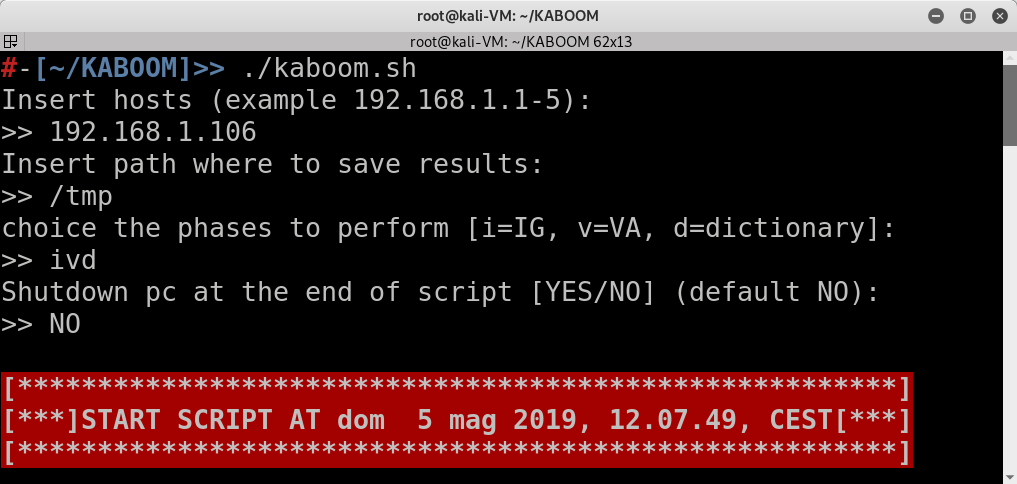 leviathan36/kaboom
A tool to automate penetration tests
 0x09al/cve-2017-11882-metasploit
This is a Metasploit module which exploits CVE-2017-11882 using the POC released here : https://embedi.com/blog/skeleton-closet-ms-office-vulnerabilit…