HFS_EXPLOIT_PROJECT
 sage954526/hfs_exploit_project
Metasploit RCE on HFS 2.3 - CVE-2014-62
educationexploit-frameworkspenetration-testing+3
sage954526/hfs_exploit_projectMetasploit RCE on HFS 2.3 - CVE-2014-62
optiv/scarecrowScareCrow - Payload creation framework designed around EDR bypass.
 purpleailab/decepticon
Autonomous Hacking Agent for Red Team
 adaptix-framework/adaptixc2
AdaptixC2 is a highly modular advanced redteam toolkit
 funnywolf/viper
Adversary simulation and Red teaming platform with AI

 t3l3machus/villain
Villain is a high level stage 0/1 C2 framework that can handle multiple reverse TCP & HoaxShell-based shells, enhance their functionality with…
 owtf/owtf
Modular penetration testing framework integrating multiple tools for automated web application security assessment, aligned with OWASP Testing Guide,…
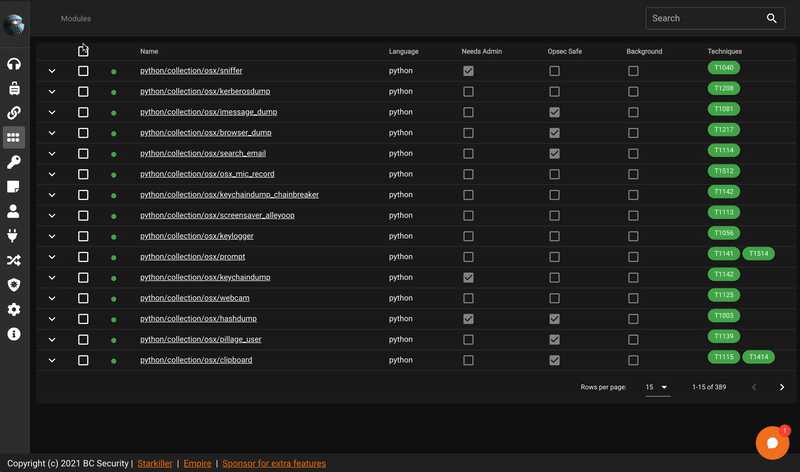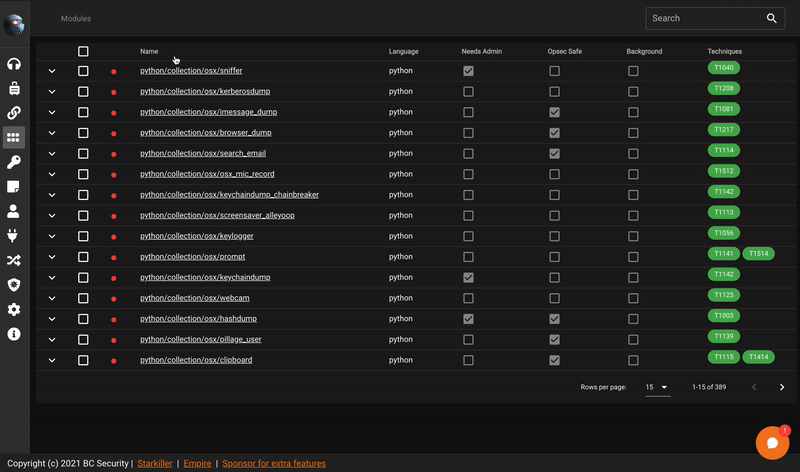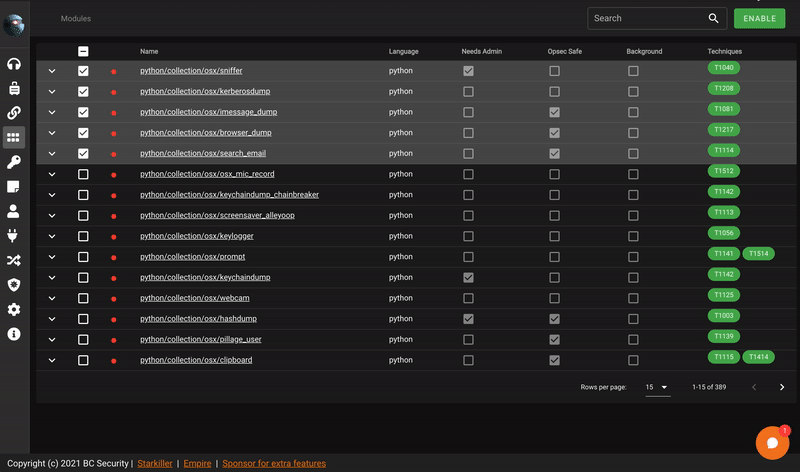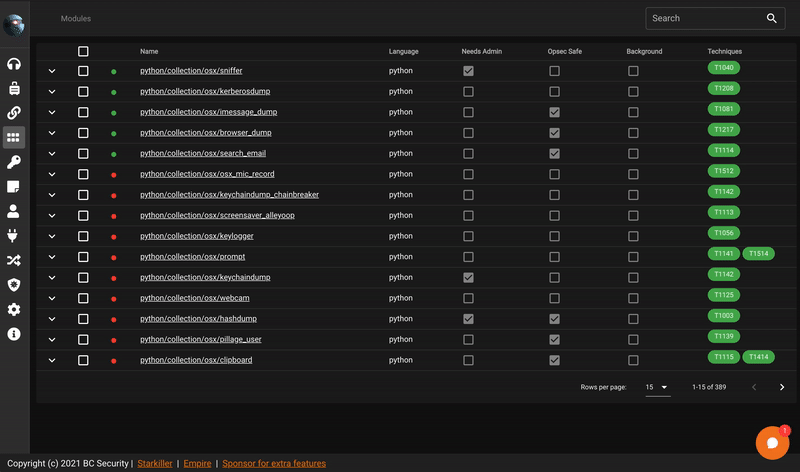 bc-security/starkiller
Starkiller is a Frontend for PowerShell Empire.
 klezvirus/inceptor
Template-Driven AV/EDR Evasion Framework
 cn33liz/p0wnedshell
PowerShell Runspace Post Exploitation Toolkit
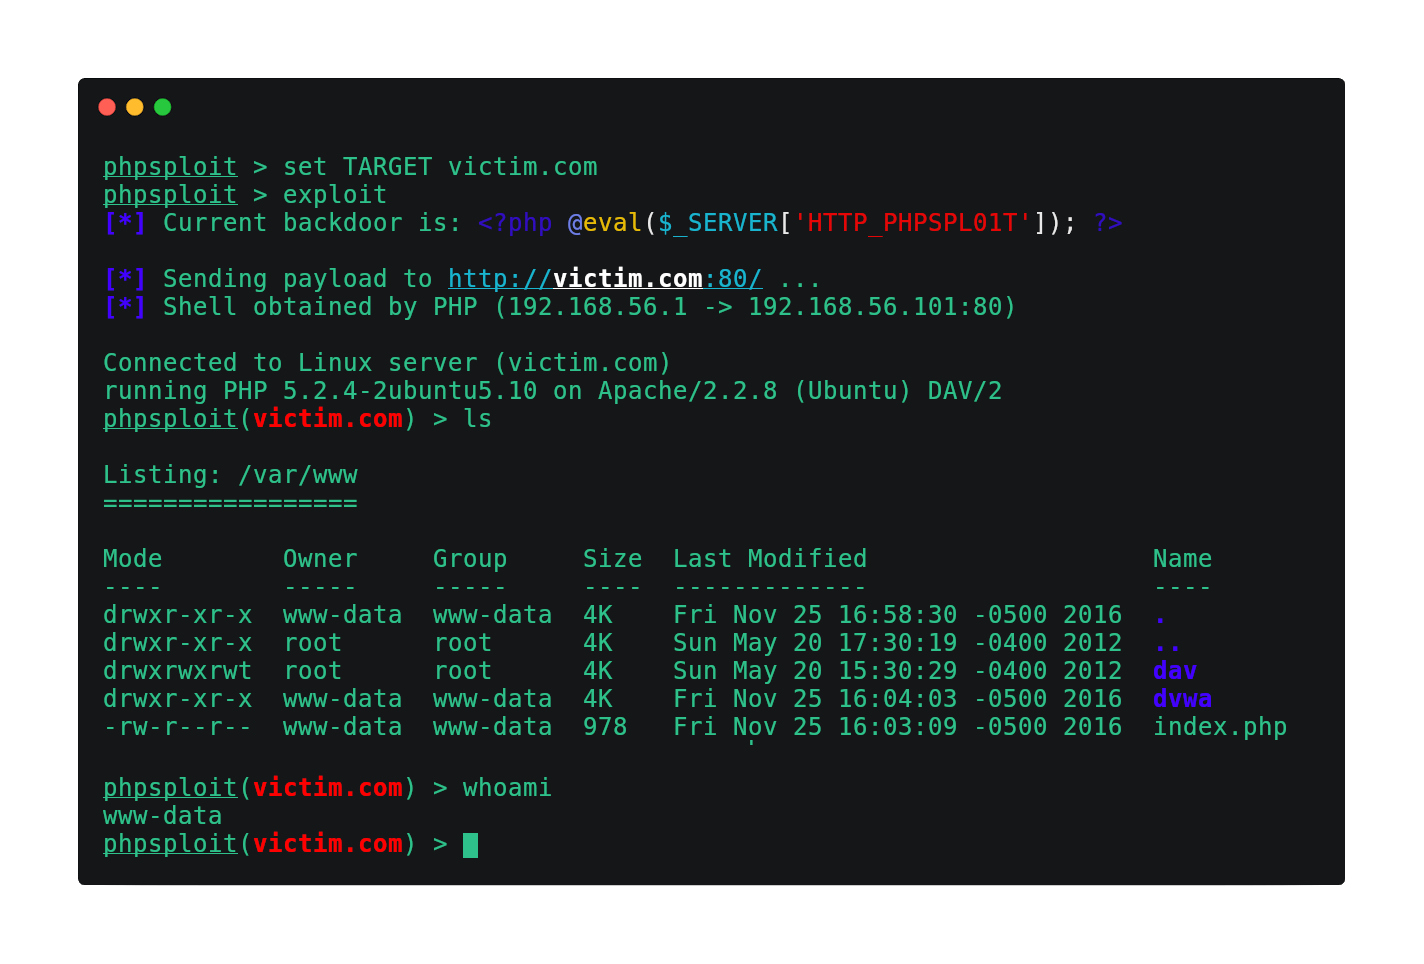 nil0x42/phpsploit
Full-featured C2 framework which silently persists on webserver with a single-line PHP backdoor
 gloxec/crossc2
generate CobaltStrike's cross-platform payload
 bhassani/eternalbluec
EternalBlue suite remade in C/C++ which includes: MS17-010 Exploit, EternalBlue vulnerability detector, DoublePulsar detector and DoublePulsar…
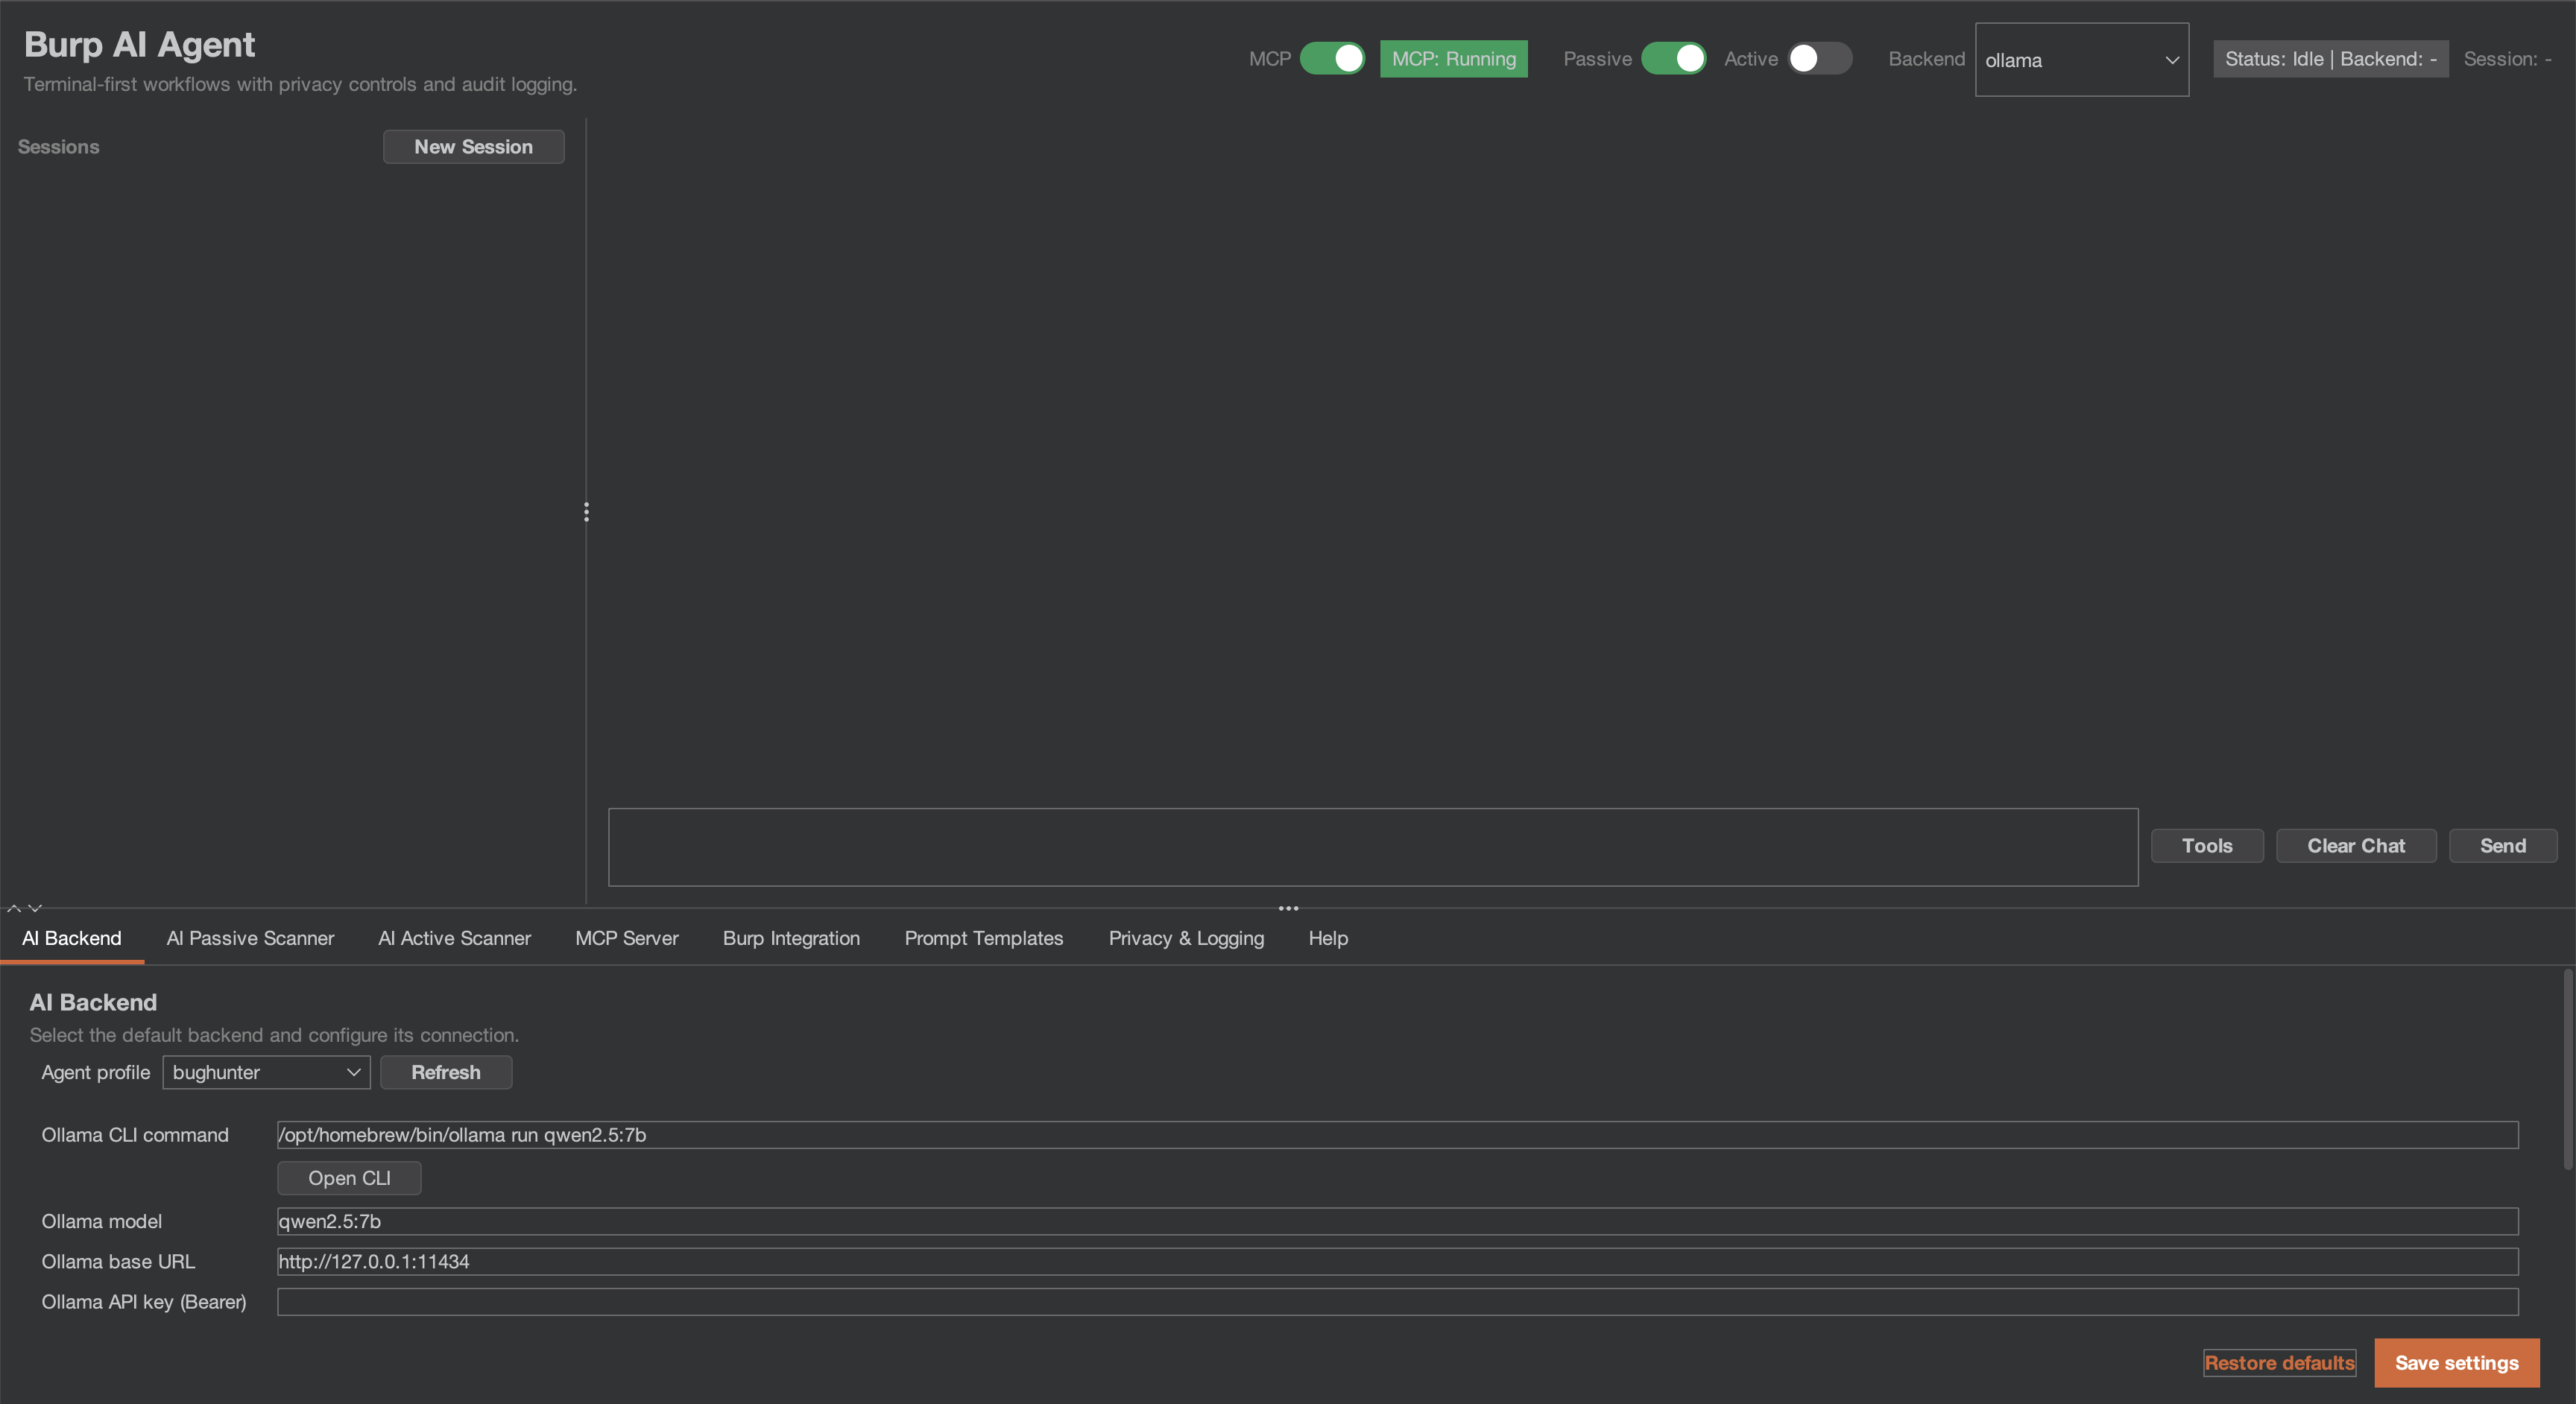 six2dez/burp-ai-agent
Burp Suite extension that adds built-in MCP tooling, AI-assisted analysis, privacy controls, passive and active scanning and more
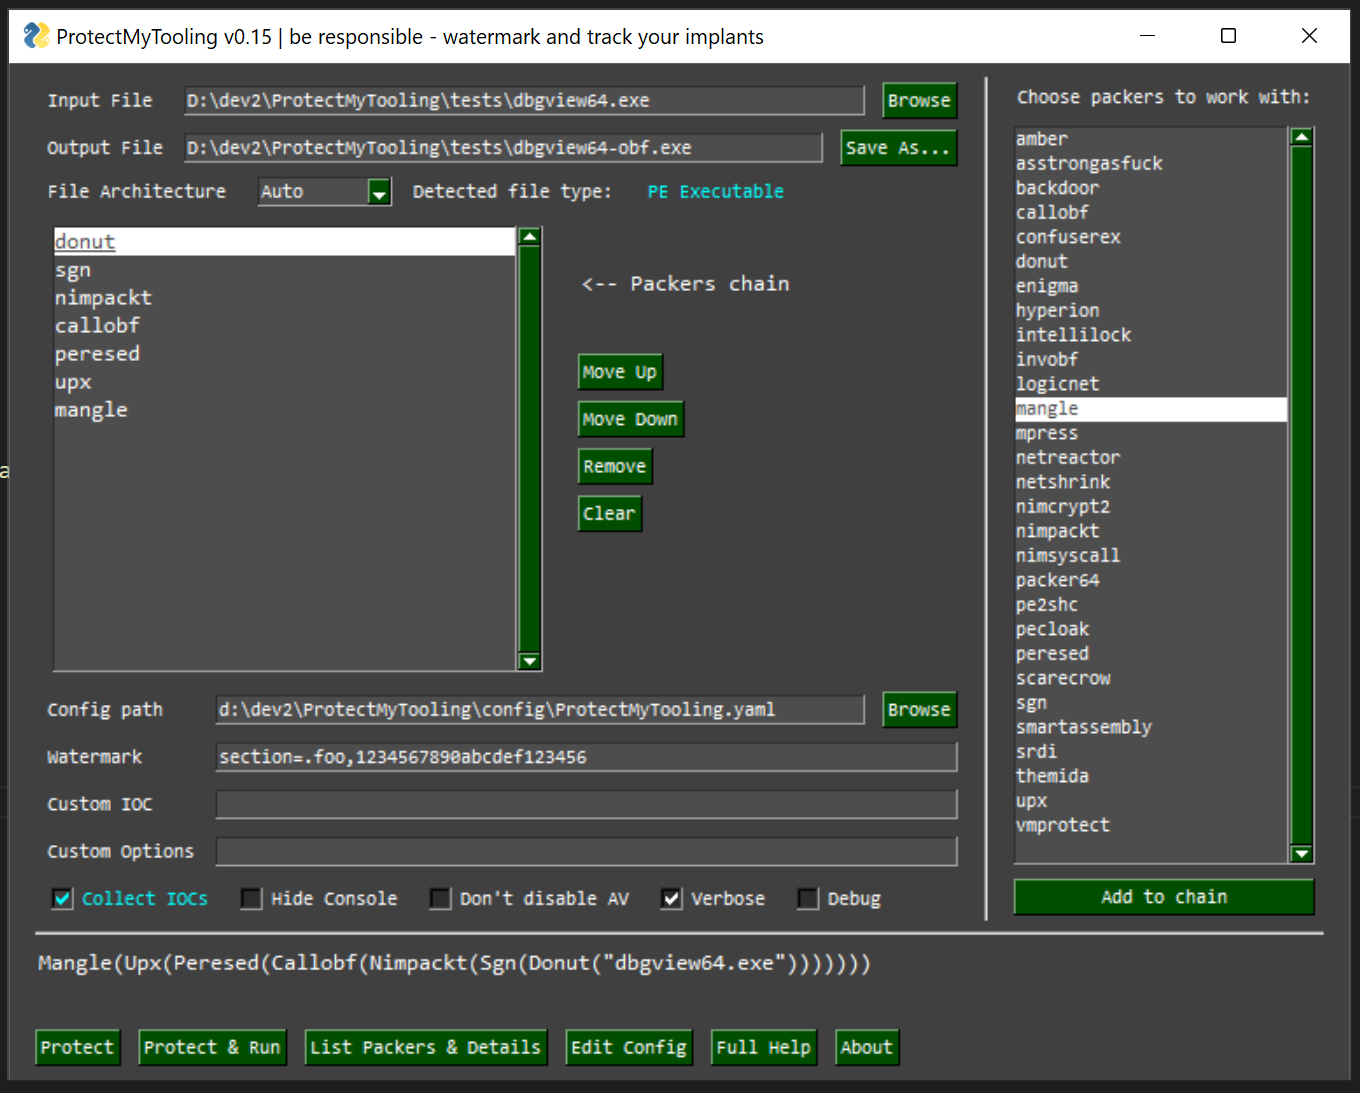 mgeeky/protectmytooling
Multi-Packer wrapper letting us daisy-chain various packers, obfuscators and other Red Team oriented weaponry. Featured with artifacts watermarking,…
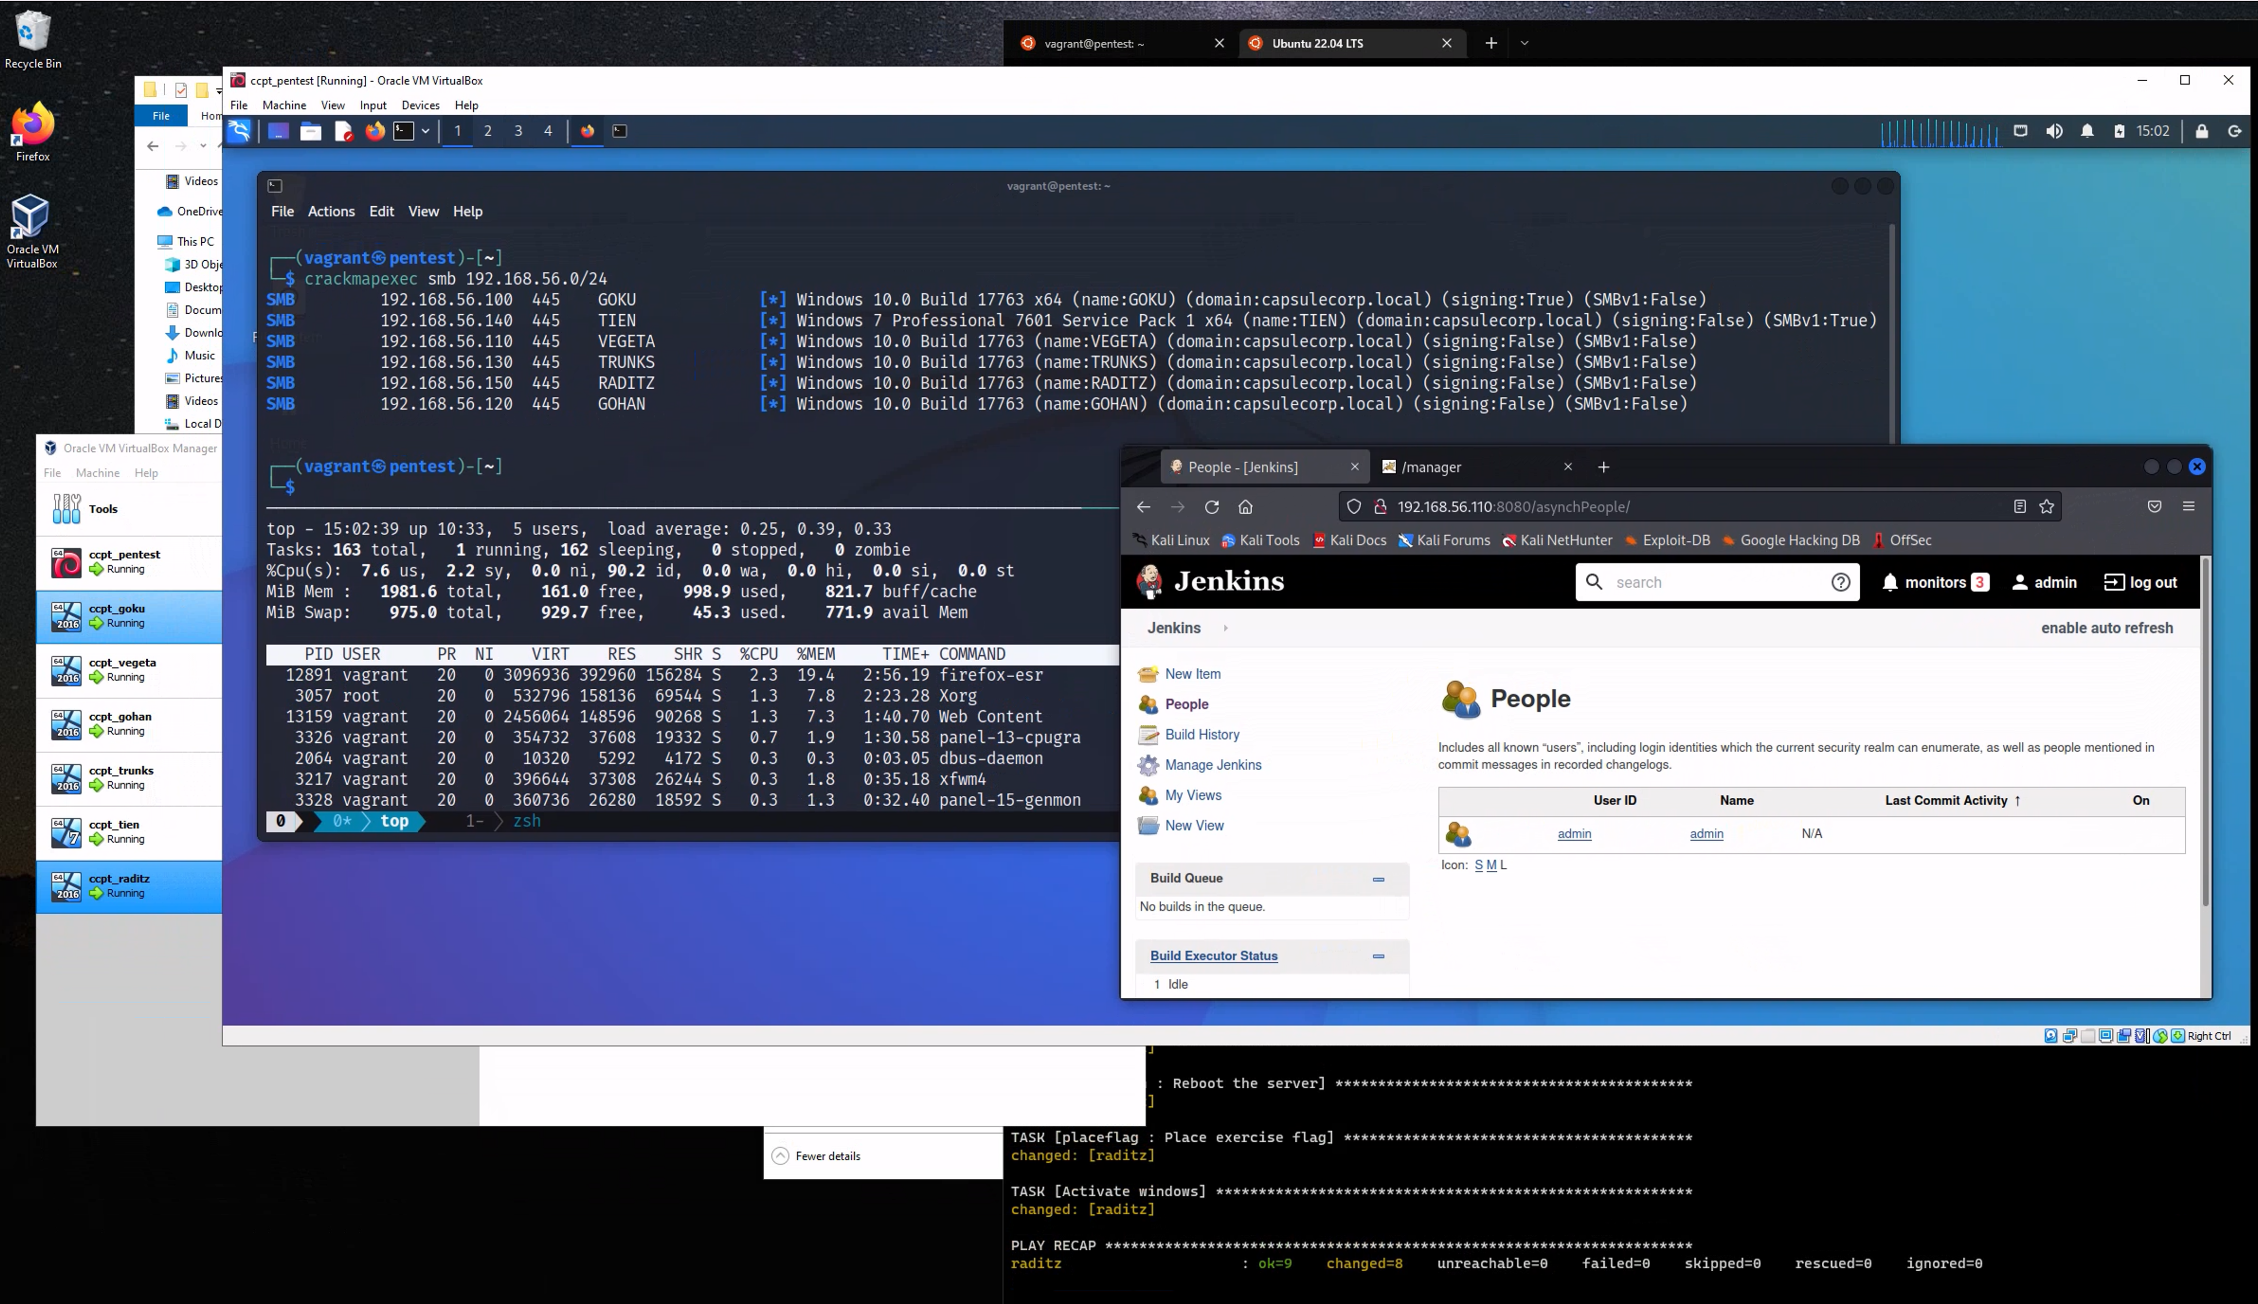 r3dy/capsulecorp-pentest
Vagrant VirtualBox environment for conducting an internal network penetration test
 sia-iotechnology/kittysploit-framework
Python Exploitation Framework, V8 Engine Debugger, Proxy interceptor, marketplace, post-exploitation, backdoor generator,....