PoC-CVE-2025-62222
 sadisticnight/poc-cve-2025-62222
Proof-of-concept demonstrating remote code execution via prompt injection in GitHub Copilot Chat, using a crafted Python file to trigger a…
command-and-controleducationexploit-frameworks+7
1
sadisticnight/poc-cve-2025-62222Proof-of-concept demonstrating remote code execution via prompt injection in GitHub Copilot Chat, using a crafted Python file to trigger a…
 sastraadiwiguna-purpleeliteteaming/llamastack-rce-deterministic-supply-chain-exploitation-hardening-framework-cve-2024-50050-
LlamaStack-RCE: Deterministic Supply Chain Exploitation & Hardening Framework [CVE-2024-50050] Focus on AI Security Research…
 4nuxd/react2shell
R2S is a comprehensive exploitation and post-exploitation framework targeting the Next.js React Server Components vulnerability (CVE-2025-55182). It…
 simoesctt/ctt-proxylogon-rce-v1.0---convergent-time-theory-enhanced-microsoft-exchange-exploit
An advanced exploit for Microsoft Exchange Server (CVE-2021-26855, CVE-2021-27065) enhanced with Convergent Time Theory principles, achieving…
 ready2disclose/cve-2022-31491
CVE-2022-31491
 nulltrace1336/samba-exploit-cve-2007-2447
Step-by-step guide to exploiting Samba 3.0.20 (CVE-2007-2447) using Metasploit, including Nmap scanning, payload setup, and reverse shell execution.
 mefulton/cve-2018-11510
Just a couple exploits for CVE-2018-11510
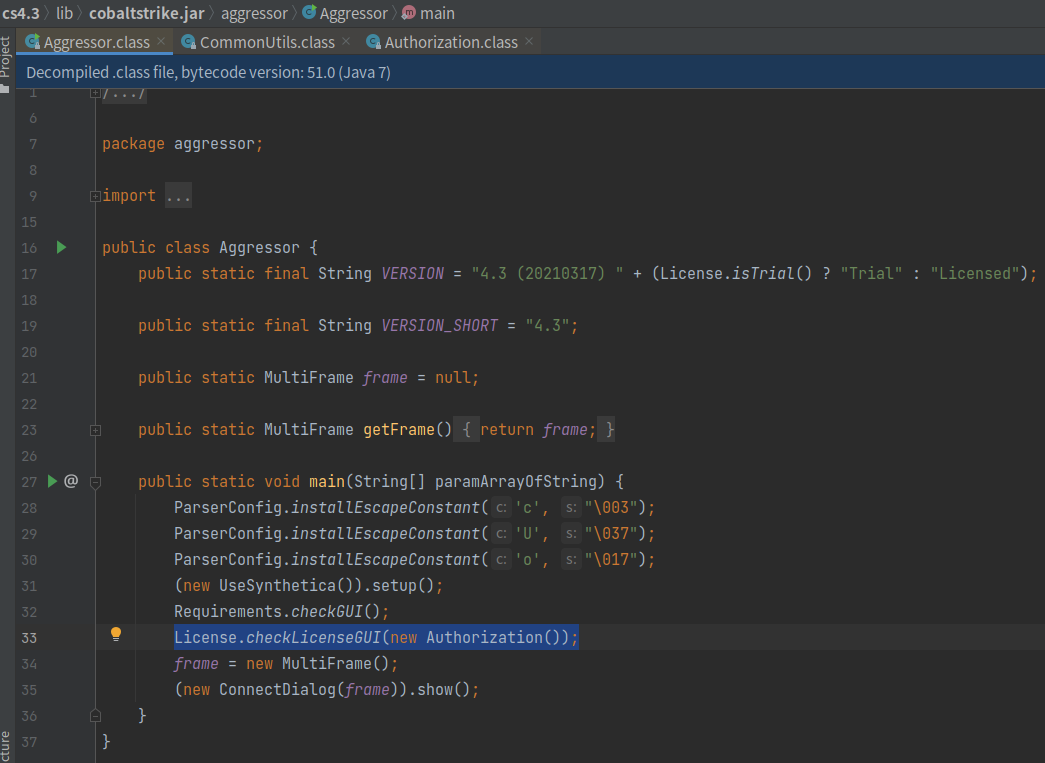 zeoday/cobaltstrike4.5_cdf-1
cobaltstrike4.5版本破/解、去除checksum8特征、bypass BeaconEye、修复错误路径泄漏stage、增加totp双因子验证、修复CVE-2022-39197等
 s-retlaw/l4s_poc
Log4Shell (Cve-2021-44228) Proof Of Concept

 vqkro/ultrasploiter
A single binary that folds a port scanner, the full Exploit-DB index (47k entries) and runnable exploit modules into one tool. Written in Rust, runs…
 zerx0r/kage
Kage is Graphical User Interface for Metasploit Meterpreter and Session Handler
 havocframework/havoc
The Havoc Framework
 rapid7/metasploit-payloads
Unified repository for different Metasploit Framework payloads
 markoarmitage/metasploit-framework
app turn nil publics and privates into blanks 3 months ago config Use bundler/setup for more graceful bundler related failures 11 days ago data…
 veil-framework/veil
Veil 3.1.X (Check version info in Veil at runtime)
 spiderlabs/msfrpc
Perl/Python modules for interfacing with Metasploit MSGRPC
 veil-framework/veil-evasion
Veil Evasion is no longer supported, use Veil 3.0!