
PEASS-ng
 peass-ng/peass-ng
PEASS - Privilege Escalation Awesome Scripts SUITE (with colors)
educationexploitationexploit-frameworks+7
peass-ng/peass-ngPEASS - Privilege Escalation Awesome Scripts SUITE (with colors)
 sgswzglwlx/vivo-root-build
Builds a root exploit for vivo/iQOO devices targeting CVE-2026-43499, leveraging kernel techniques like KASLR bypass and CFI manipulation to achieve…
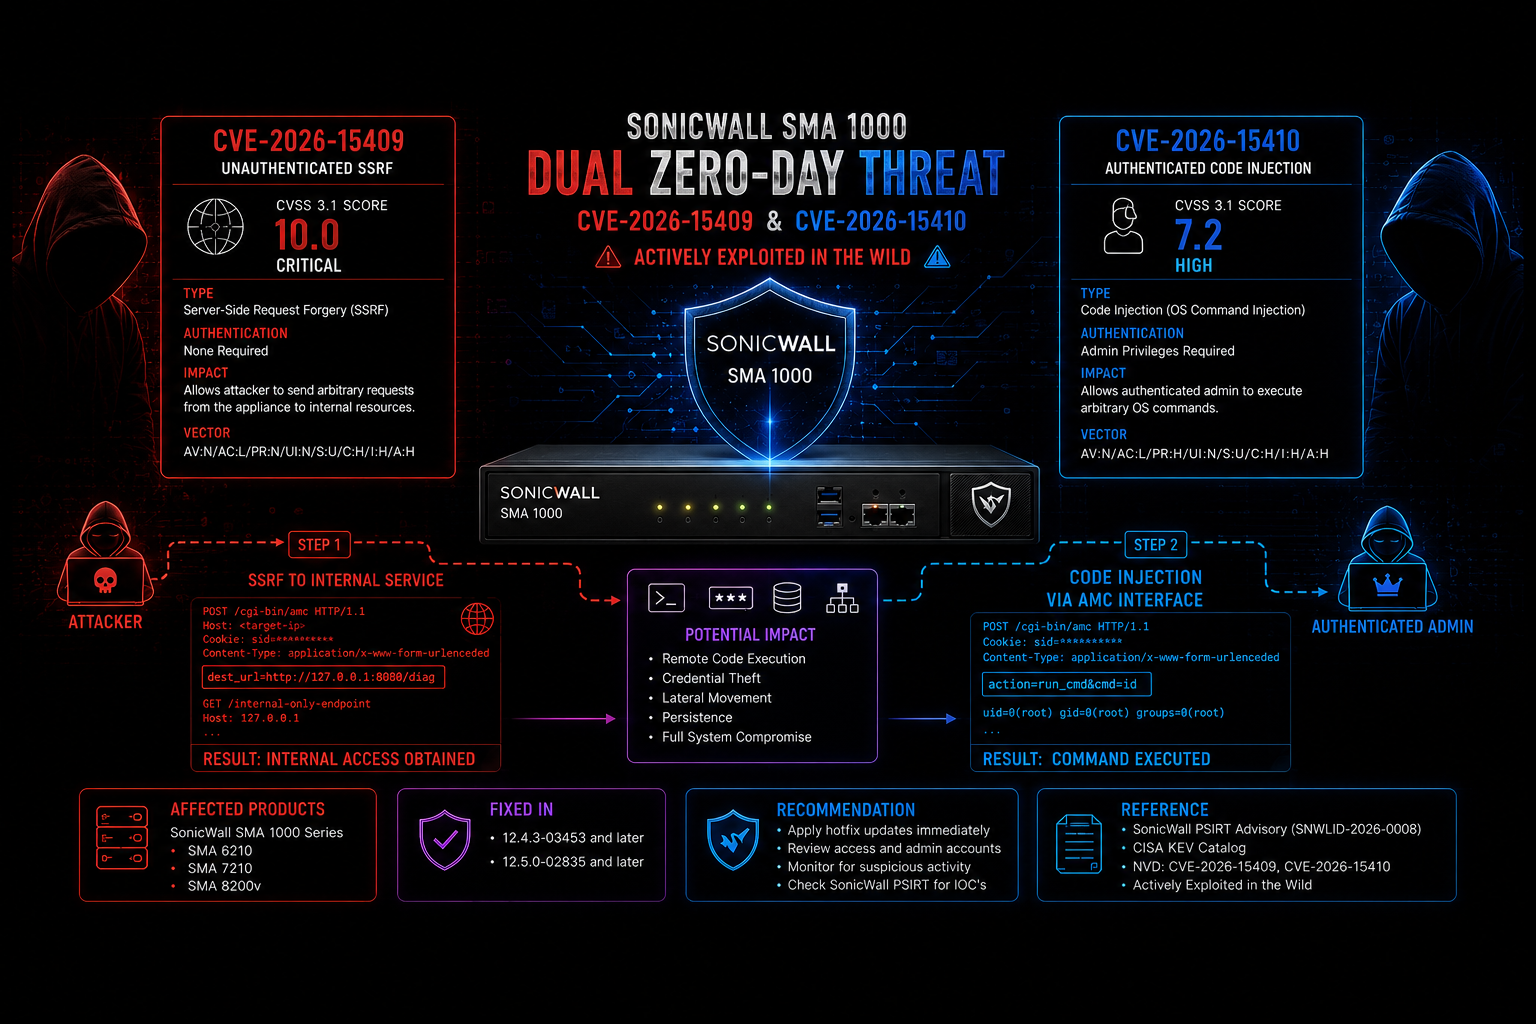 tc4dy/cve-2026-15409-15410-framework
Multi-exploit framework for SonicWall SMA1000 chaining SSRF (CVE-2026-15409) to Erlang RCE and root privilege escalation (CVE-2026-15410). Features…
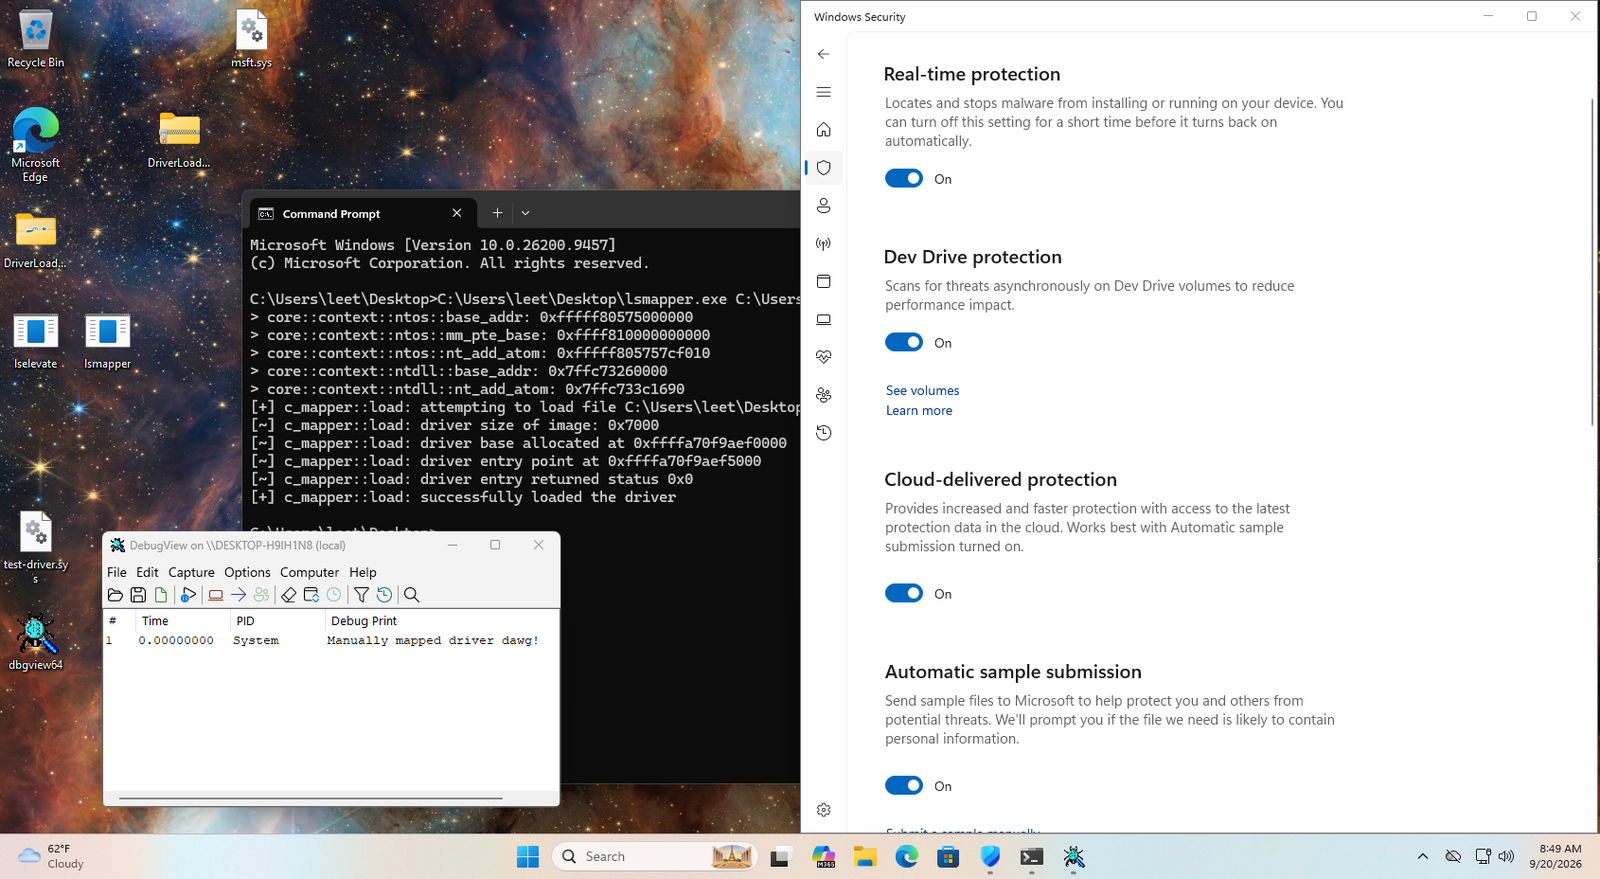 nbs32k/localstranger
PoC for WinNotify, demonstrated through a driver mapper, and local privilege escalation.
 oopnv70-lab/ghostlock-aak-apk
GhostLock AAK Launcher - CVE-2026-43499 Linux kernel rtmutex stack UAF local privilege escalation trigger (GPLv3)
 lsposed/lspromise
Android complete exploit chain that enables privilege escalation from a local untrusted app to root/kernel, combination of CVE-2026-49881 and…
 s1eezer/cve-2026-8069
Technical write-up and proof-of-concept for CVE-2026-8069, a local privilege escalation in Acer NitroSense and PredatorSense services, exploiting a…
 dbgbgtf1/cve-2026-40369-exploit
Exploit for CVE-2026-40369 that leverages kernel address leak and token forging to achieve privilege escalation in a browser sandbox environment.
 0b0111100/2009
Collection of Linux kernel exploits targeting CVE-2009-1185, CVE-2009-1337, CVE-2009-2692, CVE-2009-2698, and CVE-2009-3547, providing…
 0b0111100/2008
Linux kernel exploit implementations targeting CVE-2008-0600, CVE-2008-0900, and CVE-2008-4210, providing proof-of-concept code for privilege…
 0b0111100/2006
Linux kernel privilege escalation exploits targeting CVE-2006-2451 and CVE-2006-3626, providing proof-of-concept code for local privilege escalation…
 0b0111100/2005
Linux kernel exploit implementations targeting CVE-2005-0736 and CVE-2005-1263, providing proof-of-concept code for privilege escalation on…
 0b0111100/2004
Linux kernel privilege escalation exploits targeting CVE-2004-0077 and CVE-2004-1235, including caps_to_root technique for gaining root access.
 hackspeak/cve-2026-62735
Local privilege escalation exploit for Windows HTTP.sys integer overflow (CVE-2026-62735), demonstrating crash and full SYSTEM shell via nonpaged…
 cxyofficial/k50g-pocof4gt-cve-2026-43499-poc
Local privilege escalation exploit for Redmi K50G/POCO F4 GT using CVE-2026-43499 (futex UAF) to gain temporary root and load KernelSU without…
 lkeld/cve-2026-43499-poc
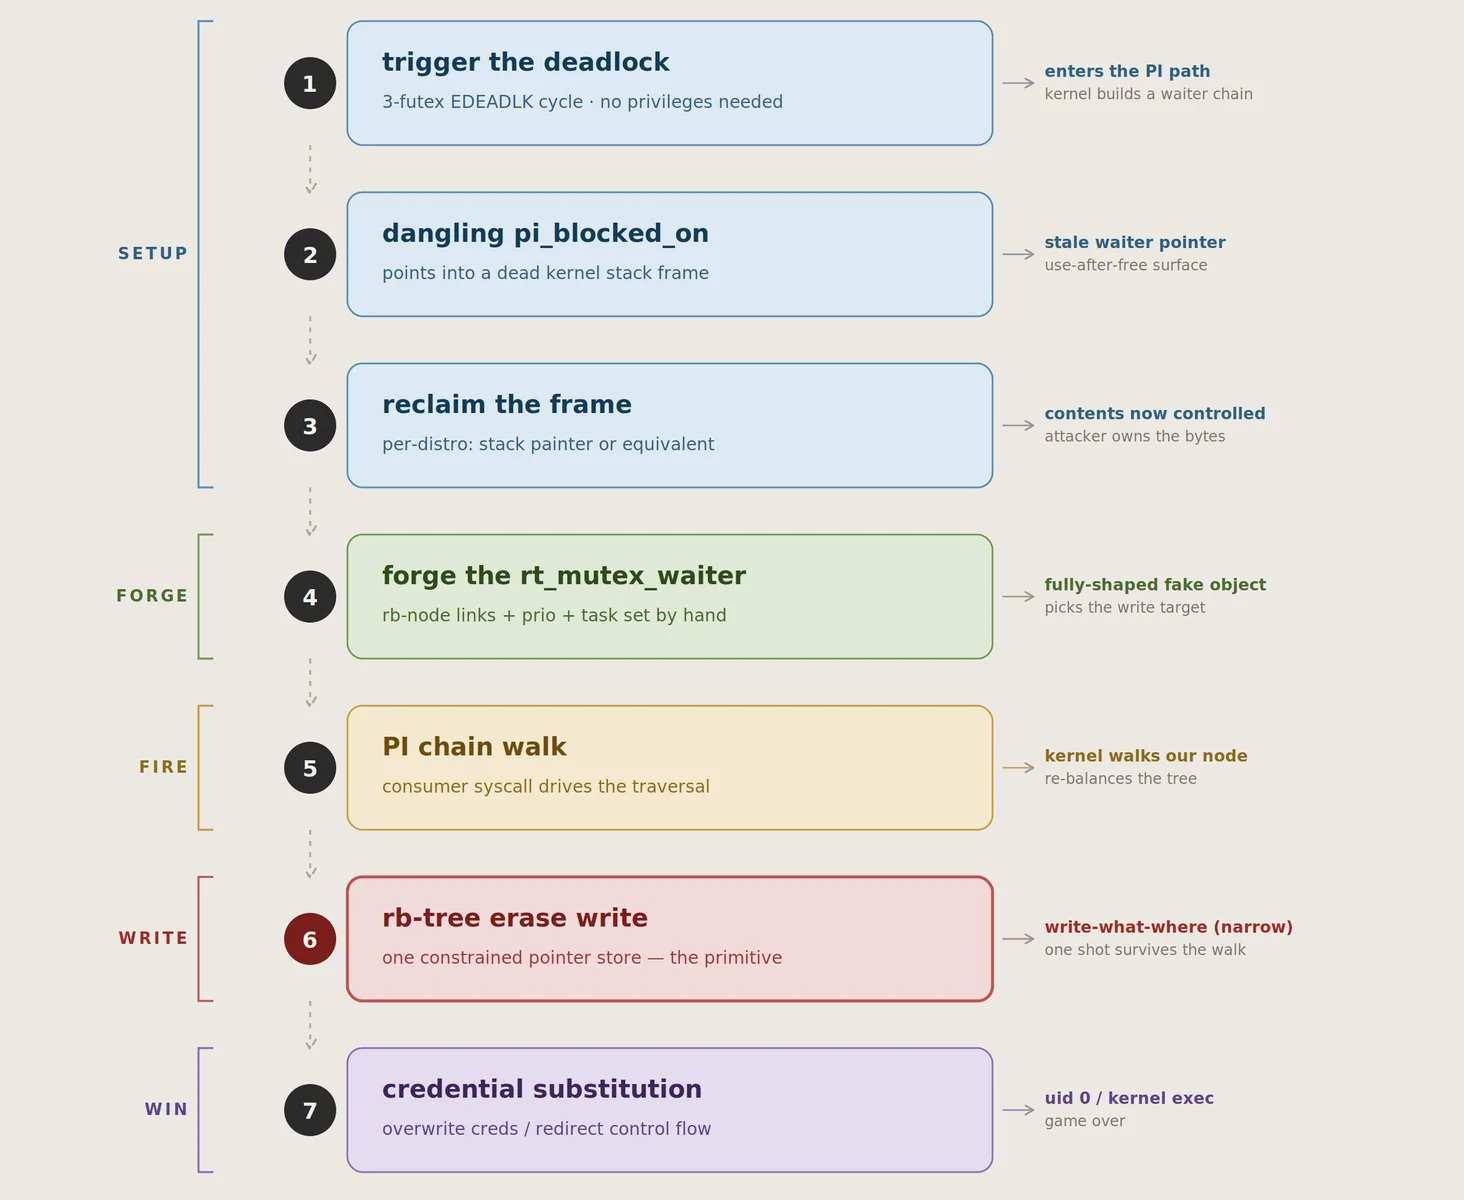
Weaponized proof-of-concept for CVE-2026-43499 (GhostLock), a Linux kernel rtmutex bug enabling local privilege escalation. Includes per-distribution…
 r3dw4n48m3d/cve-2021-3493-exploit
C-based local privilege escalation exploit for CVE-2021-3493, targeting OverlayFS in Linux kernels prior to 5.11. Provides compilation and usage…
 kongqbin/cve-2016-5195
Educational implementation of the Dirty COW (CVE-2016-5195) privilege escalation exploit, including race condition payload and SUID-based root shell…