

angr
 angr/angr
A powerful and user-friendly binary analysis platform!
ai-assisted-reversingbinary-analysisbinary-exploitation+12
9.1k2h 17m ago
angr/angrA powerful and user-friendly binary analysis platform!
 gadievron/raptor
Autonomous security research framework integrating static analysis, binary analysis, fuzzing, LLM-powered vulnerability validation, exploit…
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 newazbenalam/root-my-galaxy-payloads
Device-specific CVE-2026-43499 root payloads and KernelSU artifacts for Samsung Galaxy models, with firmware profiles, exploit source, and a support…
 aipentest/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
 ed1s0nz/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
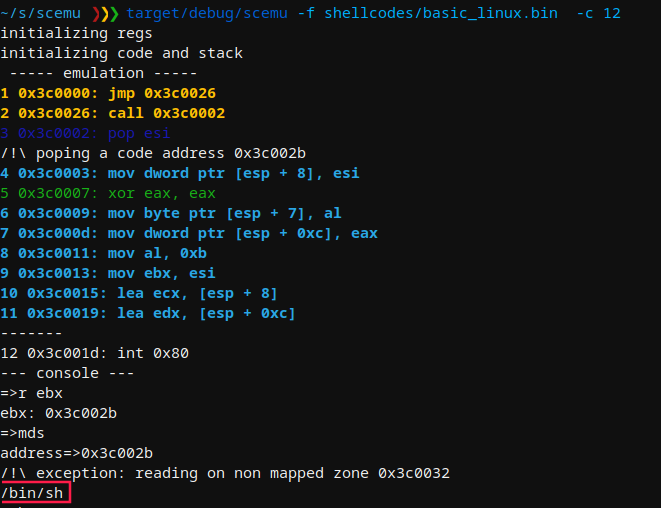 mwemuorg/mwemu
Pure Rust x86 hardware emulator and Windows process simulator for malware analysis, shellcode emulation, and payload unpacking. Supports 32/64-bit PE…
 yukonga/ghostlock-app
GhostLock One-Tap Execution App (CVE-2026-43499)
 jingmatrix/pixel-ksu-root
CVE research and exploits to help gaining roots for Pixel devices
 cyberbalsa/ghostlock-nvidia-shield-9.2.4
Validated GhostLock CVE-2026-43499 port for NVIDIA Shield TV Pro mdarcy 9.2.4
 lsposed/lspromise
Android complete exploit chain that enables privilege escalation from a local untrusted app to root/kernel, combined of CVE-2026-49881 and…
 zenyxx-xd/rootmyvivo
One-click root for vivo/iQOO devices on locked bootloader | CVE-2026-43499 + KernelSU
 pubglite55/oppo-ghostlock
OPPO Find N2 GhostLock (CVE-2026-43499) exploit adaptation
 s1eezer/cve-2026-8069
Technical write-up and proof-of-concept for CVE-2026-8069, a local privilege escalation in Acer NitroSense and PredatorSense services, exploiting a…
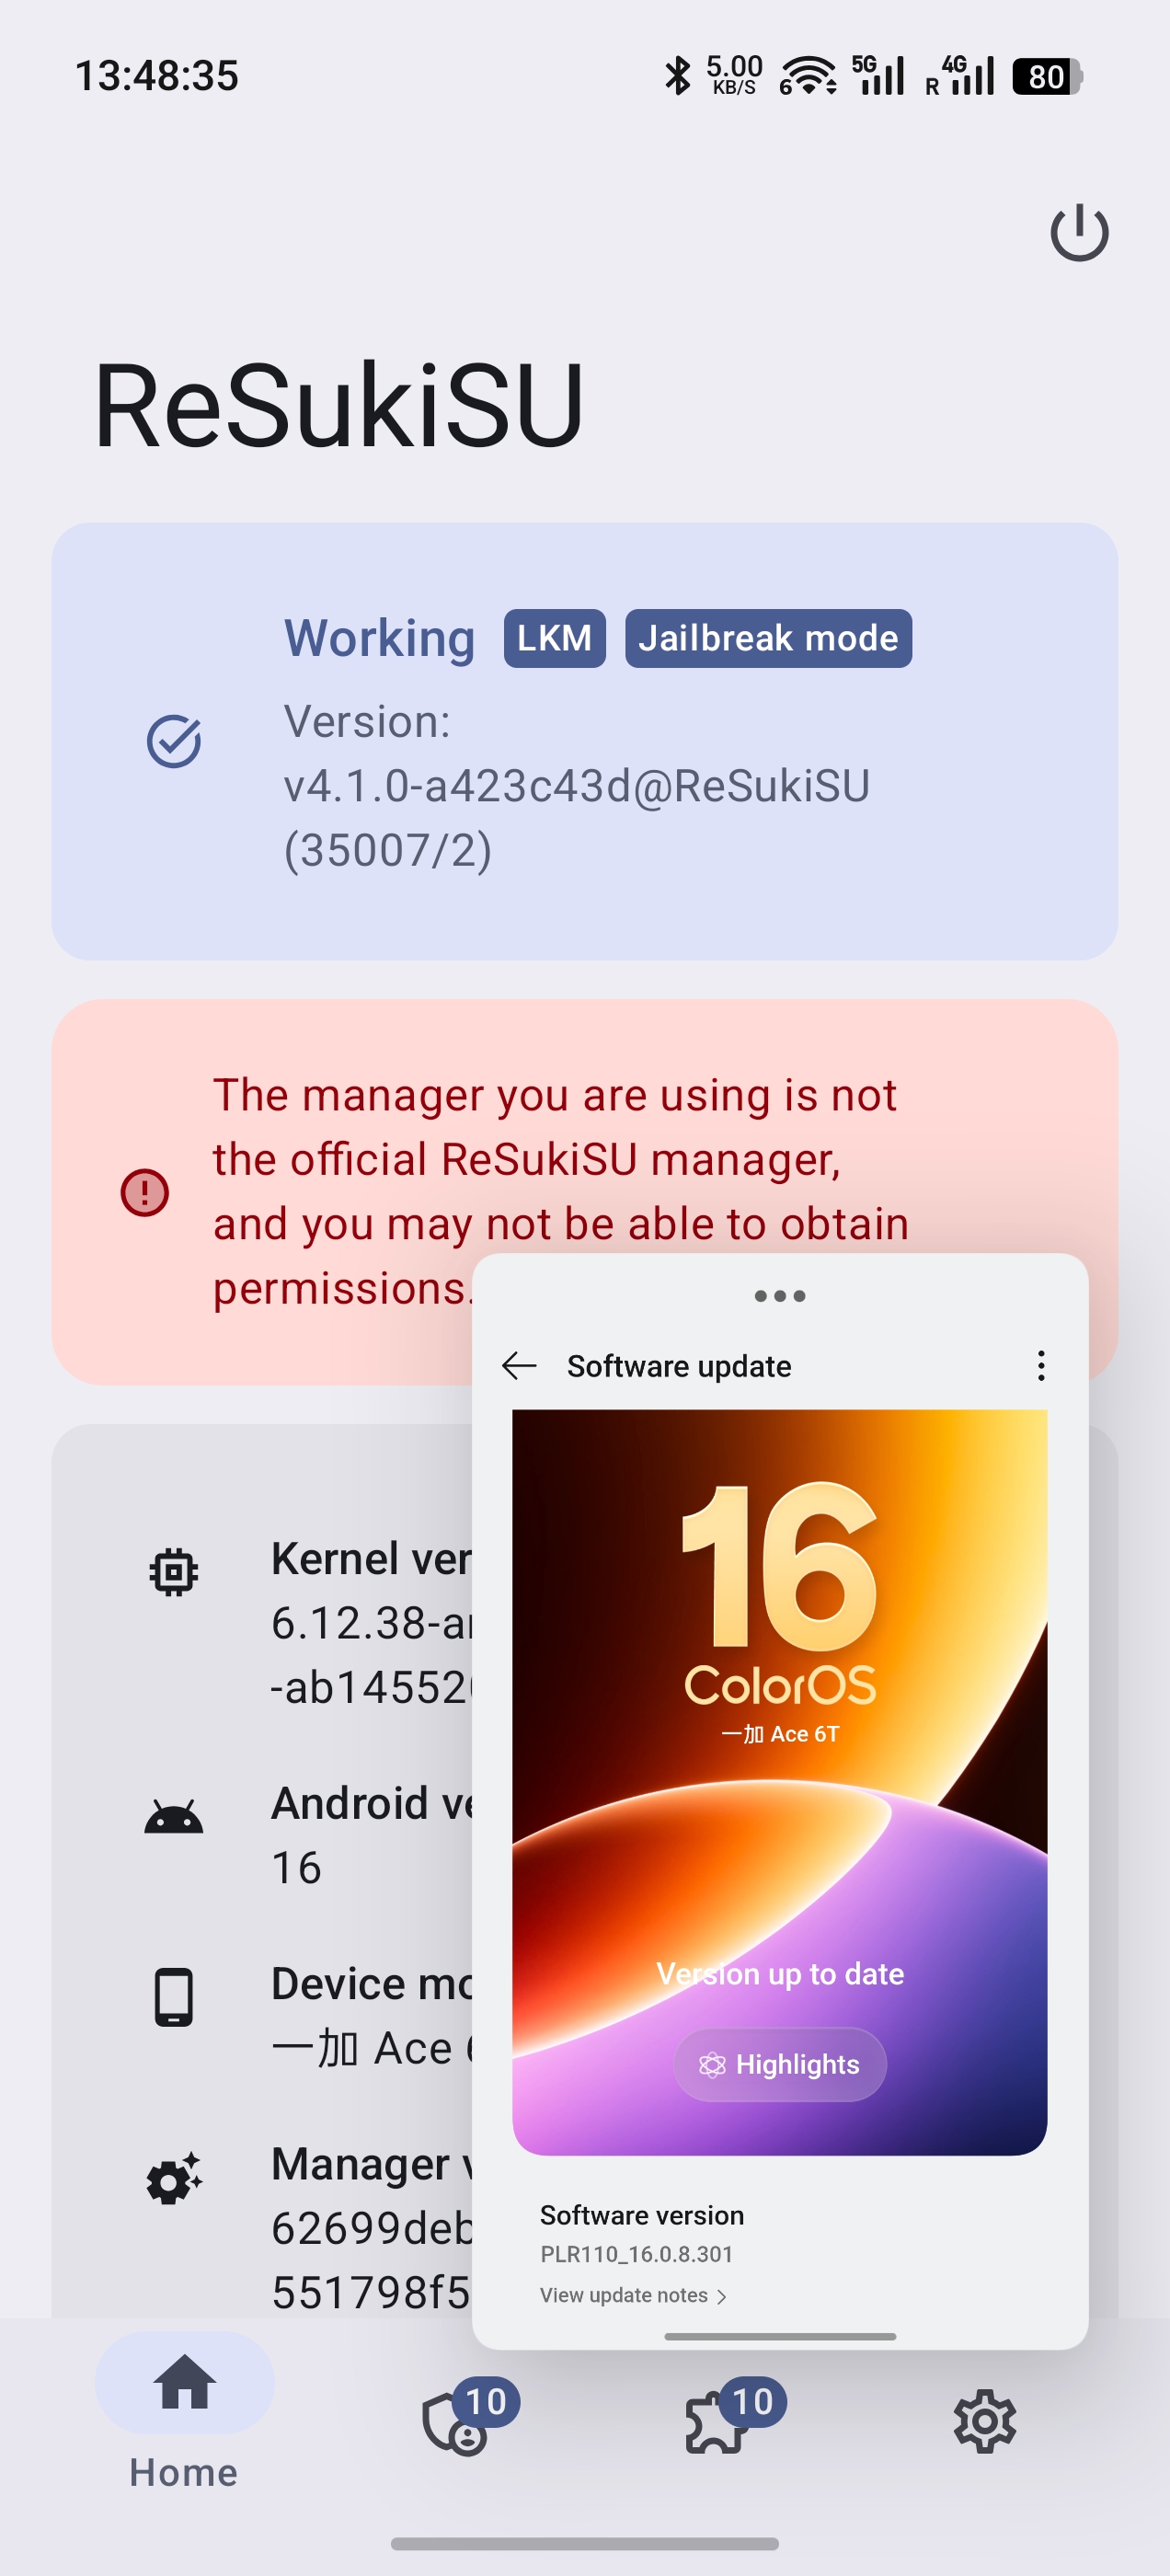 joinchang/ghostlock-oneplus
GhostLock (CVE-2026-43499) kernel exploit for Android devices with locked bootloader
 elder-plinius/t3mp3st
autonomous red teaming platform; multi-agent offensive-security meta-harness
 ruik-tech/ghostlock-s25fe
GhostLock (CVE-2026-43499) for the Galaxy S25 FE (W.I.P)
 ankitrawatgit/iqoo-z9_5g-vivo-t3_5g-root-ghostlock
An iQOO Z9 5G and vivo T3 5G jailbreak/root CVE-2026-43499 Android application and payloads. Both devices use the MediaTek Dimensity 7200 (MT6886)…