metasploit-framework

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Custom Bash and Python scripts used to automate various penetration testing tasks including recon, scanning, enumeration, and malicious payload…

Pure Rust x86 hardware emulator and Windows process simulator for malware analysis, shellcode emulation, and payload unpacking. Supports 32/64-bit PE…

Linux kernel exploit implementations targeting CVE-2008-0600, CVE-2008-0900, and CVE-2008-4210, providing proof-of-concept code for privilege…

Linux kernel privilege escalation exploits targeting CVE-2006-2451 and CVE-2006-3626, providing proof-of-concept code for local privilege escalation…

Linux kernel exploit implementations targeting CVE-2005-0736 and CVE-2005-1263, providing proof-of-concept code for privilege escalation on…

一款专注于 Java 主流 Web 中间件的内存马快速生成工具,致力于简化安全研究人员和红队成员的工作流程,提升攻防效率

Educational implementation of the Dirty COW (CVE-2016-5195) privilege escalation exploit, including race condition payload and SUID-based root shell…

LLM-driven generator for Mythic Agents, Payload-Type and C2 Profiles.

JavaScript for Automation (JXA) macOS agent

Exploit tool targeting CVE-2026-43499 with automated payload delivery and vulnerability verification for penetration testing engagements.

PoC tools for CVE-2026-58457: Unauthenticated OS Command Injection leading to remote root on Shenzhen Aitemi M300 Wi-Fi Repeater (MT02). Includes…

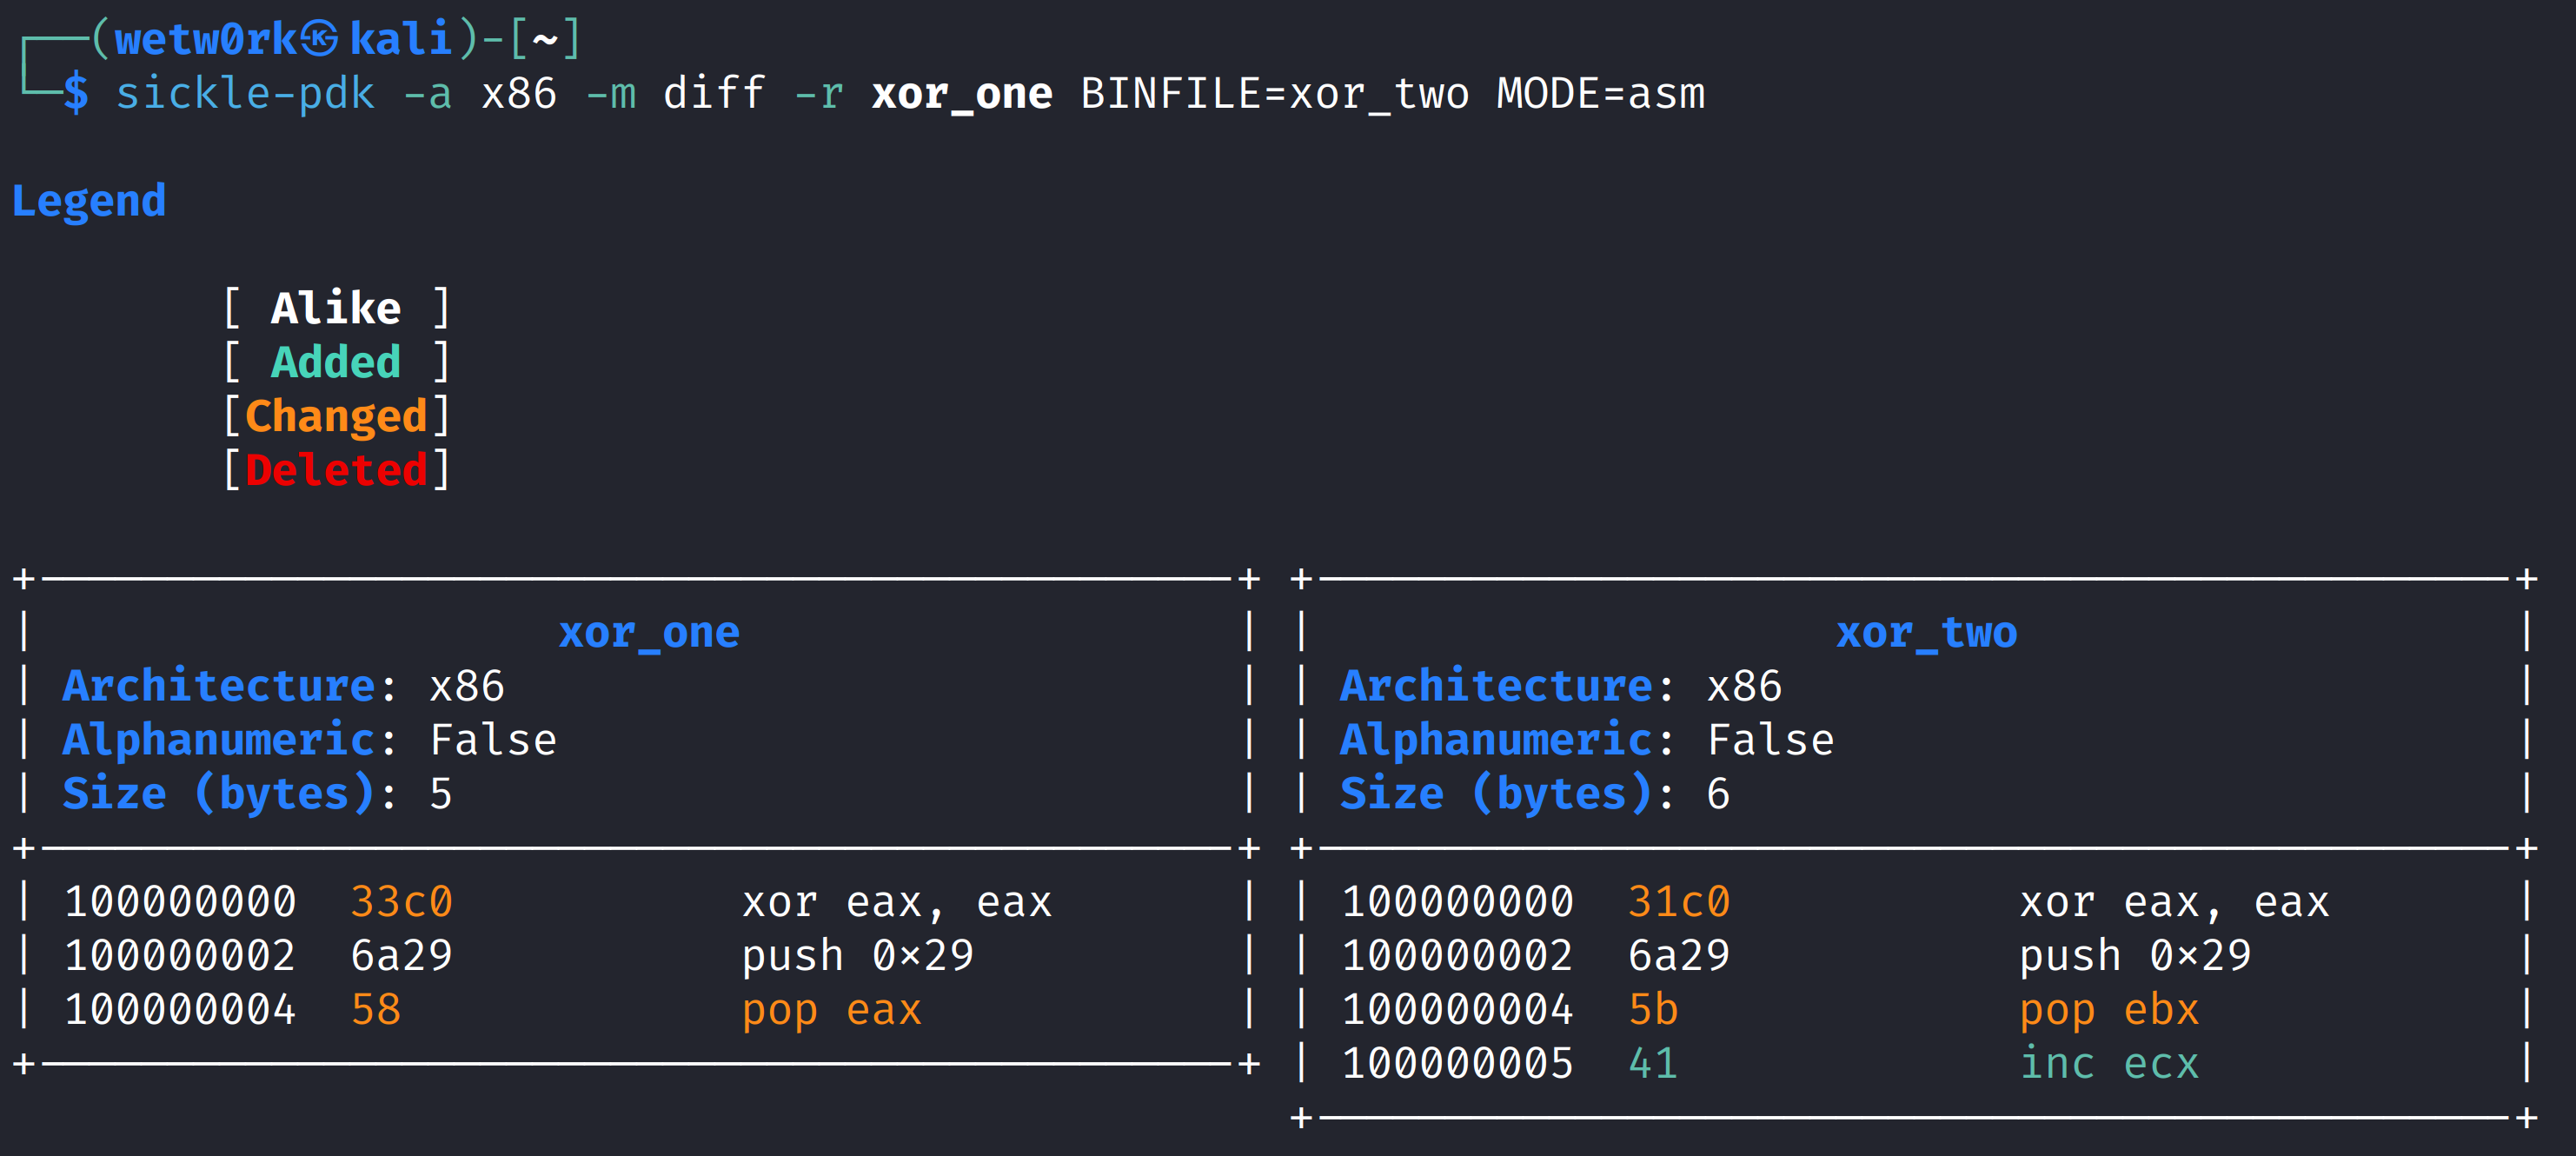
Sickle - Payload Development Kit

Autonomous security operations agent for threat intelligence, vulnerability research, IOC analysis, and red teaming. Supports dual-mode operations…

Dual-purpose JNDI injection and Java deserialization exploitation framework with advanced bypass capabilities for WAF, RASP, and high JDK versions.…

Proof-of-concept exploit for CVE-2026-20700, demonstrating a specific vulnerability with a binary exploitation payload for security testing and…

C and Rust exploit for CVE-2026-31431 with payload encryption, cache writeback, adaptive chunking, and multi-architecture support (x86, ARM, i386).

Proof-of-concept exploit for Linux kernel CVE-2026-31431, leveraging AF_ALG sockets to escalate privileges to root via payload injection and shell…