mythic_telegram_profile

Mythic C2 profile that tunnels Athena and Apollo agent traffic through Telegram bot-to-bot messages, bridging encrypted payloads to Mythic via its…

Mythic C2 profile that tunnels Athena and Apollo agent traffic through Telegram bot-to-bot messages, bridging encrypted payloads to Mythic via its…


Unicorn is a simple tool for using a PowerShell downgrade attack and inject shellcode straight into memory. Based on Matthew Graeber's powershell…

Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.

Go port of the Copy Fail PoC for CVE-2026-31431, a Linux kernel authencesn flaw enabling a 4-byte write into page cache via AF_ALG and splice.…

An Open-Source Pre and Post Callback-Based Framework for macOS Kernel Monitoring.

Controlled penetration testing lab demonstrating CVE-2011-2523 exploitation and mitigation techniques.

The Havoc Framework

Azure Post Exploitation Framework

Nebula is a cloud C2 Framework, which at the moment offers reconnaissance, enumeration, exploitation, post exploitation on AWS, but still working to…

Kubesploit is a cross-platform post-exploitation HTTP/2 Command & Control server and agent written in Golang, focused on containerized environments.

A fully public exploit of the CVE-2020-0022 BlueFrag Android RCE Vulnerability (tested on Pixel 3 XL)

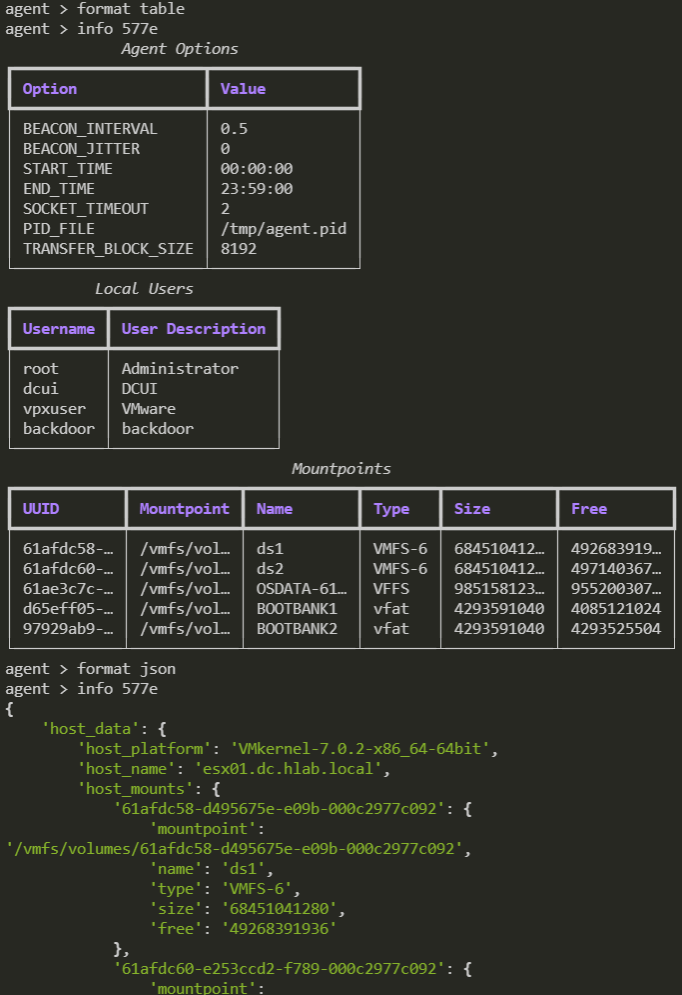
WIP Post-exploitation framework tailored for hypervisors.

generate CobaltStrike's cross-platform payload

Template-Driven AV/EDR Evasion Framework

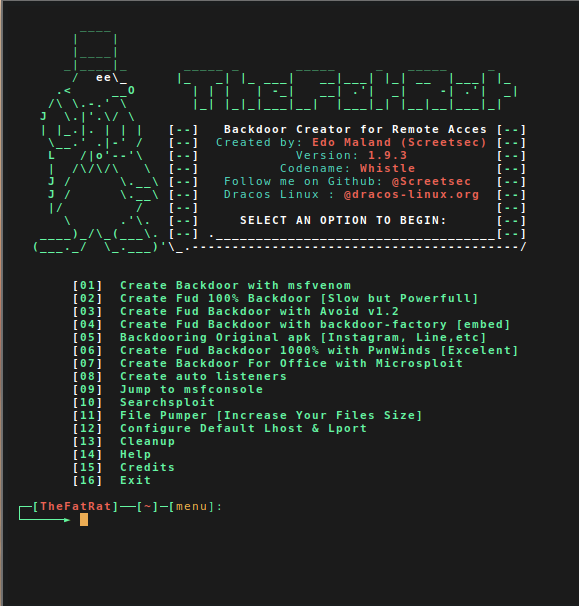
Thefatrat a massive exploiting tool : Easy tool to generate backdoor and easy tool to post exploitation attack like browser attack and etc . This…

A post exploitation framework designed to operate covertly on heavily monitored environments