

mwemu
 mwemuorg/mwemu
Pure Rust x86 hardware emulator and Windows process simulator for malware analysis, shellcode emulation, and payload unpacking. Supports 32/64-bit PE…
binary-analysisexploit-frameworksmalware-analysis+2
316
mwemuorg/mwemuPure Rust x86 hardware emulator and Windows process simulator for malware analysis, shellcode emulation, and payload unpacking. Supports 32/64-bit PE…
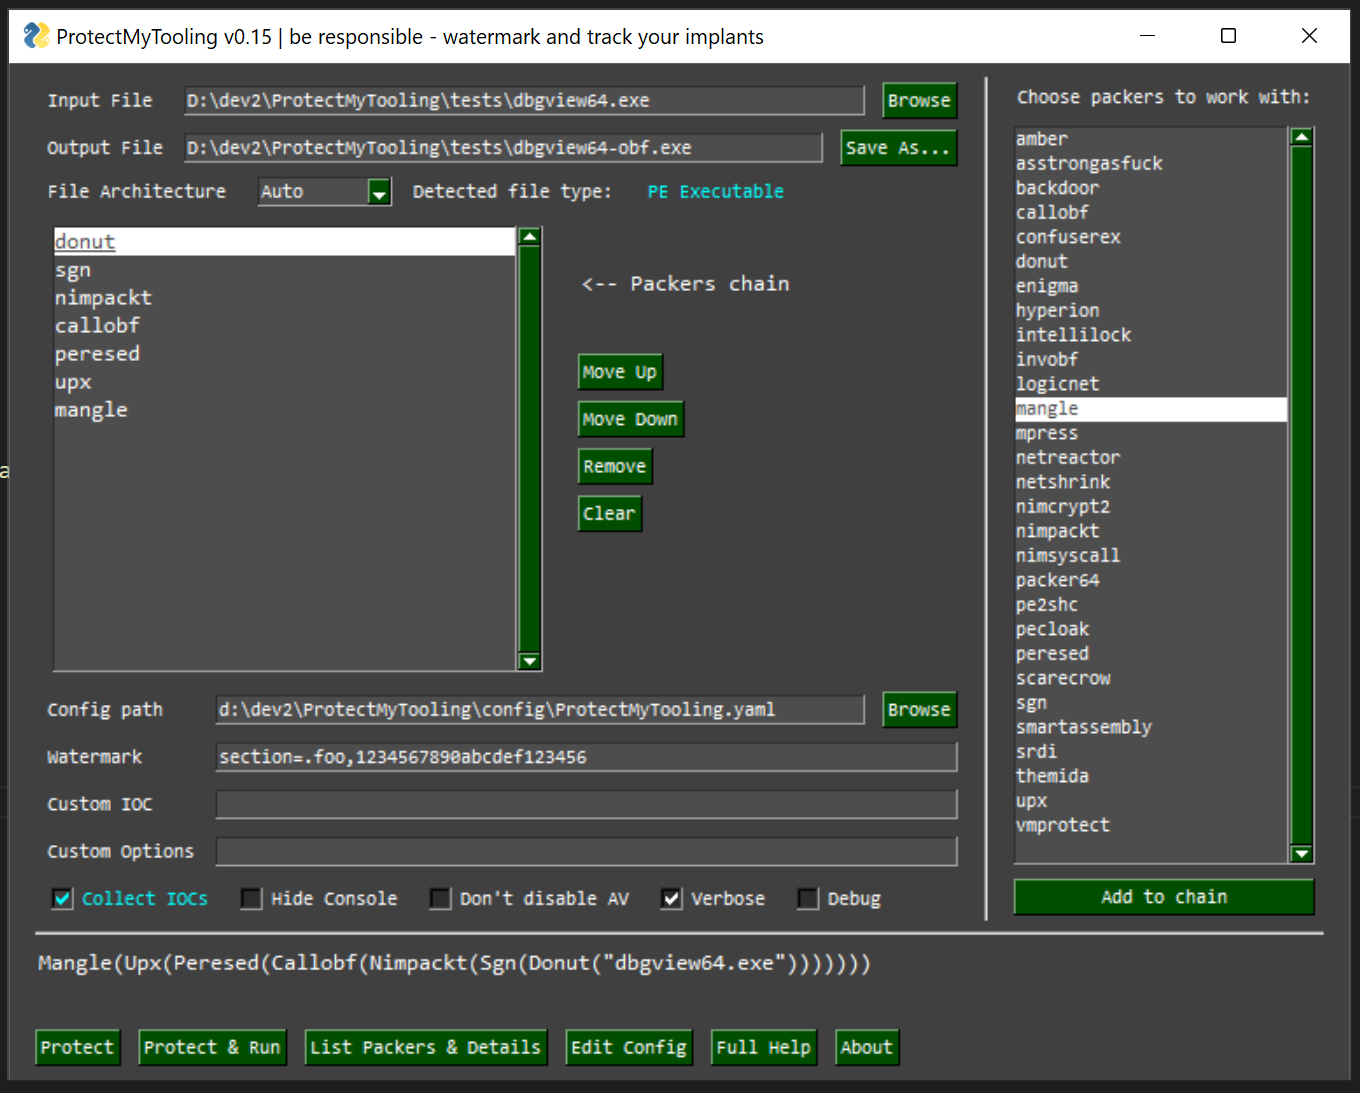 mgeeky/protectmytooling
Multi-Packer wrapper letting us daisy-chain various packers, obfuscators and other Red Team oriented weaponry. Featured with artifacts watermarking,…
 phra/pezor
Pack shellcode and PE executables into evasive payloads with anti-debug, unhooking, syscall, and memory fluctuation techniques for red-team…