

ultrasploiter
 vqkro/ultrasploiter
A single binary that folds a port scanner, the full Exploit-DB index (47k entries) and runnable exploit modules into one tool. Written in Rust, runs…
command-and-controlexploitationexploit-frameworks+9
vqkro/ultrasploiterA single binary that folds a port scanner, the full Exploit-DB index (47k entries) and runnable exploit modules into one tool. Written in Rust, runs…
 ambionics/spip-exploits
Python exploit chain for SPIP CVEs 2026-72708/72709/72710, chaining unauthenticated SQL injection to account takeover and remote code execution.
 diegslva/cve-2015-3306-lab
Reproducible Docker lab + raw-socket exploit for CVE-2015-3306 (ProFTPD mod_copy pre-auth arbitrary file copy) — a patch-diffing learning exercise
 abraxas/fortigate-ssl-vpn-exploit-kit
The FortiGate SSL-VPN pot of gold. CVE-2024-21762 and CVE-2023-27997. 79 working exploit clients. 53 hardware SKUs. 55 FortiOS builds.
 m4xsec/my-exploits
Metasploit modules, Python PoCs and throwaway Docker labs for four platform CVEs: Keycloak (CVE-2026-18963), Apache NiFi (CVE-2026-39816), HashiCorp…
 victorns69/cve-2024-12381
Exploit for Chrome V8 type confusion (CVE-2024-12381) with JSPI sandbox bypass, delivering RCE via a Flask server that fingerprints browsers and…
 sneakynachos/cve-2026-4692-trust-me-im-in-rdm
Proof-of-concept exploit for Firefox BrowsingContext authorization bypass (CVE-2026-4692), demonstrating forged IPC messages to set InRDMPane and…
 theemperorspath/cve-2026-2441-poc
Proof-of-concept exploit for CVE-2026-2441, a Chrome CSS Use-After-Free in Blink CSSFontFeatureValuesMap, achieving renderer RCE via V8…
 nightcorefan94/cve-2026-6770
Proof-of-concept exploit for CVE-2026-6770 targeting Firefox and Tor browsers, demonstrating the vulnerability and enabling security researchers to…
 jaf0rk/cve-2026-5281-cve-2026-11057-fullchain
Full-chain exploit for Android Chromium combining CVE-2026-11057 info leak and CVE-2026-5281 use-after-free to achieve vtable hijack and arbitrary…
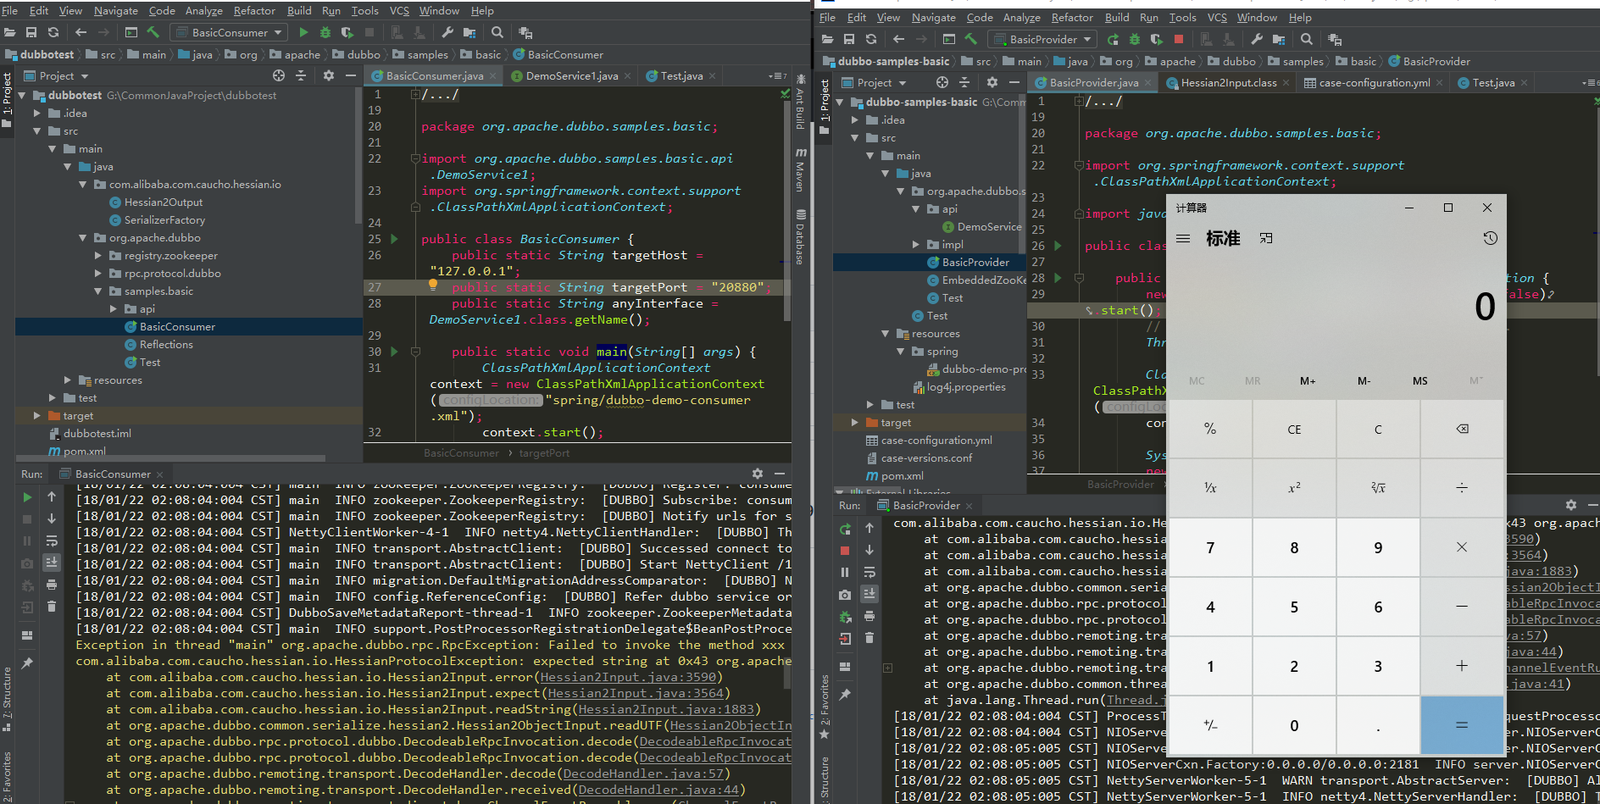 longofo/apache-dubbo-hessian2-cve-2021-43297
Demonstrates a proof-of-concept exploit for CVE-2021-43297, a deserialization vulnerability in Apache Dubbo's Hessian2 protocol, with provider and…
 sneakynachos/cve-2026-74939-escape-the-mac-n-cheese-box
Firefox content-to-parent IPDL privilege escalation (N-day, bug 2054416): forged PDocumentChannel with RemoteTypeOverride -> privilegedabout process…
 cxyofficial/x200-cve-2026-43499
Exploit tool targeting CVE-2026-43499 with automated payload delivery and vulnerability verification for penetration testing engagements.
 prapul1/vulnhub-dc1-writeup
VulnHub DC-1 boot-to-root — exploiting CVE-2018-7600 (Drupalgeddon2) for RCE, extracting DB credentials from settings.php, forging admin password…
 g0d150ne/wp2shell
Modular WordPress pre-auth exploit framework chaining SQL injection and authentication bypass to deliver remote code execution, interactive shells,…
 jbaines-r7/cisco_asa_research
Cisco ASA Software and ASDM Security Research
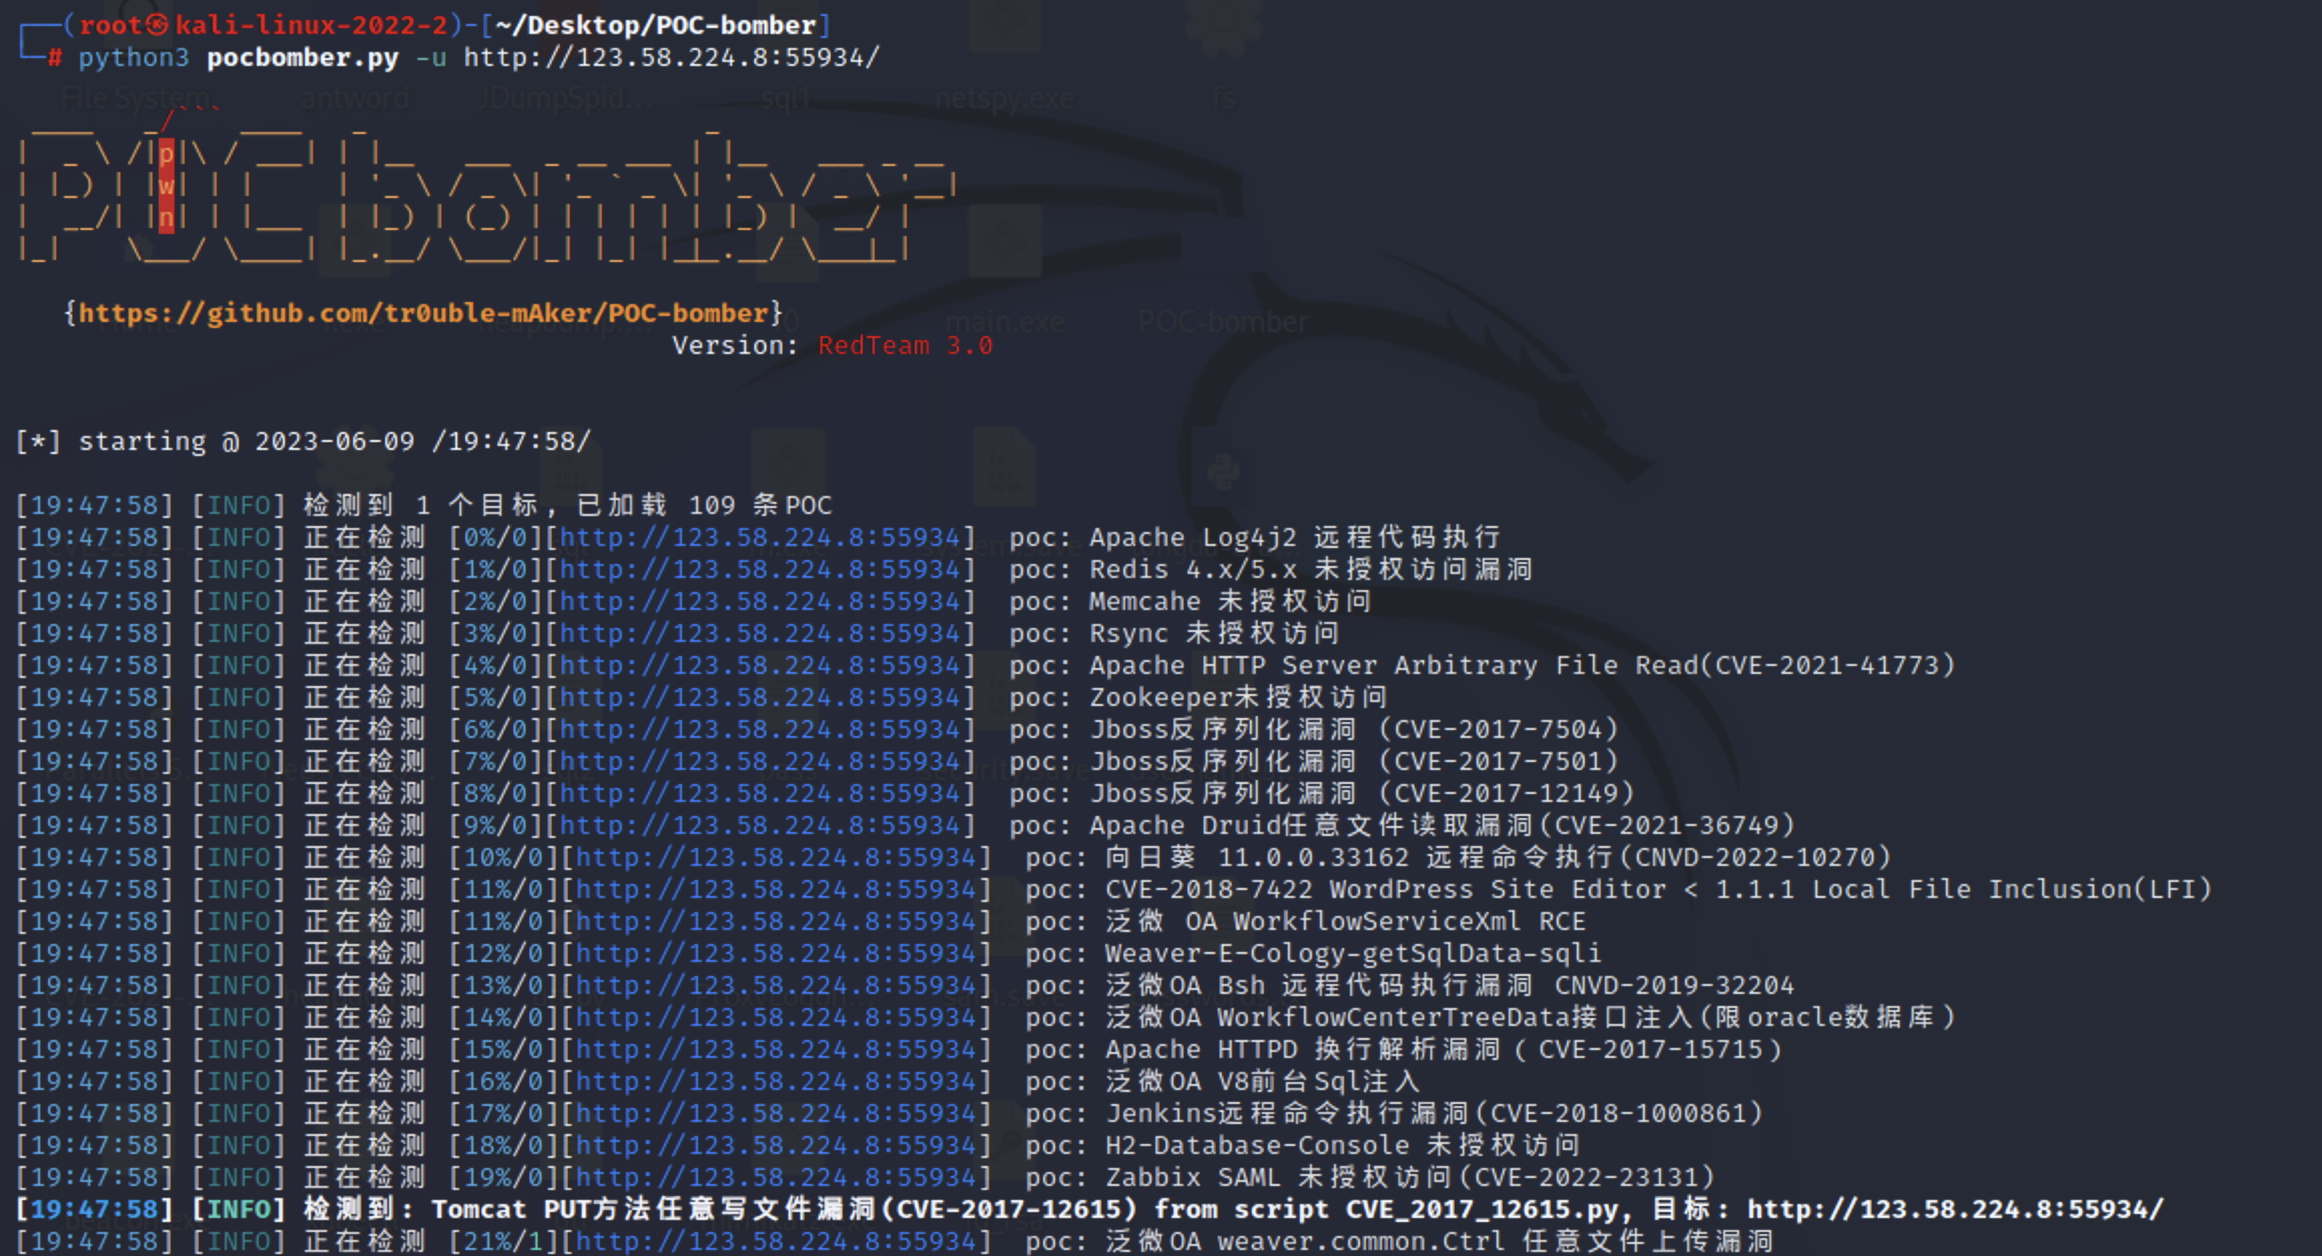 tr0uble-maker/poc-bomber
利用大量高威胁poc/exp快速获取目标权限,用于渗透和红队快速打点
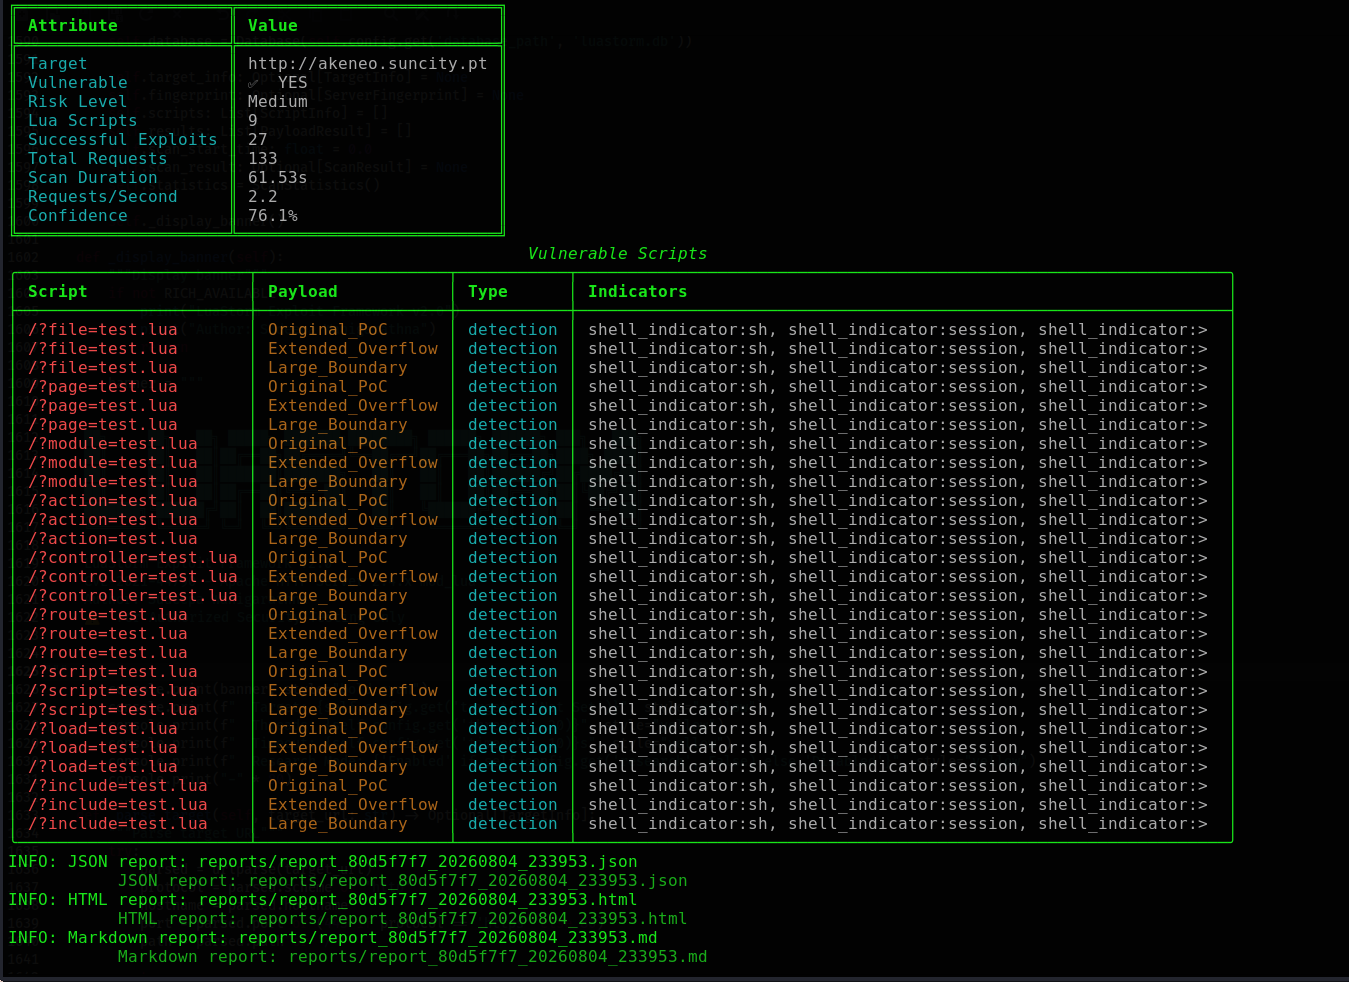 cerberusmrxi/apache-lua-buffer-overflow-exploit-cve-2021-44790
Apache HTTP Server 2.4.x mod_lua Buffer Overflow (CVE-2021-44790) - Advanced exploitation framework with fingerprinting, multi-stage scanning, plugin…