cloudrasp-log4j2
一个针对防御 log4j2 CVE-2021-44228 漏洞的 RASP 工具。 A Runtime Application Self-Protection module specifically designed for log4j2 RCE (CVE-2021-44228) defense.

一个针对防御 log4j2 CVE-2021-44228 漏洞的 RASP 工具。 A Runtime Application Self-Protection module specifically designed for log4j2 RCE (CVE-2021-44228) defense.

The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…

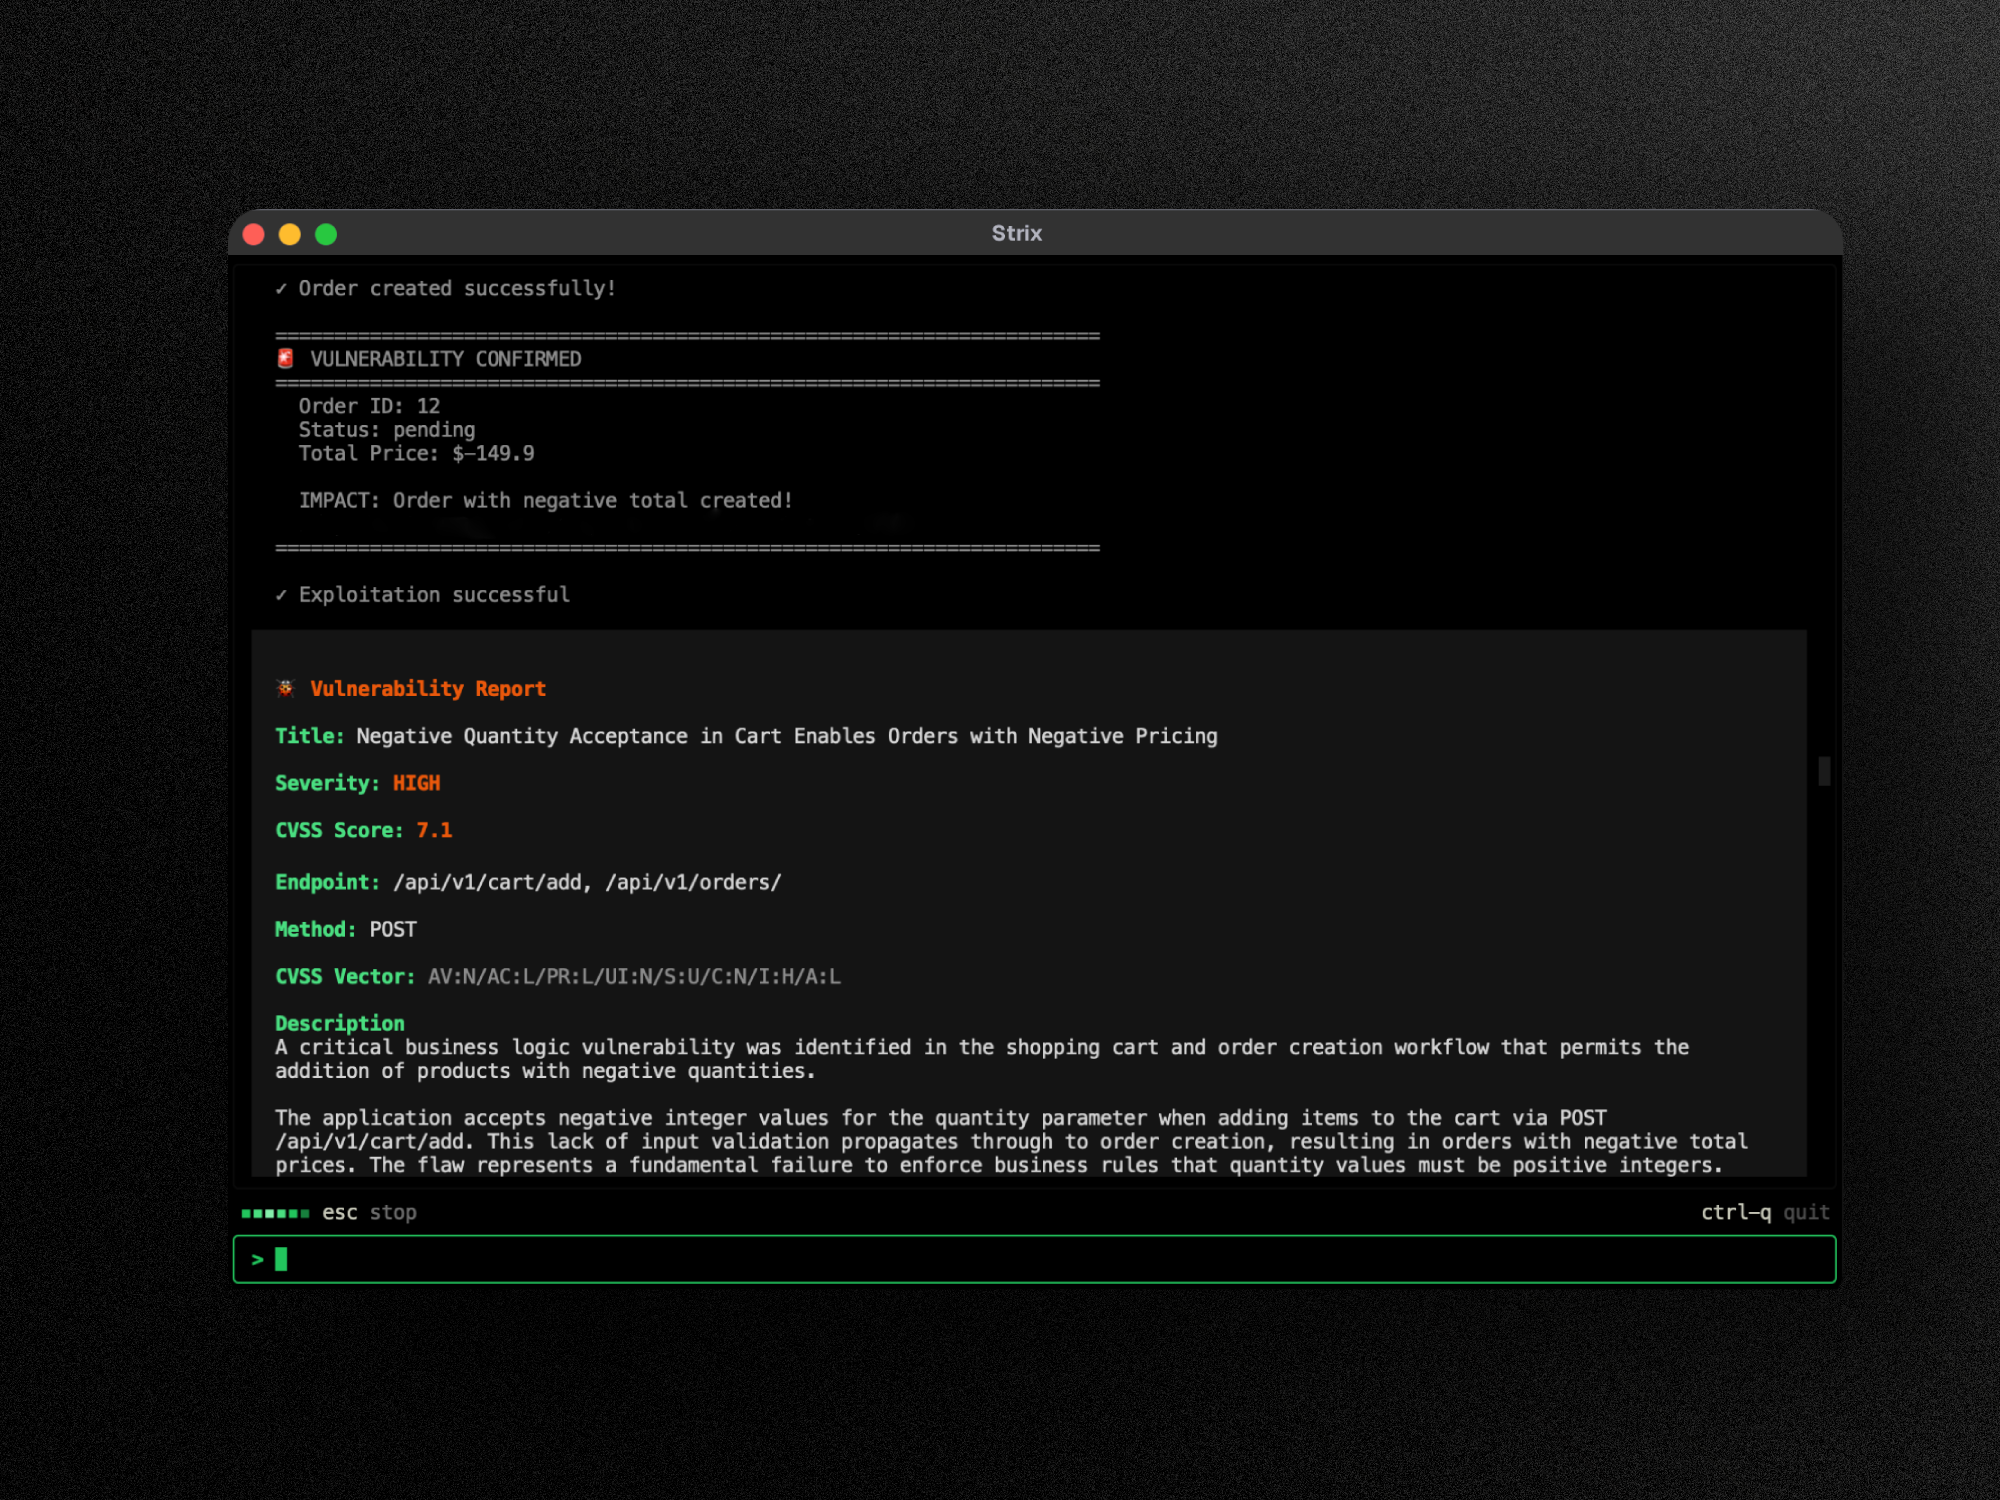
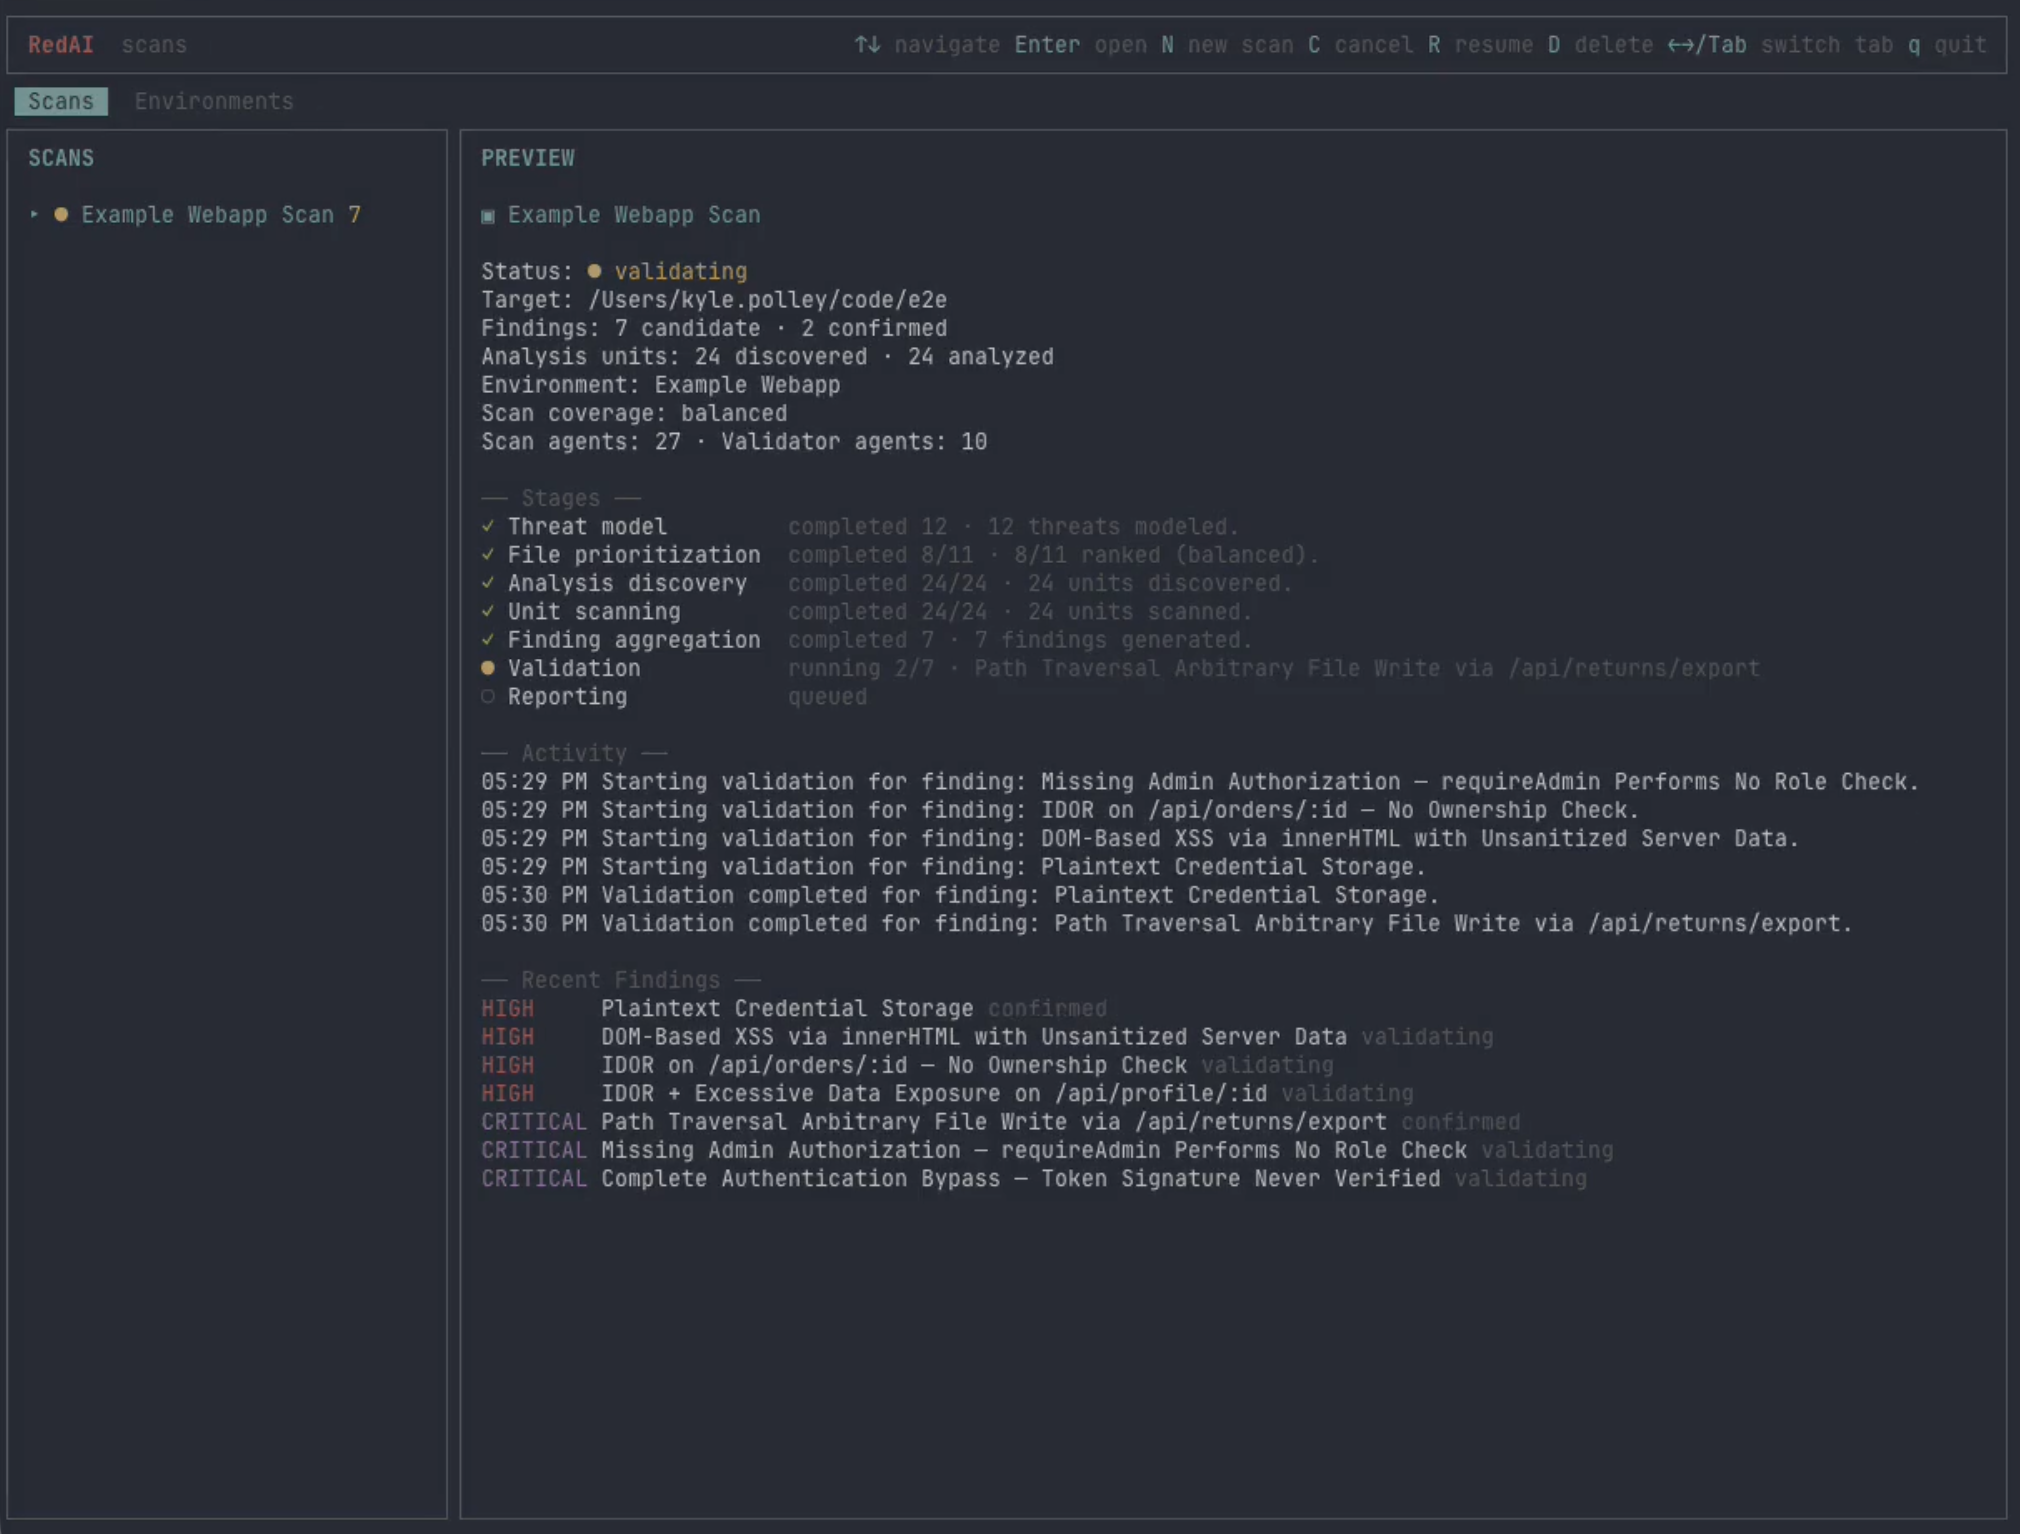
Open-source AI penetration testing tool to find and fix your app’s vulnerabilities.

Adversary Emulation Framework

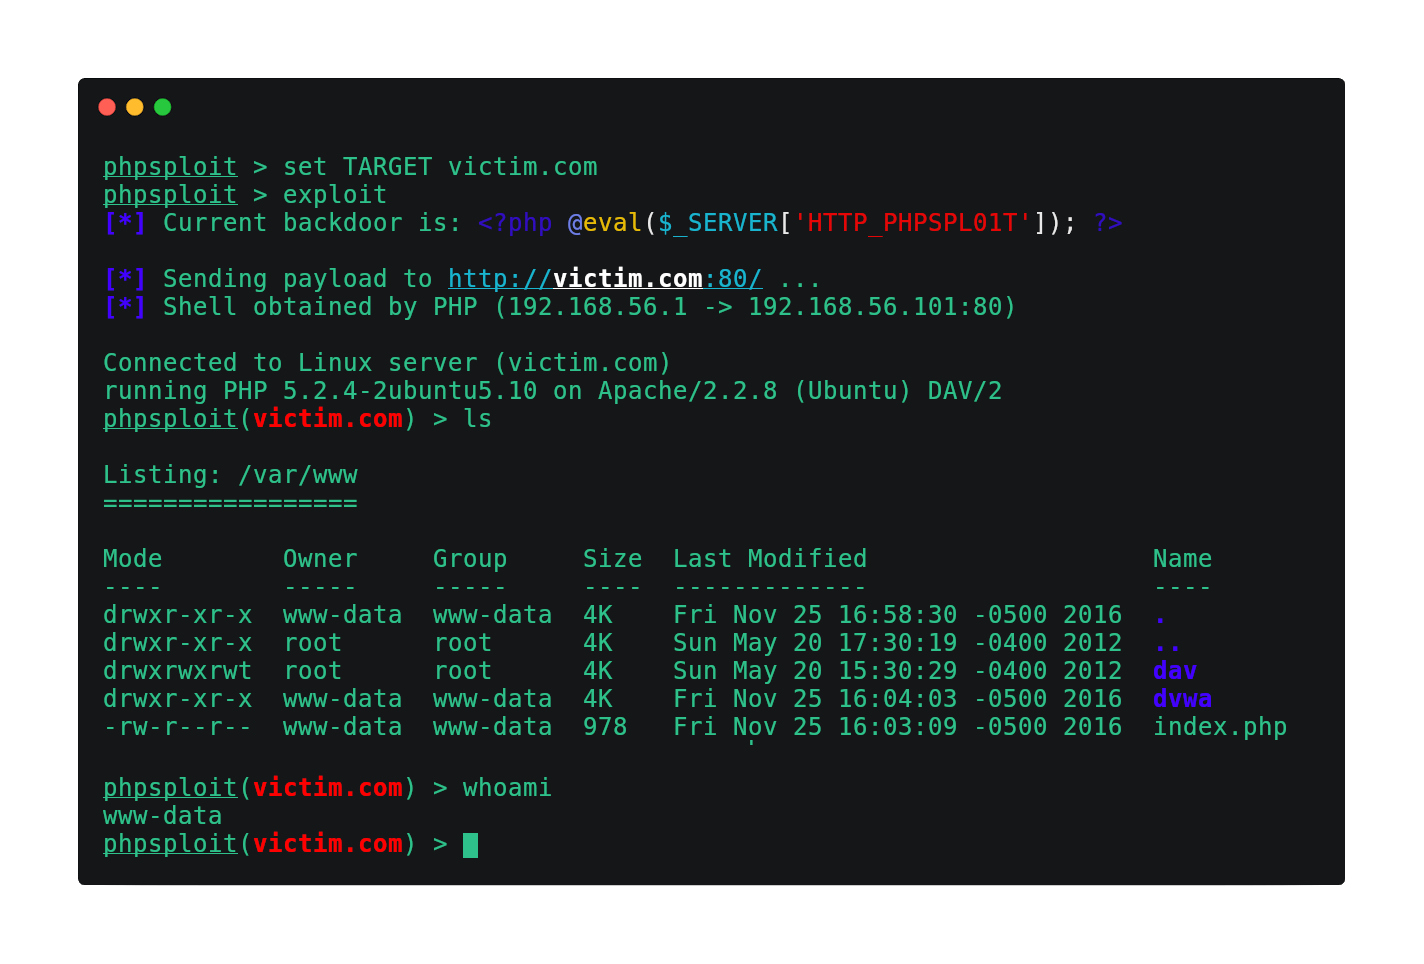
Full-featured C2 framework which silently persists on webserver with a single-line PHP backdoor

PEASS - Privilege Escalation Awesome Scripts SUITE (with colors)

Python-Based Pentesting Framework

Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.

Metarget is a framework providing automatic constructions of vulnerable infrastructures.

Modular penetration testing platform that enables you to write, test, and execute exploit code.

link is a command and control framework written in rust

Offensive Docker is an image with the more used offensive tools to create an environment easily and quickly to launch assessment to the targets.

CVE-2021-31166: exploitation with Powershell, Python, Ruby, NMAP and Metasploit.

All-in-one penetration testing platform with MITM proxy, web fuzzer, reverse connection handler, and plugin system for automated security testing and…

The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…


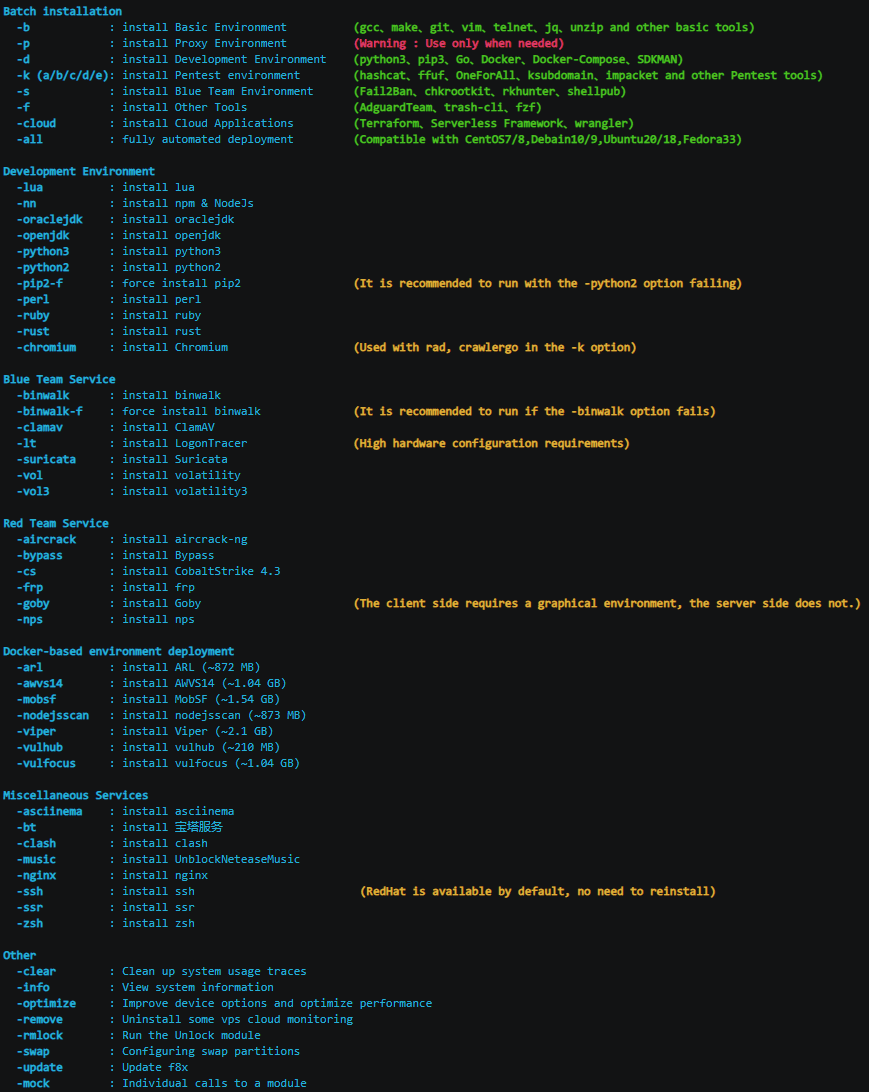
红/蓝队环境自动化部署工具 | Red/Blue team environment automation deployment tool

AI-driven vulnerability discovery and live validation