
cloudrasp-log4j2
一个针对防御 log4j2 CVE-2021-44228 漏洞的 RASP 工具。 A Runtime Application Self-Protection module specifically designed for log4j2 RCE (CVE-2021-44228) defense.

一个针对防御 log4j2 CVE-2021-44228 漏洞的 RASP 工具。 A Runtime Application Self-Protection module specifically designed for log4j2 RCE (CVE-2021-44228) defense.

exploitdb // The official Exploit-Database repository

Python-Based Pentesting Framework

Autonomous AI red team framework that chains reconnaissance, exploitation, and post-exploitation into a single pipeline, then triages findings,…

红/蓝队环境自动化部署工具 | Red/Blue team environment automation deployment tool

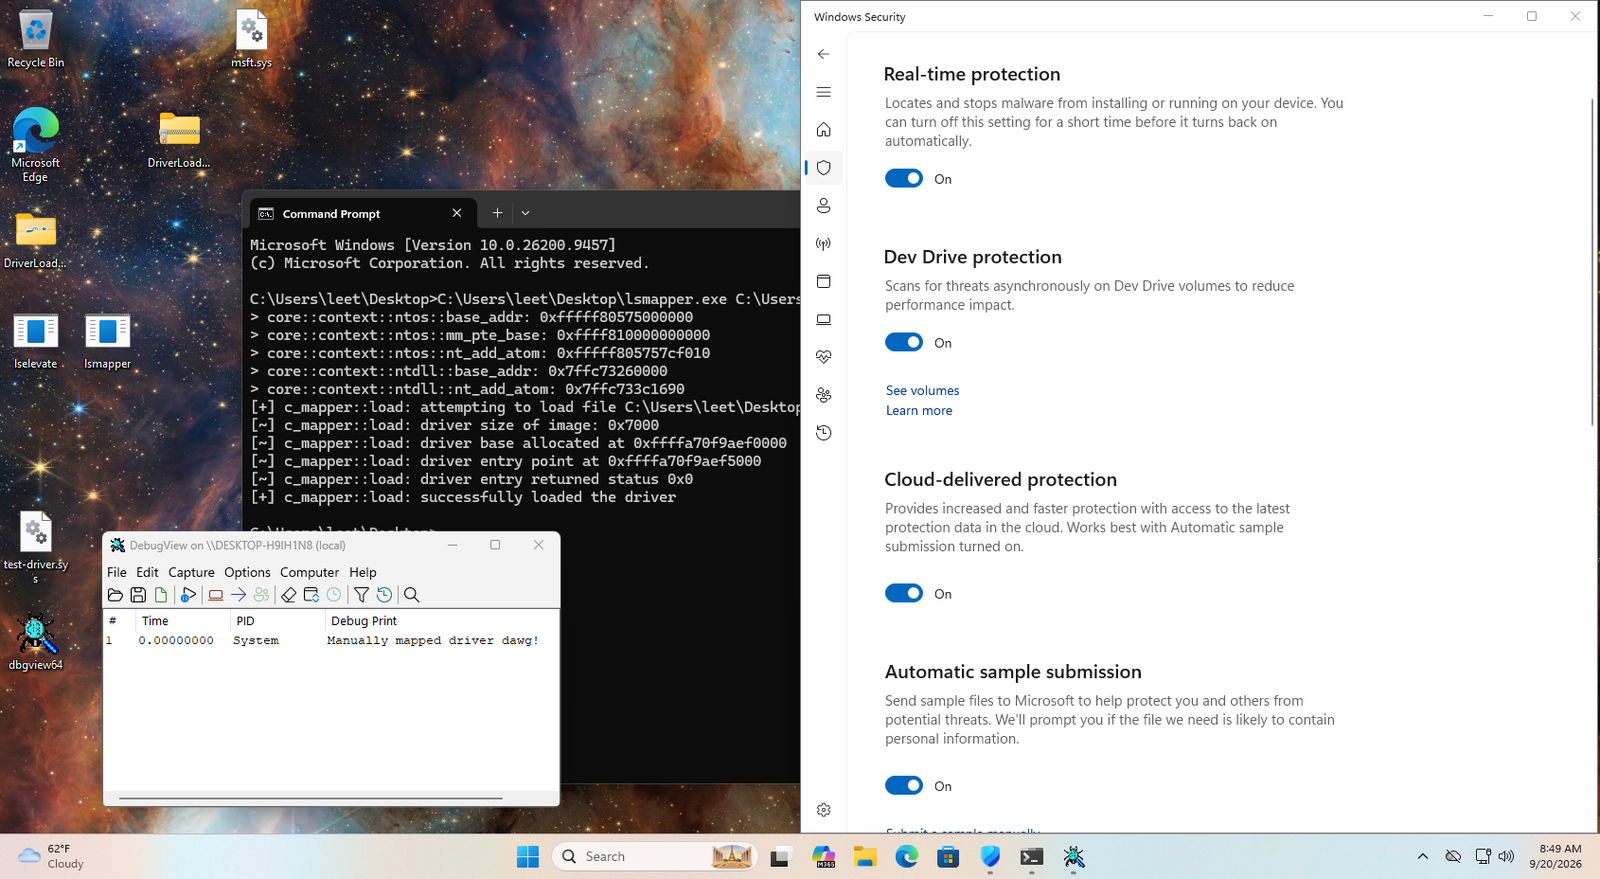
PoC for WinNotify, demonstrated through a driver mapper, and local privilege escalation.

The Browser Exploitation Framework Project

CVE-2019-0708-Msf-验证

A byte code analyzer for finding deserialization gadget chains in Java applications

Project that brings together several pentest tools

Stealthy DLL proxying implant for Microsoft Teams that injects AES-encrypted shellcode via unhooking techniques, providing persistent backdoor access…

A simple C2 Framework written in modern C++

Toolkit to weaponize Chromium vulnerabilities into reliable, cross-platform, full-chain exploits

Isolated AD/Linux attack lab: exploited CVE-2007-2447 via Metasploit, detected with Wazuh SIEM mapped to MITRE ATT&CK (T1190, T1059)

Metasploit-Framework modules (scanner and exploit) for the CVE-2021-41773 and CVE-2021-42013 (Path Traversal in Apache 2.4.49/2.4.50)

Antivirus evasion project

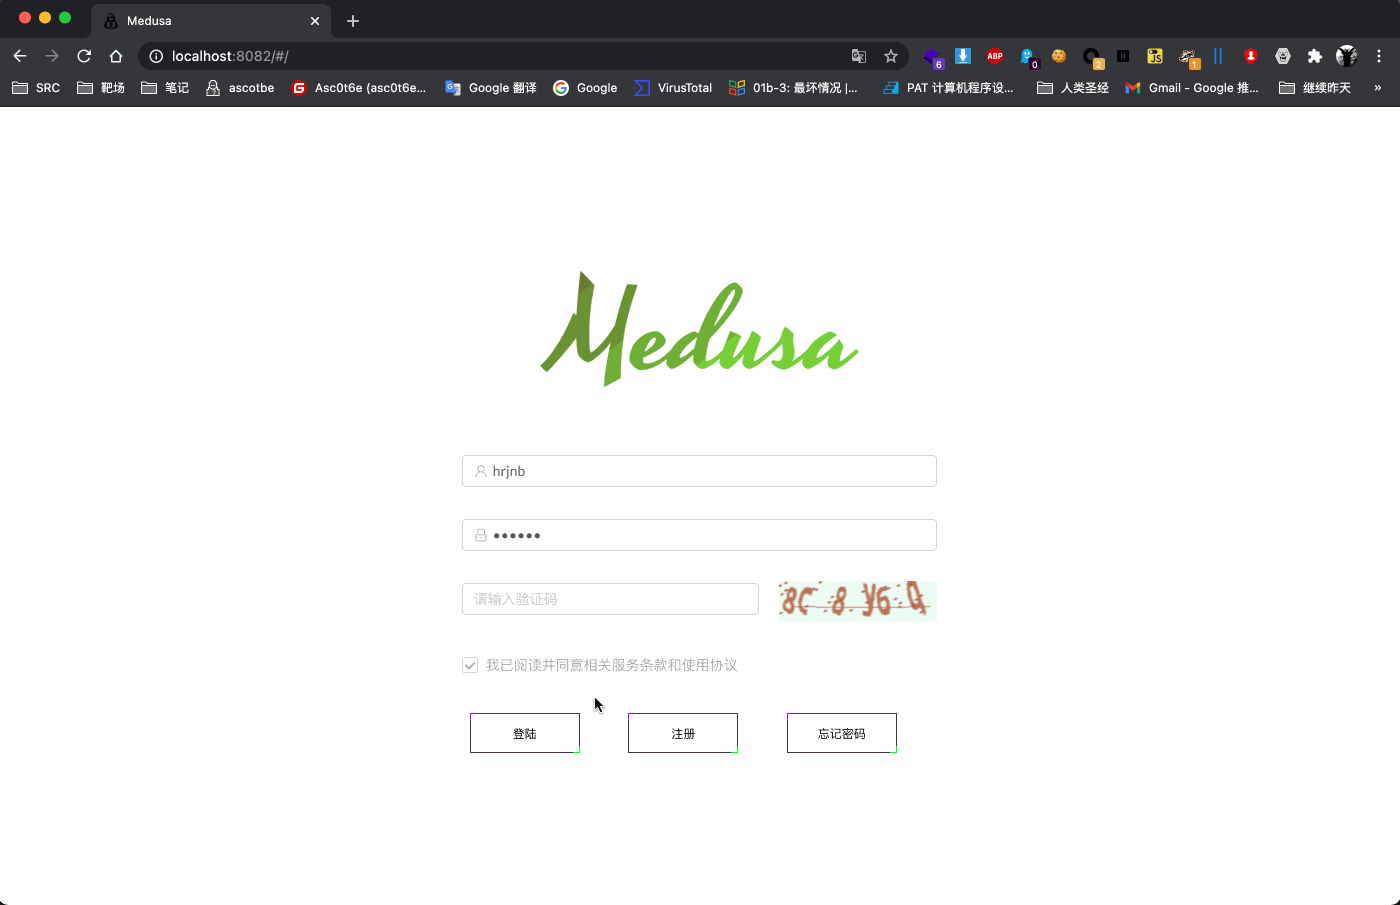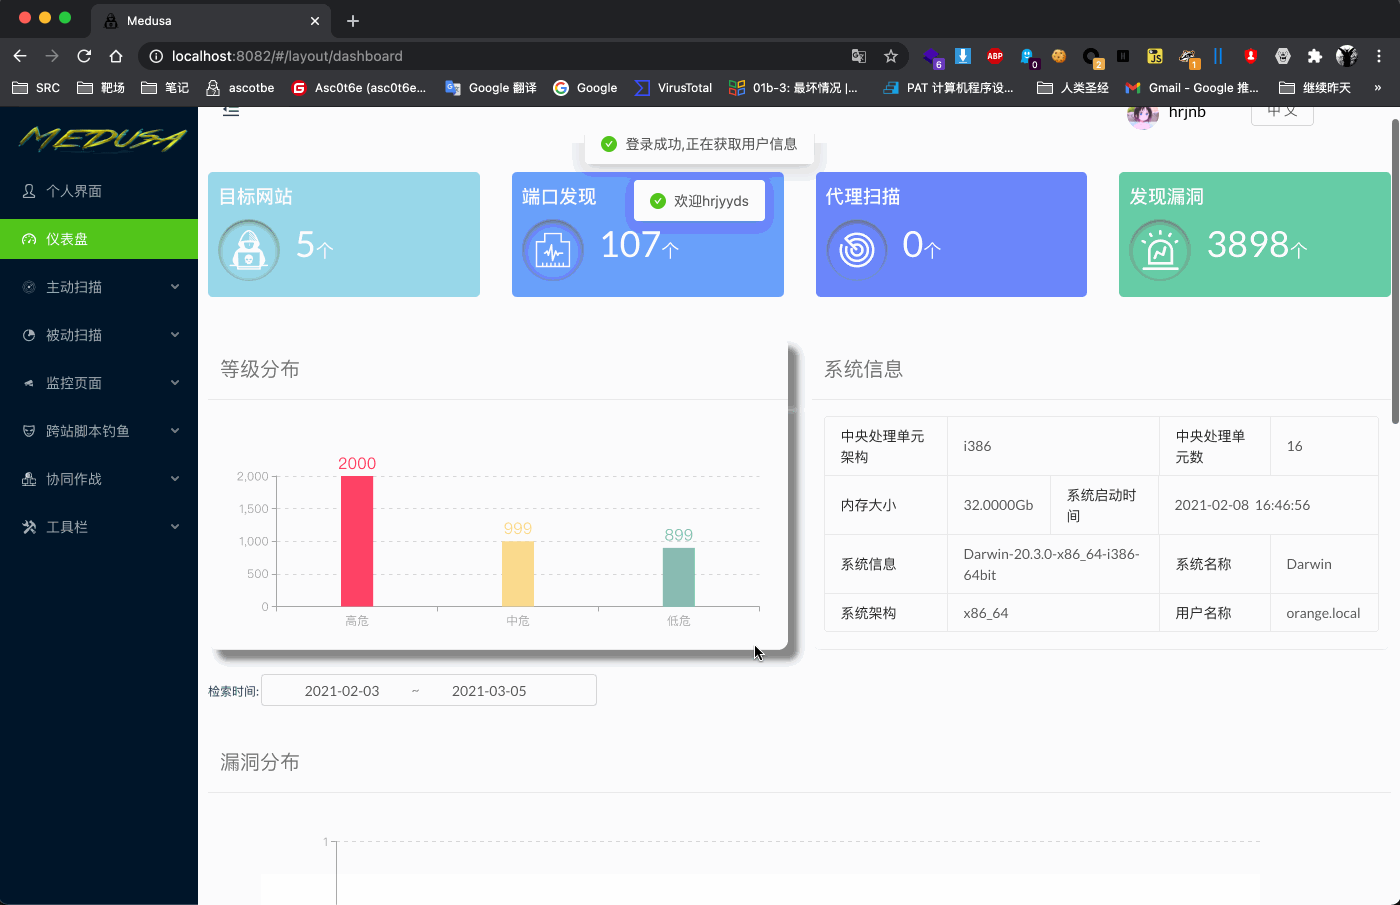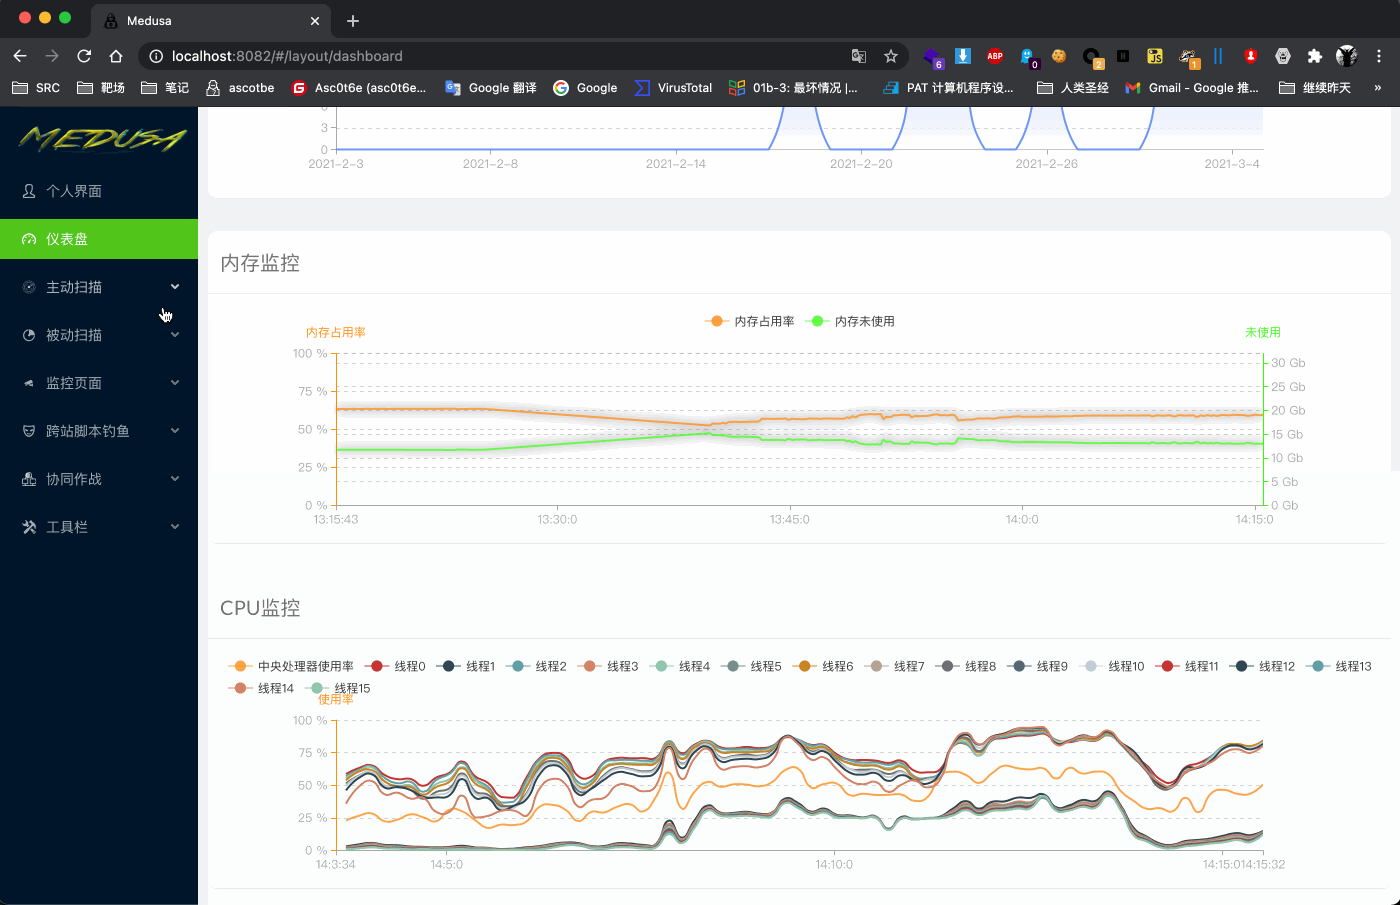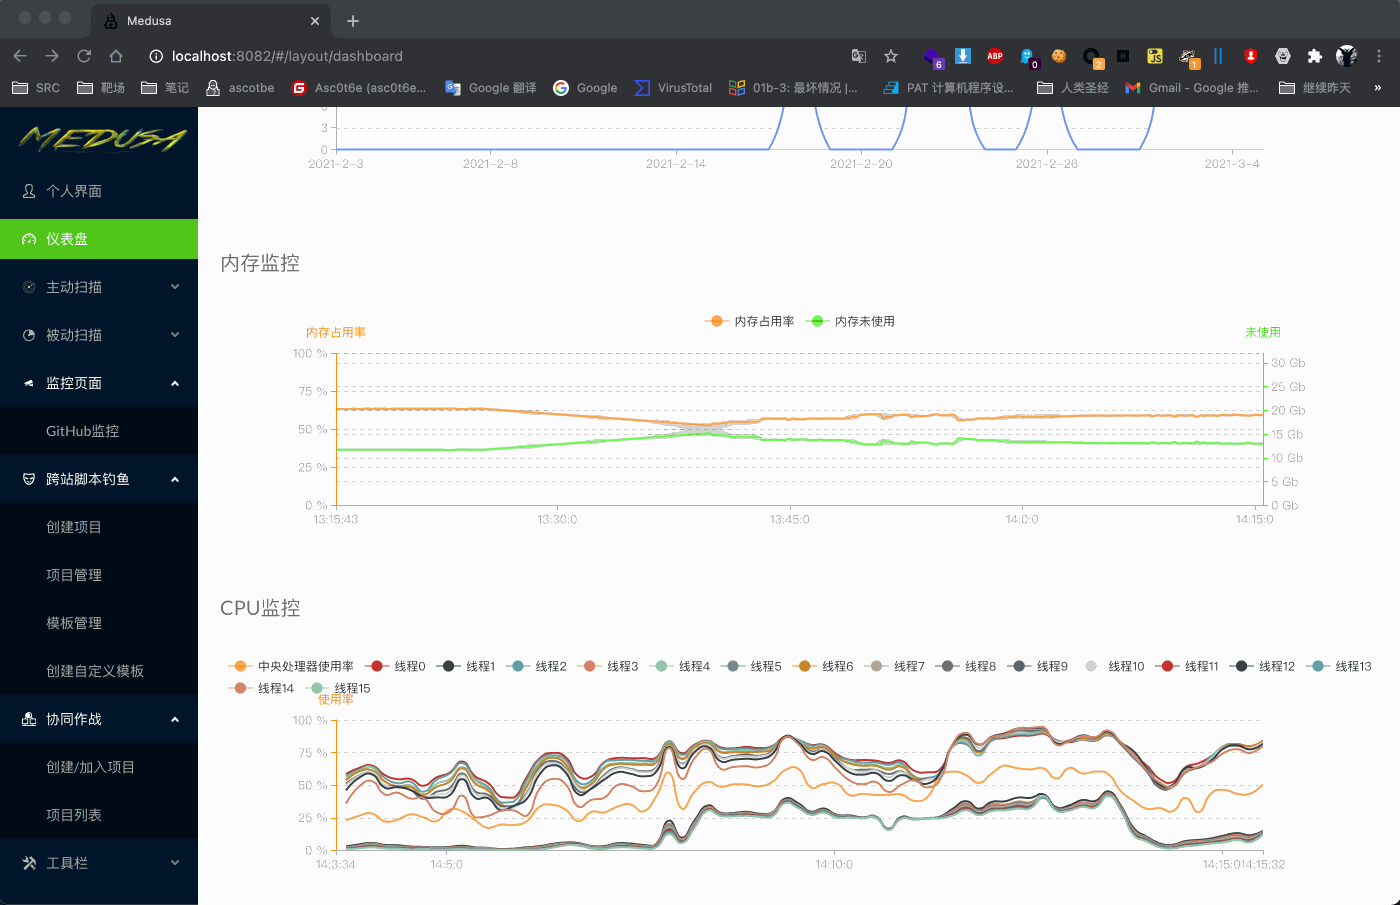
🐈Medusa是一个红队武器库平台,目前包括XSS平台、协同平台、CVE监控、免杀生成、DNSLOG、钓鱼邮件、文件获取等功能,持续开发中

Red Team engagement platform with the goal of unifying offensive tools behind a simple UI