

PowerShellArsenal
 mattifestation/powershellarsenal
A PowerShell Module Dedicated to Reverse Engineering
binary-analysisdebuggersdynamic-analysis-sandboxing+6
902
mattifestation/powershellarsenalA PowerShell Module Dedicated to Reverse Engineering
 alonemonkey/frida-ios-dump
Extracts decrypted IPA files from jailbroken iOS devices using Frida for reverse engineering, security analysis, and mobile app pentesting.
 lilify-jp/squre
🛡️ Open-source binary protection toolkit for Windows PE. Nanomite, VM protection, anti-debug, and more.
 crackercat/rootsmart-v2.0
Android Ransomware Development - AES256 encryption + CVE-2019-2215 (reverse root shell) + Data Exfiltration
 nicchongwb/rootsmart-v2.0
Android Ransomware Development - AES256 encryption + CVE-2019-2215 (reverse root shell) + Data Exfiltration
 iamsopotatoe-coder/tinyload
Open source Windows x64 PE packer and crypter. Compresses and encrypts executables with a custom virtual machine into a self extracting stub.
 gchq/cyberchef
The Cyber Swiss Army Knife - a web app for encryption, encoding, compression and data analysis
 gojue/ecapture
Capturing SSL/TLS plaintext without a CA certificate using eBPF. Supported on Linux/Android kernels for amd64/arm64.
 beemdevelopment/aegis
A free, secure and open source app for Android to manage your 2-step verification tokens.
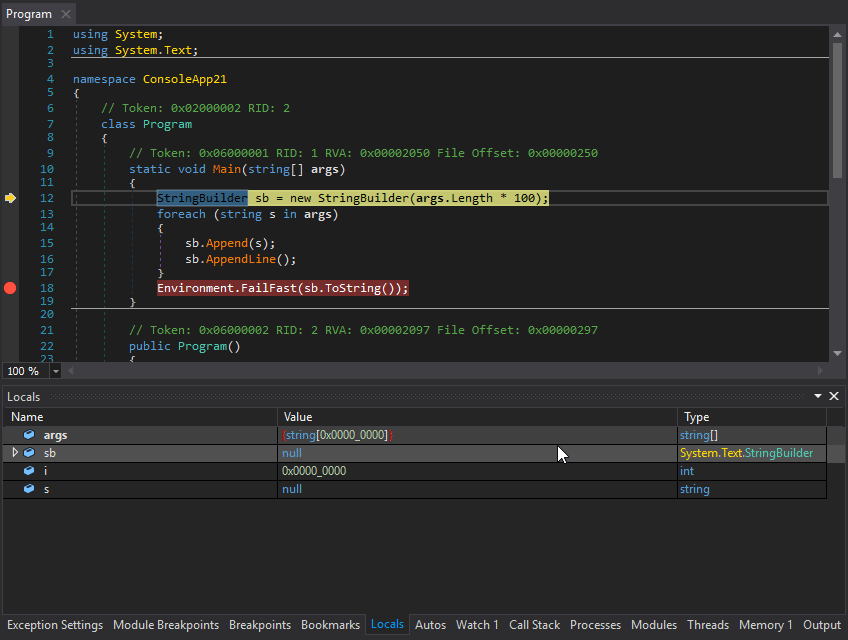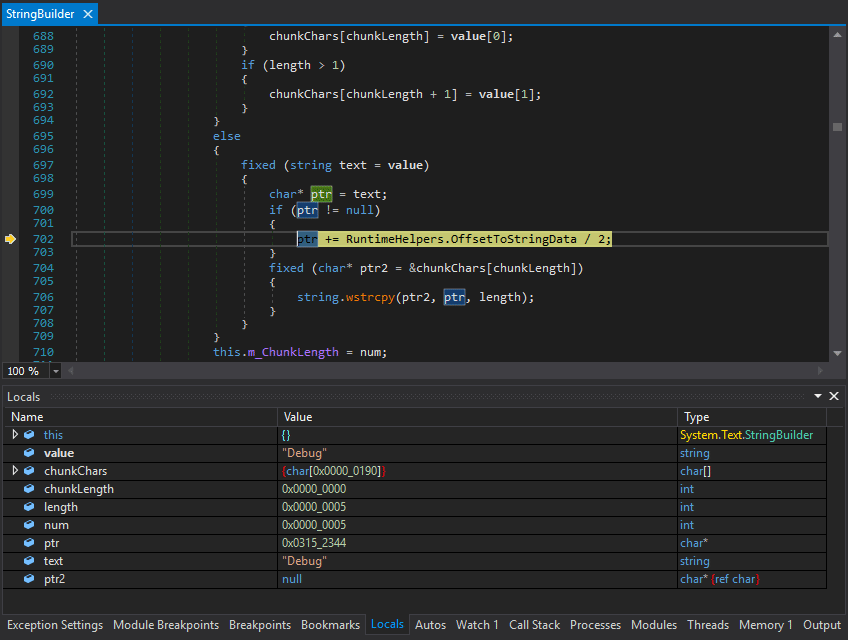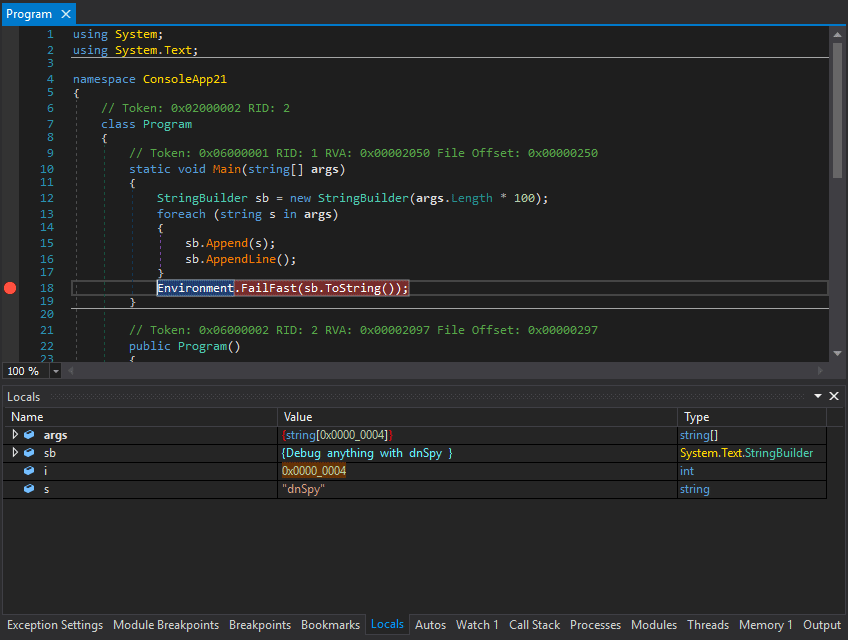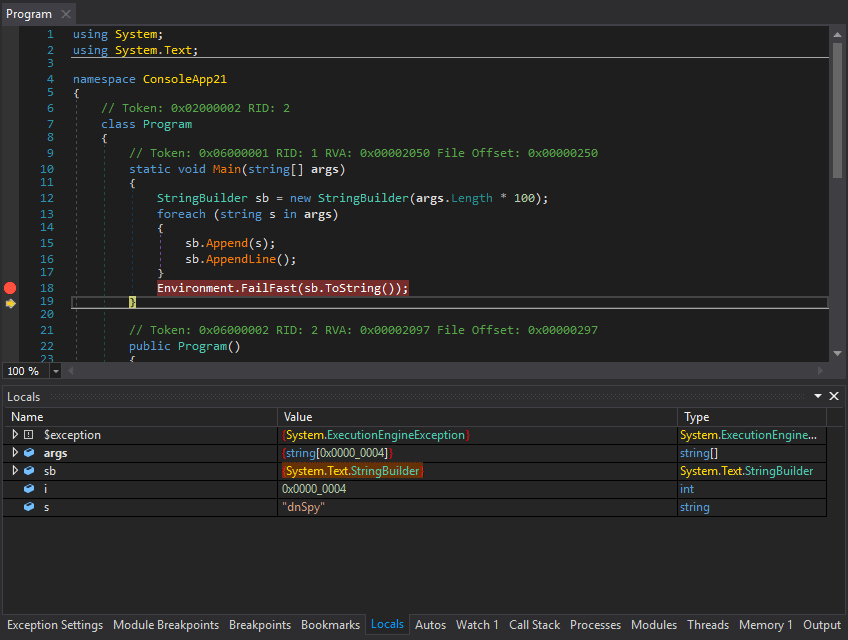 dnspyex/dnspy
Unofficial revival of the well known .NET debugger and assembly editor, dnSpy
 permissionlesstech/bitchat-android
Decentralized, encrypted peer-to-peer messaging app over Bluetooth mesh networks. No internet, servers, or phone numbers required. Features X25519 +…
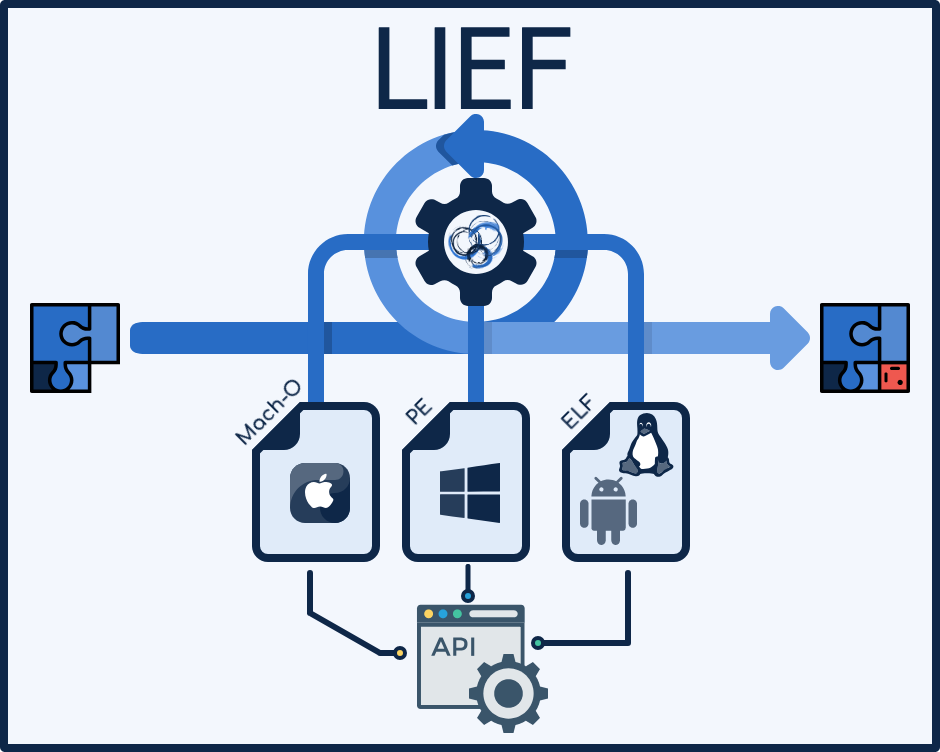 lief-project/lief
Cross-platform library to parse, modify, and abstract ELF, PE, and MachO executable formats. Supports C++, Python, and Rust APIs with disassembler,…
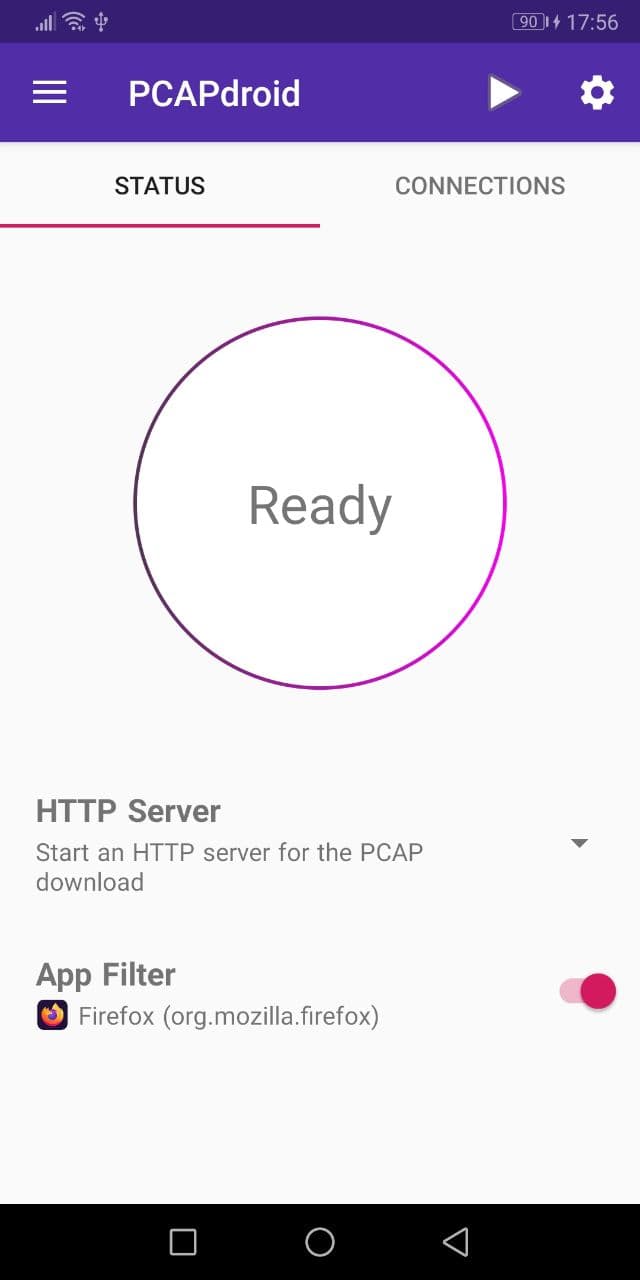 emanuele-f/pcapdroid
No-root network monitor, firewall and PCAP dumper for Android

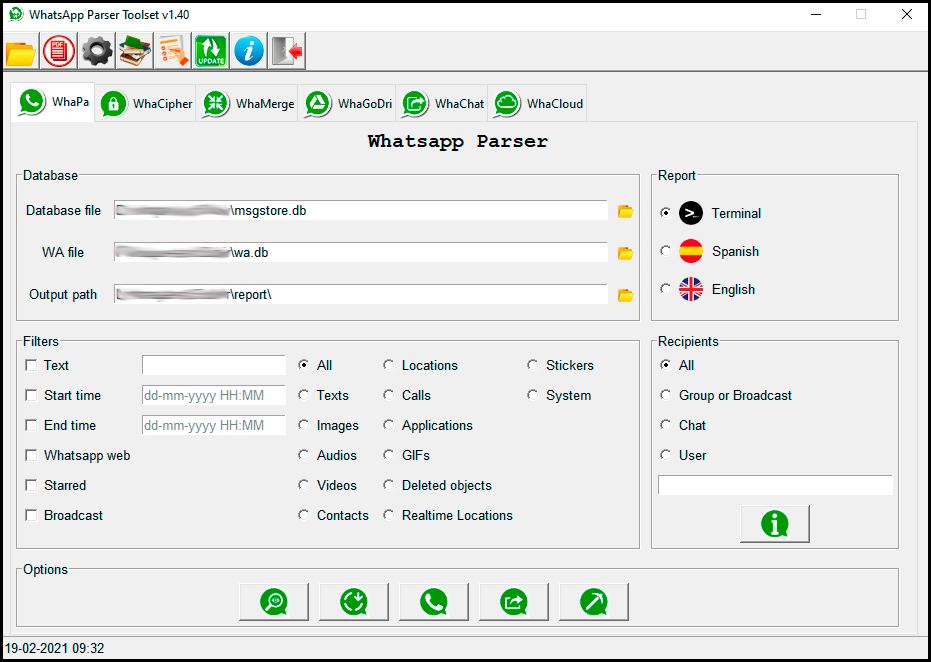 b16f00t/whapa
Graphical forensic toolkit for parsing, decrypting, and extracting WhatsApp data from Android and iOS devices, including Google Drive and iCloud…
 kjcracks/clutch
Jailbreak-only iOS utility that decrypts installed app executables and dumps them as .ipa or raw binary files for security research and…
 eldavoo/wa-crypt-tools
Manage WhatsApp .crypt12, .crypt14 and .crypt15 files.
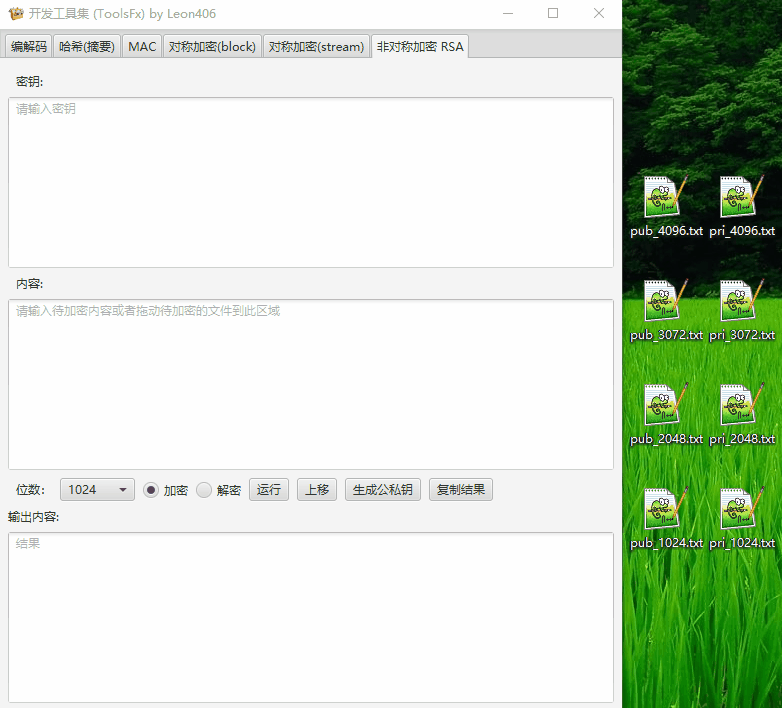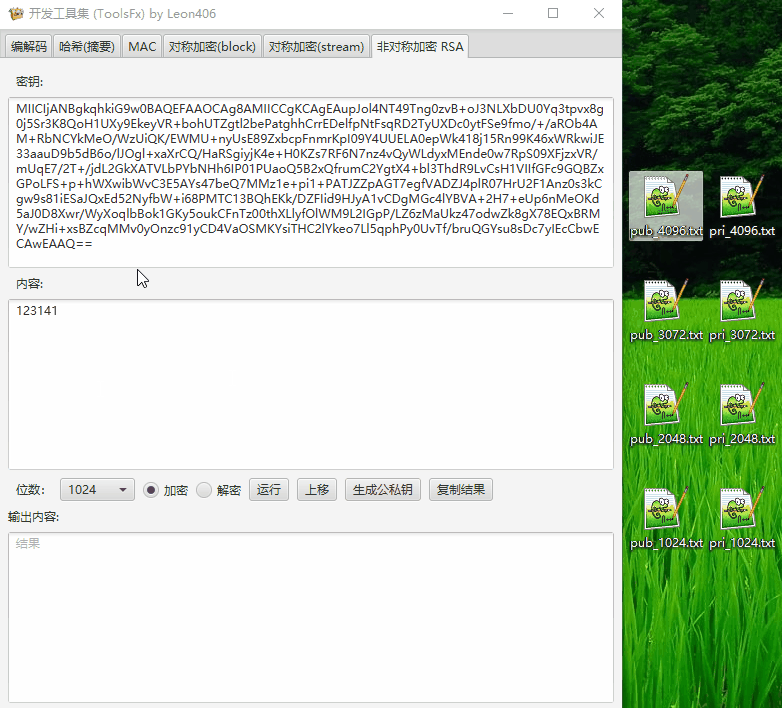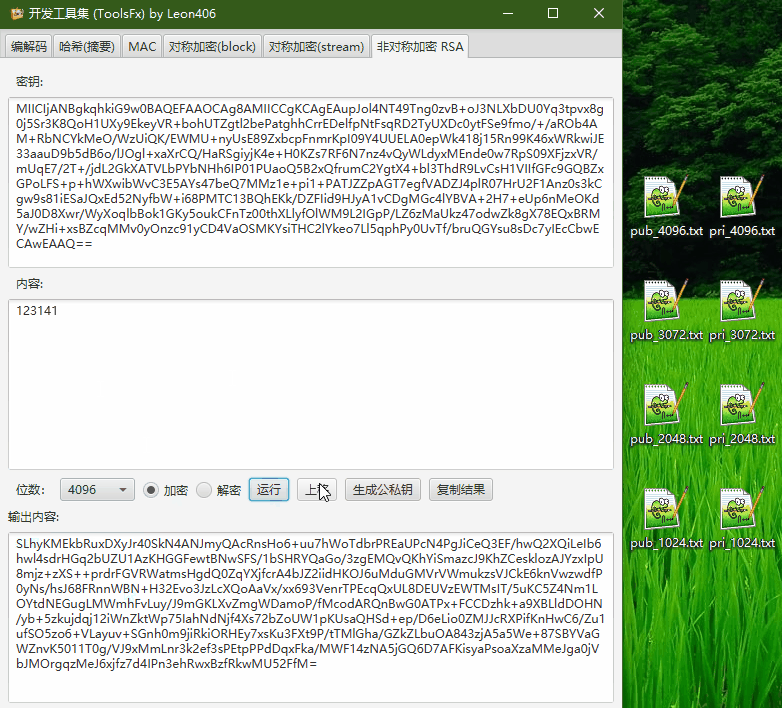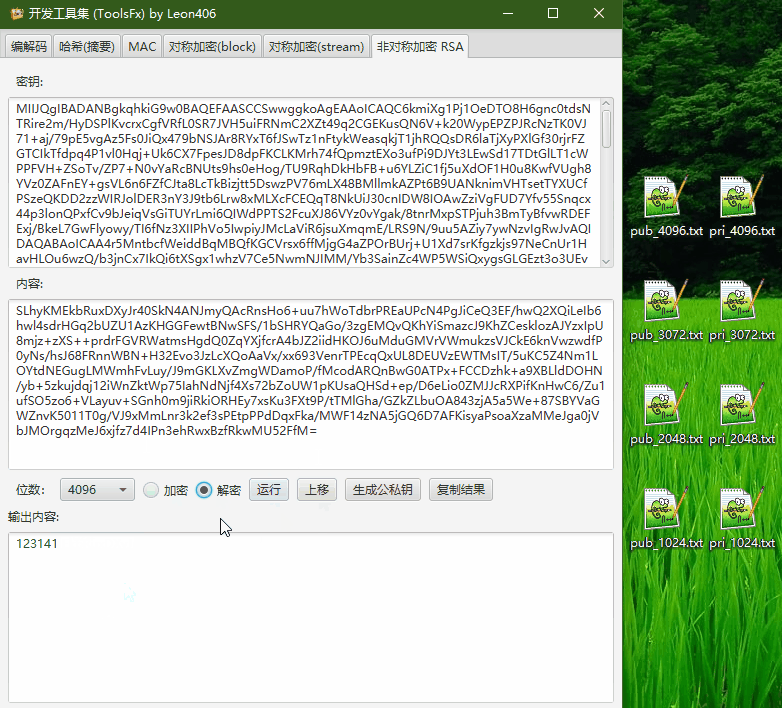 leon406/toolsfx
跨平台密码学工具箱。包含编解码,编码转换,加解密, 哈希,MAC,签名,大数运算,压缩,二维码功能,CTF等功能。