

Nimcrypt2
 icyguider/nimcrypt2
.NET, PE, & Raw Shellcode Packer/Loader Written in Nim
binary-analysisdefensive-toolsencryption-decryption-tools+6
8254 years ago
icyguider/nimcrypt2.NET, PE, & Raw Shellcode Packer/Loader Written in Nim
 gabemarshall/brosec
Brosec - An interactive reference tool to help security professionals utilize useful payloads and commands.
 captmag/maldev
Creation of multiple Malware tools consisting of evasion, enumeration and exploitation
 h3xduck/umbra
A LKM rootkit targeting 4.x and 5.x kernel versions which opens a backdoor that can spawn a reverse shell to a remote host, launch malware and more.
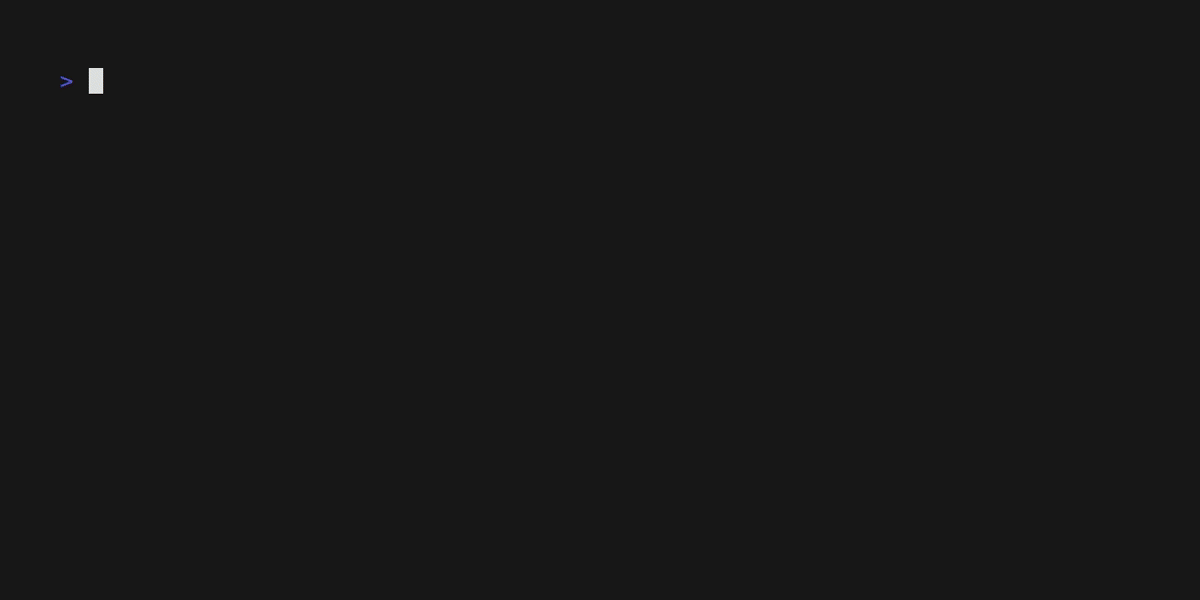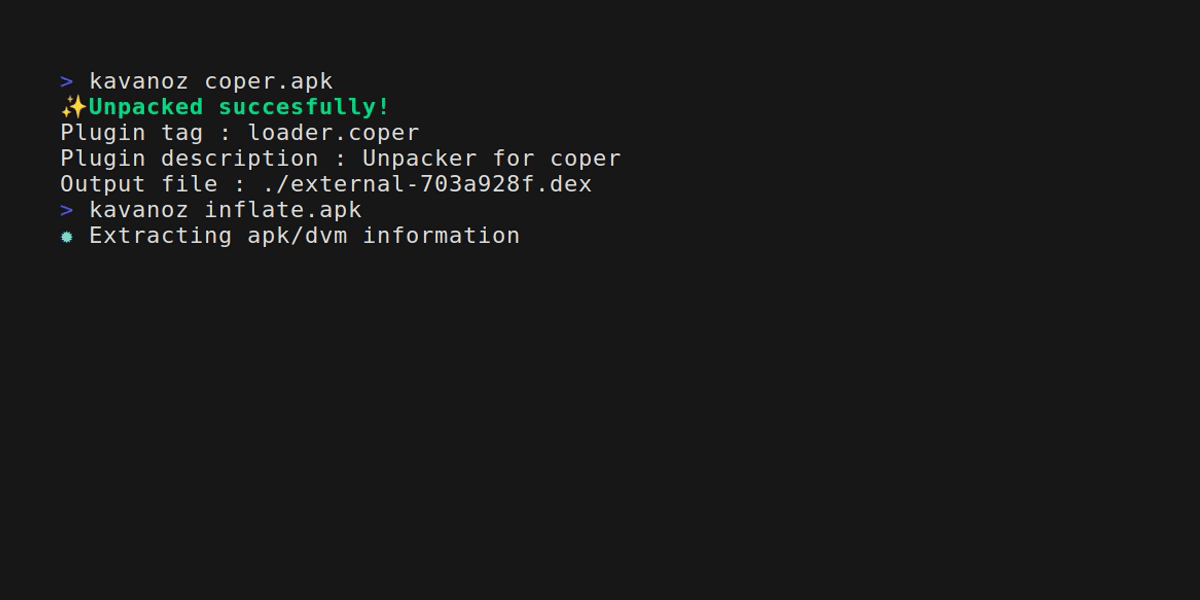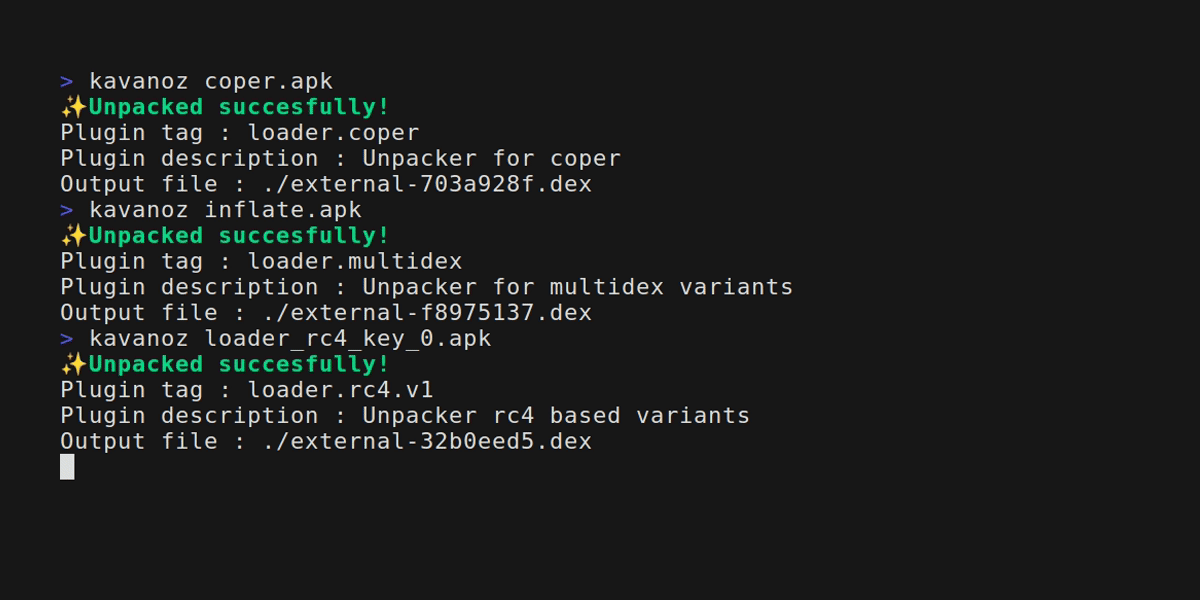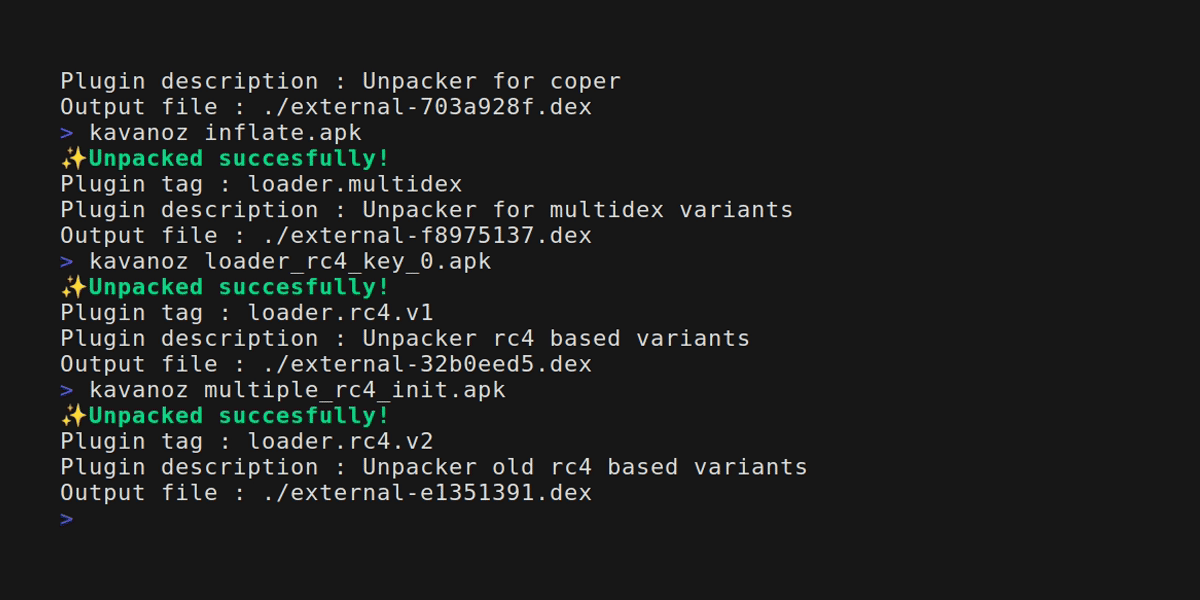 eybisi/kavanoz
Statically unpacking common android banker malware.
 enelg52/kittystager
KittyStager is a simple stage 0 C2. It is made of a web server to host the shellcode and an implant, called kitten. The purpose of this project is to…
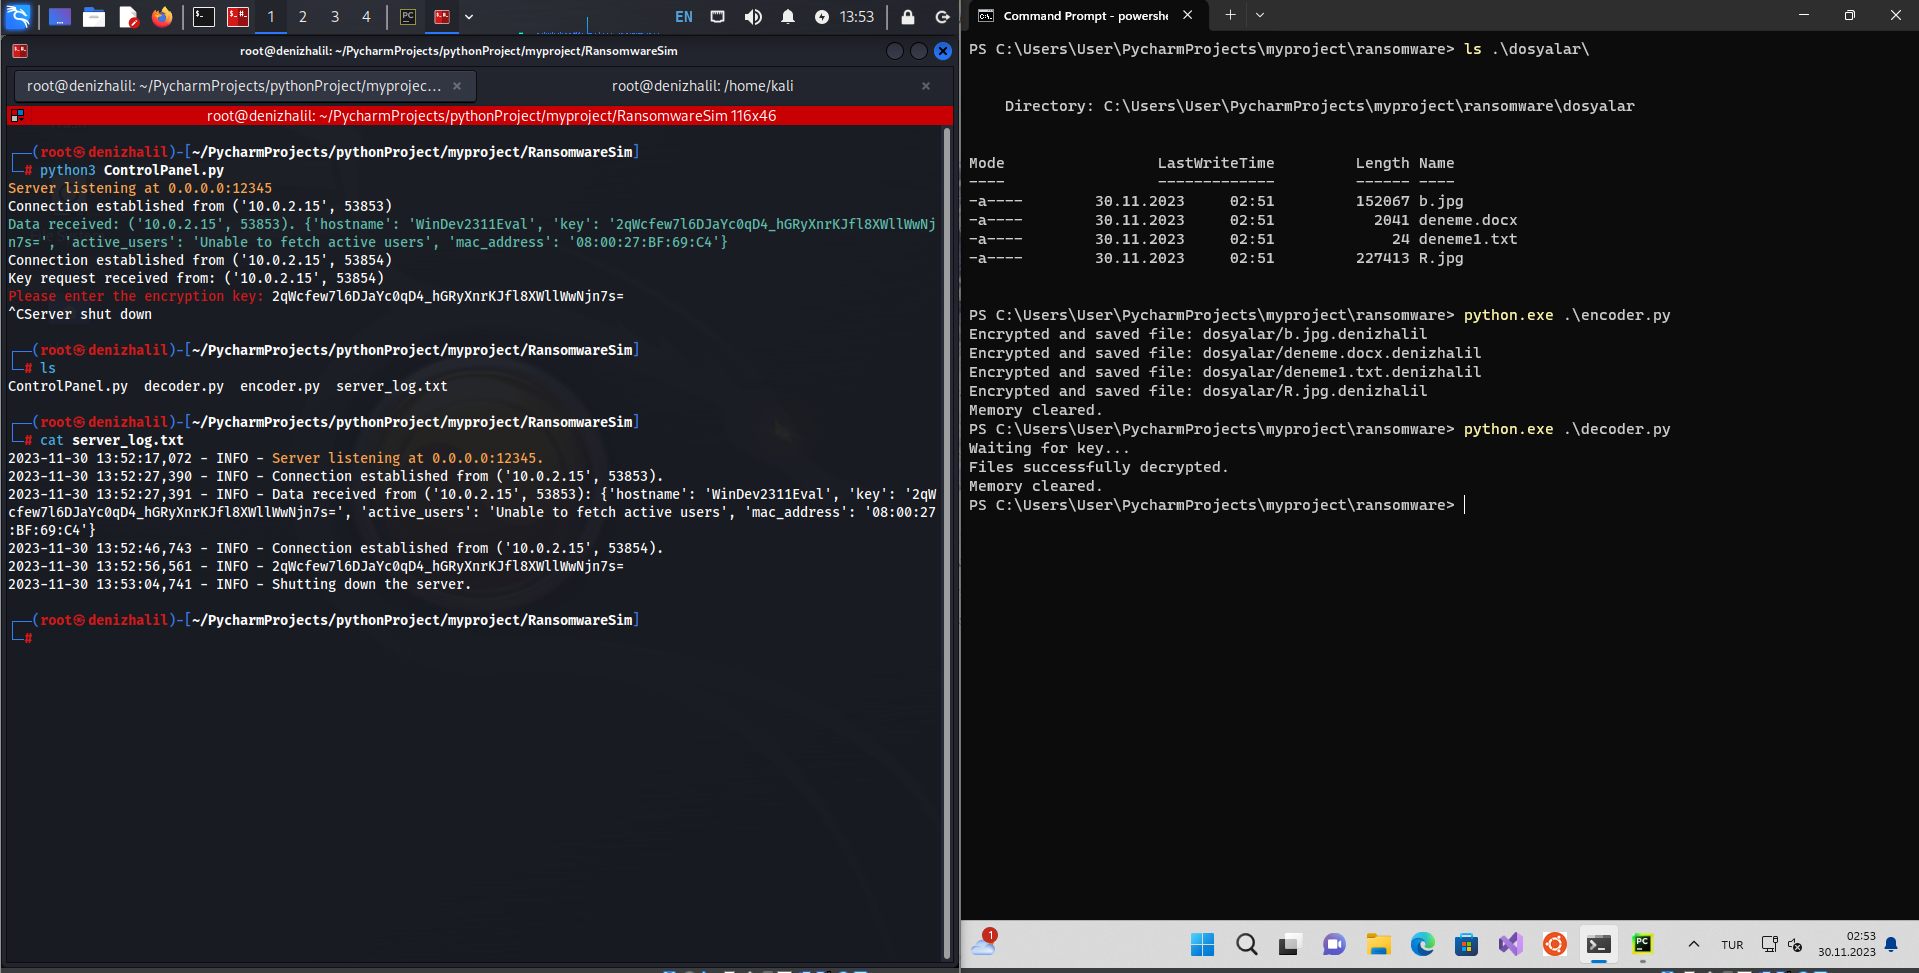 halildeniz/ransomwaresim
Educational ransomware simulator demonstrating file encryption, C2 communication, and decryption for cybersecurity training and malware analysis.
 nmantani/fileinsight-plugins
FileInsight-plugins: decoding toolbox of McAfee FileInsight hex editor for malware analysis
 farghlymal/config-extractors
Extracts and decrypts malware configuration data from captured samples, automating C2 endpoint discovery, credential extraction, and indicator triage…

 roxanne_ardary/safeforge
SafeForge is an open-source mobile app hub built on GitLab that enables developers to build, upload, and share applications in a secure, AI-verified…
 mattnotmax/cyberchef-recipes
A list of cyber-chef recipes and curated links
 frenchcisco/ratel
RAT-el is an open source penetration test tool that allows you to take control of a windows machine. It works on the client-server model, the server…
 hazcod/ransomwhere
A PoC ransomware sample to test out your ransomware response strategy.
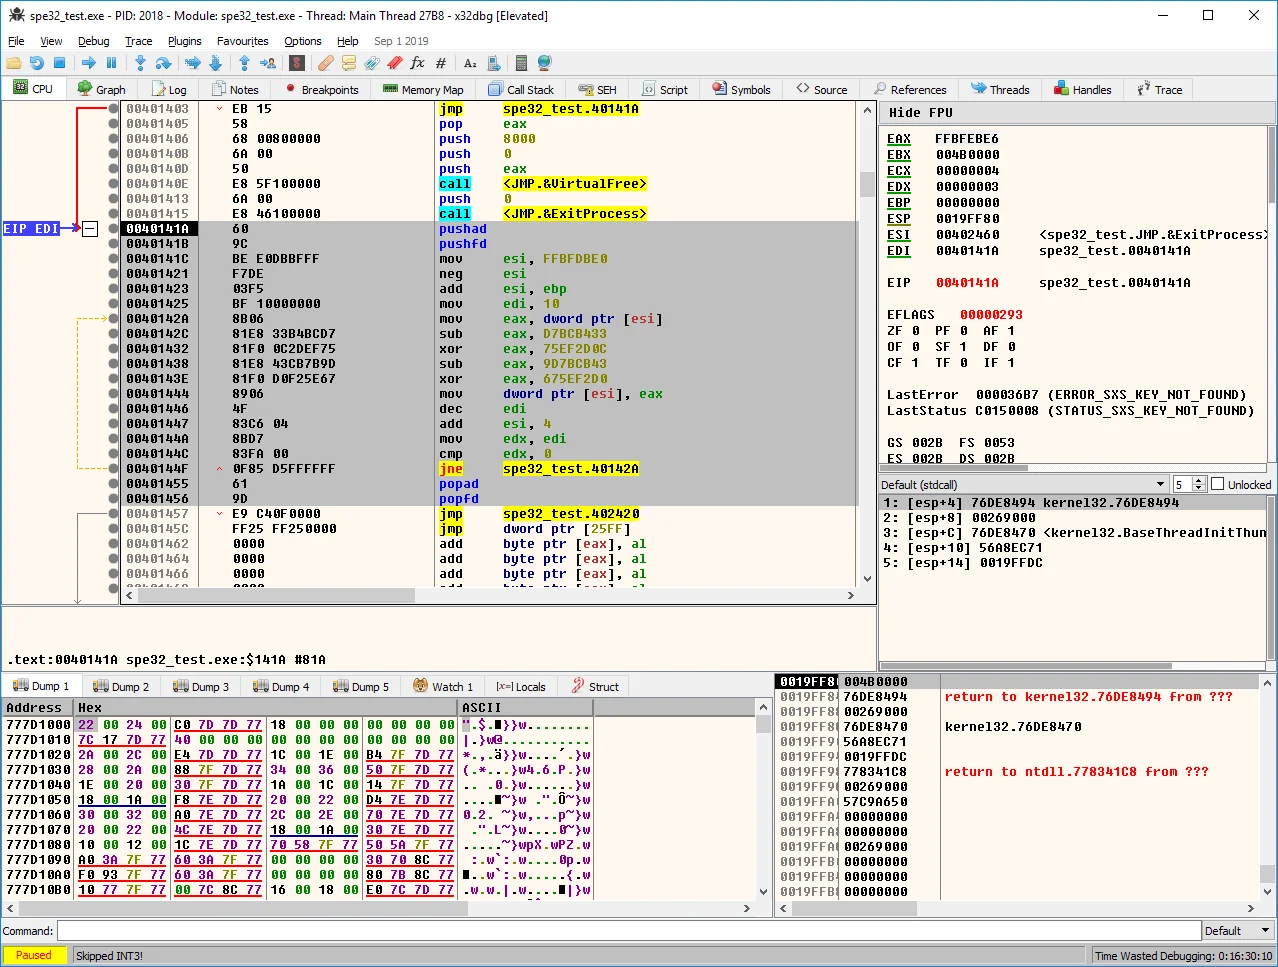 pelock/simple-polymorphic-engine-spe32
Generates unique polymorphic decryption code for encrypting data, using randomly selected instructions and keys, with junk opcode generation. Written…
 knight0x07/bumblecrypt
A Bumblebee-inspired Crypter
 cybercentrecanada/cart
Python implementation of the CaRT library for (un)inerting files.
 nicchongwb/rootsmart-v2.0
Android Ransomware Development - AES256 encryption + CVE-2019-2215 (reverse root shell) + Data Exfiltration
 gojue/ecapture
Capturing SSL/TLS plaintext without a CA certificate using eBPF. Supported on Linux/Android kernels for amd64/arm64.