apache__rocketmq_CVE-2019-17572_4-6-0

Exploit for Apache RocketMQ CVE-2019-17572 targeting distributed messaging platforms with authentication and encryption features.

Exploit for Apache RocketMQ CVE-2019-17572 targeting distributed messaging platforms with authentication and encryption features.

Enterprise Security API library providing security controls for Java web applications, including authentication, access control, input validation,…

Base64-based encryption oracle exploit for CVE-2017-9248 (Telerik UI for ASP.NET AJAX dialog handler)

Exploit for CVE-2024-43044 enabling arbitrary file read from Jenkins controller to extract and decrypt credentials.xml using secret keys.

Python exploit script for CVE-2019-5420, targeting Ruby on Rails signed-session AES GCM key brute-forcing to achieve remote code execution in…

Proof-of-concept for CVE-2018-0114, demonstrating unauthenticated remote token re-signing vulnerability in versions before 0.11.0.

Advanced dork Search & Mass Exploit Scanner

A portable, padding oracle exploit API

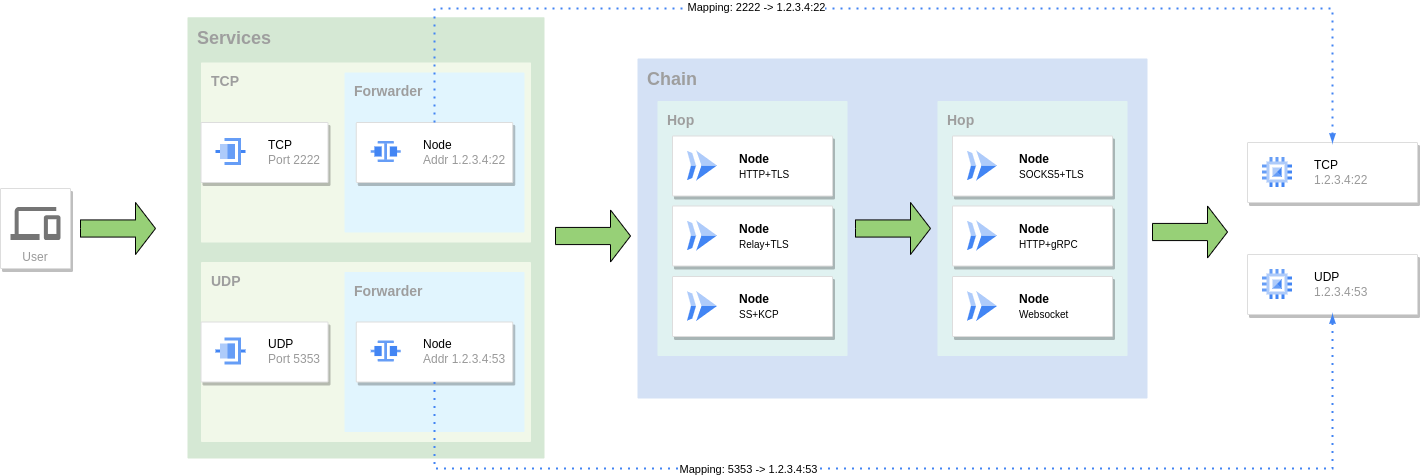
GO Simple Tunnel - a simple tunnel written in golang

Tunneling data over webrtc to bypass censorship

A PHP backdoor management and generation tool/C2 featuring end to end encrypted payload streaming designed to bypass WAF, IDS, SIEM systems.

HikvisionExploiter is a Python-based utility designed to automate exploitation and directory accessibility checks on Hikvision network cameras…

This Tool To Test Machine Keys In View State

A starttls-capable transparent man-in-the-middle proxy

CodeIgniter <=2.1.4 session cookie decryption vulnerability

Configurable Rust HTTP MITM proxy with TLS , HTTP/2 and TCP fingerprint spoofing.

泛微oa数据库配置文件读取

用于借助FOFA快速测试海康威视的CVE-2017-7921漏洞,并且给出登陆账号和密码,并输出json文件。