

PSRansom
 joelgmsec/psransom
PowerShell Ransomware Simulator with C2 Server
command-and-controleducationencryption-decryption-tools+1
joelgmsec/psransomPowerShell Ransomware Simulator with C2 Server
 cedricbonhomme/stegano
A pure Python steganography module.
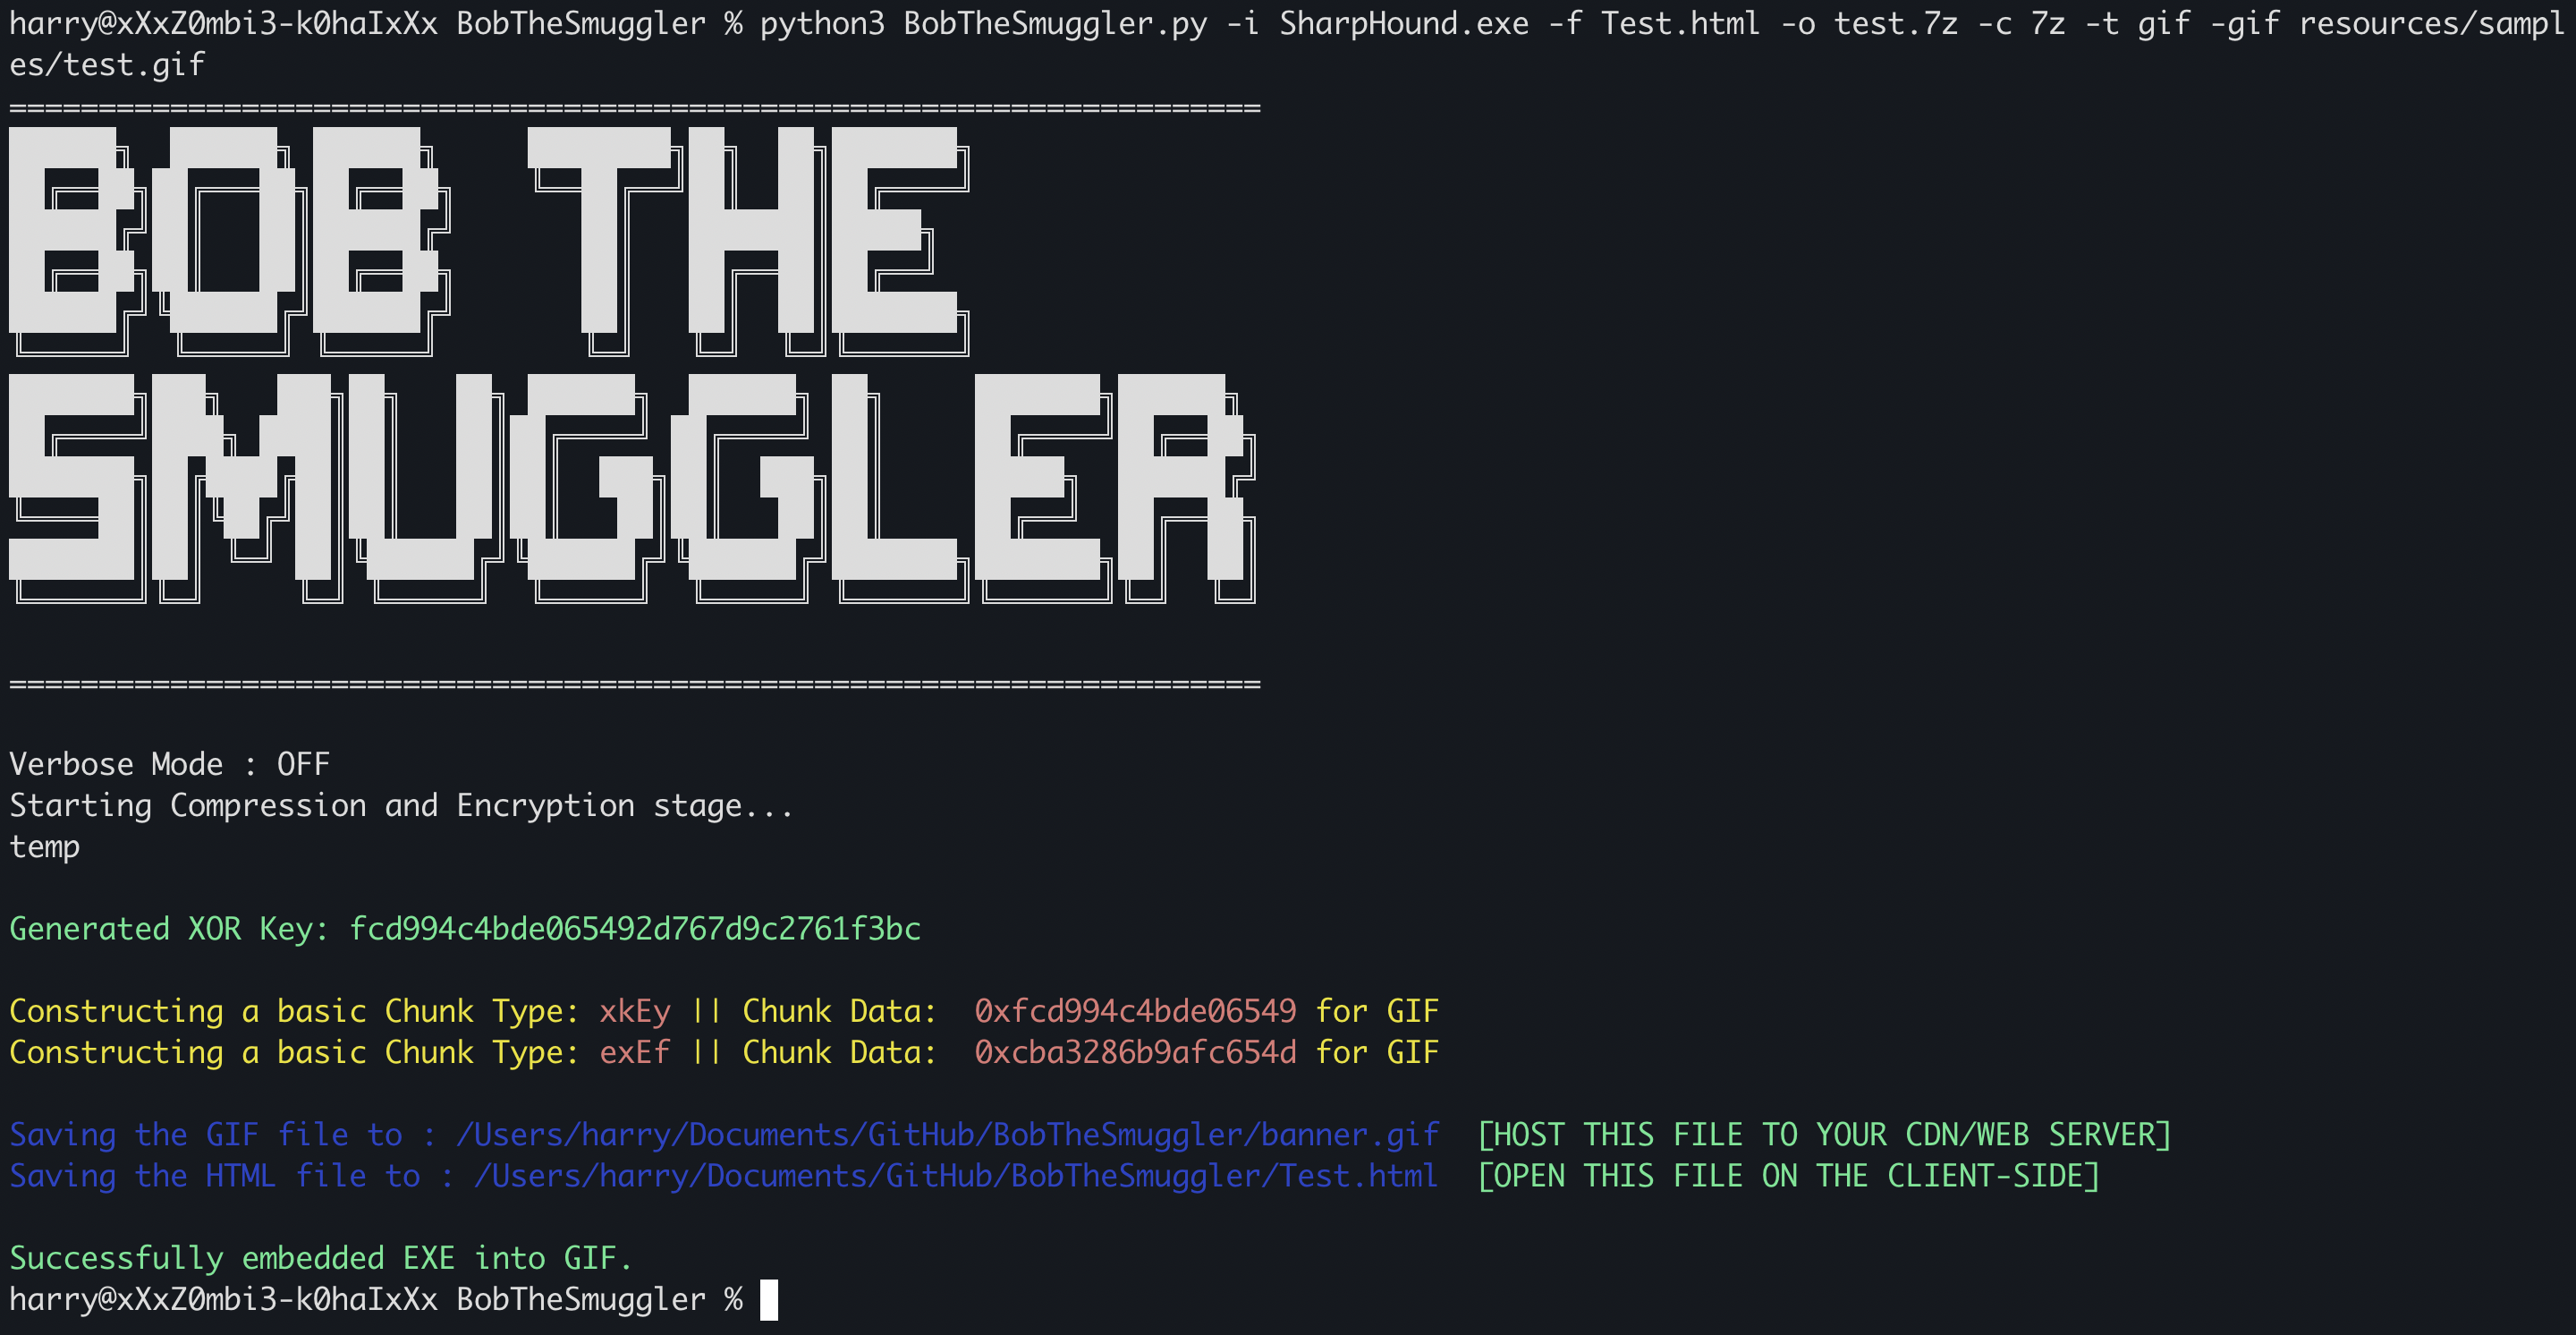 thecyb3ralpha/bobthesmuggler
"Bob the Smuggler": A tool that leverages HTML Smuggling Attack and allows you to create HTML files with embedded 7z/zip archives. The tool would…
 cy4nguy/python-ransomware
Complete Python RansomeWare Source Code With Full Decoumetions.
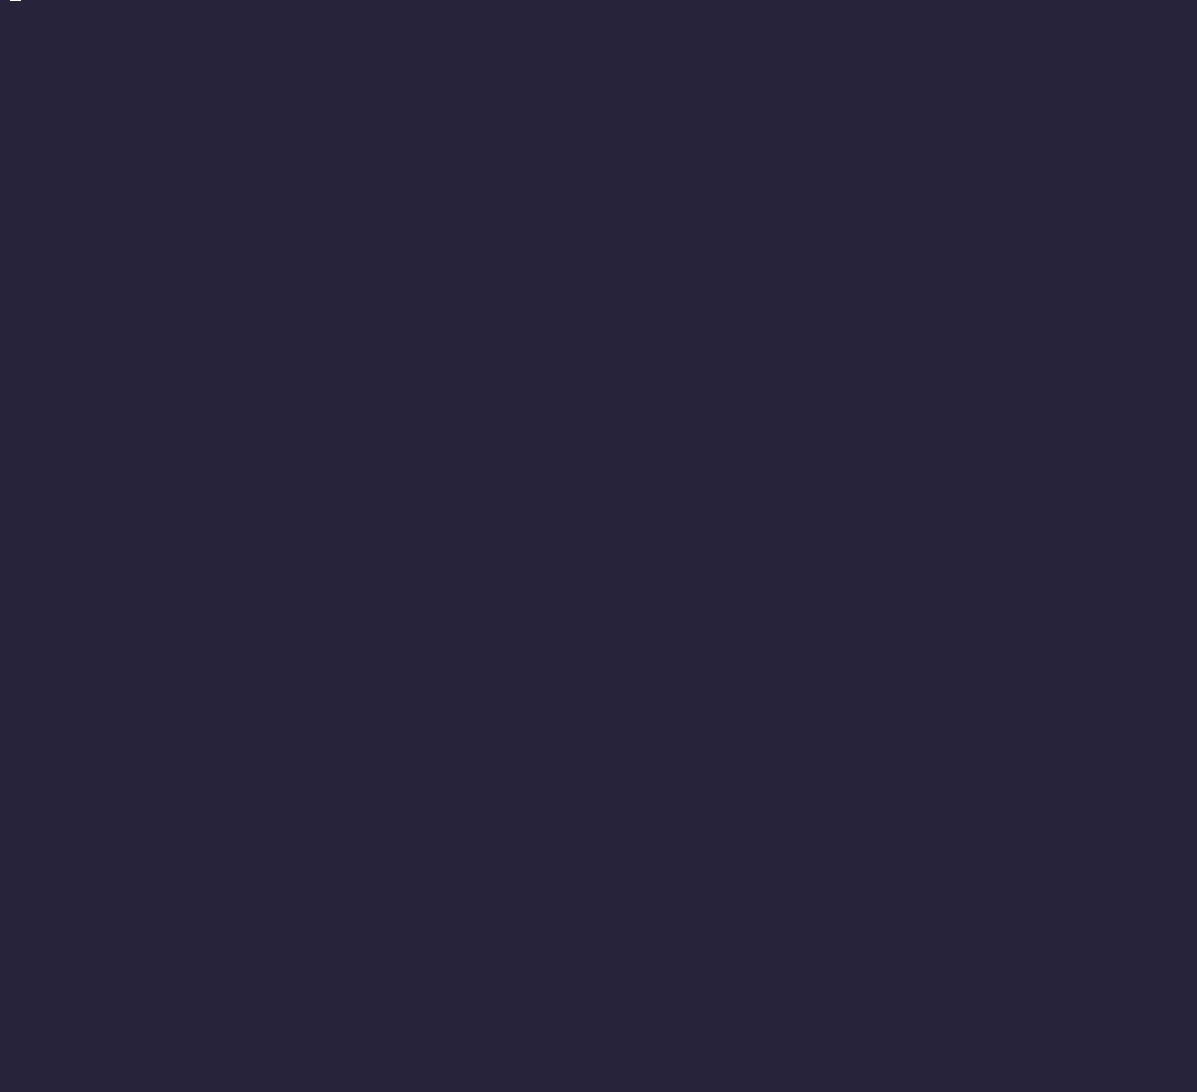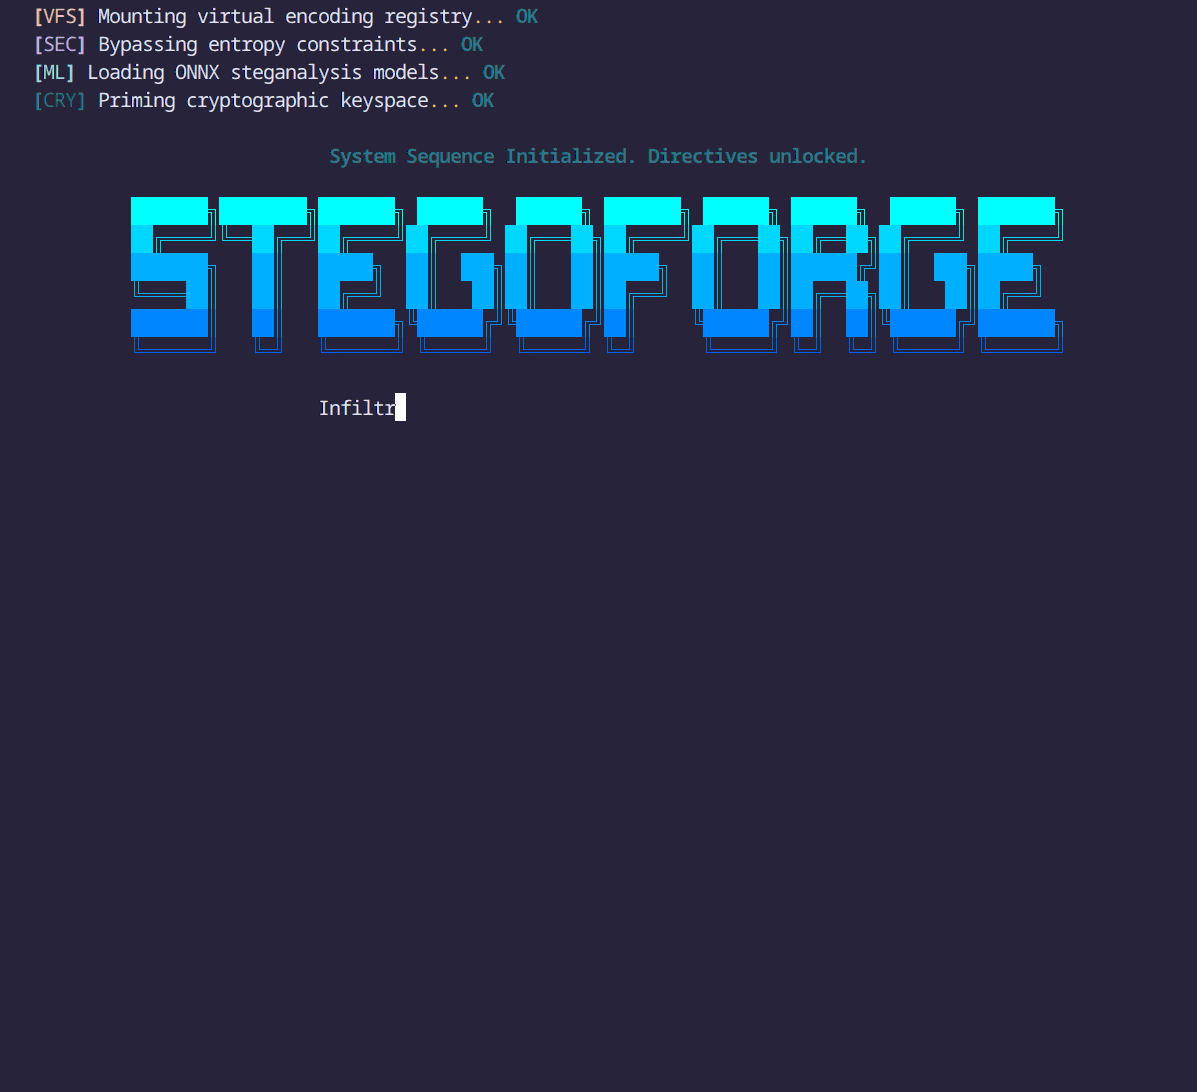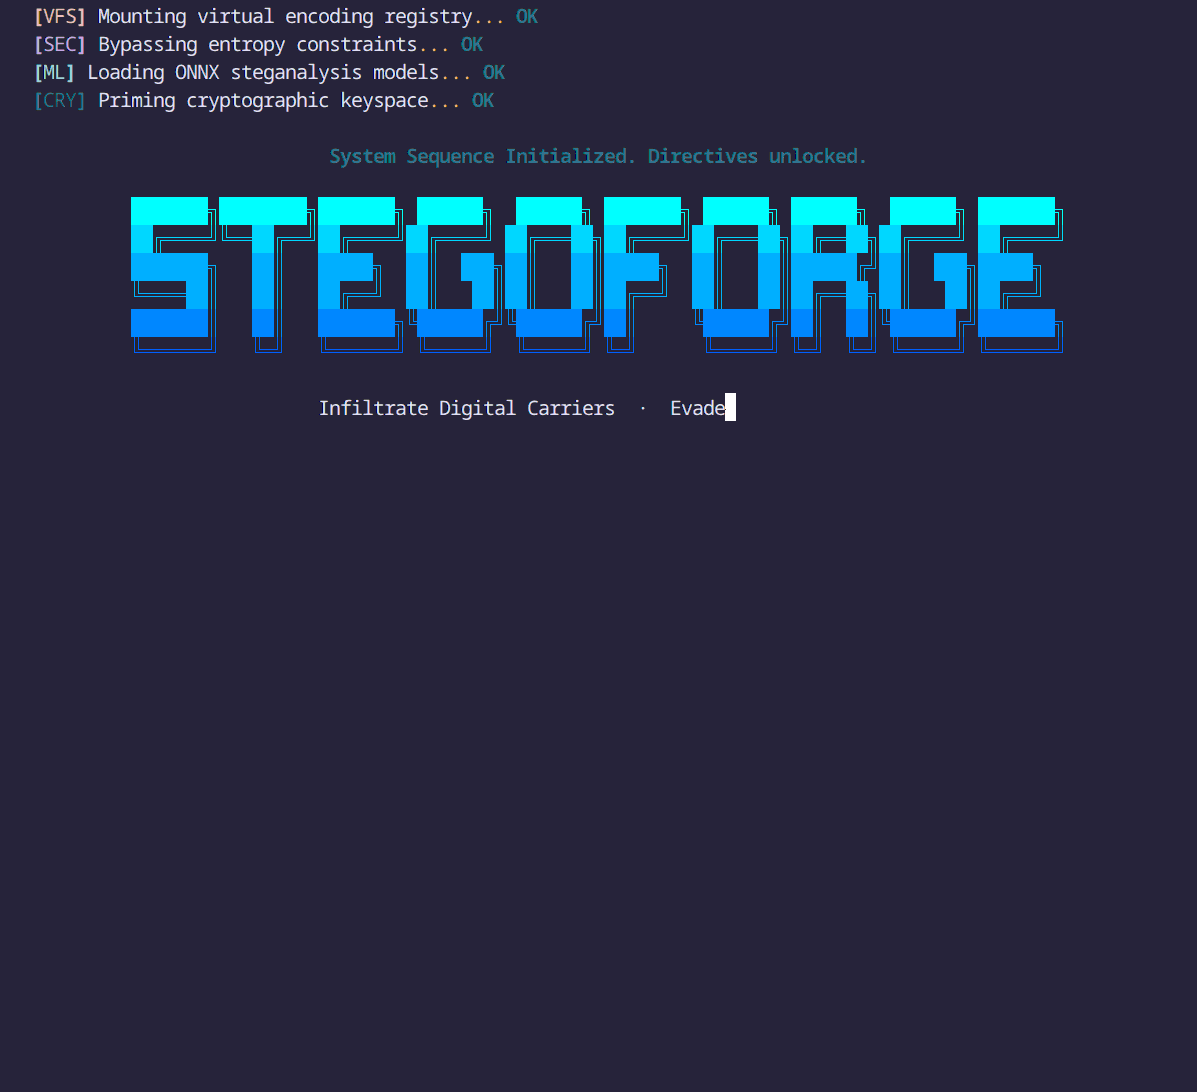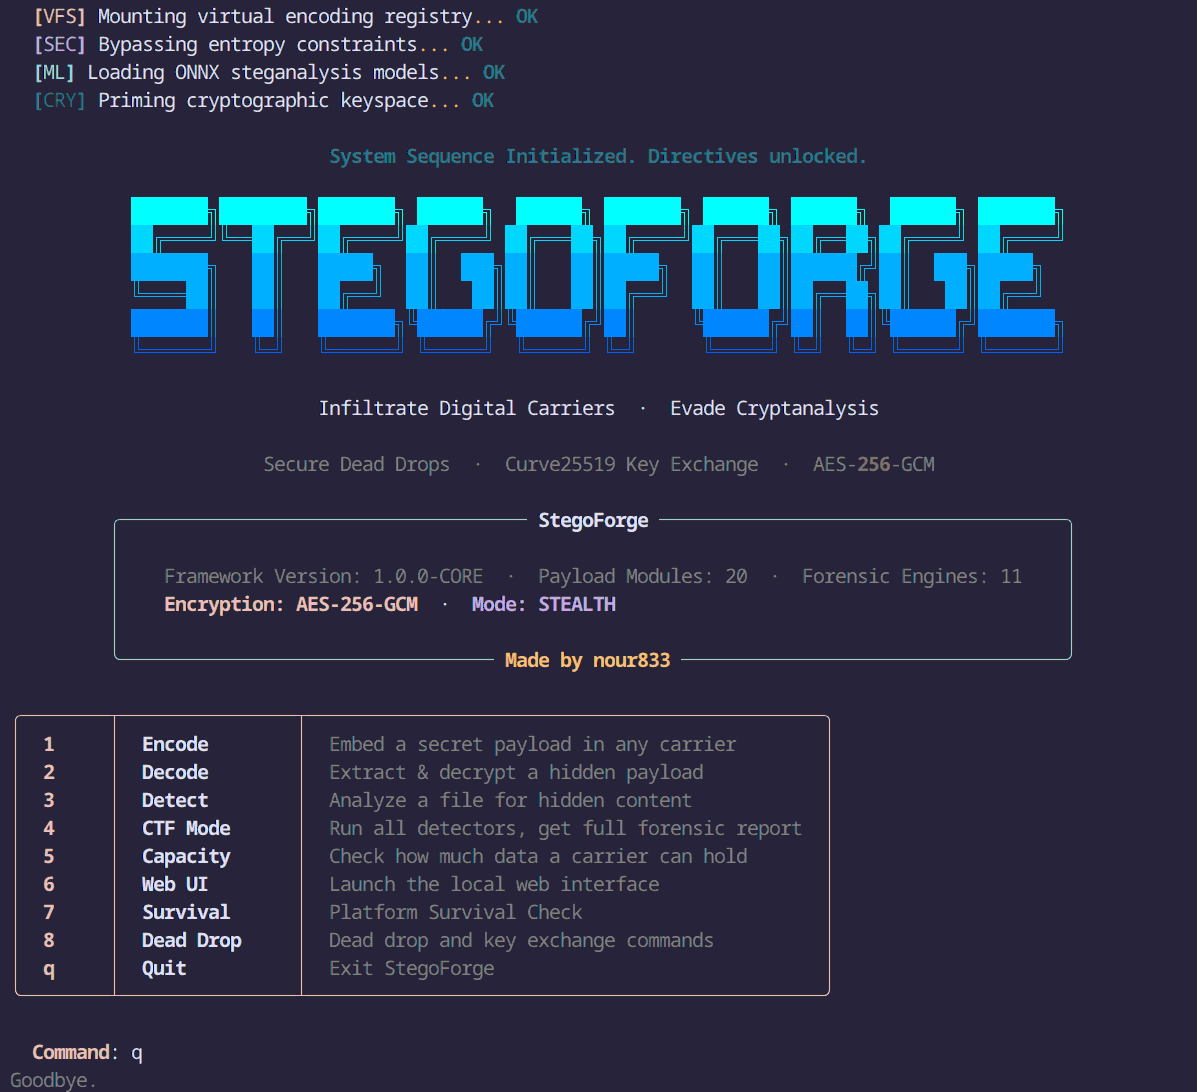 nour833/stegoforge
The ultimate steganography and digital forensics toolkit. Hide and extract data across images, audio, video, documents, and network packets, or run…
 iss4cf0ng/openpetya
A Proof-of-Concept bootkit and UEFI boot application inspired by Petya ransomware, written in Assembly, C, and C++
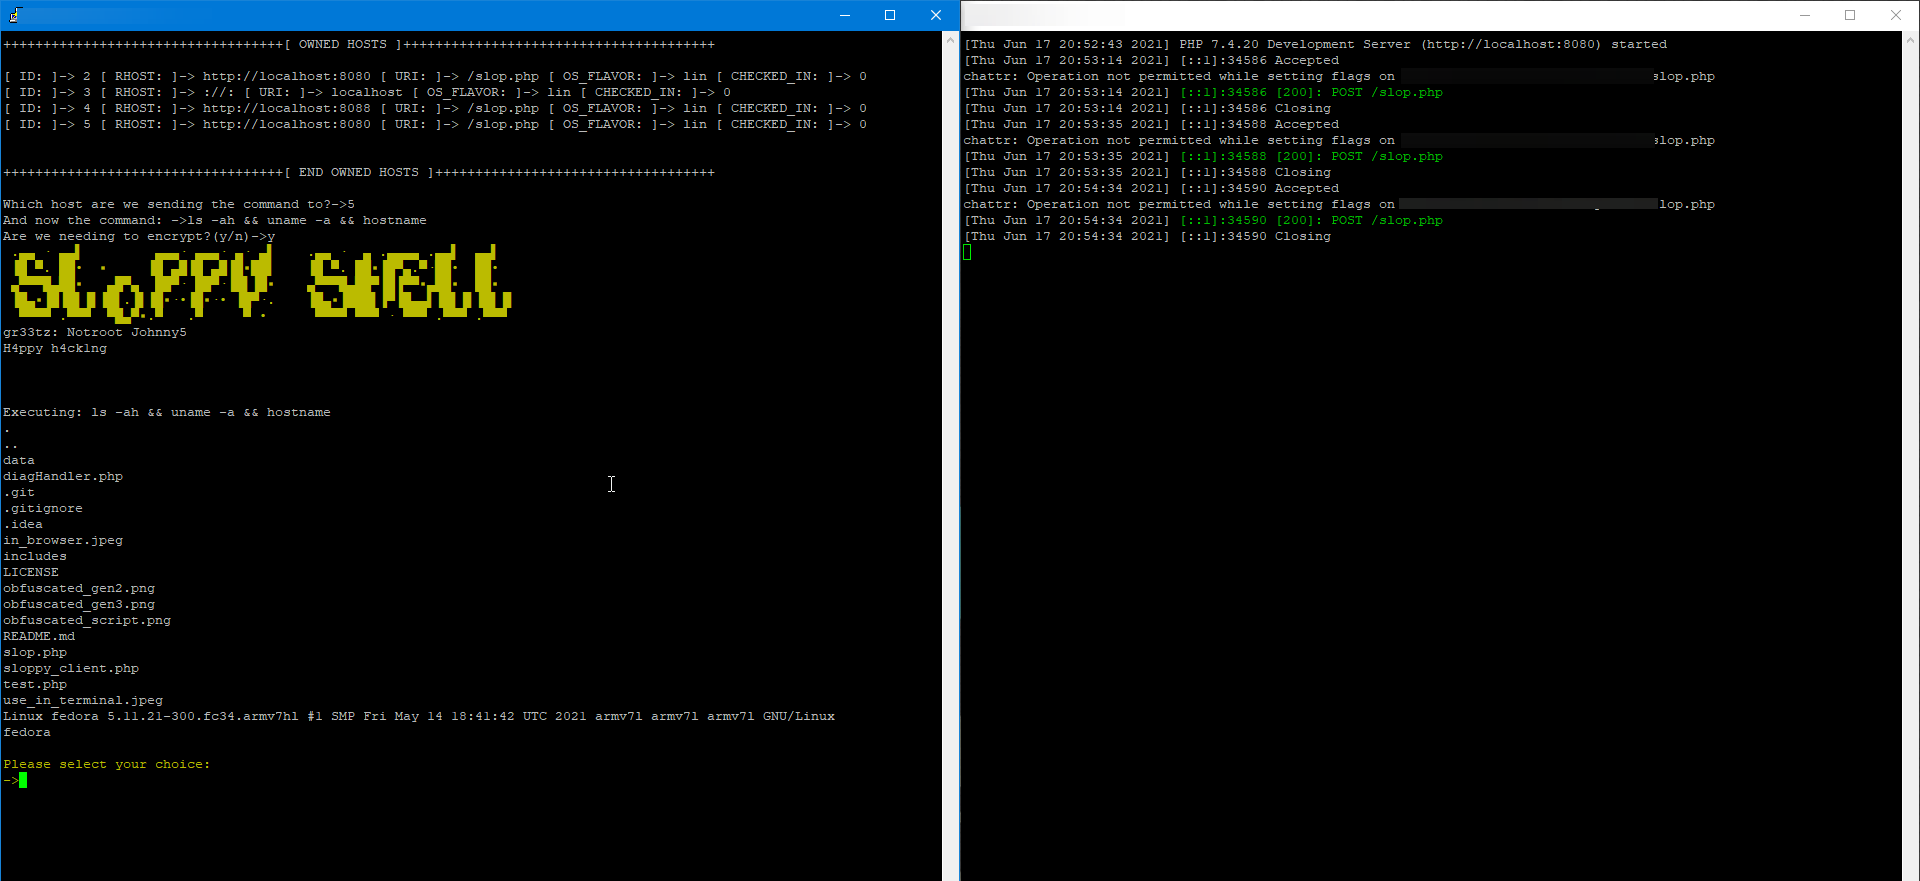 oldkingcone/slopshell
the only php webshell you need.
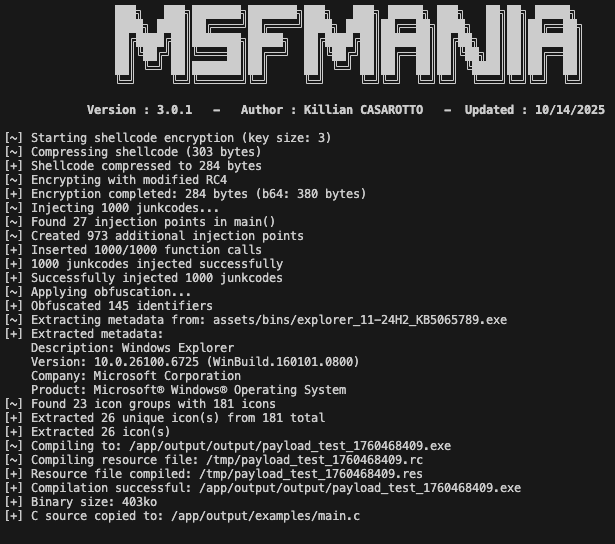 lepotekil/msfmania
Python AV Evasion Tools
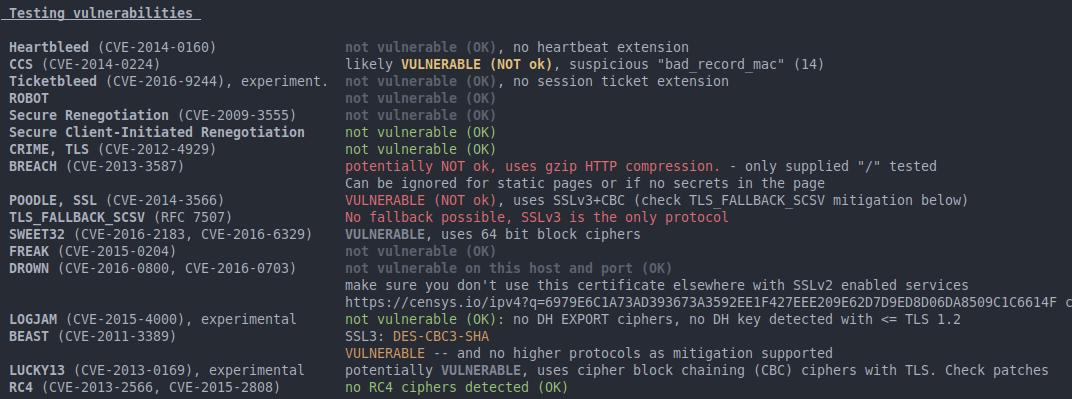 mpgn/poodle-poc
:poodle: Poodle (Padding Oracle On Downgraded Legacy Encryption) attack CVE-2014-3566 :poodle:
 ajayrandhawa/cryptolocker
CryptoLocker is open source files encrypt-er. Crypto is developed in Visual C++. It has features encrypt all file, lock down the system and send keys…
 toddmaustin/mojo-v
RISC-V ISA extension for hardware-enforced secret computation using ML-KEM-512 key encapsulation and SIMON-128 encryption, enabling data-oblivious…
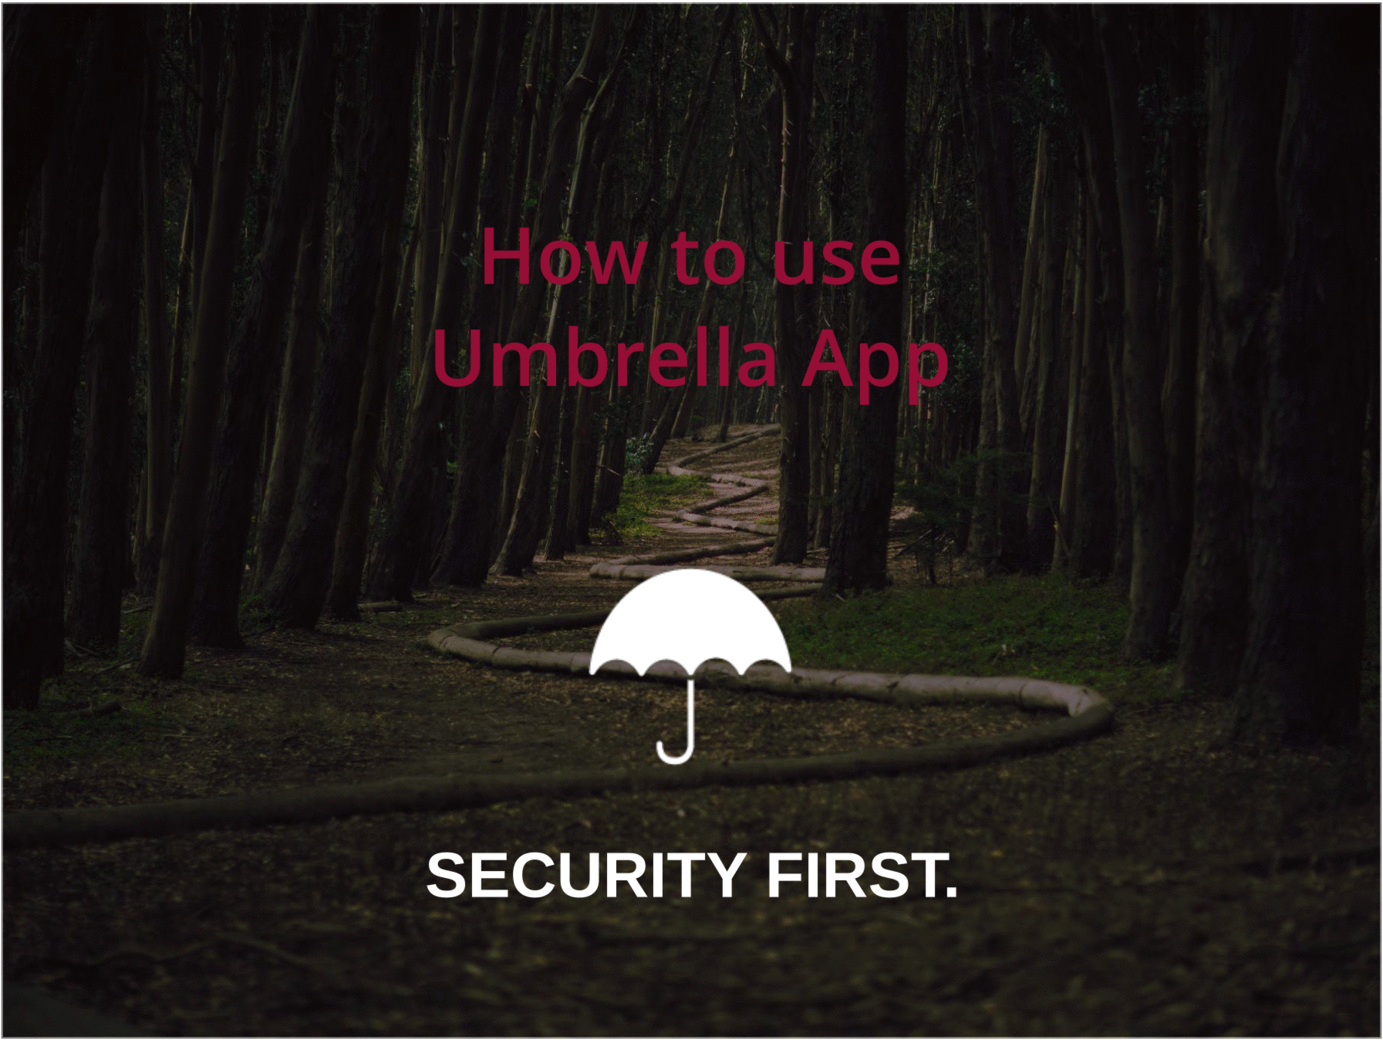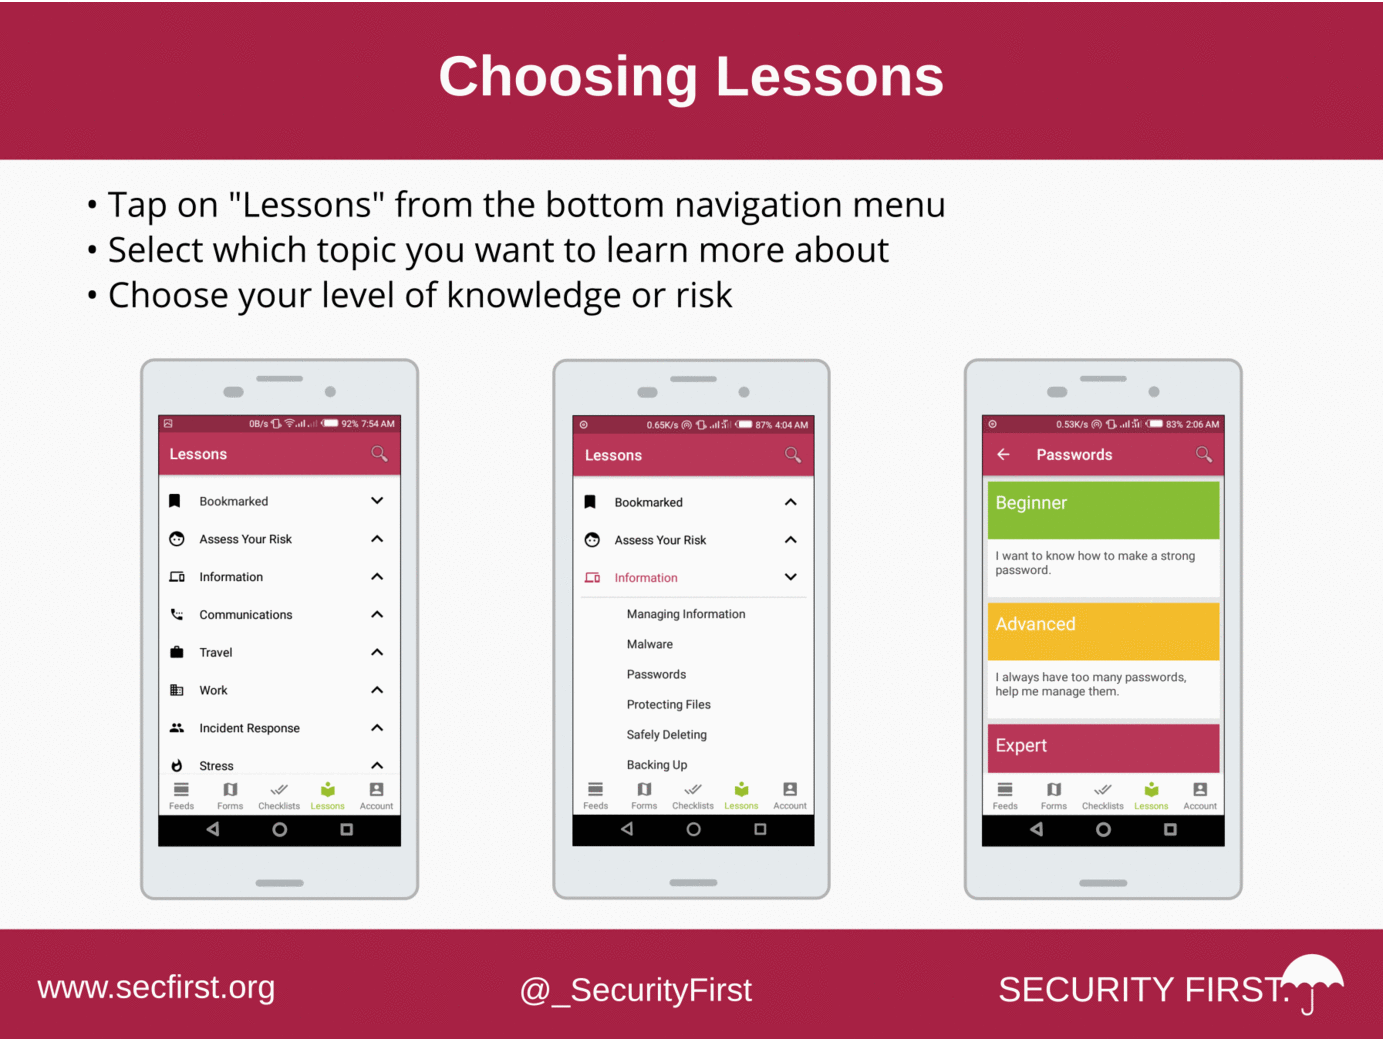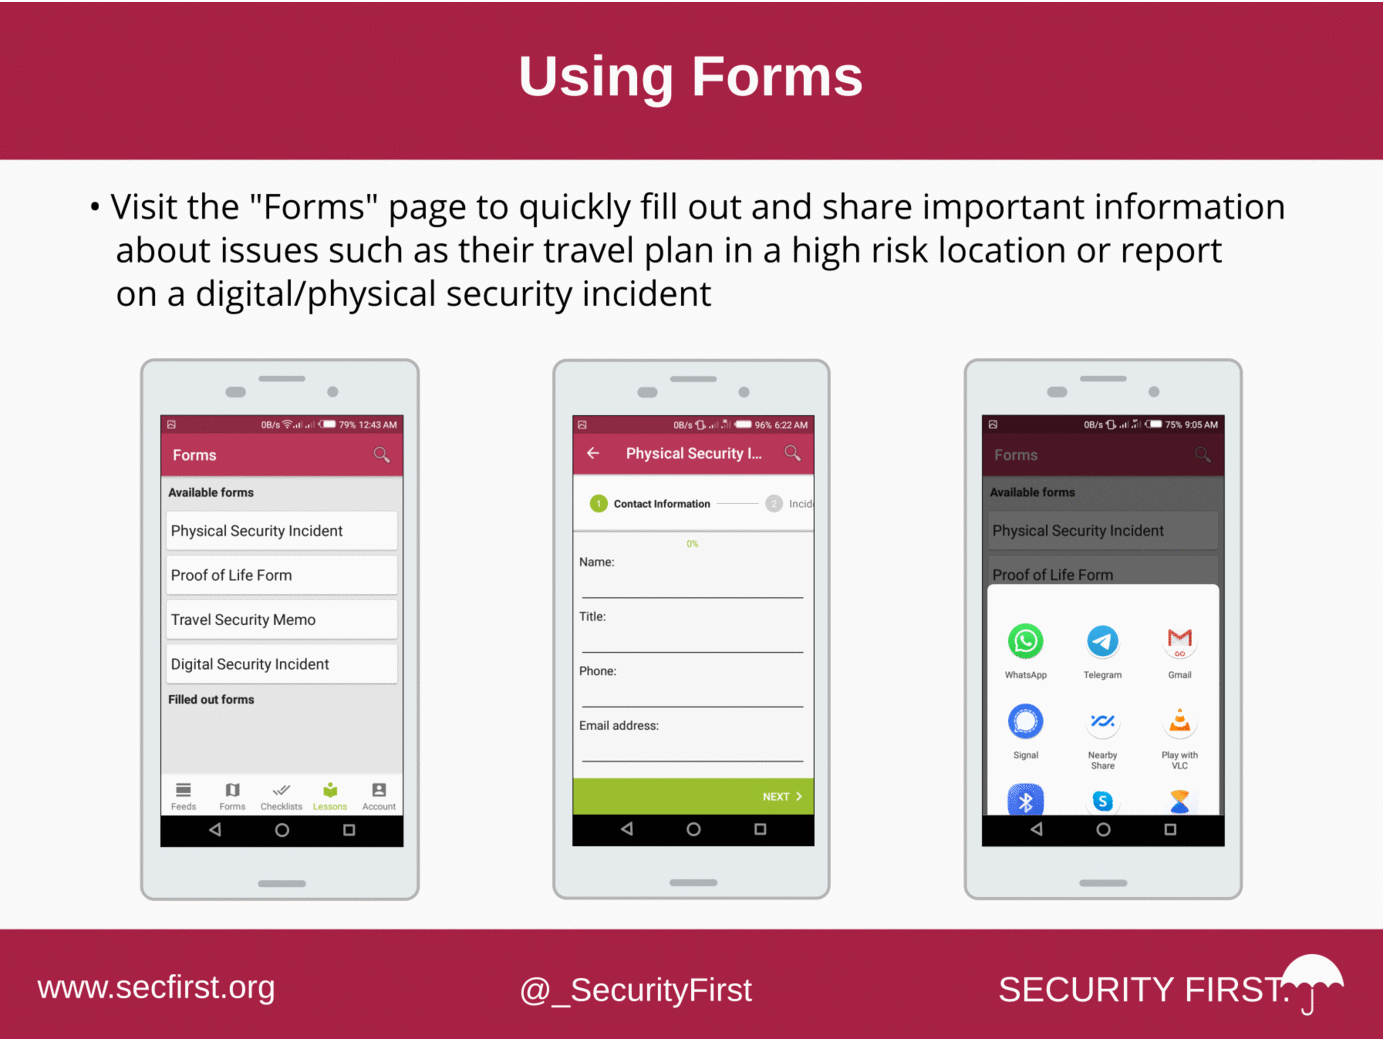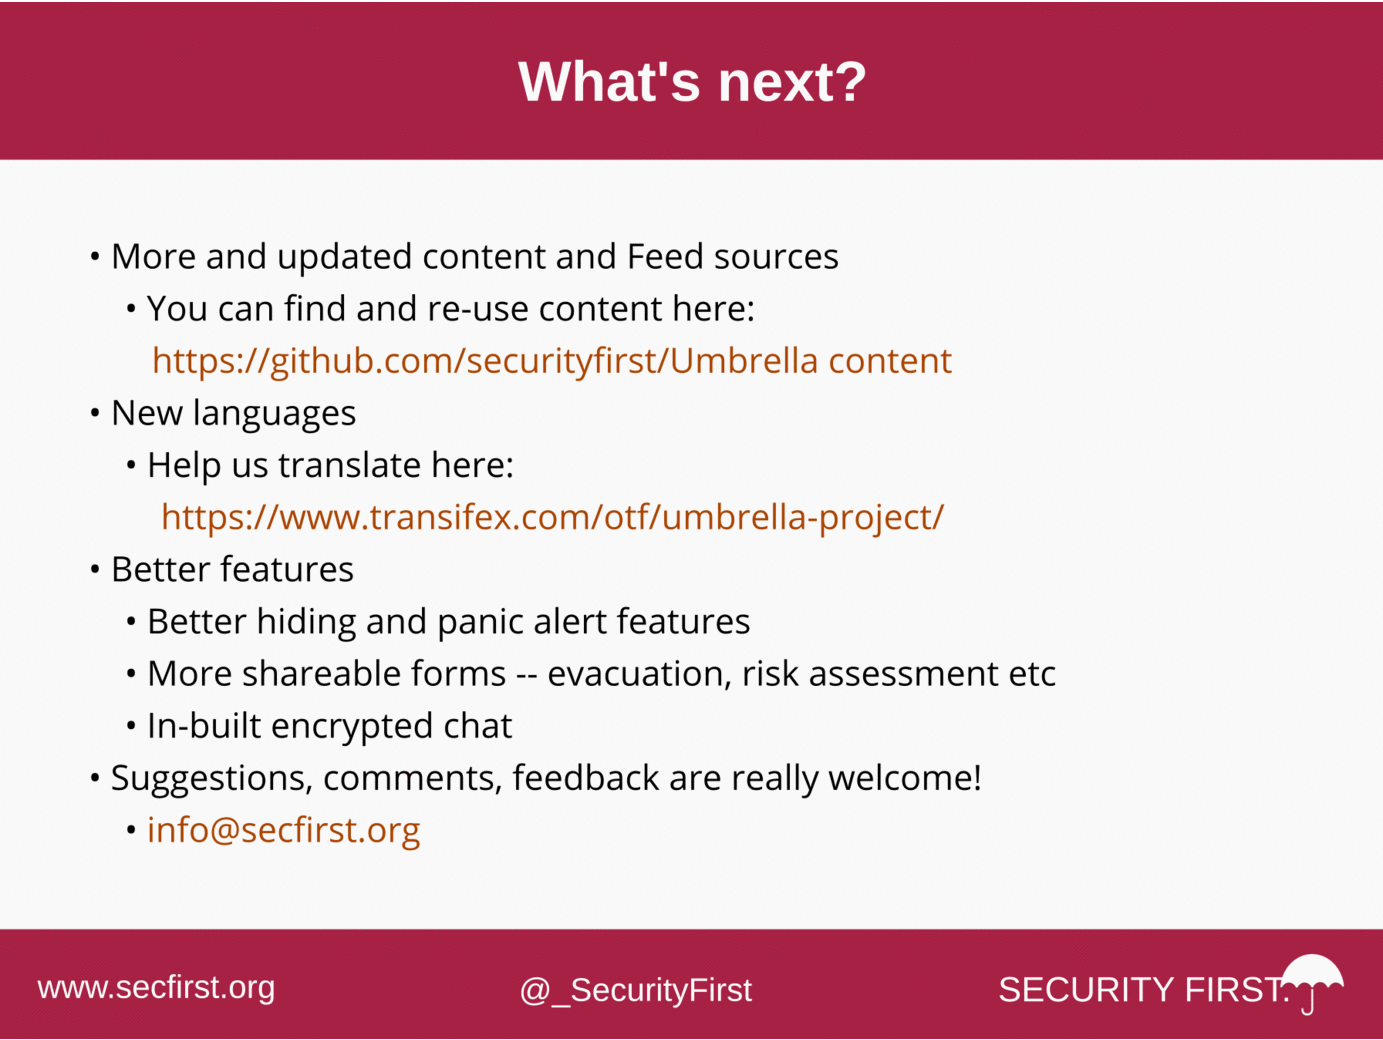 securityfirst/umbrella_android
Open source Android, iOS and Web app for learning about and managing digital and physical security. From how to send a secure message to dealing with…
 enelg52/kittystager
KittyStager is a simple stage 0 C2. It is made of a web server to host the shellcode and an implant, called kitten. The purpose of this project is to…
 captmag/maldev
Creation of multiple Malware tools consisting of evasion, enumeration and exploitation
 cybergem777/hideagem
HIDEAGEM experimental steganography platform.
 acceis/crypto_identifier
Crypto tool for pentest and ctf : try to uncipher data using multiple algorithms and block chaining modes. Usefull for a quick check on unknown…
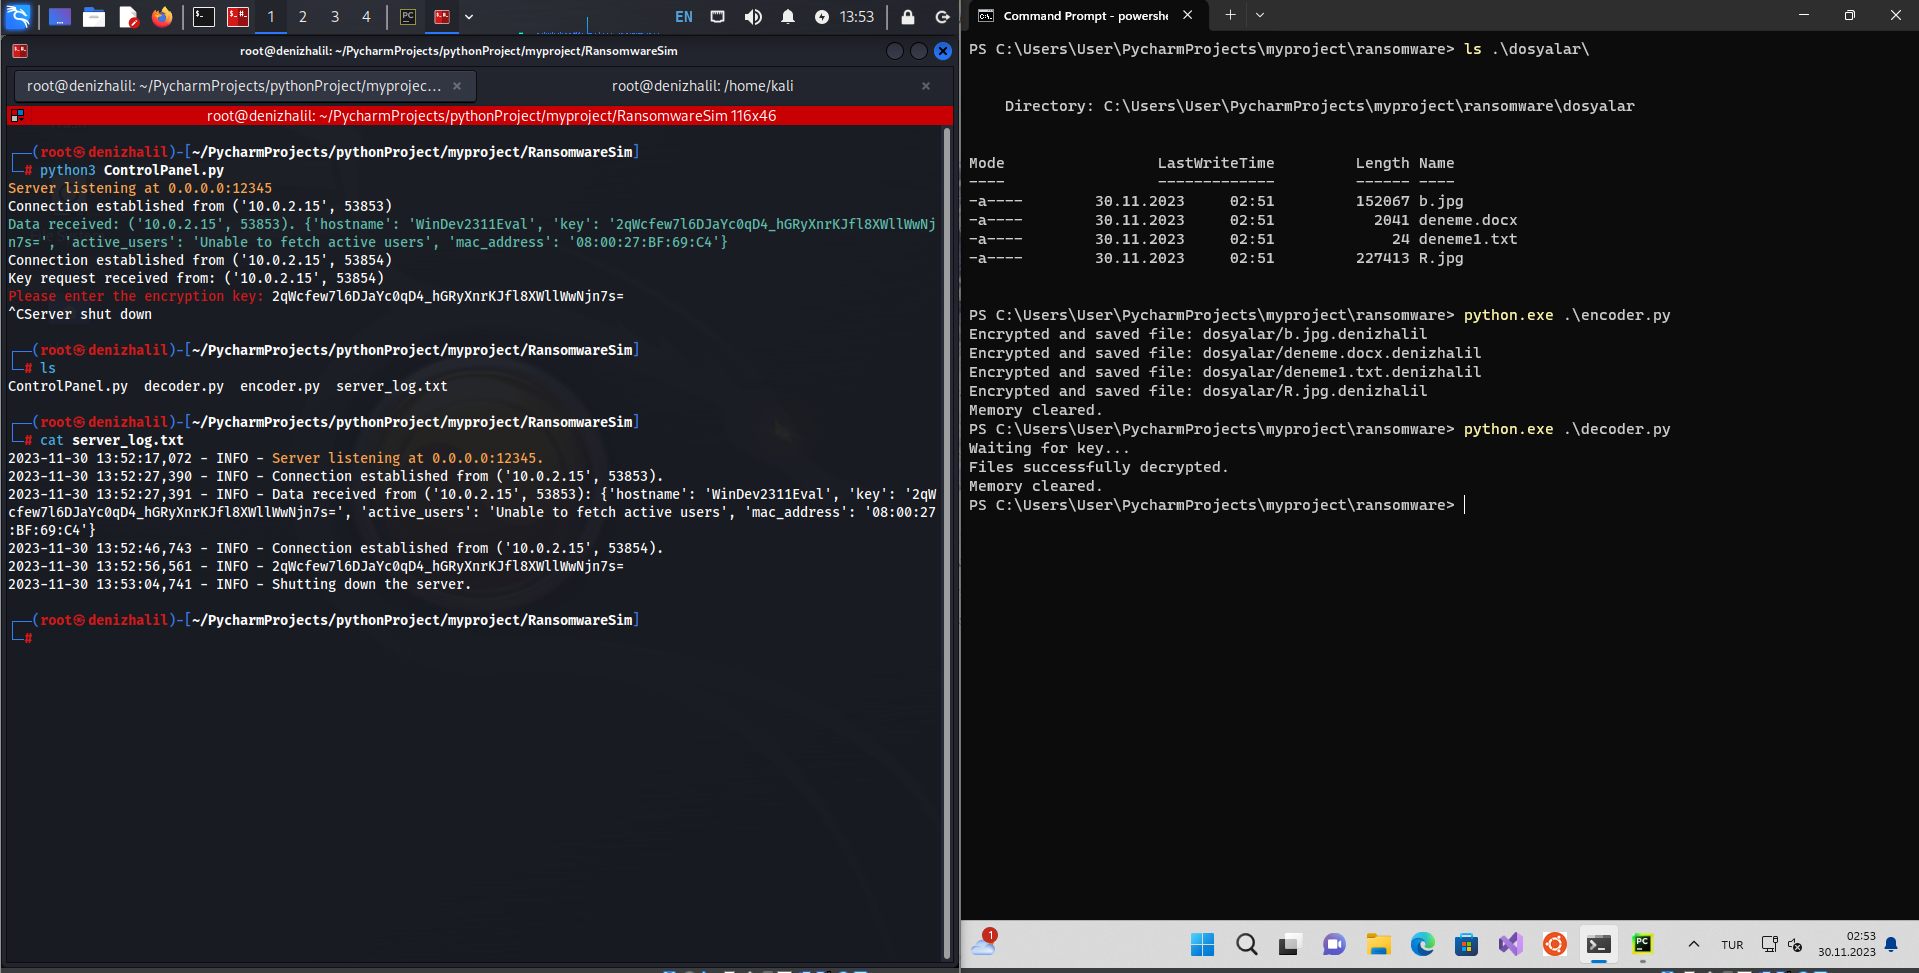 halildeniz/ransomwaresim
Educational ransomware simulator demonstrating file encryption, C2 communication, and decryption for cybersecurity training and malware analysis.
