
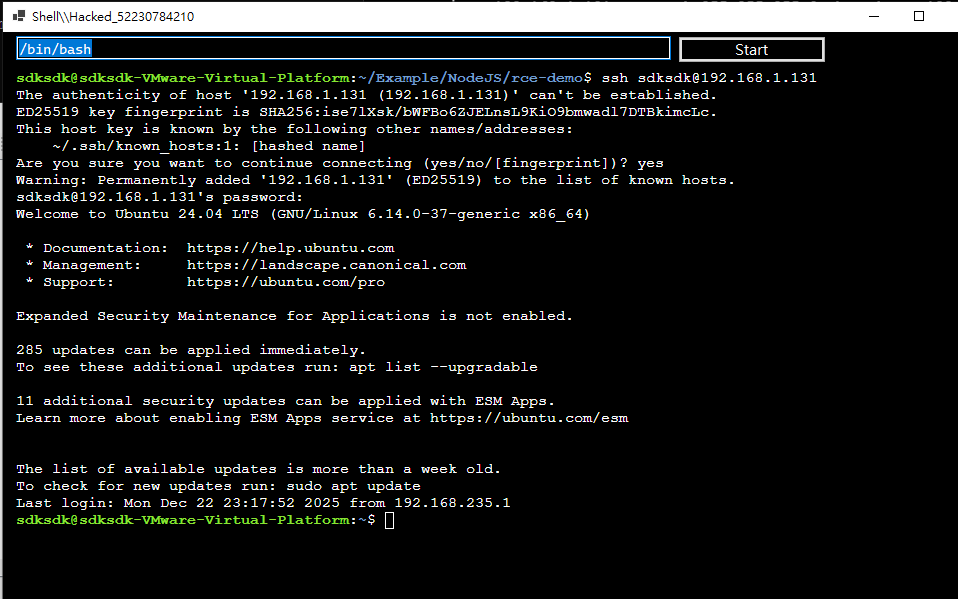
Eden-RAT
 iss4cf0ng/eden-rat
An open-source Linux GUI-based Remote Access Tool developed in C# with a Python payload, intended for legitimate penetration testing and…
command-and-controlencryption-decryption-toolsexploitation+5
33
iss4cf0ng/eden-ratAn open-source Linux GUI-based Remote Access Tool developed in C# with a Python payload, intended for legitimate penetration testing and…
 kiminewt/pyshark
Python wrapper for tshark, allowing python packet parsing using wireshark dissectors
 infobyte/cve-2023-21036
Detection and sanitization for Acropalypse Now - CVE-2023-21036
 farghlymal/config-extractors
Extracts and decrypts malware configuration data from captured samples, automating C2 endpoint discovery, credential extraction, and indicator triage…
 mhelwig/adwind-decryptor
Simple decrypter for Java AdWind, jRAT, jBifrost trojan
 elevenpaths/iphonerestrictionspasscodebf
Extracts and decrypts the 4-digit restriction passcode from iPhone backups on Windows machines, enabling recovery of device access controls.
 skelsec/pypykatz
Mimikatz implementation in pure Python
 syvaidya/openstego
OpenStego is a steganography application that provides two functionalities: a) Data Hiding: It can hide any data within an image file. b)…
 ddz/whatsapp-media-decrypt
Decrypt WhatsApp encrypted media files (images, videos, audio, documents) using media keys extracted from iOS ChatStorage.sqlite or Android…
 zblurx/dploot
Loot and decrypt Windows DPAPI secrets remotely or offline, including masterkeys, credentials, vaults, certificates, browser data, and cached Azure…
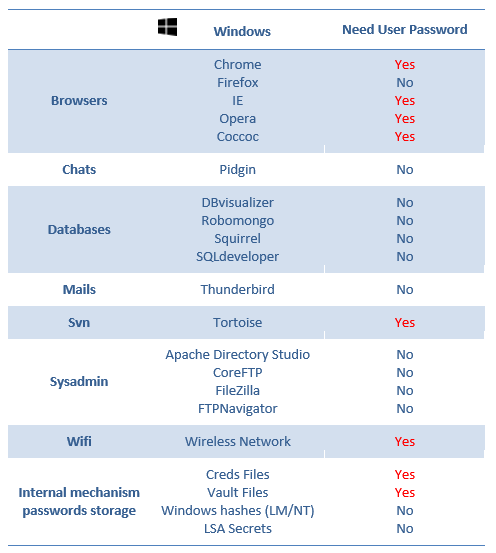 alessandroz/lazagneforensic
Windows passwords decryption from dump files
 threatlabz/tools
Tools developed by the Zscaler ThreatLabz Threat Intelligence team
 patrickdw123/paranoidf
ParanoiDF - PDF Analysis Suite based on PeePDF by Jose Miguel Esparza (http://peepdf.eternal-todo.com/). Tools added: Password cracking, redaction…
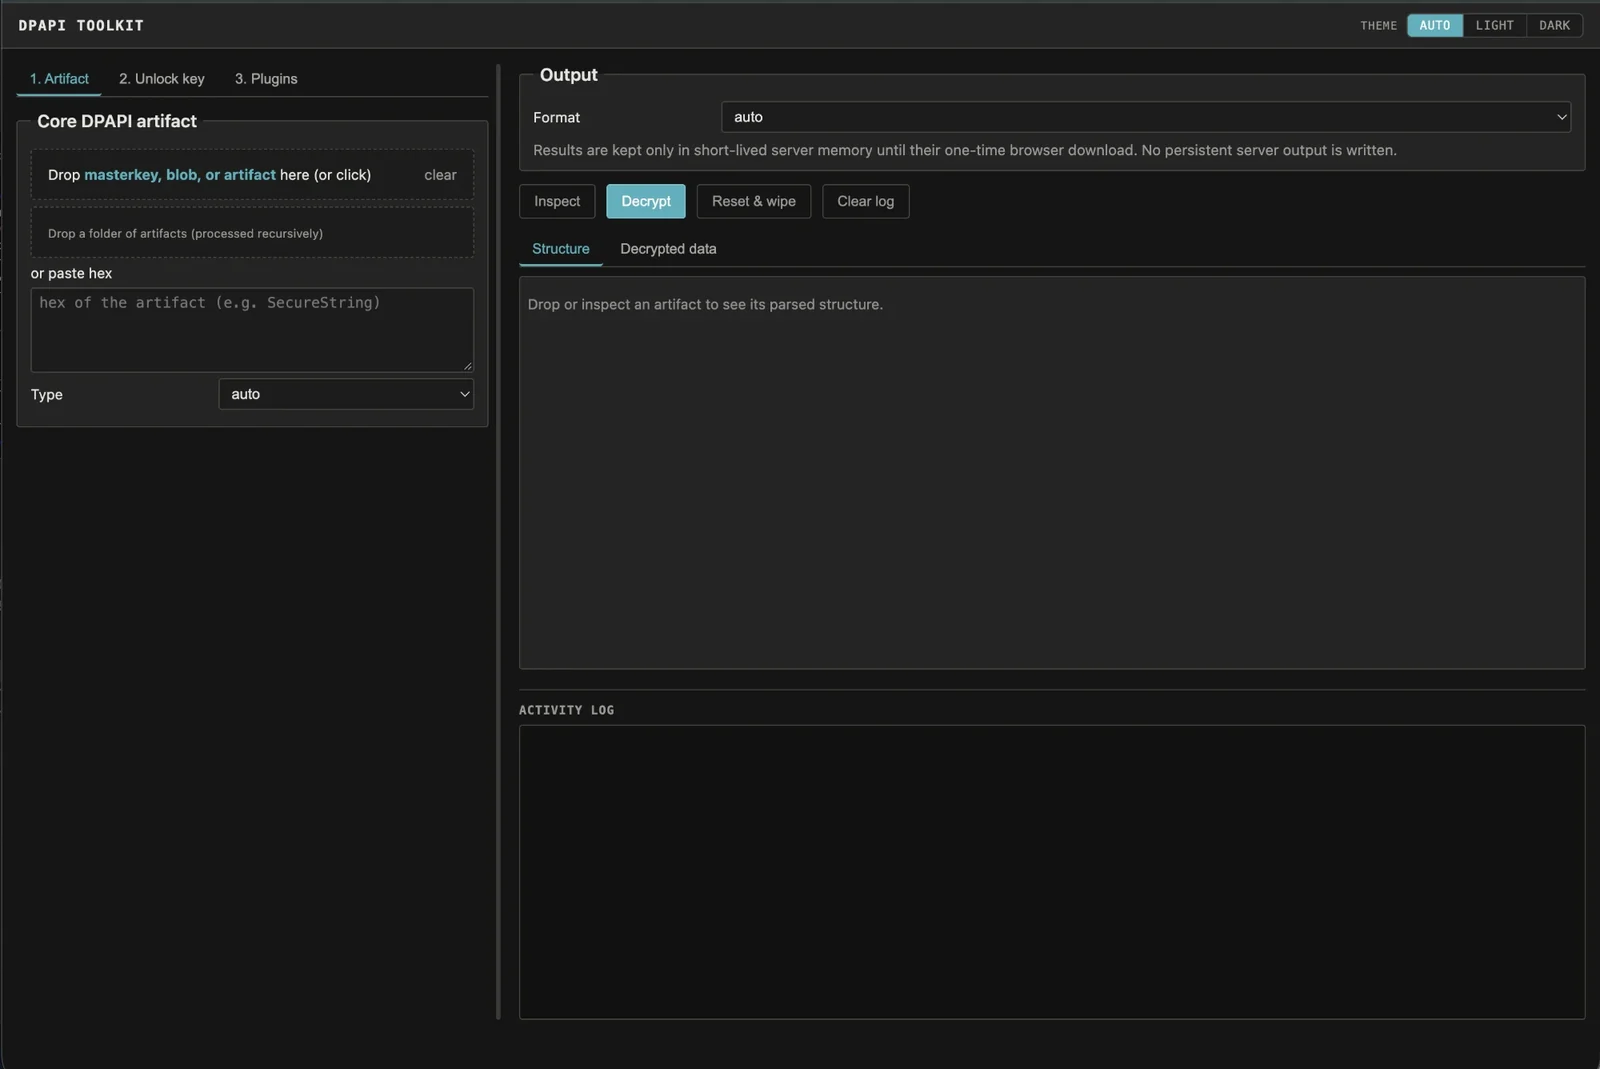 crypt0p3g/dpapi-toolkit
Drop any Windows DPAPI artifact and it identifies the format and the exact master key it needs, then decrypts once you supply the key. Offline, CLI +…
 almandin/ntdsdotsqlite
A small utility to translate NTDS.dit files to SQLite format.
 kcreyts/plugxdecoder
Decodes PlugX traffic and encrypted/compressed artifacts
 neccie/yellowkey-bitlocker-cve-2026-45585
Manage BitLocker recovery keys, unlock encrypted drives, and monitor encryption status with this lightweight Windows utility.
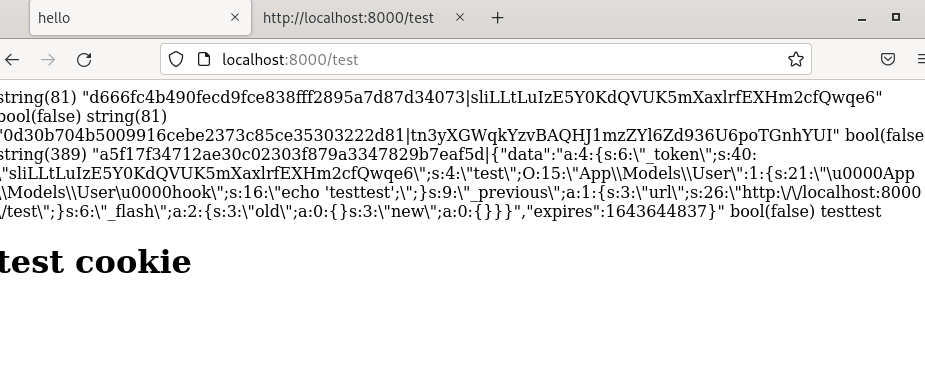 synacktiv/laravel_cookie_killer
Decrypt and re-encrypt Laravel session cookies to exploit insecure PHP deserialization for remote code execution.