


 gojue/ecapture
Capture SSL/TLS plaintext with eBPF—no MITM proxy or custom CA installation. Supports Linux and Android on x86_64 and arm64.
 alonemonkey/frida-ios-dump
Extracts decrypted IPA files from jailbroken iOS devices using Frida for reverse engineering, security analysis, and mobile app pentesting.
 lief-project/lief
Cross-platform library to parse, modify, and abstract ELF, PE, and MachO executable formats. Supports C++, Python, and Rust APIs with disassembler,…
 permissionlesstech/bitchat-android
Decentralized, encrypted peer-to-peer messaging app over Bluetooth mesh networks. No internet, servers, or phone numbers required. Features X25519 +…
 dnspyex/dnspy
Unofficial revival of the well known .NET debugger and assembly editor, dnSpy
 piotr-kniaz/eslockdecryptor
Tool for recovering and decrypting ES File Explorer encrypted files (.eslock)
 barghest-ngo/mesh
Encrypted peer-to-peer mesh VPN for remote mobile forensics, enabling wireless ADB and libimobiledevice acquisition, network monitoring, and…
 eldavoo/wa-crypt-tools
Manage WhatsApp .crypt12, .crypt14 and .crypt15 files.
 emanuele-f/pcapdroid
No-root network monitor, firewall and PCAP dumper for Android
 e-gleba/world_conqueror_4_ru
Translated strings for World Conqueror 4 (RU)
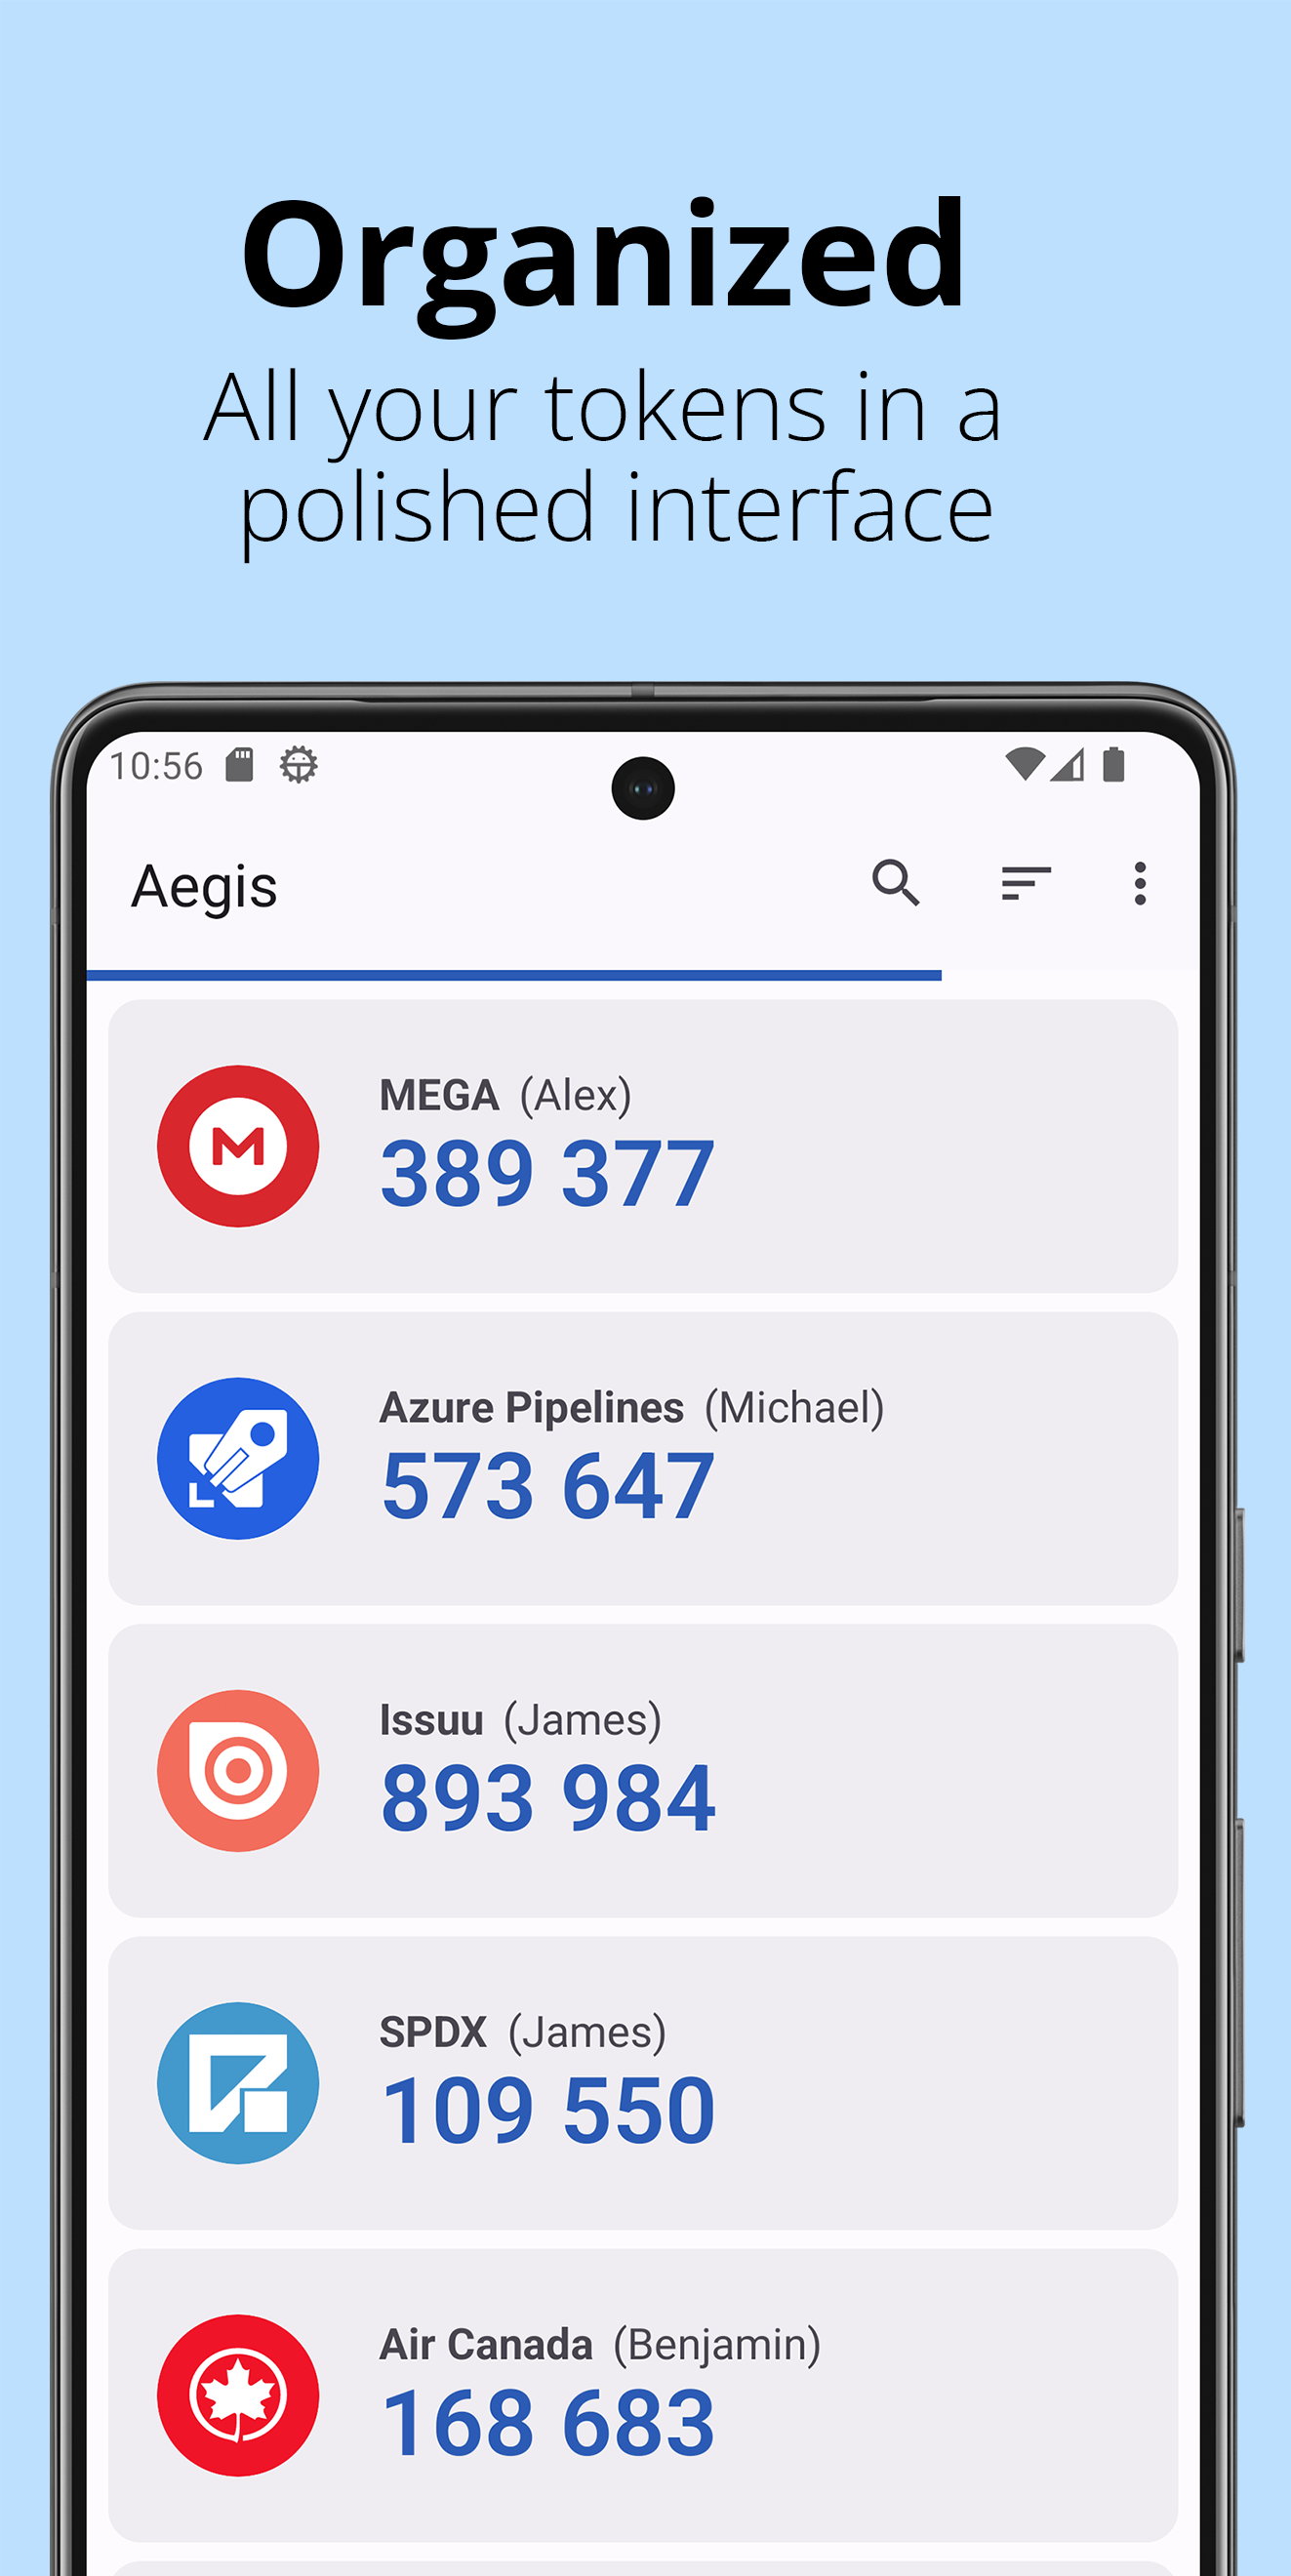 beemdevelopment/aegis
A free, secure and open source app for Android to manage your 2-step verification tokens.
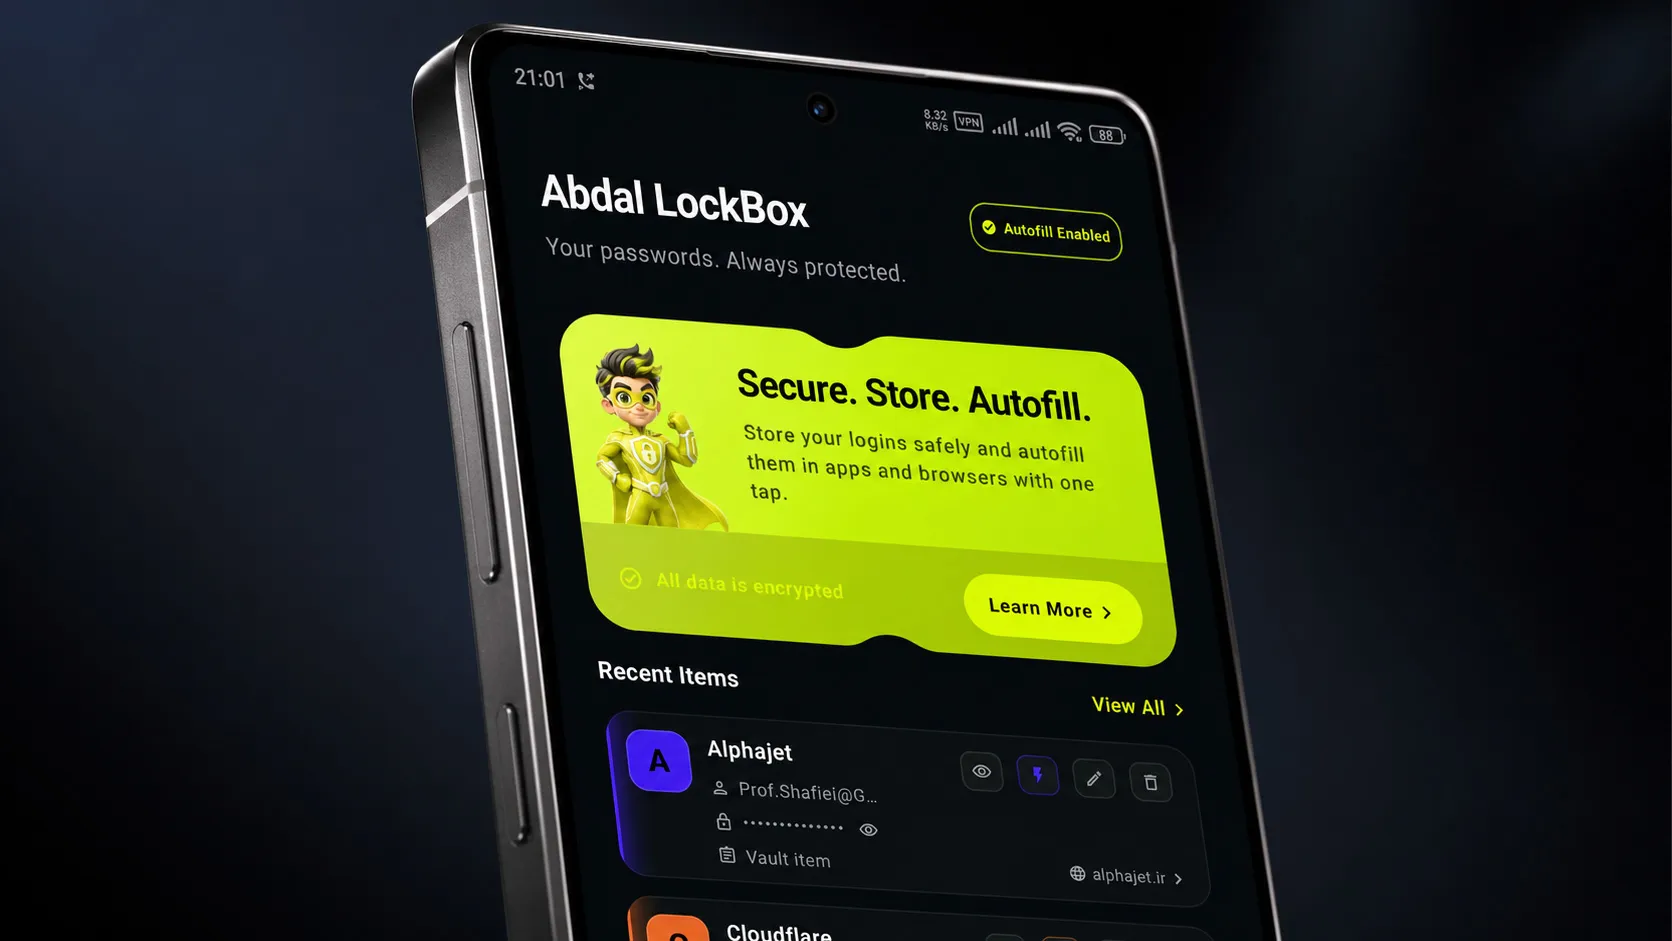
 prof.shafiei/abdal-lockbox
Local-first encrypted password vault for Android with Master Password access, Recovery Key support, Autofill integration, and portable encrypted…
 caveeroo/gv_decryptor
Gallery Vault dump recovery tool with automated discovery, key derivation and automatic media restoration.
 b16f00t/whapa
Graphical forensic toolkit for parsing, decrypting, and extracting WhatsApp data from Android and iOS devices, including Google Drive and iCloud…
 jb-selfcompany/tyr
True P2P Email on top of Yggdrasil Network for Android
 kvesel/zipbrk
Zip file format fuzzer and multi-tool.
 jas502n/2024informationsecurityengineer
2024年信息安全工程师、2024InformationSecurityEngineer