
CSharpScripts
C# offensive scripts for reflective PE and shellcode injection, in-memory payload execution, XOR brute-force shellcode decryption, and .NET assembly…

C# offensive scripts for reflective PE and shellcode injection, in-memory payload execution, XOR brute-force shellcode decryption, and .NET assembly…

Linux C2 beacon with native in-memory ELF BOF loader, AES-256-CFB encrypted polling, and a Python C2 server for fileless post-exploitation modules.

Reduce Entropy And Obfuscate Youre Payload With Serialized Linked Lists

Reverse engineering write-up of Python shellcode that APC-injects into AnyDesk, exfiltrates to a C2 over HTTPS with AES/RSA, and persists via…

The next level 100% Python obfuscator.

A listener profile for the Mythic C2 framework that utilizes AI vendors file API's

Configurable, Community driven, HTTP C2 Profile

A fileless reverse shell and C2 framework leveraging direct syscalls, proxy tunneling, and ChaCha20 encryption for AV evasion.

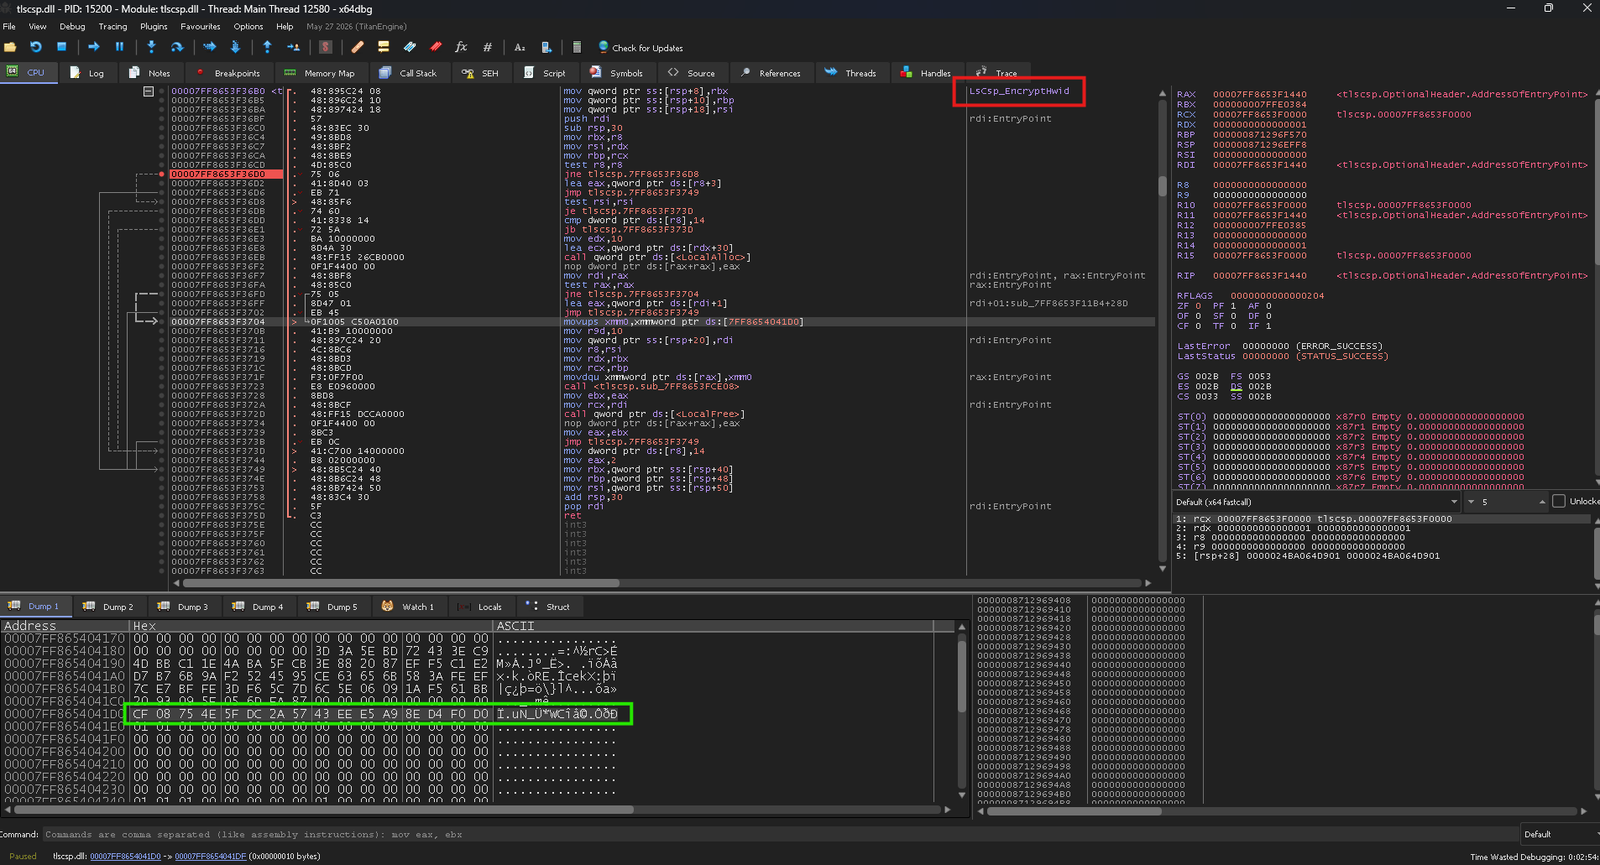
Abuses the Microsoft-signed tlscsp.dll LOLBin to run RC4 encrypt/decrypt via LsCsp_EncryptHwid, patching the hardcoded key in memory for BYOK…

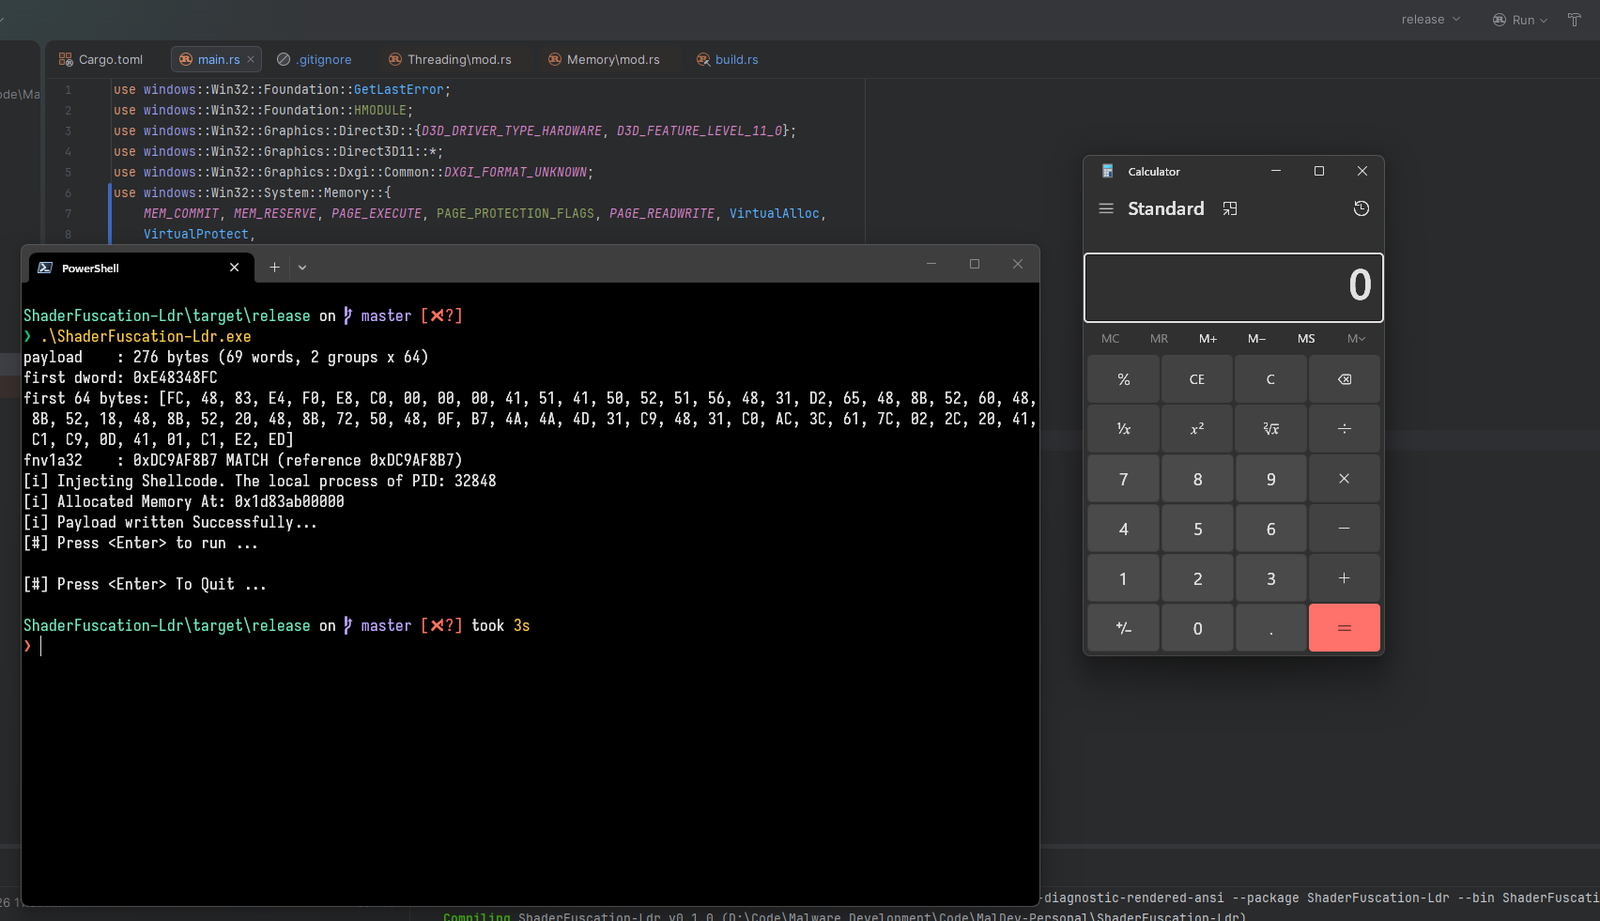
A PoC on how to use a Compute Shader as Payload

SOCKS5 proxy tunneled through Cloudflare R2 object storage, with Python and dependency-free C++ agents relaying TCP traffic via encrypted R2 objects…

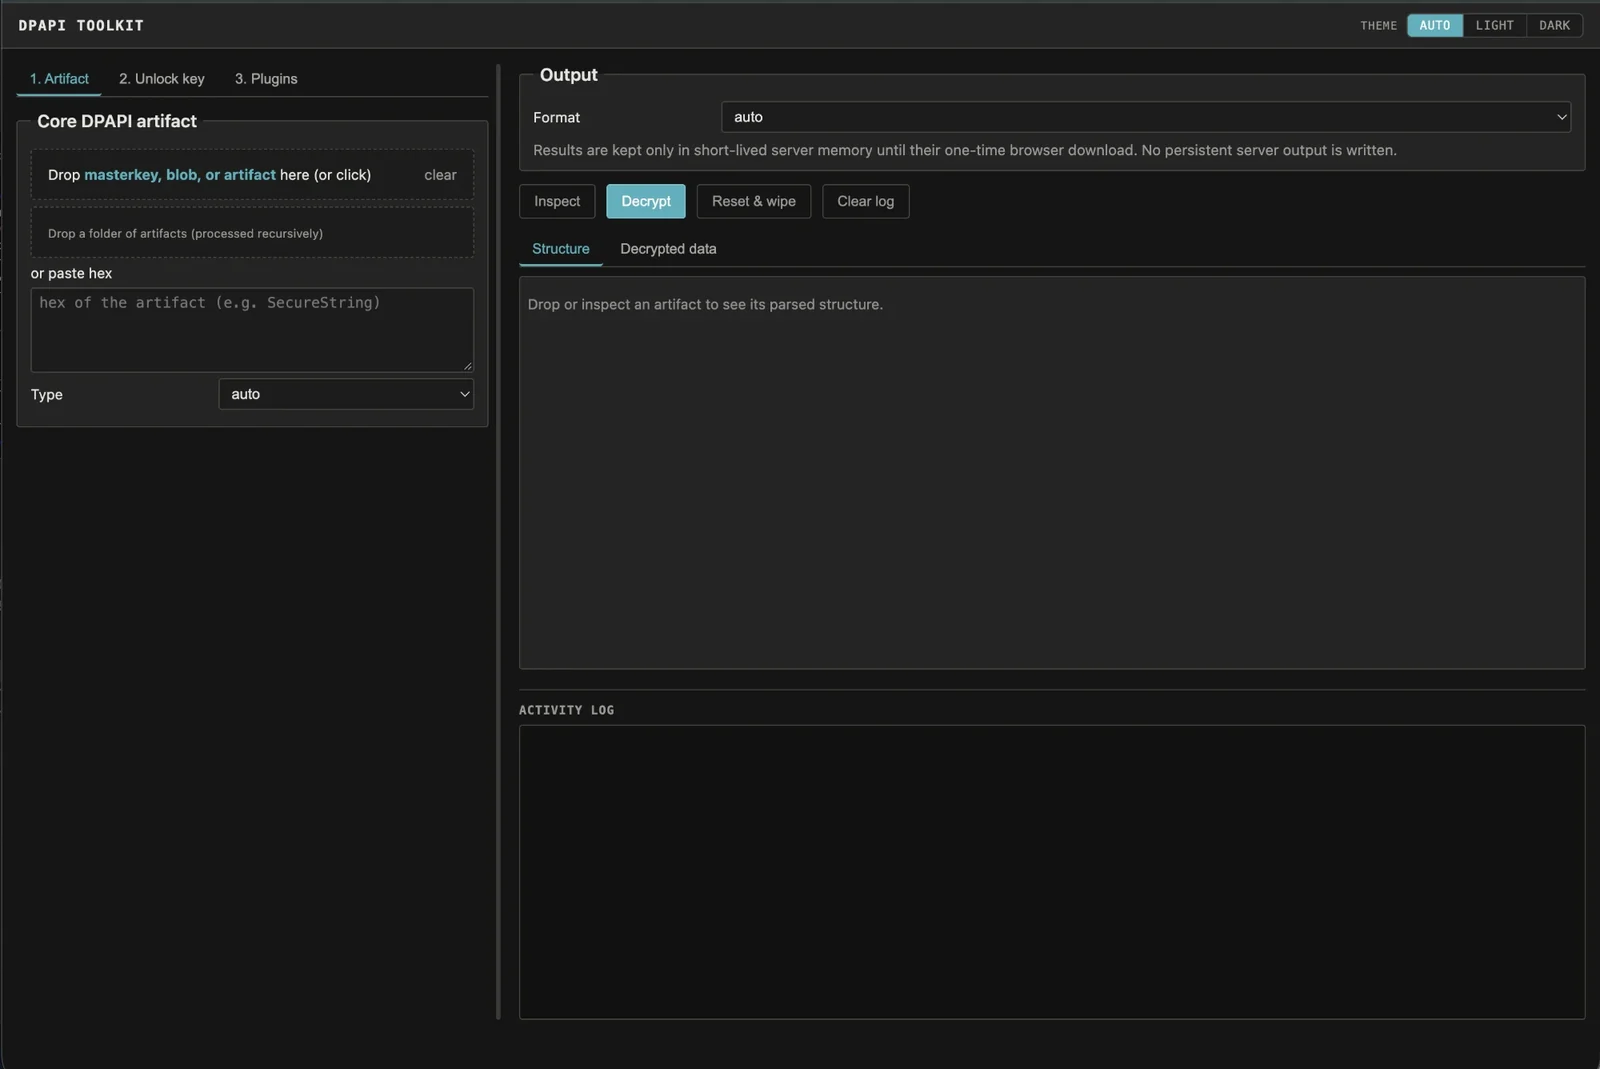
Drop any Windows DPAPI artifact and it identifies the format and the exact master key it needs, then decrypts once you supply the key. Offline, CLI +…

Mythic C2 profile that tunnels Athena and Apollo agent traffic through Telegram bot-to-bot messages, bridging encrypted payloads to Mythic via its…

Mythic C2 profile that tunnels agent traffic through Microsoft Teams channels using the Microsoft Graph API, with AES256 encryption, jitter, kill…

Python-based Discord RAT with remote command panel for webcam capture, audio recording, keylogging, file exfiltration, and persistence via Discord…

Cross-platform syscall-powered implant & C2 — direct syscalls (Win), raw syscalls (Linux), HTTPS/DNS/ICMP channels. No winapi layer.

Cloud dead-drop C2 framework — RSA-4096 + AES-256-GCM, 5 cloud providers, Rust-only agents, P2P mesh, persistence engine, credential harvesting

Proof-of-concept demonstrating bypass of TPM-bound LUKS disk encryption on Linux systems, extracting volume keys via custom root filesystem attack.