Lockbit-Black-3.0
Ransomware source code artifact for analyzing encryption routines, payload mechanics, and building detection and incident-response countermeasures.

Ransomware source code artifact for analyzing encryption routines, payload mechanics, and building detection and incident-response countermeasures.

Tools developed by the Zscaler ThreatLabz Threat Intelligence team

A PoC ransomware sample to test out your ransomware response strategy.

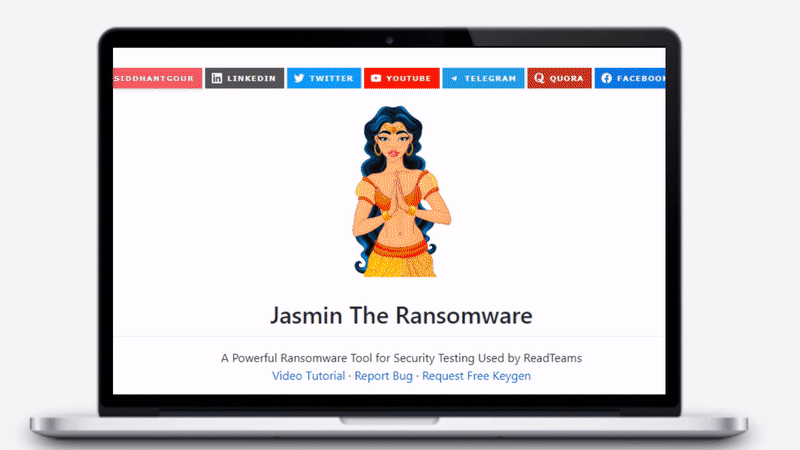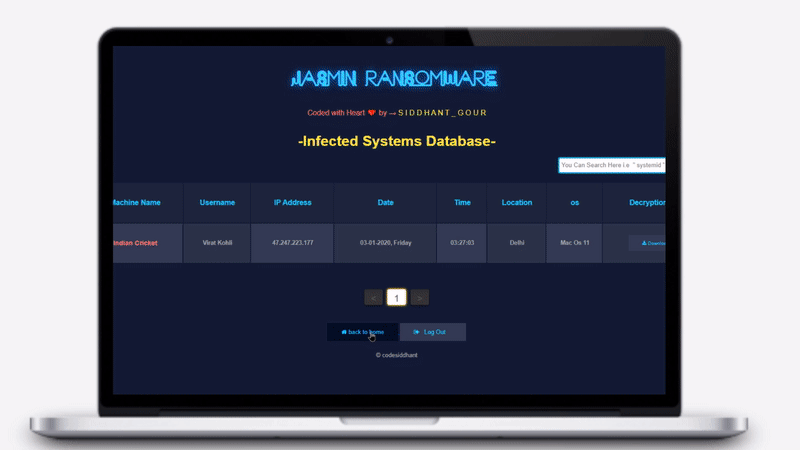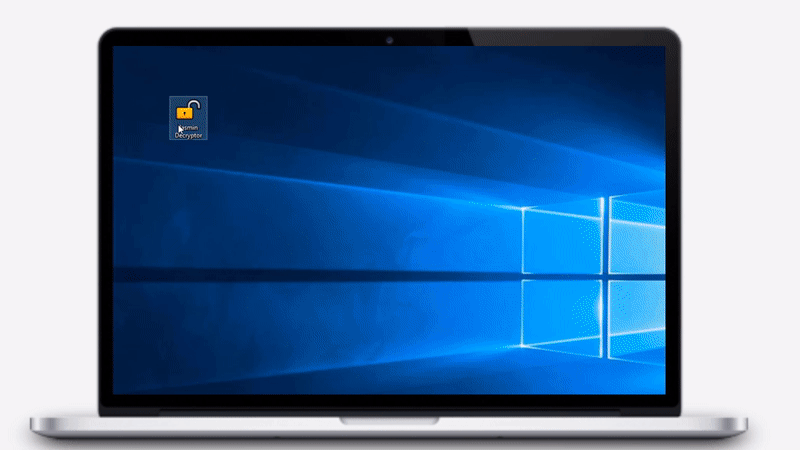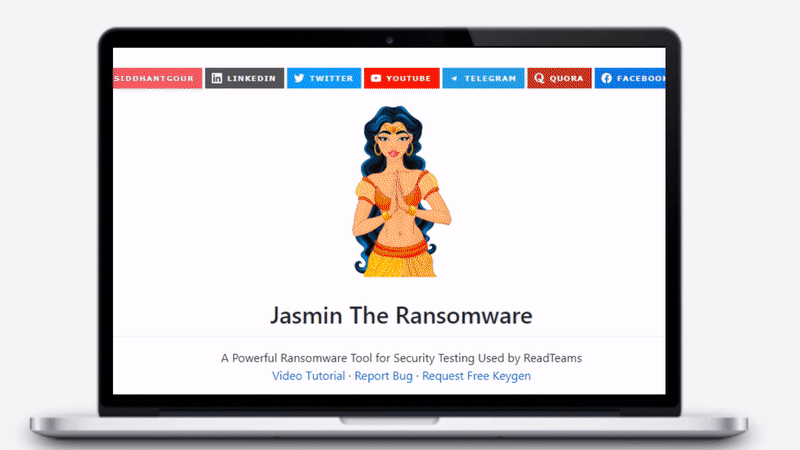
Jasmin Ransomware is an advanced red team tool (WannaCry Clone) used for simulating real ransomware attacks. Jasmin helps security researchers to…

A LKM rootkit targeting 4.x and 5.x kernel versions which opens a backdoor that can spawn a reverse shell to a remote host, launch malware and more.

Android Ransomware Development - AES256 encryption + CVE-2019-2215 (reverse root shell) + Data Exfiltration

A Proof-of-Concept bootkit and UEFI boot application inspired by Petya ransomware, written in Assembly, C, and C++

Advanced ransomware using process injection and kernel driver loading via CVE-2019-16098 to encrypt files, disable recovery, and demand ransom. For…

Fully undetectable and evasive ransomware written in Rust, leveraging a BYOVD technique to disable AV/EDR solutions on the infected systems.

A next generation of ransomware. Fully written using a .Net Framework + C&C System

CryptoLocker is open source files encrypt-er. Crypto is developed in Visual C++. It has features encrypt all file, lock down the system and send keys…

A proof of concept crypto virus to spread user awareness about attacks and implications of ransomwares. Phirautee is written purely using PowerShell…

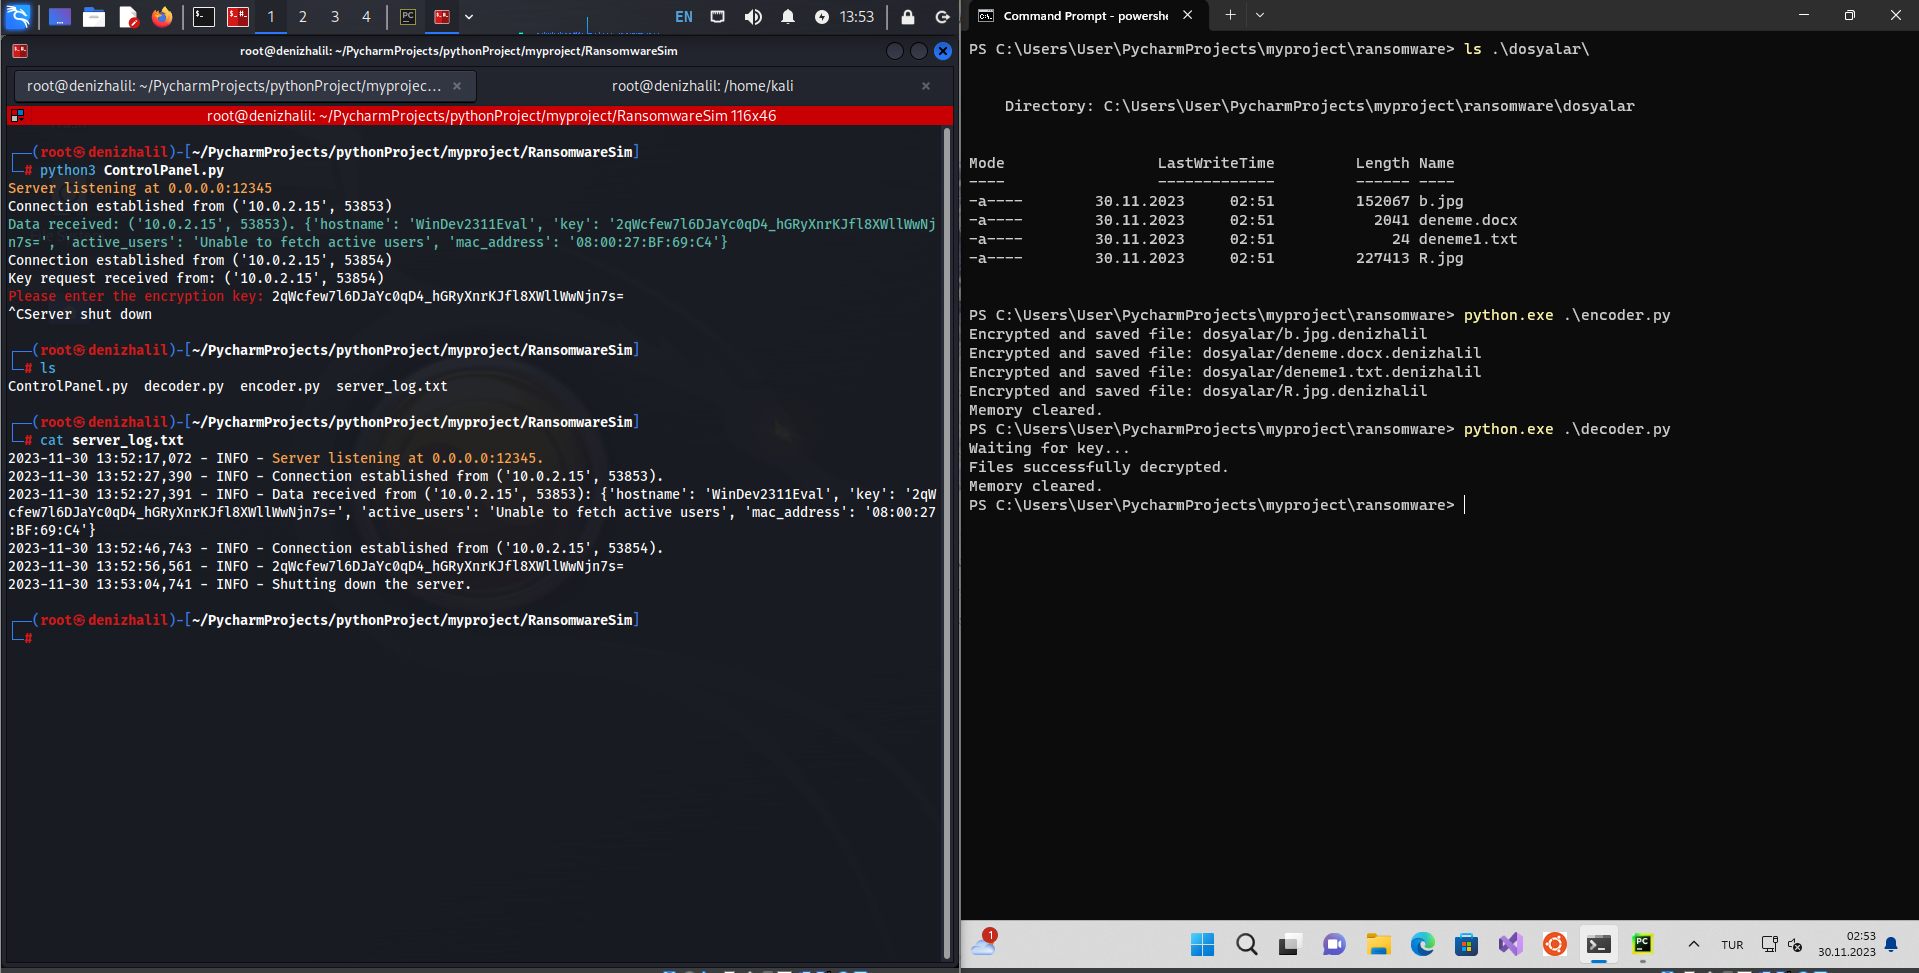
Educational ransomware simulator demonstrating file encryption, C2 communication, and decryption for cybersecurity training and malware analysis.

A utility for playing with cryptography, geared towards ransomware analysis.

PowerShell Ransomware Simulator with C2 Server

Android Ransomware Development - AES256 encryption + CVE-2019-2215 (reverse root shell) + Data Exfiltration