
 openwrt/openwrt
Linux operating system for embedded devices with writable filesystem, package management, and build framework. Enables custom firmware creation for…
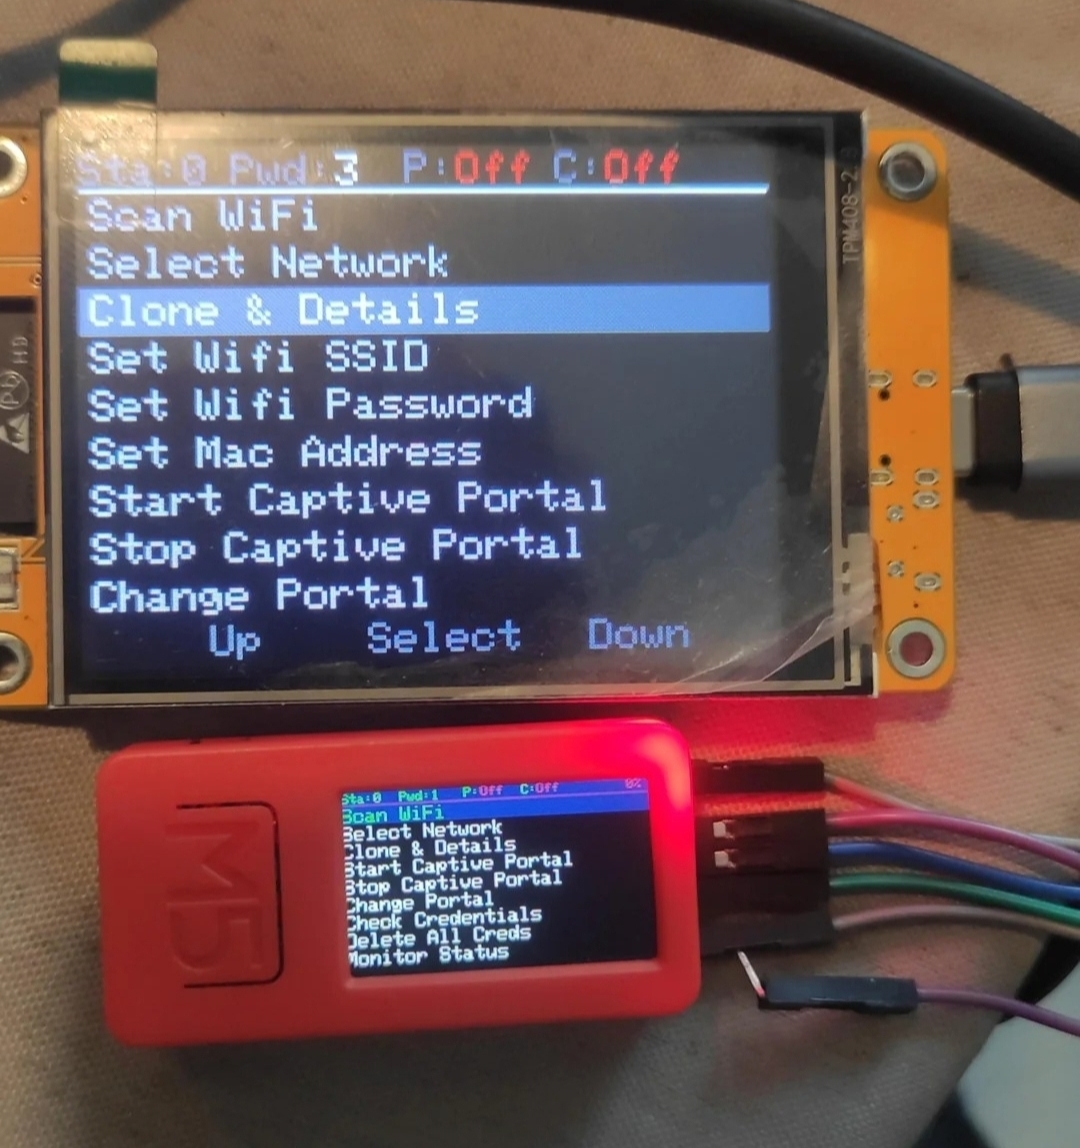 7h30th3r0n3/evil-m5project
Multi-purpose WiFi penetration testing toolkit for M5Stack devices. Performs network scanning, evil-twin attacks, deauthentication, captive portal…
 eik00d/cantoolz
CANToolz - framework for black-box CAN network analysis
 forescout/project-memoria-detector
Active fingerprinting tool that identifies 16 embedded TCP/IP stacks on network devices using ICMP, TCP, HTTP, SSH, and FTP probing techniques for…
 synwall/synwall
Linux kernel module implementing a zero-configuration, OTP-based firewall for IoT devices. Transparently authenticates network traffic using a…
 cantoolz/cantoolz
CANToolz - Black-box CAN network analysis framework
 eternityforest/lazymesh
Proof of concept IoT/Ham Radio mesh network with global routing over the internet
 khaleedbt/netis-cve-2026-36539
Python script that checks Netis routers for CVE-2026-36539, detecting vulnerable devices on a network.
 george0papasotiriou/cve-2026-21006-zigbee-light-link-factory-reset-exploit
Simulated Zigbee Light Link (ZLL) factory reset exploit for CVE-2026-21006, demonstrating unauthenticated TouchLink command injection that wipes…
 gigachadusers/cve-2026-20169
Windows-native IoT vulnerability scanner that discovers exposed management interfaces, tests default credentials, and validates network segmentation…
 0xqrx/cve-2024-6333
Authenticated Remote Code Execution vulnerability in Xerox WorkCentre printers via the Network Troubleshooting Log feature.
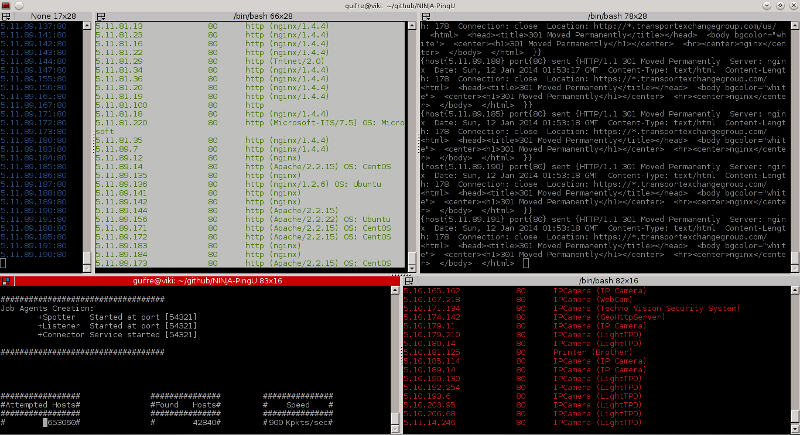 owasp/ninja-pingu
High-performance network scanner for large-scale IP and port scanning with service identification, embedded device detection, and vulnerability…
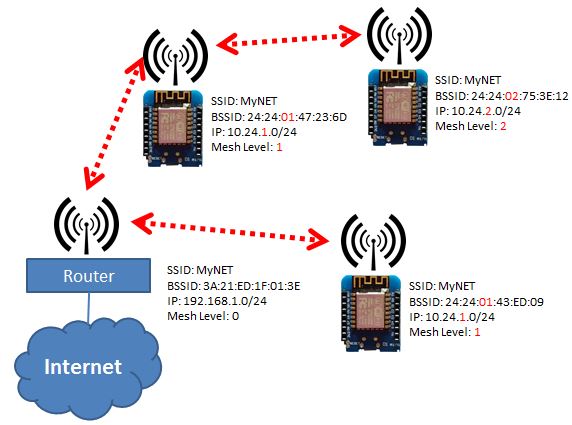 martin-ger/esp_wifi_repeater
A full functional WiFi NAT Router (and now also a WiFi Repeater)
 lyrebirds/sagemcom-fast-3890-exploit
Exploit for Sagemcom F@ST 3890 cable modem implementing Cable Haunt vulnerability to achieve remote code execution via WebSocket-based buffer…
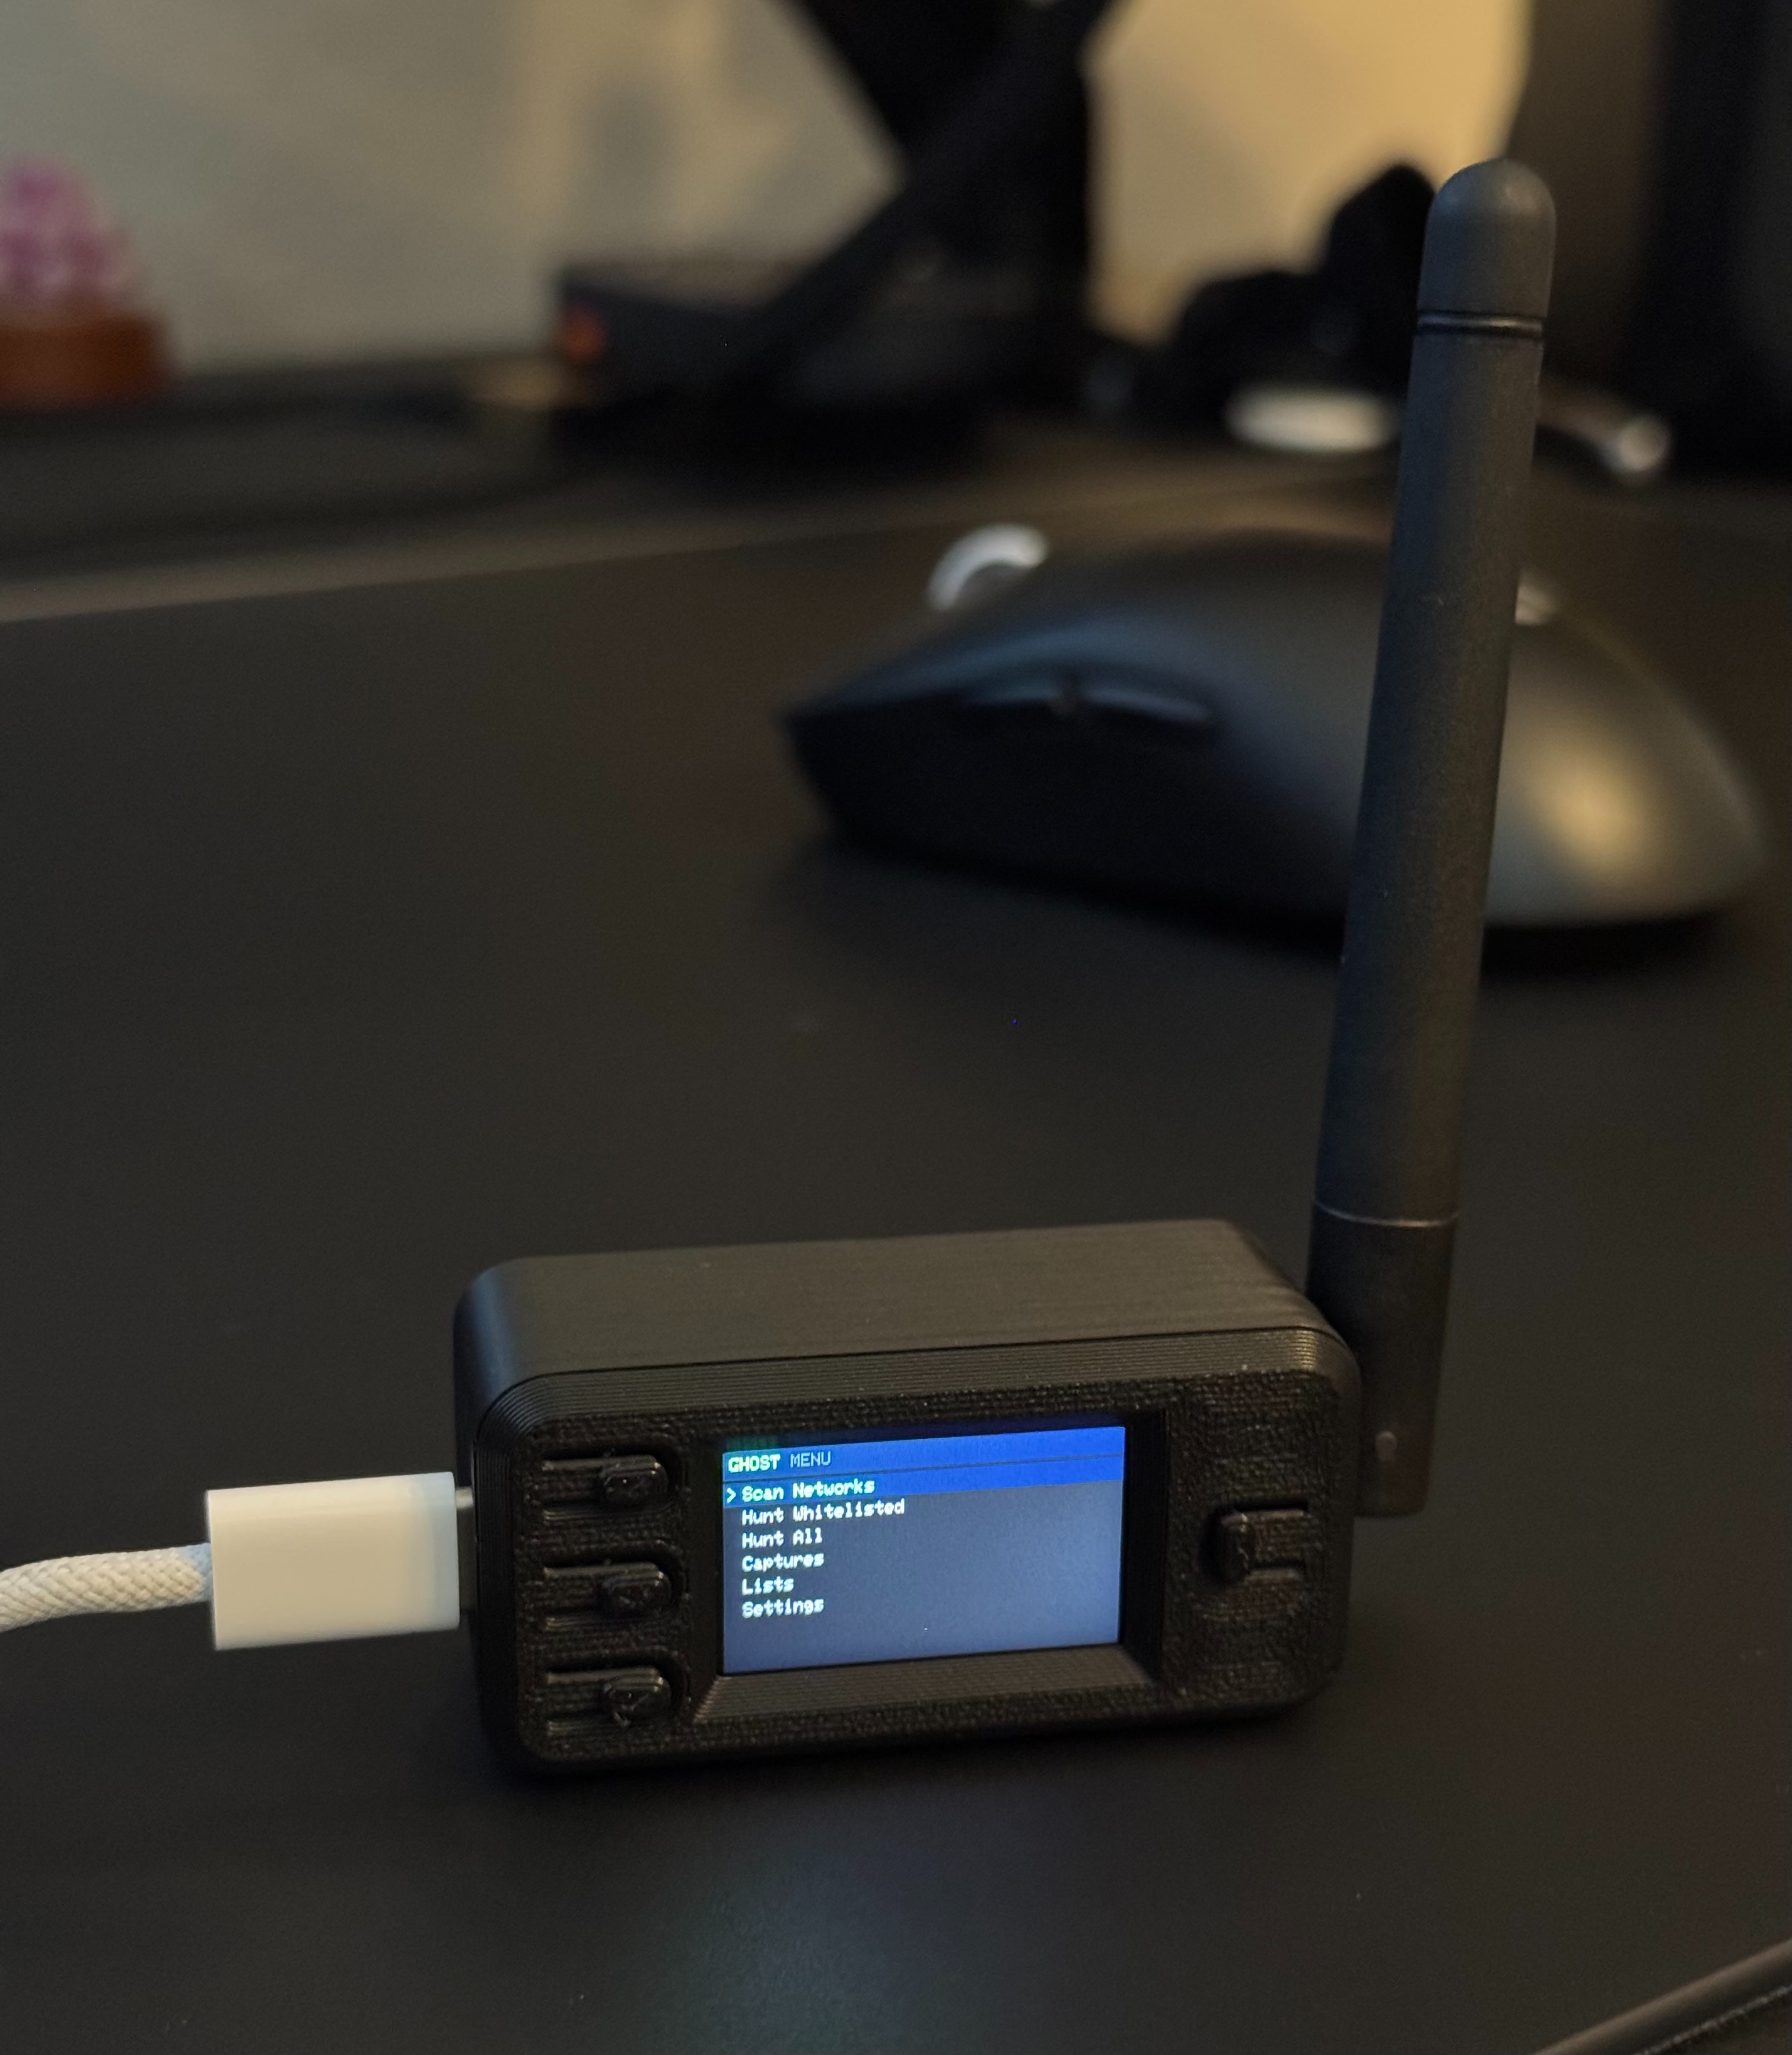 razkom/ghost
ESP32-S3 firmware for standalone WPA/WPA2 handshake capture and deauthentication testing via TFT UI, with pcap download over WiFi AP.
 dest-3/cve-2023-46012
LINKSYS AC1900 EA7500v3 IGD UPnP Stack Buffer Overflow Remote Code Execution Vulnerability
 george0papasotiriou/cve-2026-8888-printer-firmware-unsigned-update-via-http
Demonstrates CVE-2026-8888, an unsigned printer firmware update over HTTP, including a malicious update server and vulnerable printer emulator for…