

CVE-2020-14965
 g-rubert/cve-2020-14965
TP-LINK Multiple HTML Injection Vulnerabilities
embedded-systems-securityhardware-securityiot-security+3
g-rubert/cve-2020-14965TP-LINK Multiple HTML Injection Vulnerabilities
 laskdjlaskdj12/cve-2024-35106-poc
Proof-of-concept exploit for CVE-2024-35106, a stack buffer overflow in NEXTU FLETA AX1500 Wi-Fi 6 router. Demonstrates denial-of-service and…
 hunt-benito/mediatek-wlan-heap-overflow-cve-2026-20452-filogic-router-rce
Proof-of-concept exploit for CVE-2026-20452, a heap-based buffer overflow in MediaTek WLAN AP drivers. Uses scapy to send crafted Wi-Fi management…
 george0papasotiriou/cve-2026-6789-stack-buffer-overflow-in-embedded-tls-certificate-parser
Stack buffer overflow PoC in an embedded TLS certificate parser using a crafted X.509 SAN extension for remote code execution on IoT and industrial…
 enovella/tee-reversing
A curated list of public TEE resources for learning how to reverse-engineer and achieve trusted code execution on ARM devices
 lyravoid/kernelpatch
Patches and hooks the Linux kernel using only a stripped kernel image, extracting symbols and injecting code for inline and syscall hooking on arm64.
 pazhanivel07/system_bt_a10_r33_cve-2021-0474
Android Bluetooth stack (Fluoride) with a specific patch for CVE-2021-0474, providing source code for building and testing the Bluetooth component on…
 watchtowrlabs/watchtowr-vs-sonicwall-preauth-rce-chain
PoC exploit chain for pre-authentication remote code execution on SonicWall SMA 100 appliances exploiting CVE-2023-44221 and CVE-2024-38475.
 aperikube/pwn-arm-nfc
ARM buffer overflow challenge exploiting NFC tag input on Raspberry Pi. Includes hardware assembly guide, server code, and flag retrieval for CTF and…
 tnm/zclaw
Your personal AI assistant at all-in 888KiB (~35KB in app code). Running on an ESP32. GPIO, cron, custom tools, memory, and more.
 star-laboratory/prism
PrISM: A Scalable Probabilistic RowHammer Mitigation (ISCA 2026). Ramulator2 source code and evaluation scripts.
 george0papasotiriou/cve-2026-23005-matter-commissioning-code-brute-force-without-rate-limit
Simulates a Matter commissioning code brute-force attack (CVE-2026-23005) using Python to demonstrate missing rate limiting and lockout on 8-digit…
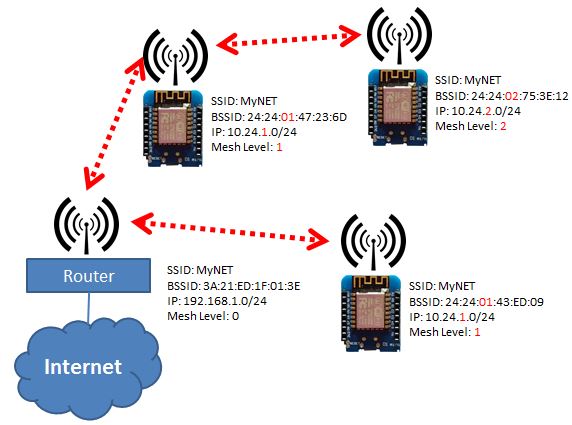 martin-ger/esp_wifi_repeater
A full functional WiFi NAT Router (and now also a WiFi Repeater)
 roostercoopllc/flipper-mcp
AI-powered MCP server for Flipper Zero. Control SubGHz, NFC, RFID, IR, BLE, GPIO, and more over WiFi using Claude or any MCP client.
 pazhanivel07/system_bt_a10-r33_cve-2021-0474
Android Fluoride Bluetooth stack source code with a focus on CVE-2021-0474, providing a foundation for vulnerability research and security analysis…
 symbrkrs/ps5-uart
Interface for interacting with PlayStation 5 EMC and EFC
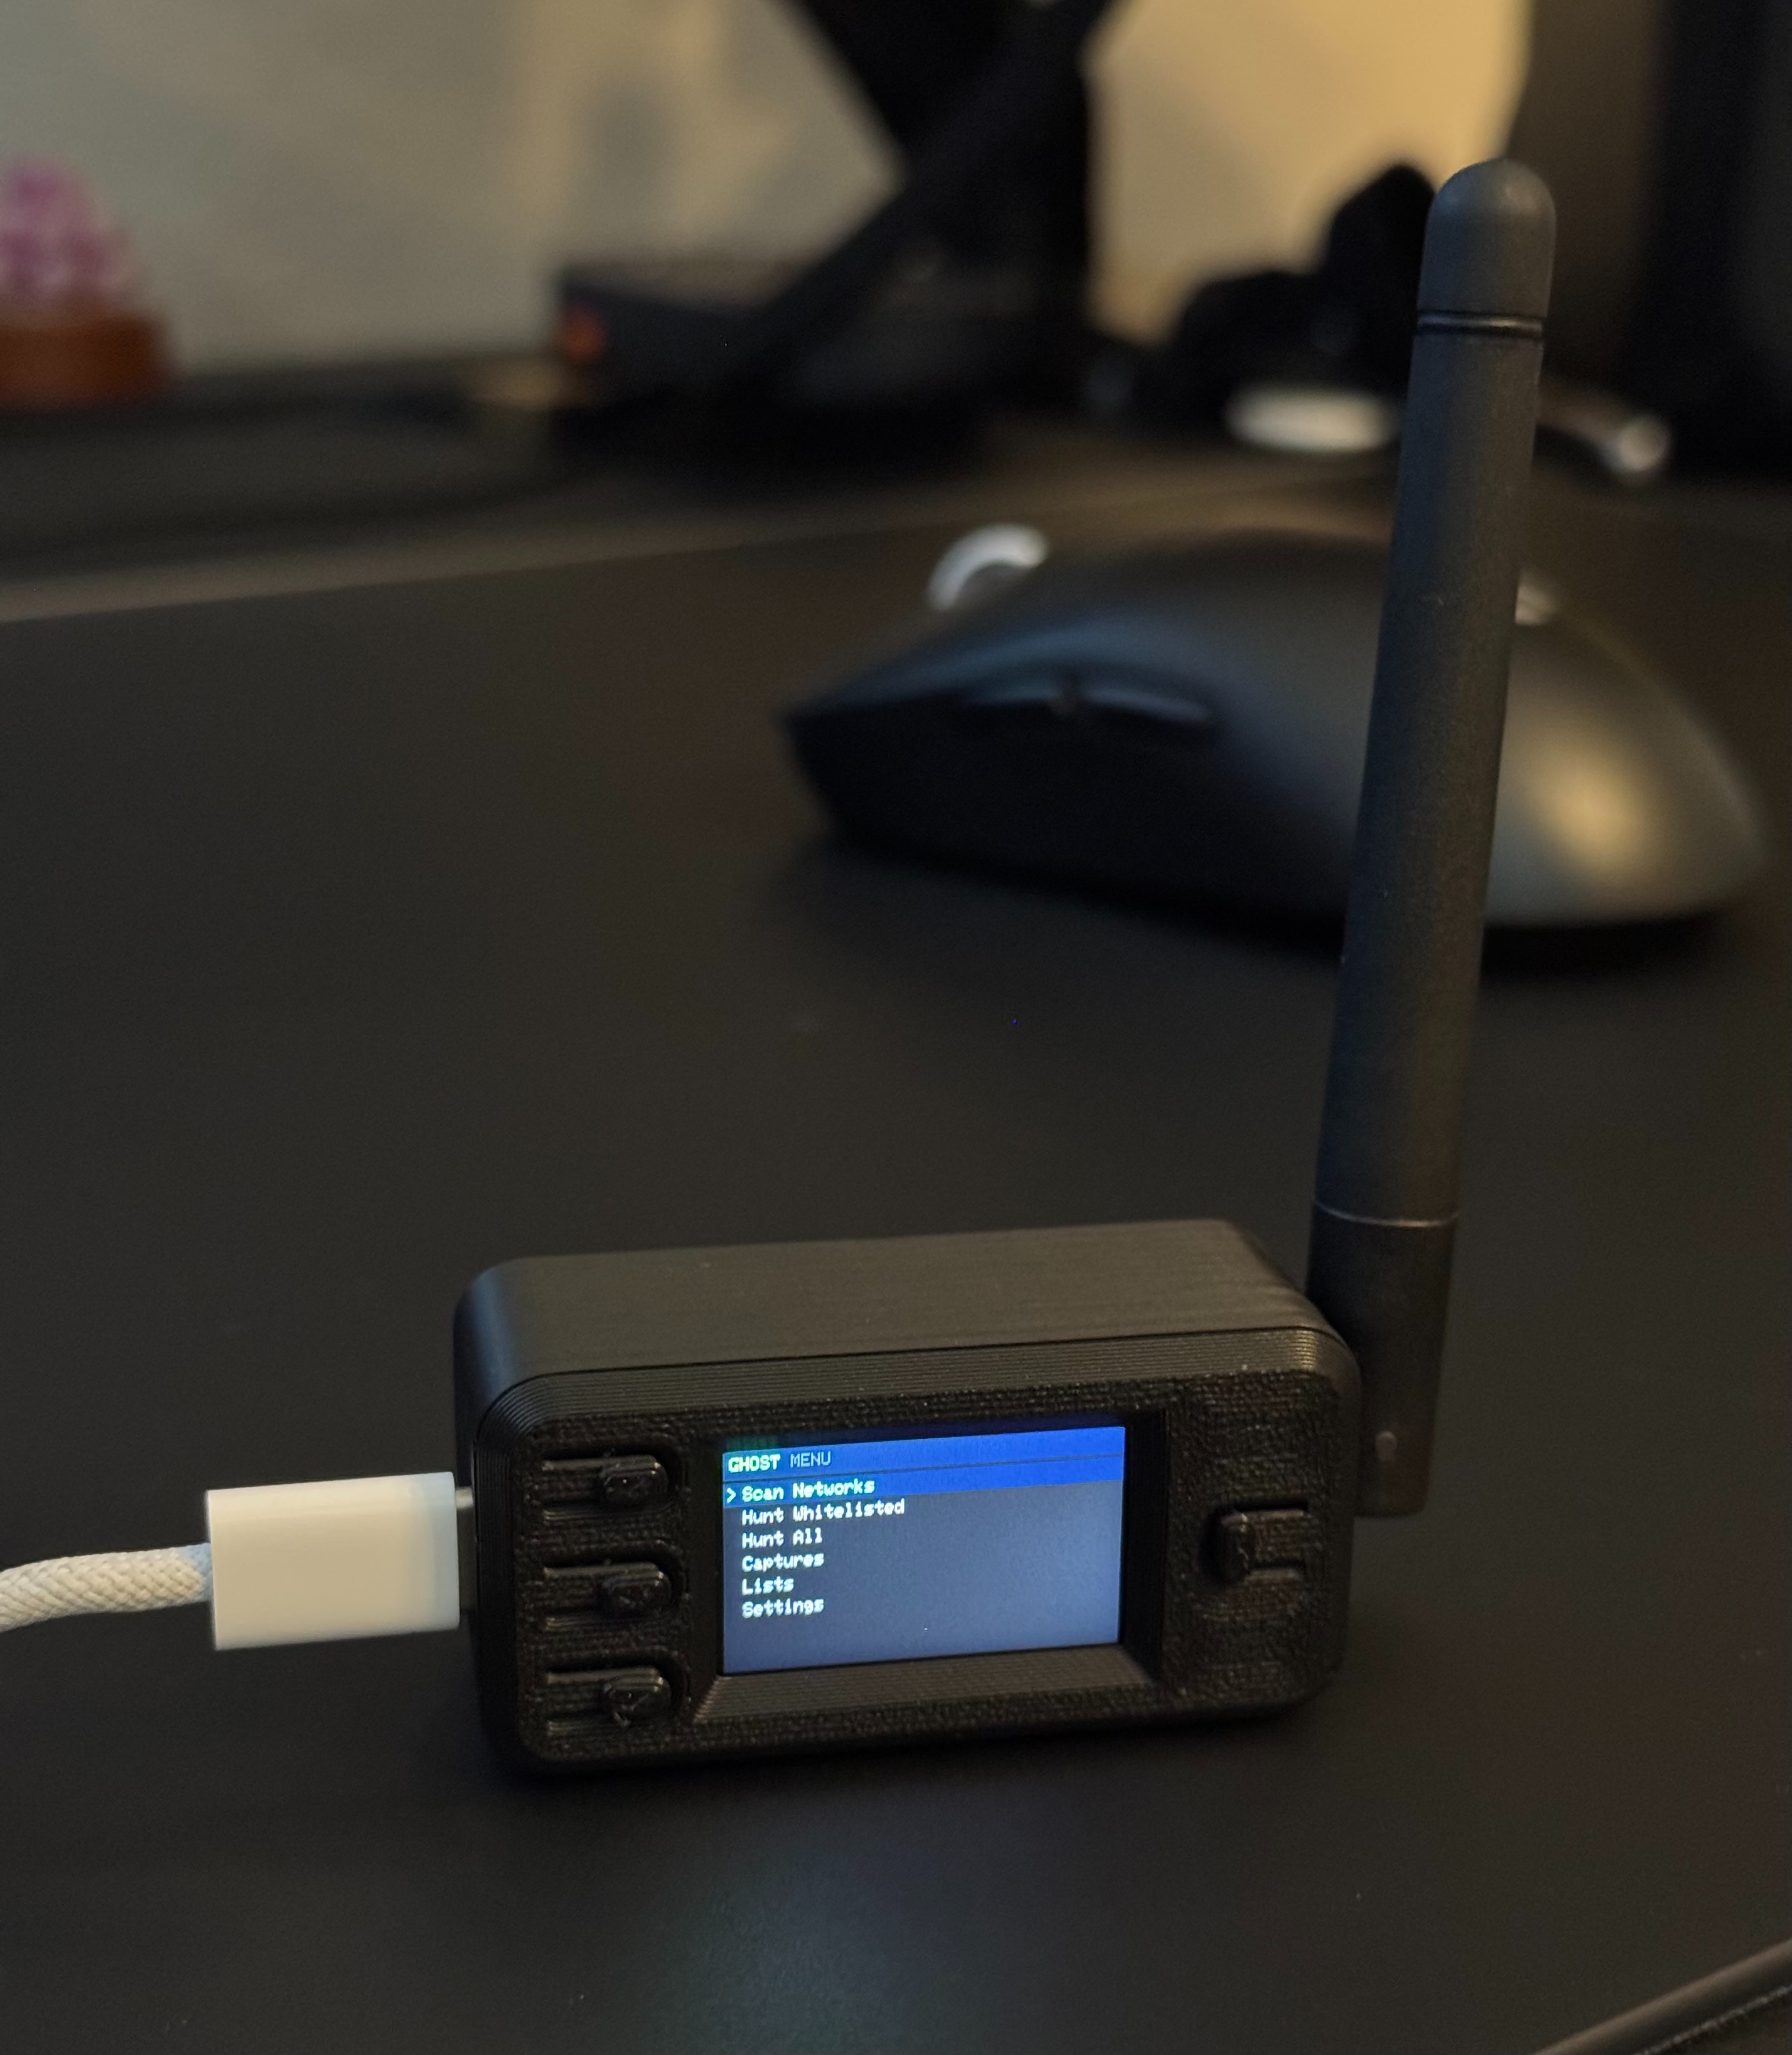 razkom/ghost
ESP32-S3 firmware for standalone WPA/WPA2 handshake capture and deauthentication testing via TFT UI, with pcap download over WiFi AP.
 lyrebirds/sagemcom-fast-3890-exploit
Exploit for Sagemcom F@ST 3890 cable modem implementing Cable Haunt vulnerability to achieve remote code execution via WebSocket-based buffer…