
d-os-descriptor
 szymonh/d-os-descriptor
CVE-2022-25258 - Demo exploit targeting usb gadget's os descriptor handler
binary-exploitationembedded-systems-securityexploitation+3
szymonh/d-os-descriptorCVE-2022-25258 - Demo exploit targeting usb gadget's os descriptor handler
 librepods-org/librepods
AirPods liberated from Apple's ecosystem.
 e-m-b-a/emba
EMBA - The firmware security analyzer
 marin-m/vmlinux-to-elf
A tool to recover a fully analyzable .ELF from a raw kernel, through extracting the kernel symbol table (kallsyms)
 nmatt0/moria
IoT firmware identification and extraction
 seemoo-lab/internalblue
Bluetooth experimentation framework for Broadcom and Cypress chips.
 e-m-b-a/embark
Centralized firmware scanning and reporting platform with a web UI, REST API, and automated analysis workflows for securing embedded/IoT devices.
 doudoudedi/hackembedded
This tool is used for encrypt backdoor,shellcode,socks5 proxy generation,Information retrieval and POC arrangement for various architecture devices
 yeet-src/usbsnoop
Live, system-wide USB transfer sniffer in eBPF — decodes USB traffic inline (control SETUP, SCSI, HID) from two universal URB hooks. No usbmon, no…
 aureliusivan/ubl-itel-s23
Unlock Bootloader for Itel S23 (S665L) / Unisoc T606 using CVE-2022-38694
 aureliusivaninvenioptl/ubl-itel-s23
Unlock Bootloader for Itel S23 (S665L) / Unisoc T606 using CVE-2022-38694
 qkaiser/broadcom-wps
Tools to fingerprint WiFi Access Points running the Broadcom SDK and a list of known affected devices.
 rfidresearchgroup/proxmark3
Hardware tool for RFID analysis, emulation, and penetration testing. Supports 125kHz, 13.56MHz protocols (MIFARE, iClass, ISO14443/15693) with key…
 unicorn-engine/unicorn
Unicorn CPU emulator framework (ARM, AArch64, M68K, Mips, Sparc, PowerPC, RiscV, S390x, TriCore, X86)
 idoka/awesome-canbus
:articulated_lorry: Awesome CAN bus tools, hardware and resources for Cyber Security Researchers, Reverse Engineers, and Automotive Electronics…
 seemoo-lab/nexmon
The C-based Firmware Patching Framework for Broadcom/Cypress WiFi Chips that enables Monitor Mode, Frame Injection and much more
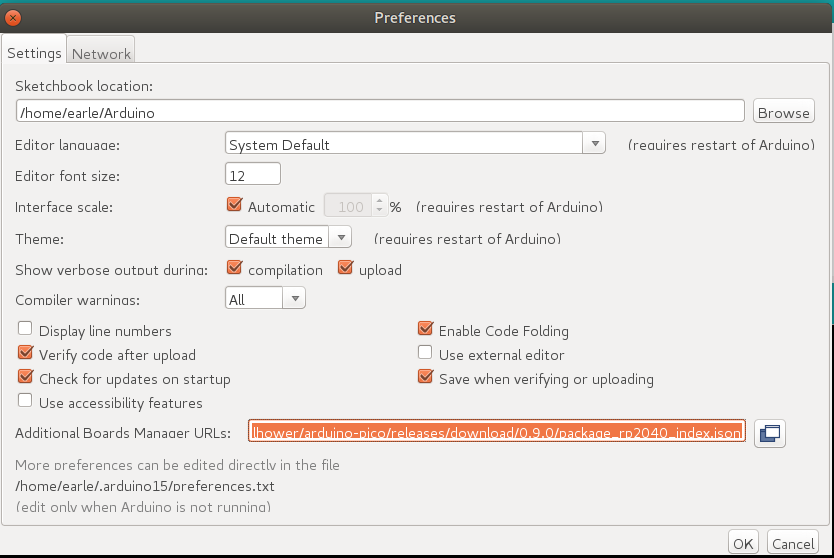 earlephilhower/arduino-pico
Raspberry Pi Pico Arduino core, for all RP2040 and RP2350 boards
 openocd-org/openocd
Official OpenOCD Read-Only Mirror (no pull requests)