
vmlinux-to-elf
 marin-m/vmlinux-to-elf
A tool to recover a fully analyzable .ELF from a raw kernel, through extracting the kernel symbol table (kallsyms)
binary-analysisembedded-systems-securityfirmware-analysis+1
1.8k
marin-m/vmlinux-to-elfA tool to recover a fully analyzable .ELF from a raw kernel, through extracting the kernel symbol table (kallsyms)
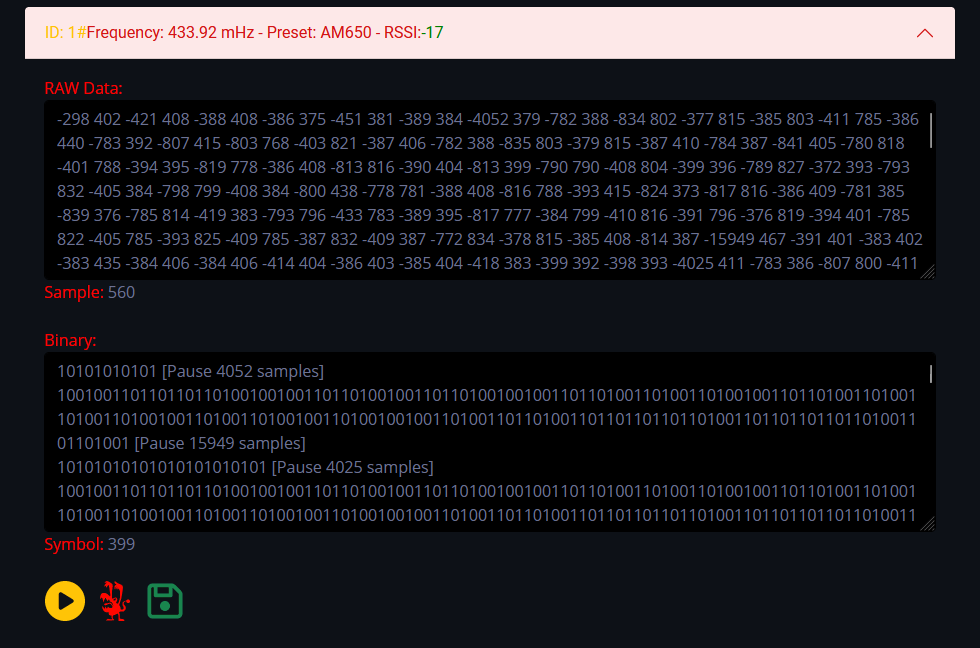 h-rat/evilcrowrf_custom_firmware_cc1101_flipperzero
This firmware is an alternative to the EvilCrowRF default firmware. Module: CC1101 - Compatible Flipper Zero file.
 trou/cpu_rec_rs
Determine which CPU architecture is used in a binary file.
 adamhrv/skylift
Wi-Fi Geolocation Spoofing with ESP8266 / ESP32
 nccgroup/ghidra-nanomips
nanoMIPS module for Ghidra
 nccgroup/zipdefrag
Presented at Recon Montreal 2018
 ret5et/watchguard_webui_unpacker
Watchguard Sysa-dl file format
 nccgroup/mtk_bp
Tools for analyzing and reverse engineering MediaTek baseband firmware, including file extraction, symbol parsing, and Ghidra integration for modem…
 ihsibo/rom-0-decoder
Rom-0 file password decrypter
 sermikr0/cve-2026-38427
CVE-2026-38427 — Integer Wraparound → Heap Buffer Overflow in Tasmota fetch_jpg() uint16_t (Tasmota <= 15.3.0.3)
 sermikr0/cve-2026-38426
CVE-2026-38426 — strcpy() Stack Buffer Overflow in Tasmota fetch_jpg() boundary[40] (Tasmota <= 15.3.0.3)
 sermikr0/cve-2026-38422
CVE-2026-38422 — Remote Code Execution via Combined Buffer Overflows in Tasmota fetch_jpg() (Tasmota <= 15.3.0.3)
 o7-machinehum/phantomdrive
Seemingly normal USB drive with a hidden security feature
 olafdaf/cve-2022-40363
A buffer overflow in the component nfc_device_load_mifare_ul_data of Flipper Devices Inc., Flipper Zero before v0.65.2 allows attackers to cause a…
 mateustesser/cve-2023-31716
Proof-of-concept exploit for CVE-2023-31716, a Local File Inclusion vulnerability in FUXA SCADA/HMI software versions <= 1.1.12, enabling arbitrary…
 cyberharsh/mini_httpd-cve-2018-18778
PoC exploit for CVE-2018-18778: arbitrary file read in mini_httpd 1.29 via empty Host header, affecting IoT devices from Huawei, Zyxel, and others.
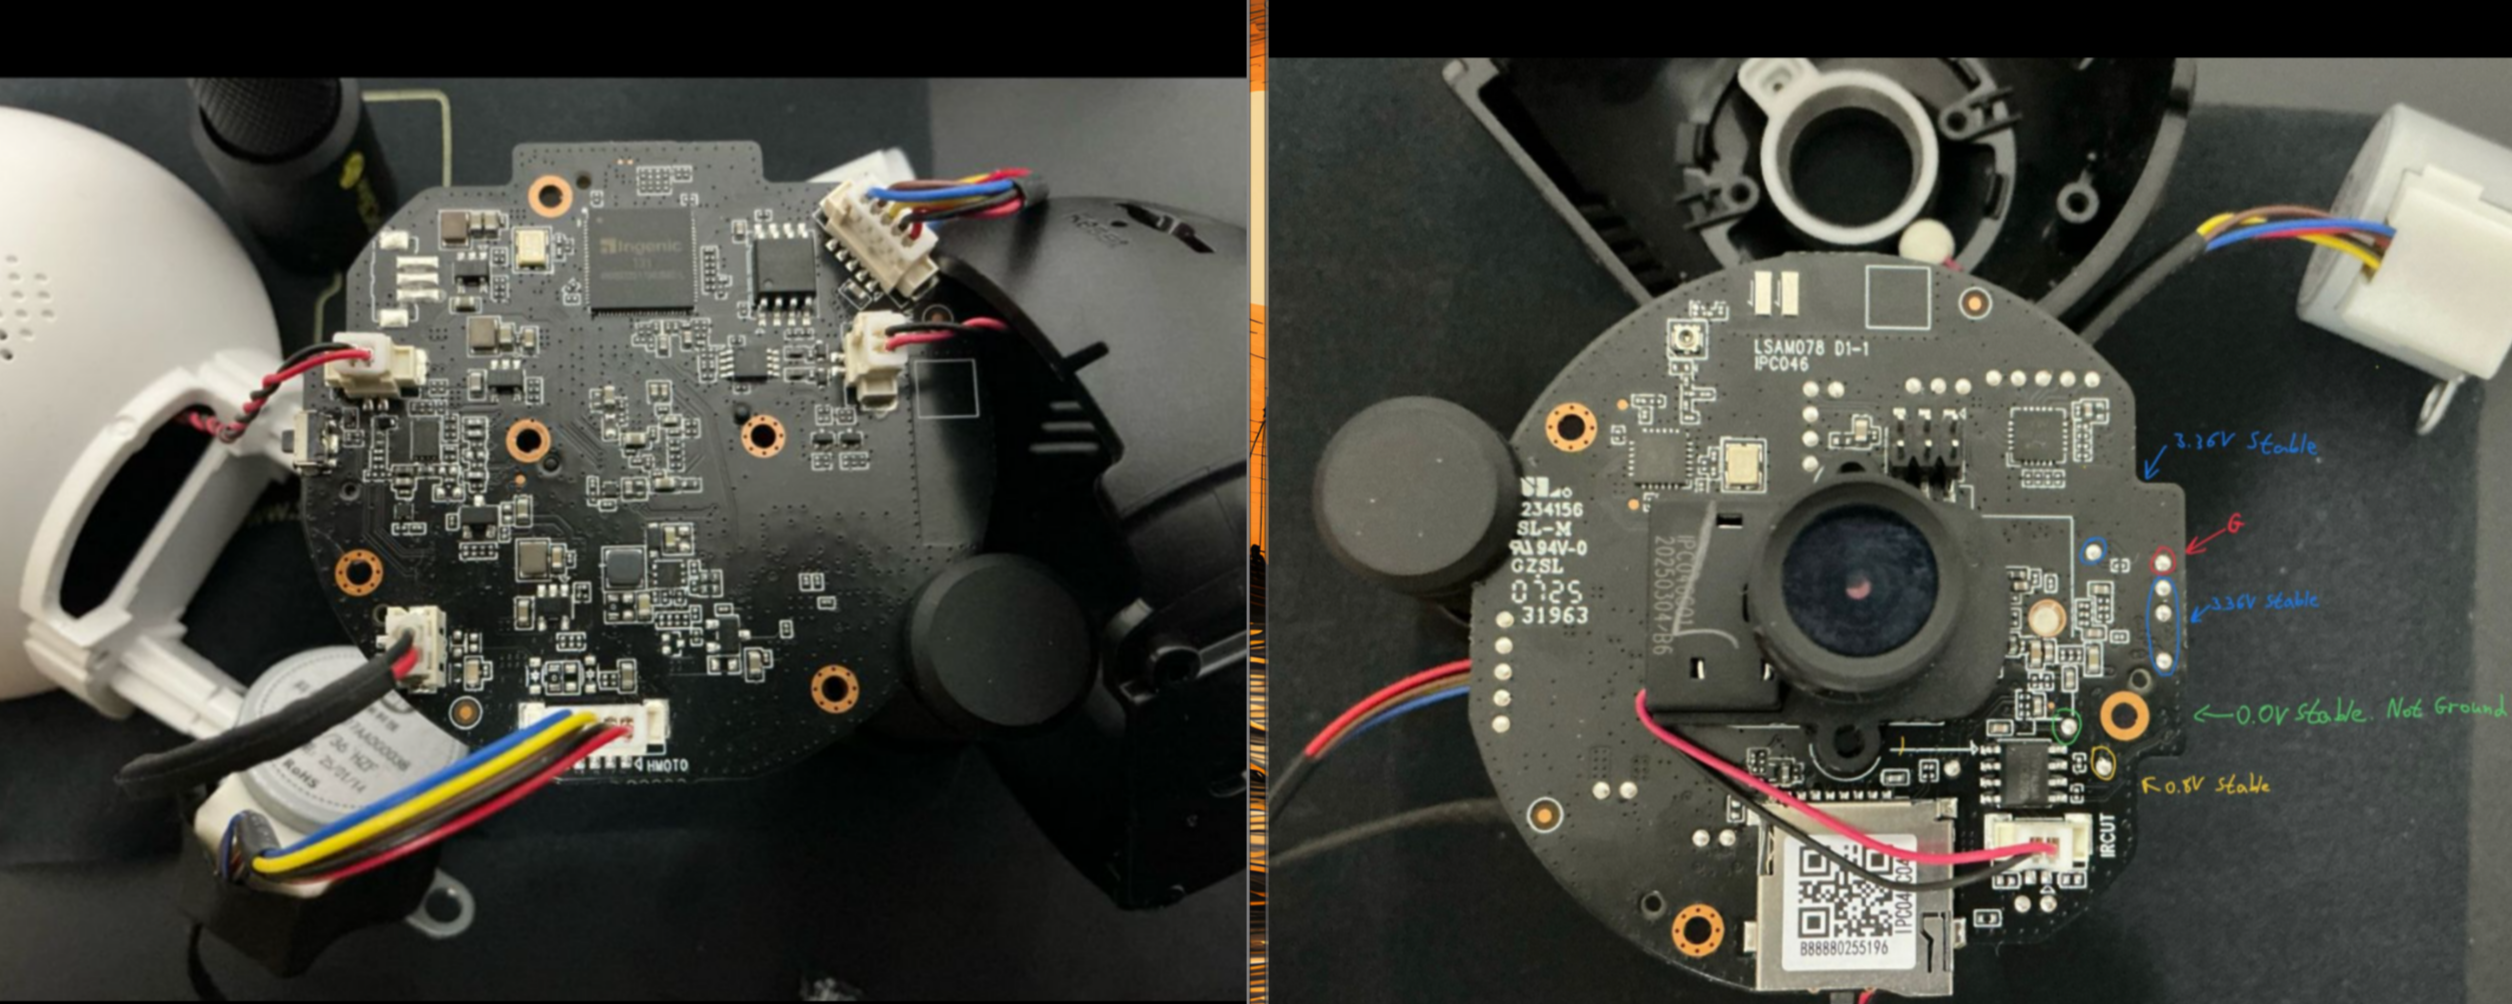 h3xdum/xiaomi-c200-firmware-analysis
From UART to Root: Breaking Into the Xiaomi C200 via U-Boot