
CVE-2026-90847
 shlln/cve-2026-90847
Proof-of-concept for CVE-2026-90847, an authenticated RCE in iux_set.cgi via malicious .cfg tar upload that writes commands into crontab for…
embedded-systems-securityexploitationiot-security+5
shlln/cve-2026-90847Proof-of-concept for CVE-2026-90847, an authenticated RCE in iux_set.cgi via malicious .cfg tar upload that writes commands into crontab for…
 hackspeak/cve-2026-94095
PoC for CVE-2026-94095, a traceroute command injection in Netcore NBR200V2 firmware via ubus JSON-RPC, enabling root RCE for authorized testing.
 mattgsys/cve-2026-19586
Python PoC exploiting CVE-2026-19586, an unauthenticated command injection in TP-Link Omada SSL VPN that executes arbitrary commands as root via…
 jiegec/loongbleed
Proof-of-concept demonstrating a microarchitectural data leak in Loongson LA464/LA664 processors via undefined upper bits of LASX vector registers,…
 hackspeak/cve-2026-93958
Authenticated command injection PoC for D-Link R95/BE9500 DHMAPI SetTimeSettings, achieving root RCE via NTPServer backtick injection, with full…
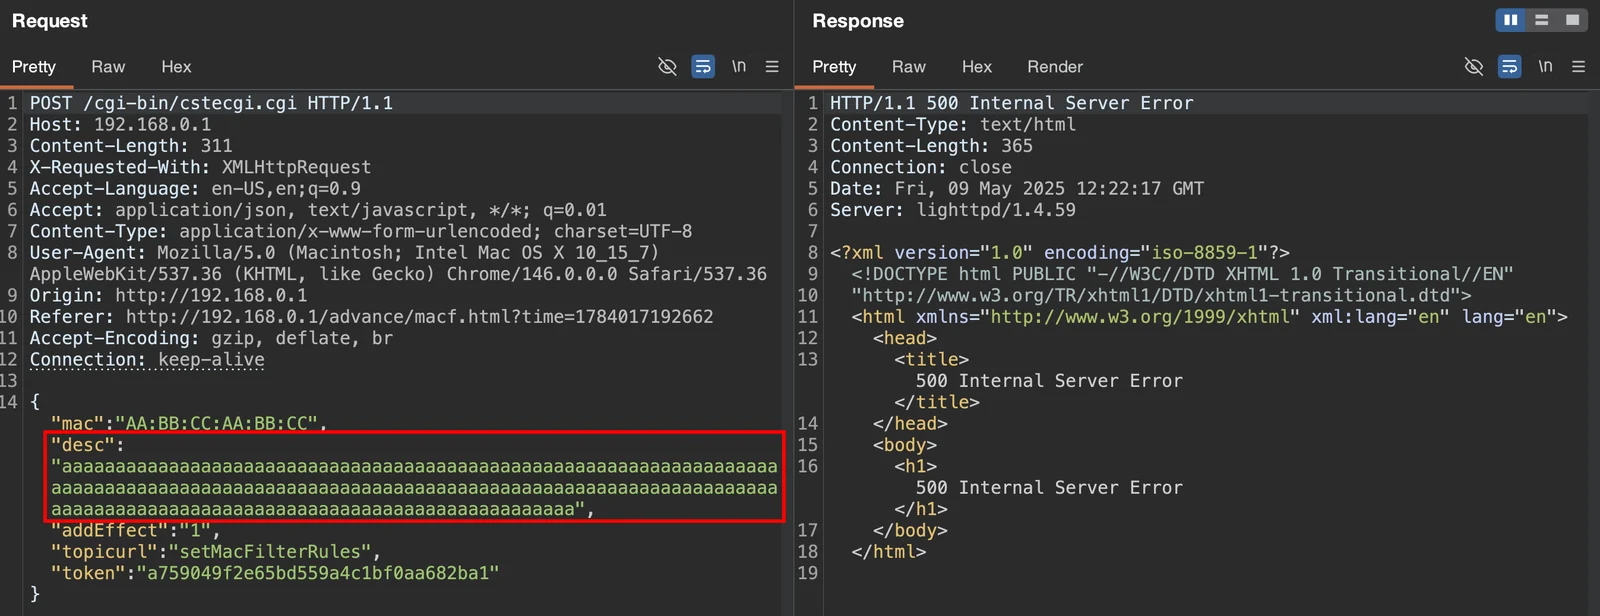 xernary/cve-2026-82539
Security advisory for TOTOLINK a720r buffer overflow vulnerability
 minanagehsalalma/zyxel-wax650s-research-notebook-public
Wiki-style research notebook for Zyxel WAX650S firmware emulation and vulnerability analysis
 rva3/cve-2026-40003
Exploit for CVE-2026-40003, an arbitrary memory write vulnerability in ZXIC/Sanechips ZX297520V3 SoC BootROM, enabling code execution via USB…
 setsuneko/ghostlock_mt6983v_5.10
High-risk vulnerability CVE-2026-43499, implementation on the 5.10 kernel and MediaTek MT6983V
 gitchw/ghostlock-cve-2026-43499
CVE-2026-43499 (GhostLock) — Linux kernel futex PI rt_mutex UAF ARM32 privilege escalation research targeting Huawei Watch 4 Pro (kernel 5.4.210)
 0xqrx/cve-2024-6333
Authenticated Remote Code Execution vulnerability in Xerox WorkCentre printers via the Network Troubleshooting Log feature.
 gimminse/firmware-analysis
Rediscovered CVE-2020-25279, a critical vulnerability in the Shannon baseband used in Samsung Exynos chipsets
 pablomk7/enlbufferpwn
Information and PoC about the ENLBufferPwn vulnerability
 msdmehdipour/meshtastic-cve-2025-52464-poc
Software-only proof of concept for CVE-2025-52464 in Meshtastic Direct Messages
 leochen-coremind/spd_flasher
CVE-2022-38694 Hardened Exploit - RP2350 USB Host Auto Flasher for Unisoc devices
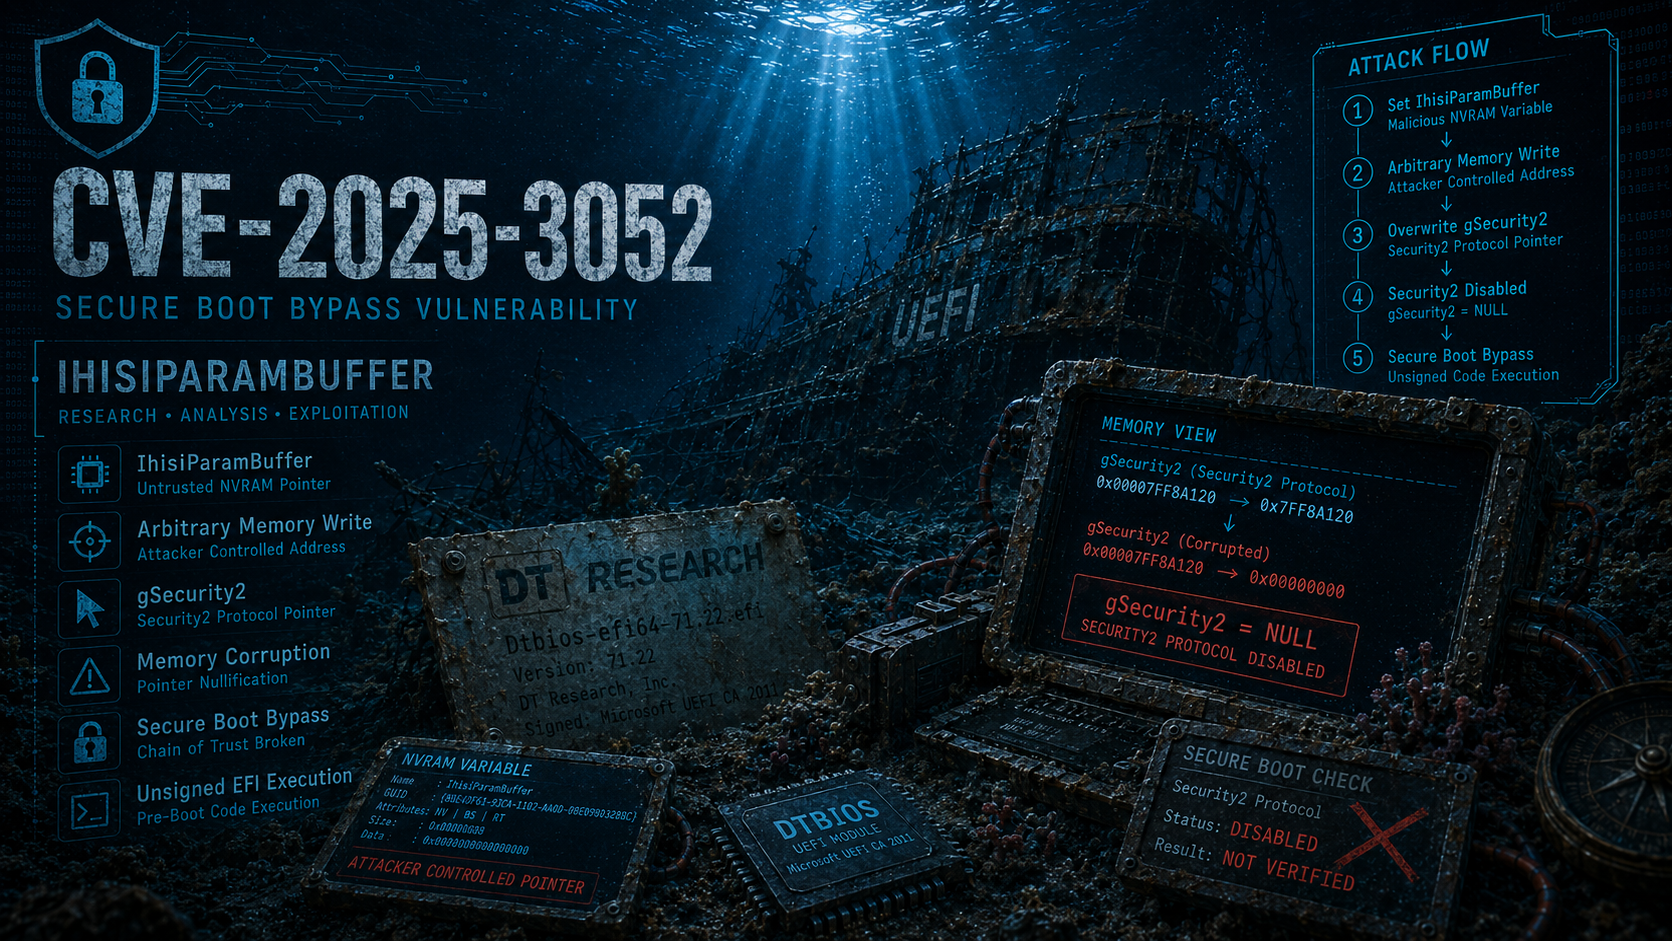 themalwareguardian/cve-2025-3052
Research on CVE-2025-3052, an Insyde firmware vulnerability that exposes an arbitrary write primitive capable of modifying security-critical pointers.
 george0papasotiriou/cve-2026-22017-firmware-update-via-ble-without-authentication
Simulated BLE peripheral exposing an unauthenticated GATT firmware-update characteristic; demonstrates critical CVE-2026-22017 device-takeover…
 hackerhouse-opensource/exploits
exploits and proof-of-concept vulnerability demonstration files from the team at Hacker House