

MeshCore
 meshcore-dev/meshcore
A new lightweight, hybrid routing mesh protocol for packet radios
command-and-controldata-exfiltrationeducation+8
meshcore-dev/meshcoreA new lightweight, hybrid routing mesh protocol for packet radios
 doudoudedi/hackembedded
This tool is used for encrypt backdoor,shellcode,socks5 proxy generation,Information retrieval and POC arrangement for various architecture devices
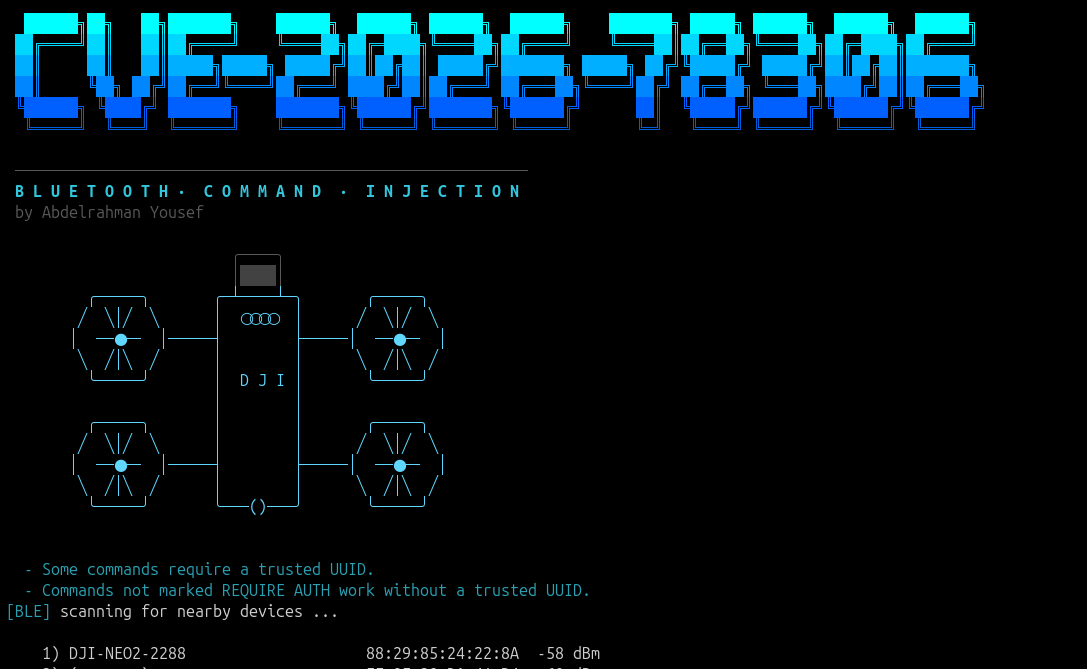 wh02m1/cve-2026-78306
Proof-of-concept exploiting DJI drone Bluetooth DUML command injection, sending unauthenticated commands to read credentials, alter Wi-Fi config, and…
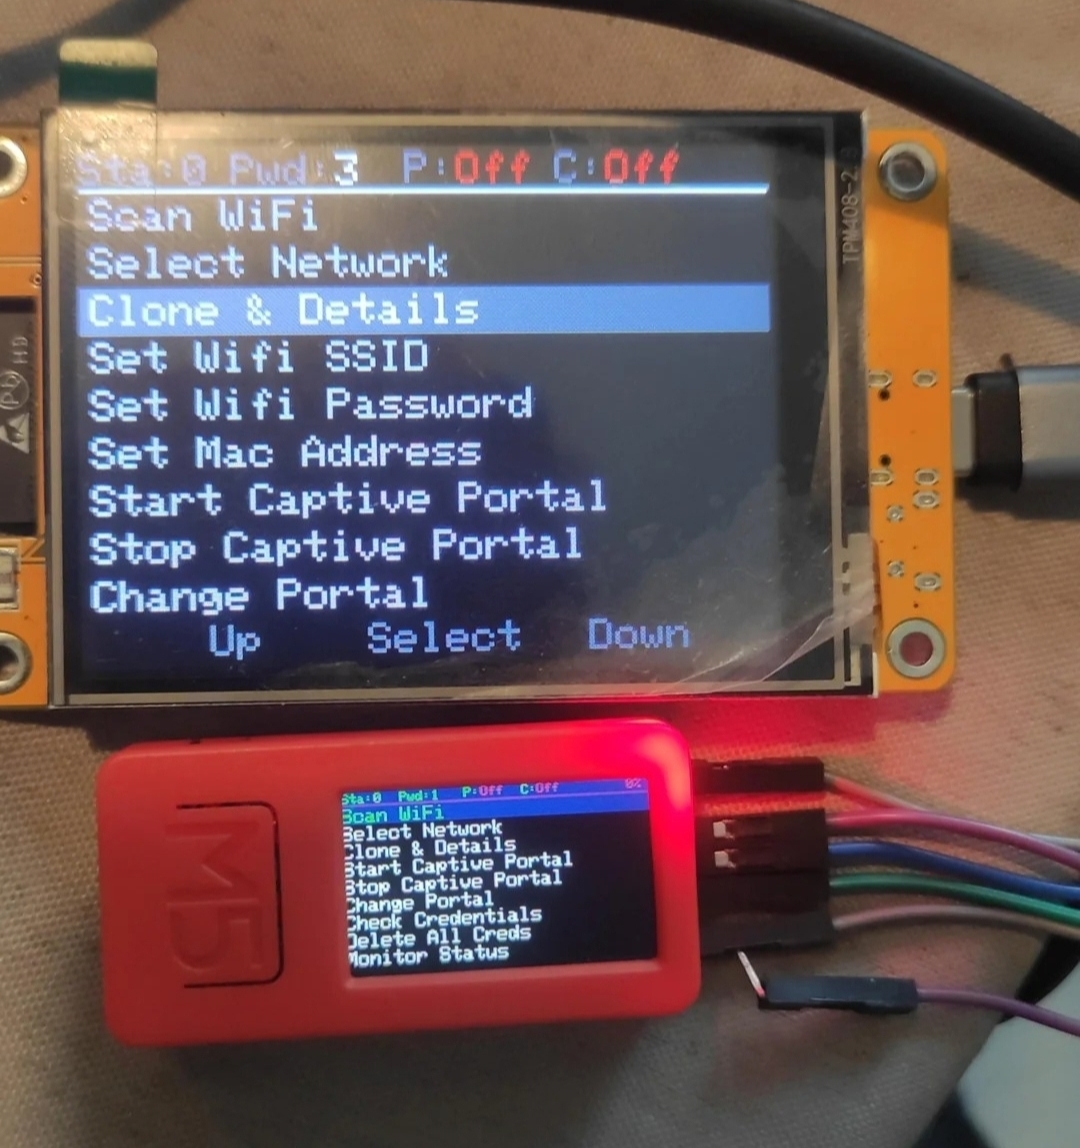 7h30th3r0n3/evil-m5project
Multi-purpose WiFi penetration testing toolkit for M5Stack devices. Performs network scanning, evil-twin attacks, deauthentication, captive portal…
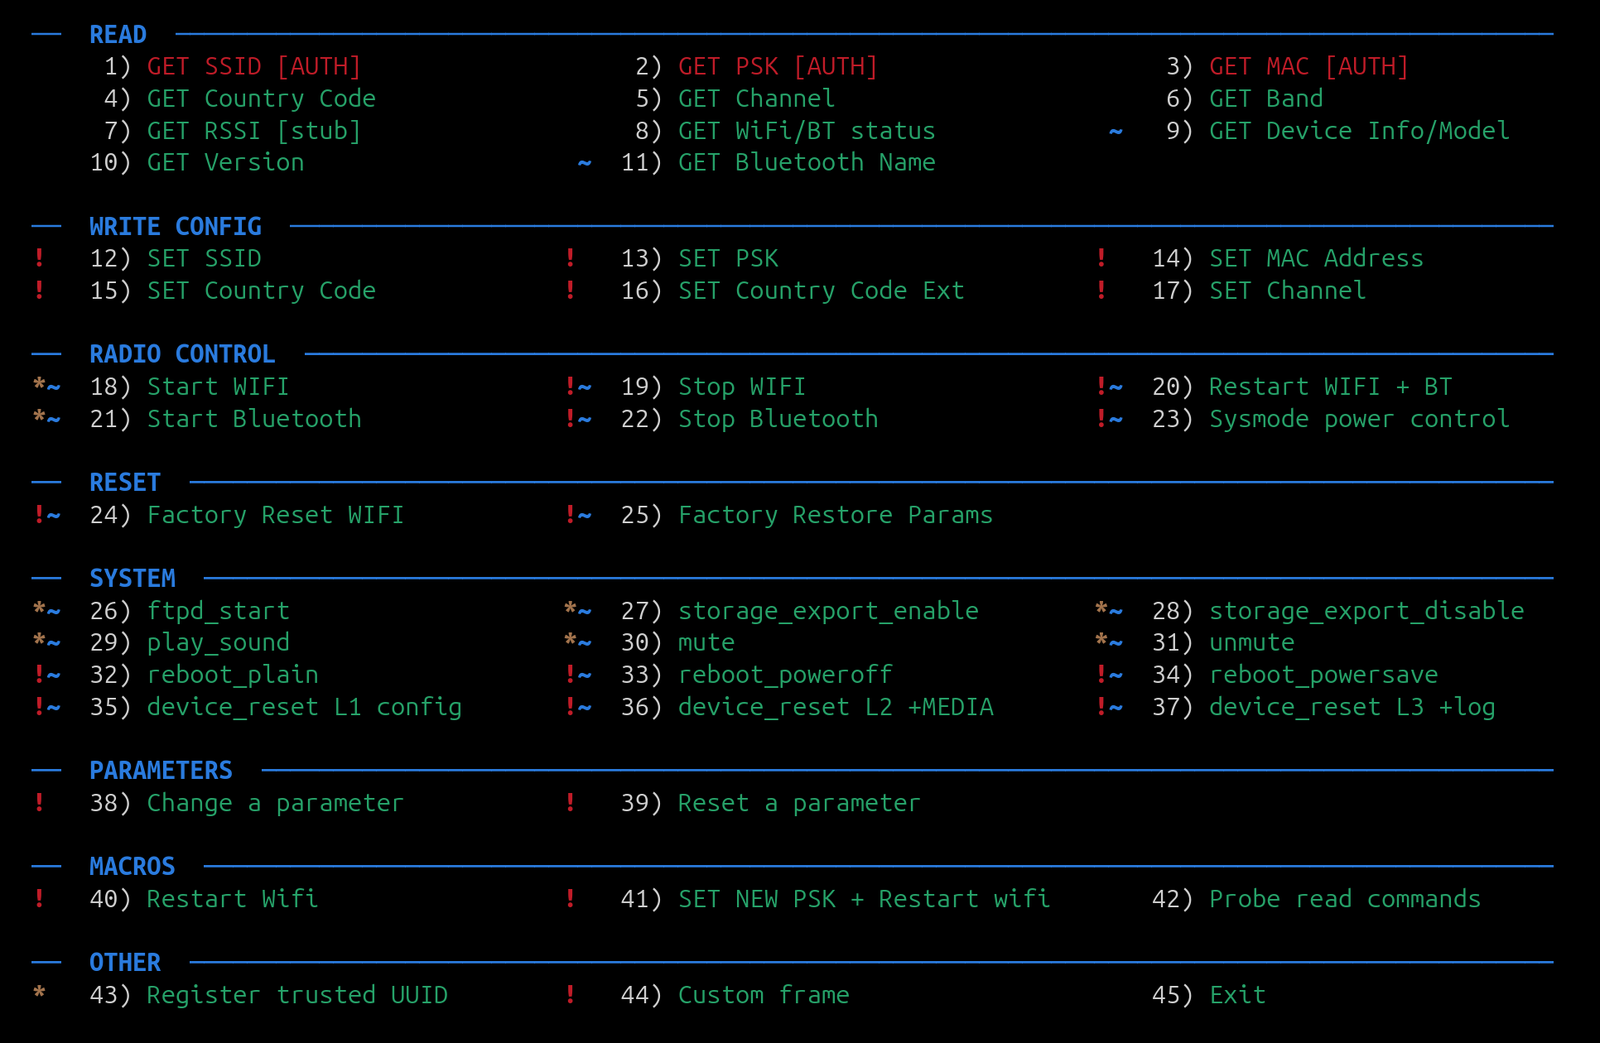 feedbeef/dji_ble_vuln
DJI Drone DUML Command Injection over Bluetooth — Proof of Concept for CVE-2026-78306
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 kristof-mattei/gardyn-hack
CVE-2025-29628, CVE-2025-29629, CVE-2025-29630, CVE-2025-29631
 qurbat/cve-2020-8958
Proof of concept for arbitrary OS command execution on Guangzhou/V-SOL 1GE ONU devices (CVE-2020-8958)
 george0papasotiriou/cve-2026-21006-zigbee-light-link-factory-reset-exploit
Simulated Zigbee Light Link (ZLL) factory reset exploit for CVE-2026-21006, demonstrating unauthenticated TouchLink command injection that wipes…
 joshuapassos/cmf-watch-pro-2-ble-protocol
Reverse-engineered BLE protocol for the CMF Watch Pro 2, documenting GATT layout, AES-128-CBC encrypted command frames, authentication handshake, and…
 analyticeth/tesla-security-research
Vulnerability research on Tesla Model 3/Y infotainment systems. 6 vulnerabilities, 4 CVEs (CVE-2022-42005 through CVE-2022-42008). Root shell,…
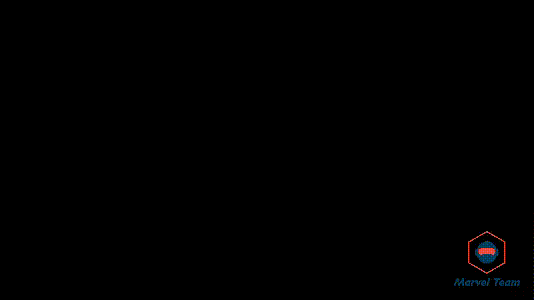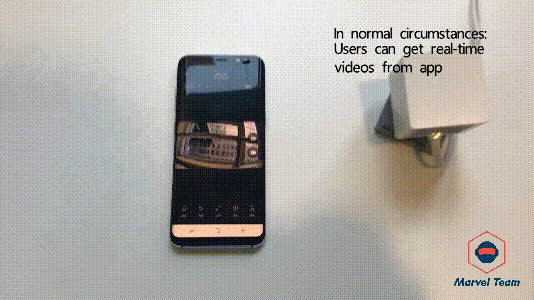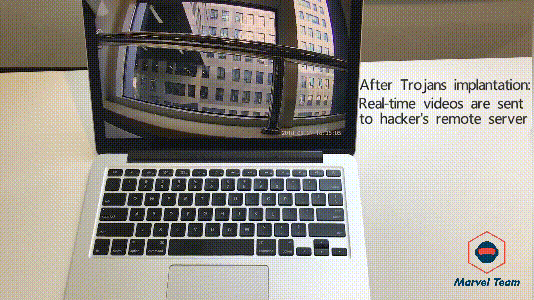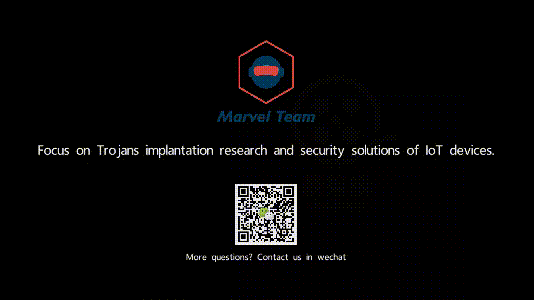 arthastang/iot-implant-toolkit
Toolkit for implant attack of IoT devices
 l0lsec/tapo-c260-rce
PoC exploit chain for TP-Link Tapo C260 camera — CVE-2026-0651/0652/0653. Research by @spaceraccoon.
 hackspeak/cve-2026-94095
PoC for CVE-2026-94095, a traceroute command injection in Netcore NBR200V2 firmware via ubus JSON-RPC, enabling root RCE for authorized testing.
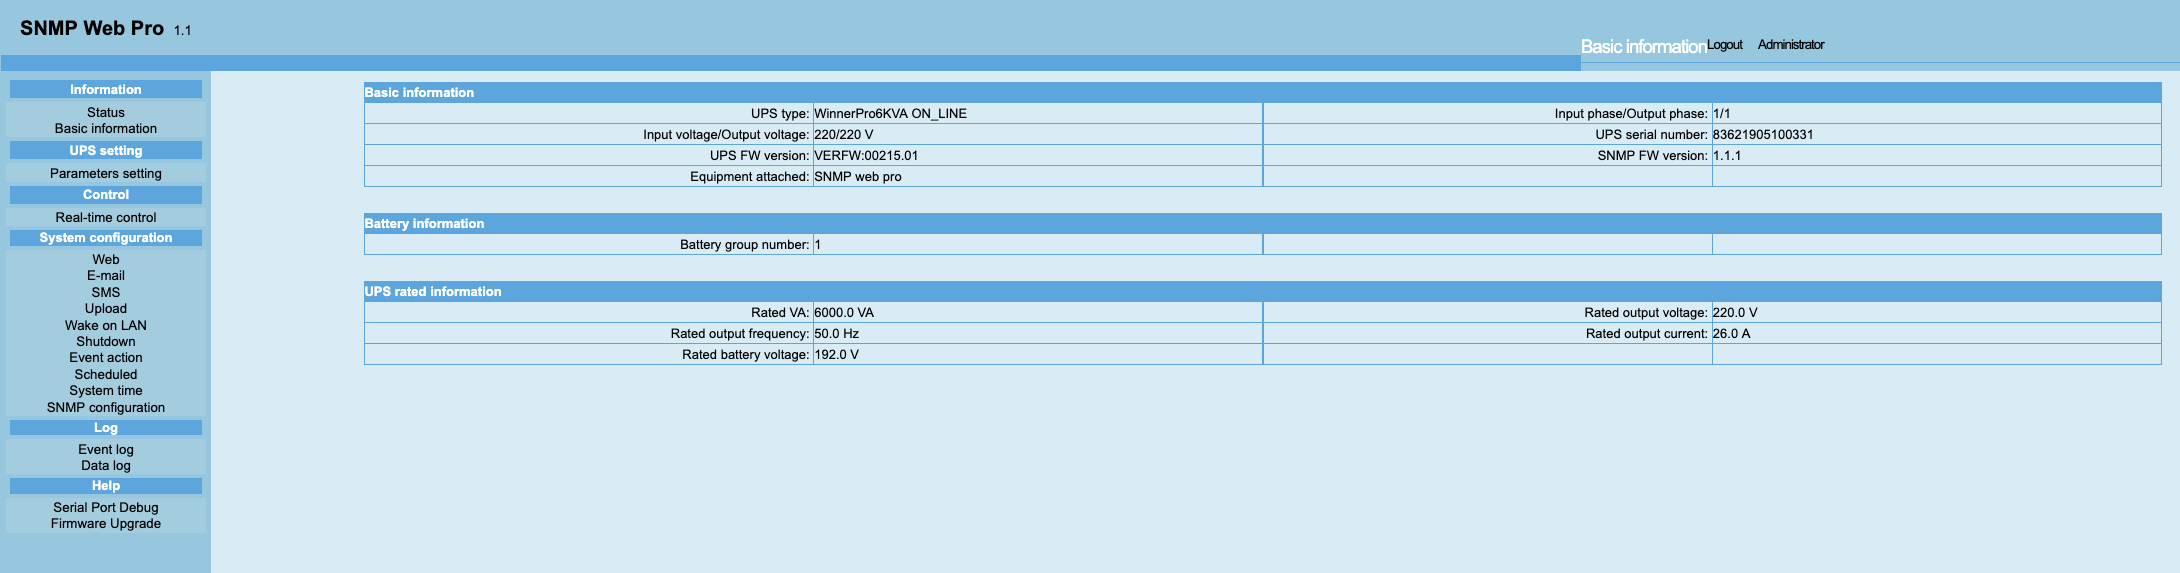 virgula0/cve-2026-44402
Pre-Authenticated Full Root Remote Command Execution in Voltronic Power SNMP Web Pro 1.1
 clearbluejar/pyghidra-mcp
Python Command-Line Ghidra MCP
 nccgroup/mtk_bp
Tools for analyzing and reverse engineering MediaTek baseband firmware, including file extraction, symbol parsing, and Ghidra integration for modem…
 nccgroup/blesuite-cli
BLESuite_CLI is a command line tool to enable an easier way to test Bluetooth Low Energy (BLE) devices