Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
31 results
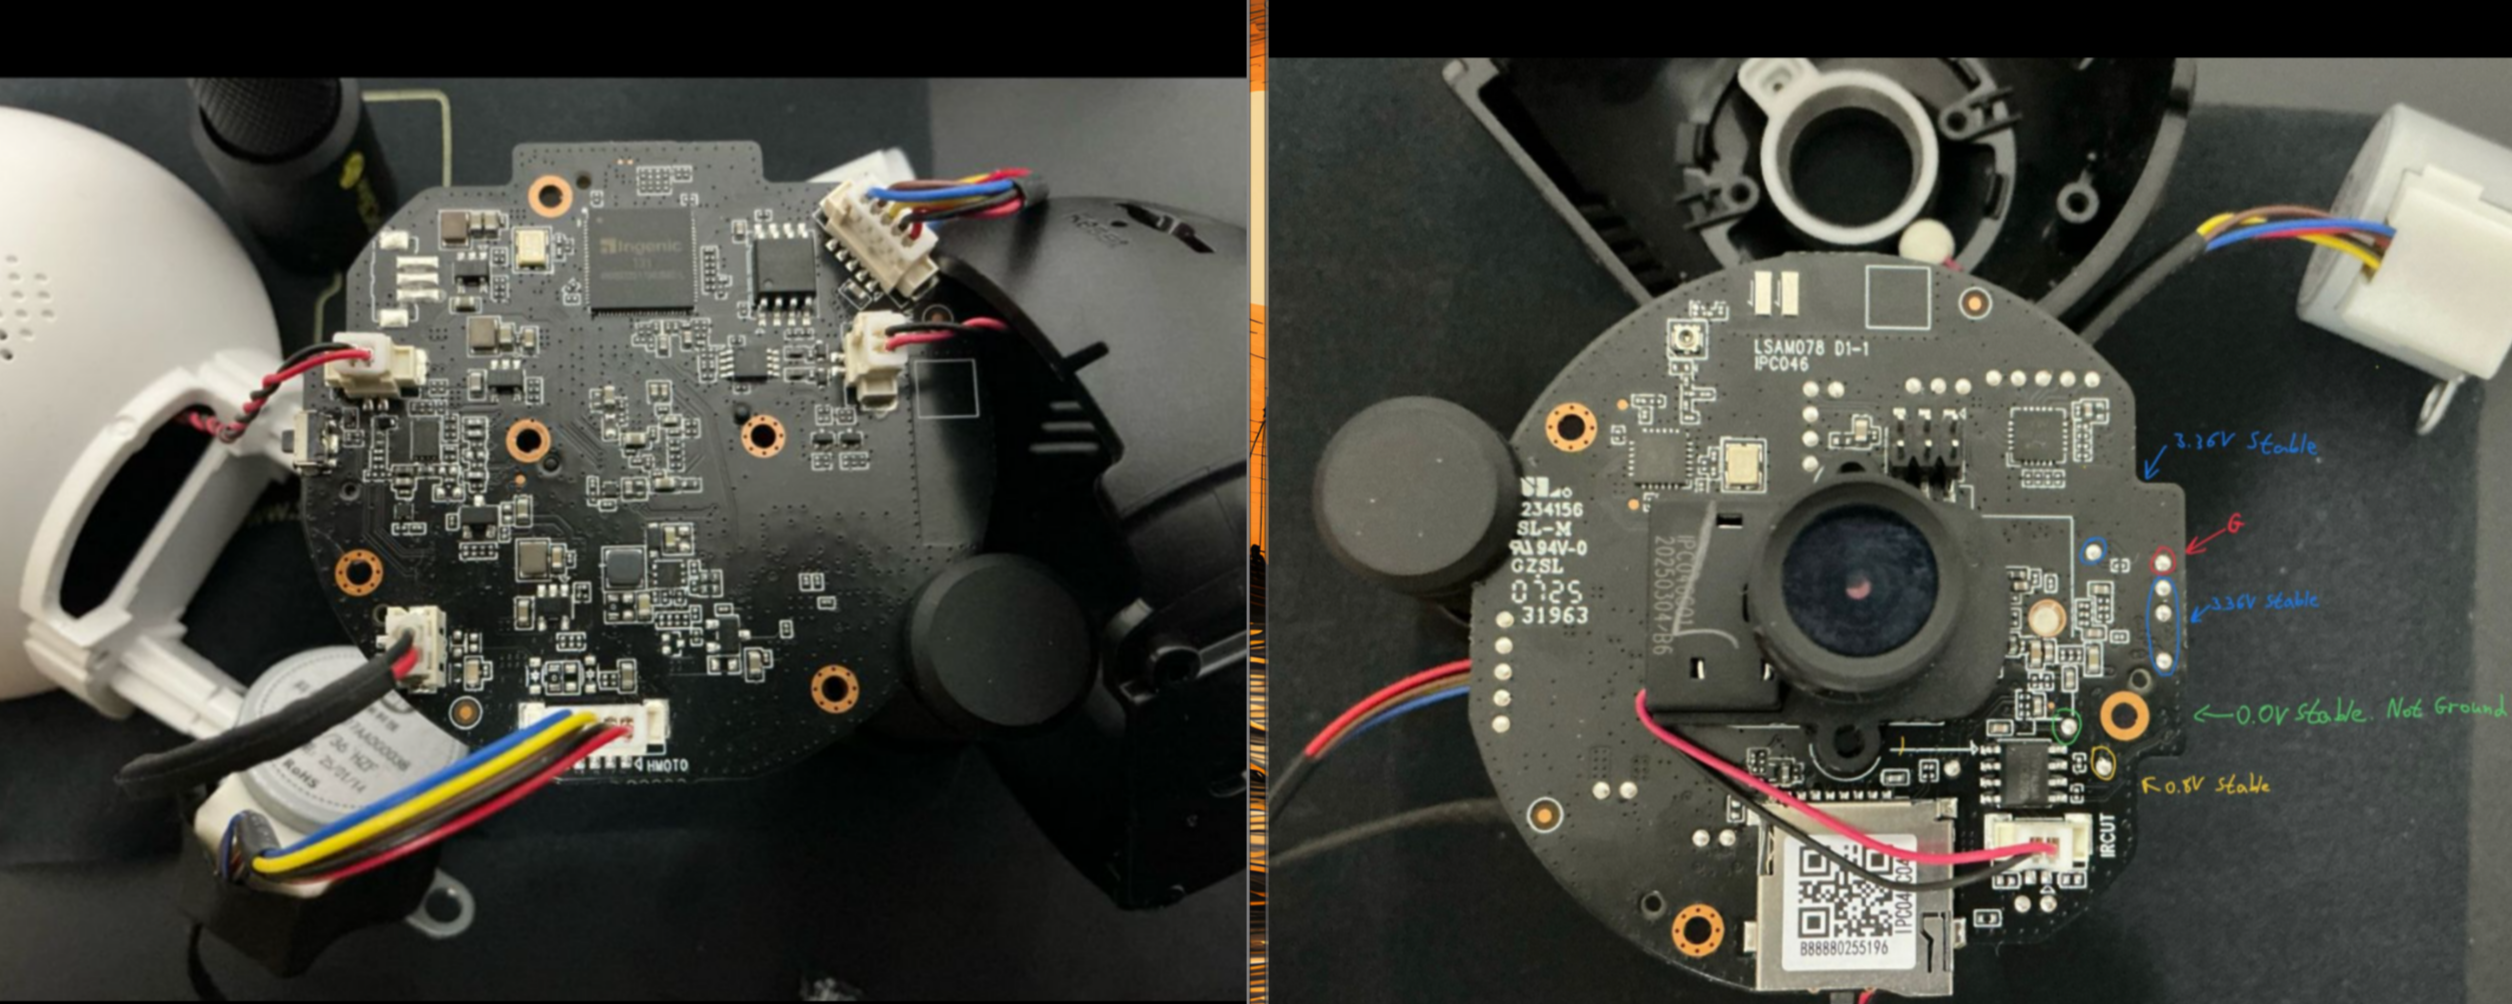
Xiaomi-C200-Firmware-Analysis preview

Xiaomi-C200-Firmware-Analysis

GitHubh3xdum/xiaomi-c200-firmware-analysis

From UART to Root: Breaking Into the Xiaomi C200 via U-Boot
data-recoveryembedded-systems-securityexploitation+6
11
9 months ago
unblob preview

unblob

GitHubonekey-sec/unblob

Extract files from any kind of container formats

binary-analysisdata-recoveryembedded-systems-security+3
2.6k2 days ago
phantomdrive preview

phantomdrive

GitHubo7-machinehum/phantomdrive

Seemingly normal USB drive with a hidden security feature
cryptographydata-recoveryembedded-systems-security+3
86825 days ago
Mini_httpd-CVE-2018-18778 preview

Mini_httpd-CVE-2018-18778

GitHubcyberharsh/mini_httpd-cve-2018-18778

PoC exploit for CVE-2018-18778: arbitrary file read in mini_httpd 1.29 via empty Host header, affecting IoT devices from Huawei, Zyxel, and others.
embedded-systems-securityexploitationfuzzing+3
6 years ago
vmlinux-to-elf preview

vmlinux-to-elf

GitHubmarin-m/vmlinux-to-elf

A tool to recover a fully analyzable .ELF from a raw kernel, through extracting the kernel symbol table (kallsyms)
binary-analysisembedded-systems-securityfirmware-analysis+1
1.8k3 months ago
uefi_retool preview
Archived

uefi_retool

GitHubyeggor/uefi_retool

A tool for UEFI firmware reverse engineering
binary-analysisembedded-systems-securityfirmware-analysis+3
3681 year ago
gdbfuzz preview
Archived

gdbfuzz

GitHubboschresearch/gdbfuzz

Fuzzing Embedded Systems using Hardware Breakpoints

binary-analysisdebuggerseducation+6
1972 years ago
skylift preview

skylift

GitHubadamhrv/skylift

Wi-Fi Geolocation Spoofing with ESP8266 / ESP32

embedded-systems-securityhardware-iot-securityimpersonation-tools+3
5252 years ago
ME2-Writeup preview

ME2-Writeup

GitHubcoremaze/me2-writeup

Reconstructing a Dead USB Protocol: A Handheld's Secrets Unlocked by a Hot Knife, a multi-disciplinary journey to reviving a forgotten USB interface
binary-analysisdata-recoveryeducation+5
505 months ago
mtk_bp preview

mtk_bp

GitHubnccgroup/mtk_bp

Tools for analyzing and reverse engineering MediaTek baseband firmware, including file extraction, symbol parsing, and Ghidra integration for modem…
binary-analysisembedded-systems-securityfirmware-analysis+4
813 months ago
zipdefrag preview

zipdefrag

GitHubnccgroup/zipdefrag

Presented at Recon Montreal 2018
data-recoverydigital-forensicsembedded-systems-security+3
78 years ago
ATAboy preview

ATAboy

GitHubredrum0381/ataboy

ATAboy is a user-friendly bridge that allows legacy CHS only style IDE (PATA) hard drives to be connected to a modern computer as a standard USB Mass…

data-recoverydigital-forensicsembedded-systems-security+4
2044 months ago
cpu_rec_rs preview

cpu_rec_rs

GitHubtrou/cpu_rec_rs

Determine which CPU architecture is used in a binary file.
binary-analysisembedded-systems-securityfirmware-analysis+2
1305 months ago
CVE-2026-38426 preview

CVE-2026-38426

GitHubsermikr0/cve-2026-38426

CVE-2026-38426 — strcpy() Stack Buffer Overflow in Tasmota fetch_jpg() boundary[40] (Tasmota <= 15.3.0.3)
binary-exploitationembedded-systems-securityexploitation+4
4 months ago
EvilCrowRF_Custom_Firmware_CC1101_FlipperZero preview

EvilCrowRF_Custom_Firmware_CC1101_FlipperZero

GitHubh-rat/evilcrowrf_custom_firmware_cc1101_flipperzero

This firmware is an alternative to the EvilCrowRF default firmware. Module: CC1101 - Compatible Flipper Zero file.
embedded-systems-securityhardware-hackinghardware-iot-security+5
6042 years ago
MK4001MTD-USB-Bridge preview

MK4001MTD-USB-Bridge

GitHubwill127534/mk4001mtd-usb-bridge

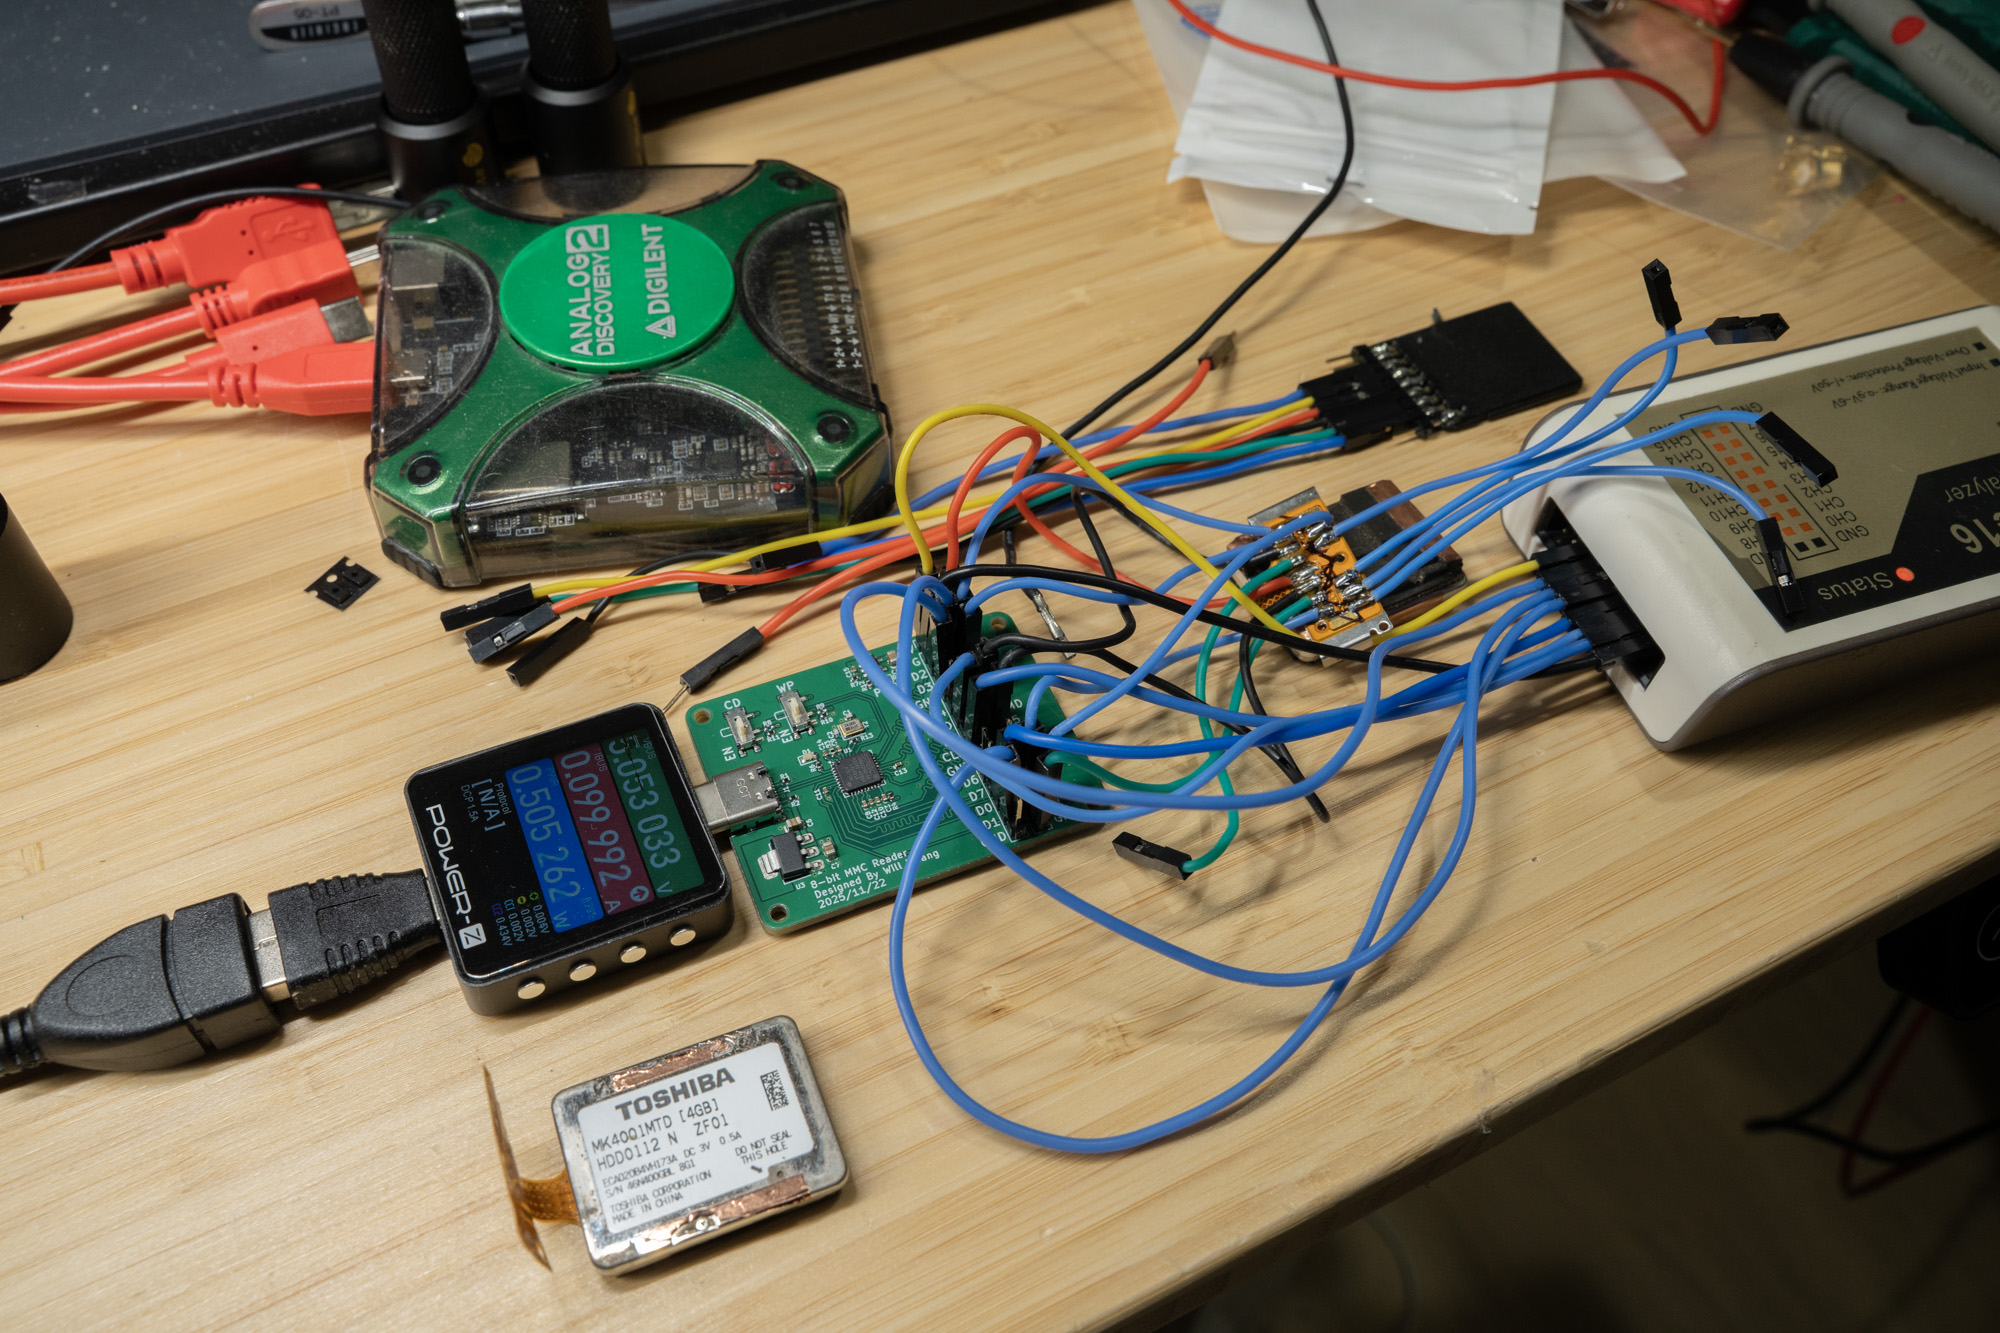
RP2040 firmware that bridges a Toshiba MK4001MTD 0.85" SDIO microdrive as a USB mass storage device, implementing the full SDIO-ATA protocol stack…
data-recoveryembedded-systems-securityfirmware-analysis+4
442 months ago
CVE-2026-90847 preview

CVE-2026-90847

GitHubshlln/cve-2026-90847

Proof-of-concept for CVE-2026-90847, an authenticated RCE in iux_set.cgi via malicious .cfg tar upload that writes commands into crontab for…

embedded-systems-securityexploitationiot-security+5
3 days ago
CVE-2024-33676 preview

CVE-2024-33676

GitHubdersecure/cve-2024-33676

Technical disclosure of CVE-2024-33676: weak authentication on Enel X JuiceBox EV chargers enabling PII extraction, settings manipulation, and OS…

authentication-authorizationeducationembedded-systems-security+9
1 year ago
Previous12Next